Results for “attacks”

The Guardian NATO Peter Beaumont Senior international correspondent

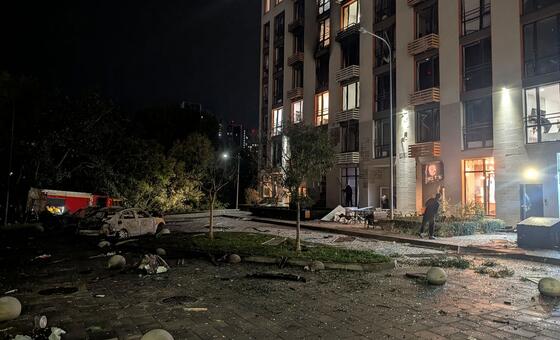
Nato increases Black Sea deployment amid escalating deadly Russian attacks

Mounting anxiety as Russia’s war on Ukraine reaches Nato’s borders with targeting of vessels transporting agricultural cargo Nato is deploying additional military assets to the Black Sea amid the recent deadly escalation of Russian attacks on merchant shipping, as five more vessels were attacked on Tuesday. Russia’s military said it ⁠struck ​three cargo vessels in Ukraine’s ⁠port of Reni and two ⁠other cargo vessels en ​route ‌to ‌Odesa.

Read at The Guardian NATO

arXiv (research papers) Zhiyue Xu SI

After the Attacker Leaves: Benchmarking Carryover Attacks on LLM Agents

Modern LLM agents persist state across sessions via two channels: long-lived memory files silently prepended to the system prompt, and scheduled tasks waking the agent without user input. A one-time indirect prompt injection committed to either channel can re-fire across sessions long after the attacker leaves, threats we term carryover attacks. Existing prompt-injection benchmarks evaluate attacks only in the session where malicious content is first observed, leaving the…

Read at arXiv (research papers)

The Guardian Sudan Carlos Mureithi and agencies

Drone attack near market kills 80 in Sudan

Witness says drone struck twice at transport hub in al-Dibab, in one of deadliest single attacks of war A drone strike near a market in southern Sudan on Sunday evening killed 80 people, mostly commuters catching rides home. Ahmed Wadi, a witness, said the attack in the town of al-Dibab in West Kordofan state left “50 bodies who I helped bury, one of them my own brother Mohamed”.

Read at The Guardian Sudan

arXiv (research papers) Mengxiao Wang SI

Fake News, Real Crashes: Information Injection Attacks on LLM Financial Trading Agents

Large language model (LLM) agents now trade real capital using news as evidence, yet they cannot reliably tell fabricated headlines from real news. Because they read the same feeds under near-identical policies, a single fabricated post can push them into the same trade at the same moment. We present a systematic attack benchmark for information injection against LLM trading agents. Unlike prompt injection, which targets the model's instructions, information injection…

Read at arXiv (research papers)

arXiv (research papers) Yuchen Chen SI

RAGLeak: Supply-Chain Privacy Backdoors in Retrieval-Augmented Generation

Retrieval-Augmented Generation (RAG) enables large language models to access external knowledge during inference, but its reliance on external knowledge bases also introduces new attack surfaces. Existing data extraction attacks against RAG systems rely on either prompt injection, which heavily depends on the generator's instruction-following capability, or backdoors that reproduce or paraphrase retrieved documents but struggle to balance extraction fidelity and…

Read at arXiv (research papers)

The Guardian NATO Peter Beaumont Senior international correspondent

Intensifying drone attacks on ships in Black Sea bring war ever closer to Nato shores

Six attacks in 10 days by suspected Russian drones mark dramatic escalation in maritime conflict The first the crew of the Bulgarian ferry Dioscuria knew of an attack on a cargo ship in their country’s exclusive economic zone in the Black Sea in the early hours of 6 October was a distant explosion 70 miles off the coastal town of Byala. The Turkish-owned Alfa Watan, heading for the Romanian port of Sulina, had been struck by suspected Russian air and naval drones. Arriving…

Read at The Guardian NATO

arXiv (research papers) Stavros Damianakis SI

SoK: PIAtlas: Decomposing the Unbounded Prompt Injection Attack Space

Prompt injection is the dominant security risk for large-language-model (LLM) applications and agents, yet the field still lacks a coherent map of how these attacks are constructed. More than twenty public datasets describe prompt injection using incompatible vocabularies, often organized around delivery vector, attacker goal, or generation method. In this Systematization of Knowledge, we present PIAtlas, a taxonomy organized instead around how the injected instruction is…

Read at arXiv (research papers)

Hacker News adikshatriyag SI

Show HN: AegisKernel – Test prompt injection attacks on AI agents in the browser

Article URL: https://adikshatriyag-crypto.github.io/aegis-kernel/ Comments URL: https://news.ycombinator.com/item?id=50132623 Points: 1 # Comments: 0

Read at Hacker News

Journal articles (OpenAlex) Fadhila Tlili, Samiha Ayed, Lamia Chaari Fourati · Soft Computing Security

A SOC-innovative intelligent framework for UAVs cybersecurity

Abstract Unmanned Aerial Vehicles (UAVs) have increasingly emerged as critical assets in various civil and military applications, yet they remain highly vulnerable to a broad spectrum of cyber and physical security attacks. Such threats can compromise essential UAV functionalities, including communication links, navigation accuracy, and data integrity. While Security Operation Centers (SOCs) have been widely deployed to safeguard Internet of Things (IoT) infrastructures…

Read at Journal articles (OpenAlex)

arXiv (research papers) Egor Zverev SI

SPIDES: Information-Flow Control for Browser Agents

Browser agents automate complex workflows by reading and acting on arbitrary page content, but this flexibility exposes them to prompt injection attacks and unintended data exfiltration. Recent work argues that LLM-driven browser agents erode traditional web security boundaries such as the Same-Origin Policy (SOP) by acting across origins with the user's authority and no built-in isolation. We argue that restoring SOP is neither sufficient (a same-origin public sink can leak…

Read at arXiv (research papers)

Committee to Protect Journalists

Pakistan media regulator orders new restrictions on TV coverage of attacks and other ‘unpleasant’ incidents

New York, October 16, 2026—The Committee to Protect Journalists urges Pakistan authorities to withdraw sweeping restrictions preventing television network broadcasts from airing live coverage of terrorist attacks and other vaguely defined “unpleasant” incidents. Journalists and media workers must be able to report breaking news and current affairs independently, free from fear of legal retaliation, and...

Read at Committee to Protect Journalists

UN News Human Rights

Ukraine: Civilian casualty rates among ‘deadliest’ in years, as energy attacks intensify

Civilian casualties in Ukraine remain at record levels, with intensified Russian attacks in September continuing a pattern of harm in 2026 far exceeding previous years, UN human rights monitors in Ukraine said on Friday.

Read at UN News Human Rights

arXiv (research papers) Farhan Zarif SI

Ignored, Not Refused: What Low Prompt-Injection Success Rates Hide in Small Tool-Using Agents

Tool-using agents read untrusted external content, which exposes them to indirect prompt injection (IPI), where hidden instructions hijack the agent's tool calls. Benchmarks measure IPI security by the attack success rate (ASR), which treats every failed attack as a successful defense. To test this assumption, we audit 33,000 trajectories from eleven open-weight agents (2-14B parameters) on InjecAgent and AgentDojo. A label-blind LLM judge shows that most failed attacks are…

Read at arXiv (research papers)

arXiv (research papers) Xianglin Yang SI

From Approval to Abuse: Privilege Escalation Attacks on Harness-Protected Coding Agents

Coding agents use execution harnesses to constrain the consequences of prompt injection by enforcing permission boundaries. These systems deterministically intercept any out-of-sandbox action and prompt the user for approval. To reduce approval fatigue, users can approve allow-rules proposed by the agent, after which any future action matching the rule is allowed without a prompt. In this work, we show that this mechanism introduces a new risk: untrusted context can…

Read at arXiv (research papers)

arXiv (research papers) L. Zhu SI

Stealthy Poisoning Attacks via Reused KV Cache of Reasoning

Modern large language model (LLM) systems reuse key-value (KV) caches to accelerate inference. Recent work has shown that reusing KV caches from reasoning traces can also improve task performance, similar to retrieval-augmented generation (RAG). We demonstrate that this form of KV cache reuse introduces new poisoning vulnerabilities. We propose R$^2$ECAP (Reused Reasoning-Cache Poisoning), a black-box attack that plants poisoned reasoning traces solely through interactions…

Read at arXiv (research papers)

The Guardian Yemen Guardian staff and agencies Geopolitics

Houthi missiles strike Yemen presidential palace, killing five

Attack was the first on Aden’s Al-Maashiq palace ⁠in the latest fighting between ​the Iran-aligned Houthis and Saudi Arabia Yemen’s Houthis fired missiles at the presidential palace complex in the southern city of Aden on Thursday, killing five people, the government said, as the Saudi-led coalition listed dozens of Houthi attacks on Saudi infrastructure in ⁠recent weeks. The attack was the first on Aden’s Al-Maashiq palace ⁠in the current conflict between ​the Iran-aligned…

Read at The Guardian Yemen

Journal articles (OpenAlex) Kira Kudar, Юлія Павлова, Ганна Склярова et al. · European Psychologist Geopolitics

MHPSS Interventions for War-Affected Residents of Ukraine

Abstract: Russia’s war against Ukraine (February 2022 – ongoing) has generated a large-scale humanitarian emergency characterized by widespread trauma, prolonged uncertainty, and mass displacement. In contrast to prior conflicts, it has been marked by nationwide attacks, urbanized warfare, digitally mediated trauma exposure, and societal fragmentation – factors that have created extensive mental health needs and prompted the rapid launch of diverse mental health and…

Read at Journal articles (OpenAlex)

The Guardian Yemen Patrick Wintour

Saudi Arabia strikes oil depots in Yemen and says missiles launched toward location of Saudi Aramco HQ

Civilians warned to leave target area near Sana’a before attacks as conflict between Riyadh and Houthi forces escalates Saudi Arabia has launched a series of strikes on a strategic oil depot on the outskirts of Yemen’s capital, Sana’a, while later on Tuesday it said it had intercepted missiles launched toward Dharan, location of the headquarters of the huge national energy company Saudi Aramco. The attacks on both sides were a fresh escalation of the conflict between Riyadh…

Read at The Guardian Yemen

IranWire

Iran Military Denied Ordering Tanker Attacks, Says Reformist Politician

Behzad Nabavi, a prominent Reformist politician, stated that Masoud Pezeshkian raised complaints with armed forces commanders following ...

Read at IranWire

UN News Humanitarian Aid

Ukraine: Residents killed and dozens injured in attacks on Kharkiv and Kyiv

Russian attacks in recent days on on Ukraine’s two largest cities have again killed and injured civilians, damaged homes and civilian infrastructure, the UN aid coordination office (OCHA) said on Tuesday.

Read at UN News Humanitarian Aid

The Guardian Yemen Patrick Wintour Diplomatic editor Geopolitics

Saudi Arabia further suspends flights after latest deadly Houthi attack on airport

Energy minister says ‘fear has no place in the Saudi lexicon’ as paramilitary group again breaches stretched defences Why are the Houthis attacking Saudi airports and how are the missiles getting through? Saudi Arabia has been forced to suspend all flights to and from its main international airport in Riyadh until next Saturday after a further round of Houthi missile attacks caused more damage and left one person dead. Some airlines, including Gulf Air, had already said they…

Read at The Guardian Yemen

The Guardian Yemen Jason Burke

Why are the Houthis attacking Saudi airports and how are the missiles getting through?

Attacks by Iran-backed group come amid counteroffensive by Yemeni government supported by Riyadh

Read at The Guardian Yemen

KabulNow Nazanin Mohseni

Two Men Killed in Separate Attacks in Southern and Eastern Afghanistan

KABUL, AFGHANISTAN - Local sources have reported the killings of two men by unidentified individuals in the southern province of Kandahar and eastern Nangarhar province. According to sources, a man was attacked with a knife and then beheaded on Sunday, October 11, in the second district of Kandahar city.

Read at KabulNow

The Guardian Yemen William Christou in Jerusalem

Riyadh airport hit again after deadly Houthi missile attack, Saudi authorities say

Unidentified projectile strikes King Khalid airport, killing one and injuring 11, as escalating attacks threaten to draw more countries into Yemen conflict Analysis: attack will force rethink of Trump strategy A projectile hit a passenger terminal at the airport in Riyadh on Sunday, the day after a deadly missile attack on the facility carried out by Yemen’s Iran-backed Houthi rebel group killed 13 people. An unidentified projectile hit terminal 4 at King Khalid…

Read at The Guardian Yemen

The Critic Josephine Bartosch Geopolitics

Why Conservatives should oppose the conversion practices ban

What seems tolerant and progressive actually attacks freedom and family life Source

Read at The Critic

arXiv (research papers) Michael Cardei SI

Only What You've Signed up For: Secure Workflows with Constrained Diffusion Agents

As agentic AI systems take on increasingly complex and consequential tasks, securing them against prompt injection becomes critical. Existing defenses often rely on detecting or reasoning about injected malicious instructions and can therefore remain vulnerable to adaptive attacks that optimize the injection itself. Diffusion language models (dLLMs), an emerging framework for language generation, offer a new opportunity for security enforcement: by iteratively refining their…

Read at arXiv (research papers)

arXiv (research papers) Josef A. Habdank SI

Can agents whose sole duty is to keep humans alive be hijacked to kill? Delayed multi-turn derived-action trap attacks in simulated high-stakes environments

We ask whether a tool-using agent whose sole duty is to keep humans alive can be induced, by delayed prompt injection, to kill. The keep-alive duty is in force from the first watch, with the attack arriving later, appended to otherwise truthful telemetry the operator is required to read. Experiments are based on a NASA-derived BioSim lunar habitat simulation, where the AI operator controls the life-support systems. The attacker cannot falsify sensors or operate equipment: it…

Read at arXiv (research papers)

The Guardian Cuba Shaun Walker

Why the mystery over Havana syndrome refuses to die

Dozens of CIA officers have been afflicted by debilitating symptoms over the past decade. Are they the result of ‘mass hysteria’? Or are they from attacks with an energy weapon and, if so, who is responsible? And has there been a cover-up? Shortly after 1am one night in April 2019, a CIA officer on a work trip to London was jolted awake in his hotel room by the most intense head pain he had ever experienced. His body was soaked with sweat and he felt like his eyes were…

Read at The Guardian Cuba

Journal articles (OpenAlex) Lena Maria Huber, Martin Haselmayer · European Journal of Political Research Geopolitics

Strategic alienation: The dynamics of group appeals in negative campaigning

Abstract This paper examines how political parties use social group appeals in negative campaigning. We argue that parties strategically target opponents with group-based attacks to portray them as failing key social groups. Using a novel dataset of Facebook and Twitter posts by parties in the UK (2016–2024), linked to voter perceptions of group representation from the British Election Study, we test whether such attacks are more likely when the sender party enjoys strong…

Read at Journal articles (OpenAlex)

arXiv (research papers) Luman Zhao SI

LTBD: Learnable Trust-Boundary Delimiters for Prompt Injection Defense

Large language models (LLMs) perform remarkably well on complex tasks, yet remain highly vulnerable to prompt injection attacks, where malicious instructions embedded in external data can override user intent. Existing defenses remain limited by model fine-tuning requirements, vulnerability to adaptive attacks, or reliance on brittle handcrafted prompts. We argue that a fundamental source of this vulnerability is the lack of an explicit representation of trust provenance. To…

Read at arXiv (research papers)

Older stories