Results for “Attack”

UN News Humanitarian Aid

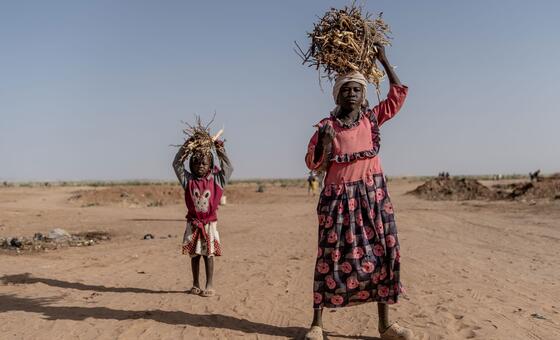
‘This is not about politics. This is about people’: UN warns of impact of deadly drone strikes in Sudan

Intensifying drone attacks on civilian infrastructure across Sudan are disrupting electricity, water and fuel supplies, putting lives at risk and hampering the delivery of humanitarian aid, the UN’s top official in the country has warned.

Read at UN News Humanitarian Aid

CISA advisories CISA Security

Subnet Solutions PowerSYSTEM Center

View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to execute unauthorized SQL commands and gain access to unauthorized resources. The following versions of Subnet Solutions PowerSYSTEM Center are affected: PowerSYSTEM Center 2020 <=5.29.x (CVE-2026-63017) PowerSYSTEM Center 2024 >=6.0.x|<=6.2.x (CVE-2026-63017, CVE-2026-63774) PowerSYSTEM Center 2026 >=7.0.x|<=7.1.x (CVE-2026-63017, CVE-2026-63774) CVSS Vendor Equipment v3 9 Subnet…

Read at CISA advisories

CISA advisories CISA Security

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-119977 WordPress Core Time-of-check Time-of-use (TOCTOU) Race Condition Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability…

Read at CISA advisories

Infosecurity Magazine Security

NCSC Chief Warns of Imminent AI Ransomware Threat to UK Critical Infrastructure

The UK’s cyber chief has warned that AI-powered malware is highly likely to feature in ransomware attacks targeting British critical infrastructure by 2028

Read at Infosecurity Magazine

arXiv (research papers) Yao Wang SI

Right Tool, Wrong Parameters: Defending LLM Agents Against Parameter Poisoning

Indirect Prompt Injection (IPI) poses a critical threat to LLM agents. Existing defenses largely focus on whether an injection induces a new tool invocation or unintended action. In this paper, we study a different attack surface, parameter poisoning, where the attacker preserves the intended action but manipulates one or more tool arguments, such as a recipient or other task-critical value. Such attacks are difficult to detect because no new action is introduced, while…

Read at arXiv (research papers)

arXiv (research papers) Jiamin Chang SI

The Devil is in the Context: Nine Dimensions of Prompt Injection Attacks

Prompt injection is usually discussed and evaluated as a single, homogeneous type of attack. However, vulnerabilities reported in real-world systems show that prompt injections vary widely. Moreover, the same instruction can be a prompt injection in one context and a legitimate request in another, depending on the user's intent and the system's policies. Ignoring this variation leaves gaps in how defenses are evaluated, and can give a false sense of security against…

Read at arXiv (research papers)

Asia Times Jinkyung Baek Geopolitics

How North Korea became the crypto heist king

Binance, the world’s largest cryptocurrency exchange, was the victim of a massive heist in late October. Approximately US$6.36 billion of funds were stolen within the space of 20 minutes in an attack that has been described as the largest of its kind in history. The source of the attack has not yet been officially confirmed.

Read at Asia Times

SecurityWeek Eduard Kovacs Security

Over 100 European Stores Hit as Supermarket Fridge Attacks Return

Attackers again tampered with internet-exposed refrigeration controllers, this time at stores in Belgium, Sweden, Ireland and beyond.

Read at SecurityWeek

arXiv (research papers) Gia Phong Tran SI

From Guidelines to Practice: Defining Requirements for AI Red-Teaming Tools

Artificial Intelligence (AI) has seen significant developments and increased usage in recent years. AI benefits various tasks, automates decision-making, and enhances efficiency. However, AI also introduces additional attack surfaces for threat actors to perform attacks like prompt injection and jailbreaking, making security a great concern. AI security testing aims to imitate adversarial attacks or malicious inputs via manual testing or with the assistance of tools. Thus…

Read at arXiv (research papers)

9to5Mac Marcus Mendes Security

Apple recently notified users in 99 countries of potential mercenary spyware attacks

Apple reportedly sent notifications to users in 99 countries warning of potential mercenary spyware attacks, as German authorities investigate reports that lawmakers and government officials may have been targeted. Here are the details.

Read at 9to5Mac

Amnesty International Amnesty International

Mali: Still no accountability six months after abduction of pro-democracy politician Mountaga Tall and his son

Malian authorities must urgently disclose the fate and whereabouts of lawyer and pro-democracy politician Mountaga Tall and his son Cheick Mamadou Tall, Amnesty International said six months after their abductions. On the night of 3 May 2026, just days after a series of attacks by armed groups across Mali, Mountaga Tall, leader of the National

Read at Amnesty International

Journal articles (OpenAlex) Ruixi He · Frontiers in Computing and Intelligent Systems

Machine Learning-Based IoT Intrusion Detection: A Survey and Performance Comparison

As IoT devices multiply, the cyber attack surface has widened just as fast, and with it the need for intrusion detection systems (IDS) that are efficient, dependable, and protective of user privacy. This paper organizes IoT IDS methods into a taxonomy built around training architecture and reviews them under two main paradigms, misuse detection and anomaly detection, with the focus on centralized traditional machine learning and deep learning. Experiments on several public…

Read at Journal articles (OpenAlex)

Journal articles (OpenAlex) Bakhtawar Saeed, Sobia Arshad, Sanay Muhammad Umar Saeed et al. · Applied Sciences

Multi-Agent Agentic AI and Federated Learning for Attack Detection in Sustainable IoT

The Internet of Things (IoT) comprises a vast number of digitally networked devices. Machine learning (ML), deep learning (DL), and federated learning (FL), all subfields of artificial intelligence (AI), have recently been investigated as cybersecurity solutions for protecting these networked devices from intrusions and cyberattacks. However, existing ML and DL techniques for Sustainable IoT data carry significant privacy implications. Because of its inherent suitability for…

Read at Journal articles (OpenAlex)

Journal articles (OpenAlex) Ghita Hana, Mourad Hana, Abdelmjid Saka · Electronics

Artificial Intelligence-Based Intrusion Detection Systems for Smart University Ecosystems: A Survey of IoT Security, Cloud Learning Platforms, and Connected Campus Services

Smart Universities increasingly rely on connected learning platforms, smart classrooms, Internet of Things (IoT) devices, cloud services, and digital administrative systems. This integration expands the attack surface and creates security requirements involving educational data, heterogeneous infrastructure, and the continuous availability of academic services. This survey examines AI-based intrusion detection through three complementary perspectives: campus-specific threats…

Read at Journal articles (OpenAlex)

Journal articles (OpenAlex) Hari Krishna Parvatham, Shiyu Liu, Yiannis G. Ampatzidis et al. · Smart Agricultural Technology

Adversarial robustness of vision-based perception in precision agriculture: Attacks, defenses, and a case study on the Agrosense v2 platform

AI-enabled vision-based perception models are increasingly used in precision agriculture for tasks such as fruit detection, trunk detection, and autonomous navigation. As these models move into field deployment, their errors no longer stay confined to the image: they propagate into the counts, maps, and yield estimates that downstream automation depends on, making adversarial robustness a security concern. Yet this robustness remains underexplored in orchard settings. Using…

Read at Journal articles (OpenAlex)

Journal articles (OpenAlex) Stuart James Turnbull-Dugarte, Peter Luca Versteegen, Daniel Devine et al. · Political Science Research and Methods Geopolitics

Partisan responsiveness in real time: causal evidence from Trump’s military attack on Iran

Abstract Elite cues signal citizens how to interpret political events through a partisan lens. Do these effects occur in real time? We exploit President Trump’s unexpected announcement of US military strikes against Iran during a nationally representative survey to estimate the causal effect of elite cues on public opinion. Leveraging minute-level variation in exposure, we find that partisan divergence emerges almost immediately: support for military intervention increases…

Read at Journal articles (OpenAlex)

Journal articles (OpenAlex) Junghun Yuk, KyungTae Lim, Hyeong-Won Seo et al. · Scientific Reports Security

A document classification benchmark dataset on cybersecurity policy domain

Document classification in the cybersecurity domain is essential for the efficient identification of emerging threats, technologies, and policy trends. However, existing datasets and language models are biased toward technical, attack-oriented texts such as CTI reports and CVE descriptions, and there is a critical lack of data for the cybersecurity policy domain. To address this gap, we introduce the first benchmark dataset for cybersecurity policy document classification…

Read at Journal articles (OpenAlex)

Journal articles (OpenAlex) Advait Gourkhede, Ashmit Cajla, Gurpal Singh Chhabra et al. · International Journal of Computational Intelligence Systems Security

CAMRA: Cross-Architecture Multimodal Reinforcement Learning with Federated Adaptation for IoT Malware Detection and Classification

Abstract The domain of Internet of Things (IoT) has been rapidly developing, consequently expanding the attack surface for malware that exploits vulnerabilities across various hardware architectures and evades conventional static detection techniques. Past frameworks for IoT malware detection and classification often rely on a single data modality or are designed for a specific device architecture, which limits their ability to detect and classify malware in heterogeneous…

Read at Journal articles (OpenAlex)

Dark Reading Jai Vijayan Security

One Compromised Laptop, Billions Lost: The Binance Attack-Path Warning

The record theft shows how weak system separation, inadequate controls, and untested attack possibilities can turn one breach into systemic loss.

Read at Dark Reading

BleepingComputer Bill Toulas Security

Chinese hackers use ARTEX AI in automated attacks against 200 orgs

Chinese hackers used ARTEX, an open-source, multi-agent AI penetration-testing framework, in attacks against more than 200 organizations across 14 countries.

Read at BleepingComputer

GNET (Global Network on Extremism and Technology) Francesco Marone Geopolitics

The Centocelle School Attack and the Consolidation of Nihilistic Violent Extremism in Italy

On Friday, 18 September 2026, during the first week of the new school year, a 13-year-old Italian student entered a classroom at a middle school in Rome’s Centocelle district, wearing a helmet with a smartphone attached via an improvised harness. He sprayed an irritant at his teacher and stabbed her three times under the armpit with a 20-centimetre diving knife,

Read at GNET (Global Network on Extremism and Technology)

Amu TV Siyar Sirat Geopolitics

IFJ calls for prosecution of those behind journalists’ killings

“Every day, journalists are targeted, intimidated, attacked and murdered for holding those in power to account,” IFJ President Zuliana Lainez said.

Read at Amu TV

Asia Times Julia Conley Geopolitics

As Trump renews Iran nuke threats, Dems ponder blocking war funds

As President Donald Trump and Iranian officials traded threats over the weekend, and with the Trump administration reportedly considering renewed attacks against an underground complex it claims is a nuclear site – which Iran denies – critics of the US-Israeli war on the Middle Eastern country called on Democrats to take decisive action to end

Read at Asia Times

Dark Reading Andrew Grotto Security

Microsoft's AI Risk Report Misses This Key Detail

The latest "Digital Defense Report" identifies government agencies as prime targets for AI attacks, but it doesn't mention that they are broadly being targeted through Microsoft bugs.

Read at Dark Reading

The Register Security Security

Nuclear threats and street brawls: Russia, Ukraine report attacks on their emergency alert apps

Within minutes of a ceasefire lifting in Kherson, Ukraine’s citizens were pummelled with threatening notifications

Read at The Register Security

Dark Reading Elizabeth Montalbano Security

PapRAT Cyber-Espionage Campaign Leaves a 'Bitter' Taste in South Asia

Organizations in the region face growing cyberattacks from the known India-linked threat group, which leverages legitimate Windows functionality in three distinct attack chains.

Read at Dark Reading

Article 19 natashas Geopolitics

International: End impunity for attacks on journalists

As voters have made their voices heard in four crucial elections in Brazil, Israel, Serbia, and the United States, we have witnessed the power of authoritarian agendas playing out in the public space. While this is far from new, what is more alarming than ever is how the silencing of journalists and the undermining of

Read at Article 19

SecurityWeek Ionut Arghire Security

Malicious Claude Code Extension Served in Cursor Supply Chain Attack

The extension performed host reconnaissance and attempted to create a reverse SSH tunnel.

Read at SecurityWeek

SecurityWeek Ionut Arghire Security

Chainalysis Discloses Data Breach Following AI-Driven Cyberattack

The attackers used offensive agentic techniques to access the company’s systems and internal tools.

Read at SecurityWeek

Older stories