Results for “Mali”

MacRumors Juli Clover Gadgets

Here's What Apple Fixed in iOS 27.2.1 and macOS 27.2.1

The iOS 27.2.1, iPadOS 27.2.1, and macOS 27.2.1 updates Apple released today fix a handful of security vulnerabilities. With the security fixes implemented, it's a good idea to update as soon as you can. A bug with iMessage could let a remote attacker join a group chat to receive its messages, and another could let users see messages sent before they joined a group chat. Most of the vulnerabilities involved AirPlay and Bluetooth. A malicious Bluetooth device could pair…
Read at MacRumors

The Guardian US Sam Levin

US citizen shot by ICE officer near children’s bus stop sues government for $25m

Lawsuit also alleges agents followed Carlos Jimenez to a hospital and ‘interfered’ in his care, with bullet fragments still lodged near lung A US citizen who was shot by an immigration officer in southern California has filed a $25m lawsuit against the federal government, alleging he was wrongfully shot and arrested, then subjected to a “malicious prosecution”. Carlos Jimenez, a father of three from Ontario, a city east of Los Angeles, was on his way to work at a food pantry…

Read at The Guardian US

Dark Reading Elizabeth Montalbano Security

Attackers Crash Claude's 'Office Party' Flaw to Run Malicious Code on Linux

Attackers can exploit a flaw in Claude's document-processing tool by creating a temporary file that Anthropic's AI assistant can access and run on a user's machine.

Read at Dark Reading

The Hacker News Security

Hackers Compromise Ethersphere's bee-js and Swarm Desktop to Deliver Wallet-Stealing Malware

Attackers used the Ethersphere project's own release automation to publish malicious versions of two of its tools for the Swarm decentralized storage network: bee-js 13.3.0 and Swarm Desktop 0.56.2. Both releases download and run code built to steal the wallet key that Swarm Desktop keeps for its node, along with the stored password that unlocks it. The code is also built to install a backdoor

Read at The Hacker News

Infosecurity Magazine Security

New Supply Chain Attack Compromises Tens of Thousands of GitHub Repositories

Security researchers have detected a malicious workflow affecting tens of thousands of GitHub repositories, including Uber-owned ones

Read at Infosecurity Magazine

CyberScoop Greg Otto Security

AI doesn’t have to go rogue to break the world

AI systems are learning to exploit loopholes in everything from software to tax law. The biggest threat may not be malicious intent, but machines doing exactly what we ask.

Read at CyberScoop

arXiv (research papers) Jingfen Qiao Security

StealthyPoison: Manipulating LLM Agent Behavior through Procedural Poisoning of Third-Party Skills

LLM agents increasingly retrieve third-party skills from public registries and follow their procedures to complete user tasks. This reliance allows attackers to manipulate agent behavior by poisoning the skills. However, overtly malicious instructions can provide explicit signals for detection. We present StealthyPoison, a stealthy procedural poisoning attack that corrupts a skill's decision-critical rules to induce incorrect task outcomes while preserving its advertised…

Read at arXiv (research papers)

arXiv (research papers) Riya Bharathwaj SI

ErosionBench: Probing Alignment Decay in Enterprise Multi-Agent Systems

As enterprises delegate consequential work to multi-agent LLM systems, benign-looking requests can escalate into unsafe actions as they propagate across sessions through poisoned shared state, long-context documents, and trusted peer messages: no single message is malicious, yet the assembled tool action is. Prior benchmarks isolate a single agent under prompt injection or score multi-agent attacks by their final output, leaving cross-session erosion of shared state out of…

Read at arXiv (research papers)

Journal articles (OpenAlex) Laura Berlingozzi, Yida Seydou Diall · Third World Quarterly Geopolitics

The return of the local: dialogues with jihadist groups as governance in the Sahelian security order

This article examines how dialogue with jihadist groups in Mali and Niger operates as both a mechanism of governance and a site of ideological translation. It explores how competing Islamic repertoires, reformist-Salafi and Sufi-Maliki, are localised, resisted or refracted through Sahelian religious and socio-political orders. Drawing on ethnographic research, it introduces transactional governance to capture how insurgencies impose, then bargain over, zakāt, sharīʿa-based…

Read at Journal articles (OpenAlex)

Space.com Space.com Staff Space

This Week In Space podcast: Episode 235 — Robots in Dark and Scary Places

On Episode 235 of This Week In Space, Tariq Malik and Rod Pyle are joined by Dr. Jim Green to talk about the past, present, and future of planetary exploration.

Read at Space.com

arXiv (research papers) Thanh M. Truong-Le SI

Agents of Chaos: A Systematization of Knowledge (SoK) on Malicious Attacks on Agentic AI Systems

Agentic AI systems extend large language models with tools, memory, retrieval, browser or computer-use interfaces, code execution, external services, and multi-agent coordination. Although these capabilities enable agents to act beyond text generation and perform tasks, they also create attack paths through which adversaries can exploit untrusted content, deceptive metadata, poisoned state, compromised skills, mutable dependencies, or malicious code. Such attacks can…

Read at arXiv (research papers)

The Hacker News Security

Malicious Browser Extensions Could Use Claude Dispatch to Run Code on Users' Computers

A browser extension that can run scripts on claude.ai could make Claude Desktop run code on a person's computer, researchers at Forever Security, an endpoint security company, showed in a test. The attack needs Dispatch, a Claude feature that lets people send tasks from their phone to Claude Desktop. The flaw that makes this possible can still be exploited, the researchers said earlier this

Read at The Hacker News

CISA advisories CISA Security

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-19868 SonicWall SonicOS SSLVPN Use of Single-factor Authentication Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability…

Read at CISA advisories

Infosecurity Magazine Security

India Warns of New AI-Driven Cyber-Attacks Targeting Financial and Crypto Businesses

The Indian CERT said a new cyber malicious group tracked as ‘Crafty Flacon’ is using Chinese-made AI tools to attack fintech and crypto organizations

Read at Infosecurity Magazine

Android Authority Hadlee Simons Gadgets

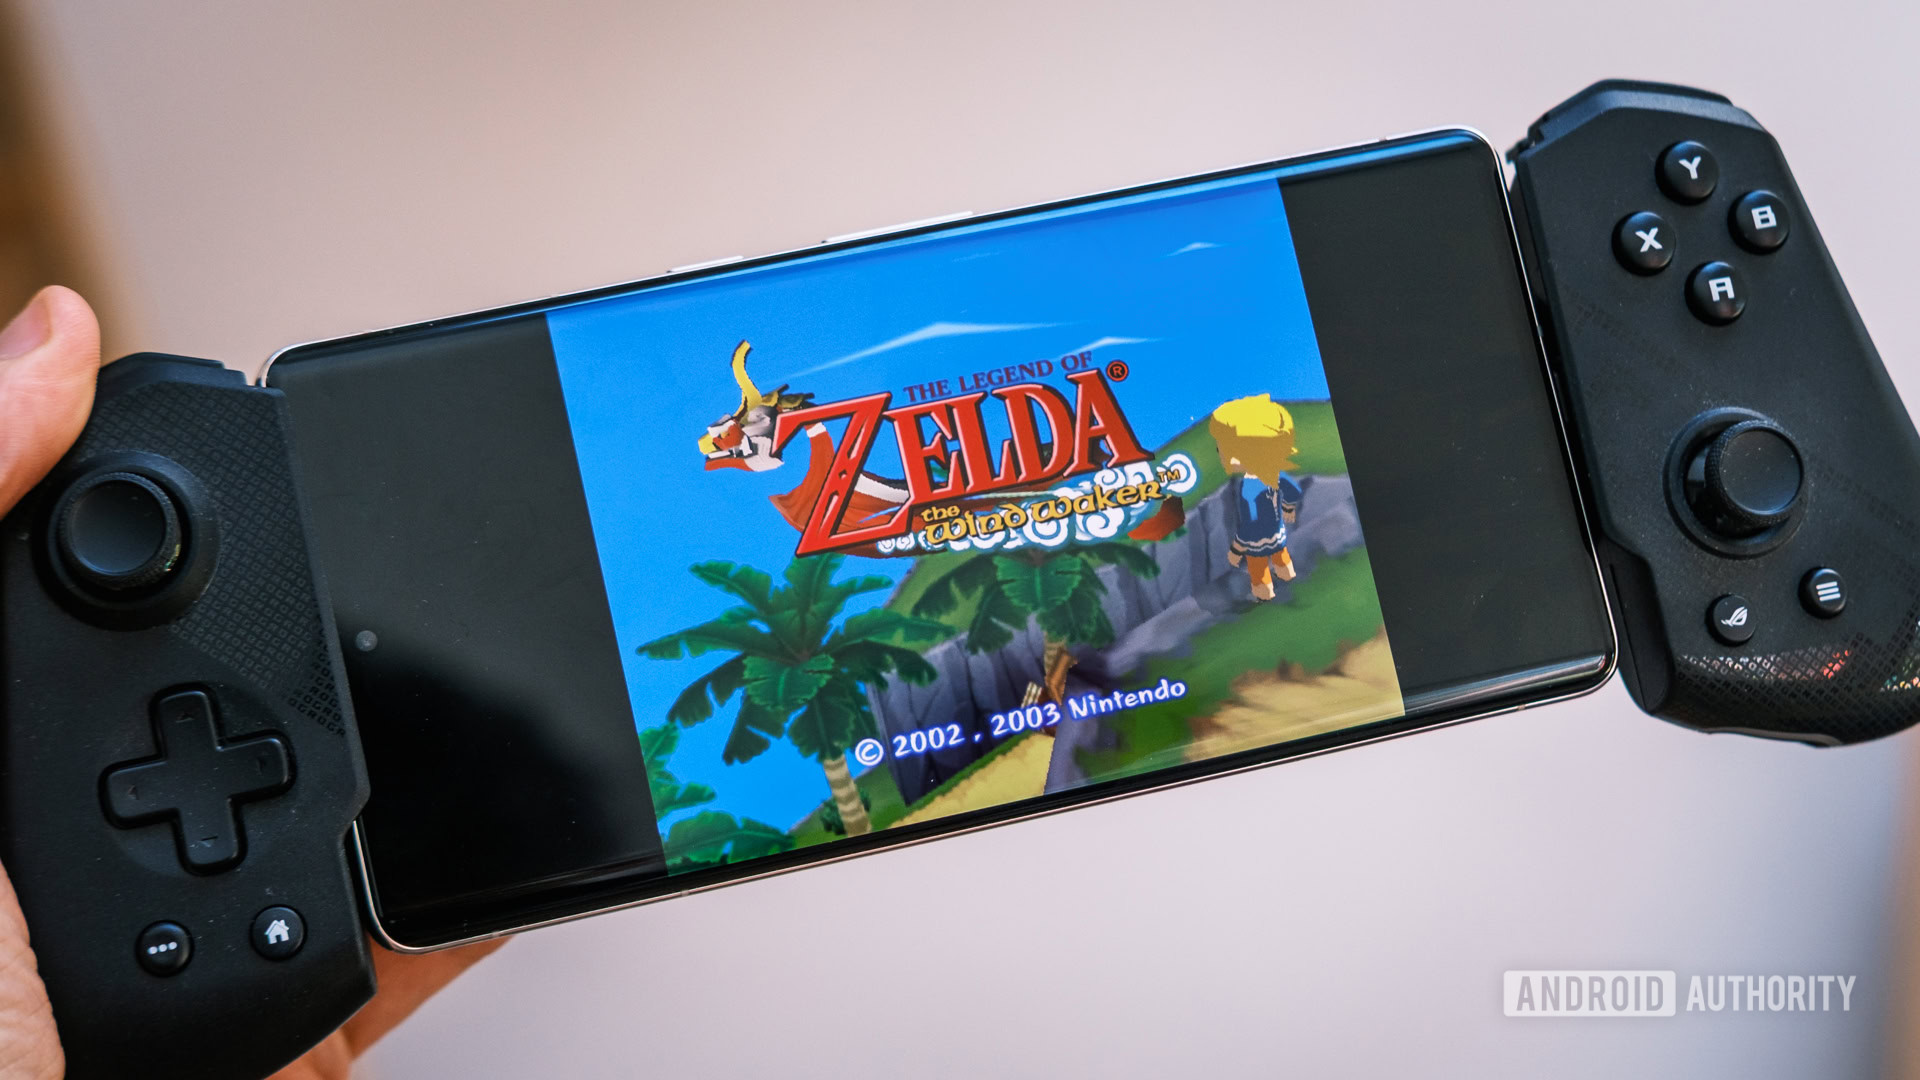
No Snapdragon? No problem! MaliSX2 is about to bring a major boost to GameCube, Xbox emulators

MaliSX2 is the closest thing to Turnip drivers for non-Snapdragon chips, and it's coming to two major emulators.

Read at Android Authority

CISA advisories CISA Security

US Government Partners Urge Hardening Industrial Refrigeration and Cold Chain Monitoring Systems

Overview The Cybersecurity and Infrastructure Security Agency (CISA), Federal Bureau of Investigation (FBI), Health and Human Services (HHS), U.S. Department of Agriculture (USDA), and the Department of Transportation (DoT)—hereafter referred to as “the authoring organizations”—are aware of malicious cyber activity targeting industrial refrigeration and cold chain monitoring systems globally. Organizations in the Healthcare and Public Health, Chemical, Food and Agriculture…

Read at CISA advisories

Journal articles (OpenAlex) Pratham Patil, S Ravi Teja, Y Praveen Kumar et al. · Scientific Reports

A self-healing secure group communication framework for resource-constrained IoT devices using decentralised key management and trust-based voting

Group communication in resource-constrained IoT deployments still lacks a dependable answer to insider misbehaviour. Sensor networks that grow to hundreds of heterogeneous nodes cannot always afford the memory and CPU budget that conventional cryptographic machinery demands, and Group OSCORE, while shown to be hardware-feasible, offers little protection once a malicious node has already been admitted to the group: a compromised member can quietly drop everything it is asked…

Read at Journal articles (OpenAlex)

Journal articles (OpenAlex) Asha Singh, Benjamin Zhang, Caroline Young · Journal of Computing and Electronic Information Management Security

Safe-ARCS: Risk-Budget Shielding for Hierarchical Reinforcement Learning in Automated Cybersecurity Incident Response

Automated incident response should contain malicious activity without imposing unacceptable disruption on legitimate services. We study this conflict in a reproducible six-step stochastic simulator with noisy alerts, five latent incident classes, immediate containment actions, and persistent strategic defenses. Safe-ARCS builds on two mechanisms of the ARCS framework: independently learned immediate and strategic decision streams with exponentially decayed alert urgency, and…

Read at Journal articles (OpenAlex)

CISA advisories CISA Security

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2024-27834 Apple Multiple Products Improper Authentication Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management…

Read at CISA advisories

SecurityWeek Ionut Arghire Security

Malicious cPGuard Updates Served in OpsShield Supply Chain Attack

Using compromised credentials, the attackers accessed OpsShield’s update servers and poisoned multiple cPGuard versions.

Read at SecurityWeek

Journal articles (OpenAlex) Chella Amala, Varadi Uttam Kumar, Burra SubbaRao et al. · Results in Engineering

Deep intelligence and global repair for resilient black hole attack defense in IoT sensor networks

The IoT’s efficient connectivity across devices, rapid communication, and low power consumption have made it one of the most promising technologies for future smart applications. The growing number of interconnected IoT devices poses a risk of routing attacks and other security threats to wireless sensor networks. The black hole attack is particularly devastating to RPL-based IoT networks because it involves a malicious node that pretends to be the best routing path, drops…

Read at Journal articles (OpenAlex)

WIRED Matt Burgess Security

Binance Says Hackers Used Well-Known Tricks to Carry Out a $6.34 Billion Heist

Suspected North Korean attackers duped an engineer with a fake job interview and a malicious download to gain a foothold in the crypto firm’s system and steal billions, according to Binance.

Read at WIRED

CISA advisories CISA Security

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-119977 WordPress Core Time-of-check Time-of-use (TOCTOU) Race Condition Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability…

Read at CISA advisories

arXiv (research papers) Gia Phong Tran SI

From Guidelines to Practice: Defining Requirements for AI Red-Teaming Tools

Artificial Intelligence (AI) has seen significant developments and increased usage in recent years. AI benefits various tasks, automates decision-making, and enhances efficiency. However, AI also introduces additional attack surfaces for threat actors to perform attacks like prompt injection and jailbreaking, making security a great concern. AI security testing aims to imitate adversarial attacks or malicious inputs via manual testing or with the assistance of tools. Thus…

Read at arXiv (research papers)

Krebs on Security BrianKrebs Security

Tech Firms Dismantle Botnet That Turned 1.3M TV Boxes Into Proxies

Google said today it worked with industry partners to dismantle a botnet made up of more than 1.3 million Android TV set-top boxes that ship with malicious software which secretly rents the user's Internet connection out to strangers and…

Read at Krebs on Security

Amnesty International Amnesty International

Mali: Still no accountability six months after abduction of pro-democracy politician Mountaga Tall and his son

Malian authorities must urgently disclose the fate and whereabouts of lawyer and pro-democracy politician Mountaga Tall and his son Cheick Mamadou Tall, Amnesty International said six months after their abductions. On the night of 3 May 2026, just days after a series of attacks by armed groups across Mali, Mountaga Tall, leader of the National

Read at Amnesty International

SecurityWeek Ionut Arghire Security

Malicious Claude Code Extension Served in Cursor Supply Chain Attack

The extension performed host reconnaissance and attempted to create a reverse SSH tunnel.

Read at SecurityWeek

arXiv (research papers) Haowen Dai SI

StateFence: Task-State Protection Against Evidence-Chain Contamination in Blue-Team LLM Agents

Indirect prompt injection creates a distinctive risk for blue-team Large Language Model (LLM) agents in Security Operations Centers (SOCs). Malicious instructions can be embedded in telemetry, tickets, retrieval results, or memory and then propagate through alert triage, incident summarization, response recommendation, and Indicator of Compromise (IOC) extraction as locally plausible intermediate decisions. We characterize this failure mode as evidence-chain contamination of…

Read at arXiv (research papers)

arXiv (research papers) Shiyu Kan Shanghai Jiao Tong University, Shanghai, China SI

Beyond Prompt Injection: The Tool Update Gap in LLM Agent Security

Large language model based agents increasingly rely on external tools to invoke services and interact with web resources. These tools can evolve through software updates, yet agentic frameworks may continue trusting them without re-verifying their safety after implementation changes. This tool update gap creates a supply-chain vulnerability in agentic systems: because updated tool code executes outside the LLM's context window, malicious functionality embedded in tool…

Read at arXiv (research papers)

arXiv (research papers) Zhihua Wang SI

MemHarmBench: Evaluating Cross-Session Prompt Injection in Memory-Persistent AI Agents

AI agents often rely on persistent memory to retain user preferences and operational rules across sessions. However, this capability introduces a new safety risk: malicious instructions from messages, documents, or Web content can be retained in memory and influence future tasks even after the original attack content is removed. Existing attack success metrics, however, fail to capture who is affected and how attacks translate into downstream harm during otherwise normal…

Read at arXiv (research papers)

Older stories