ArcticRAT Cybercrime Gang Profiles Victim Finances With AI
The Android malware has expanded from focusing on crypto theft to full device control, and the attackers have added advanced analysis of stolen information.
The Android malware has expanded from focusing on crypto theft to full device control, and the attackers have added advanced analysis of stolen information.
Osaka, Japan's third-largest city, told its 2.8 million residents to be wary of suspicious emails purporting to come from the local government.
The company says a bad update—not a cyberattack or AI—caused its servers around the world to crash.
Microsoft says a widespread outage they are still working on resolving was not caused by a cyberattack but by "a network capacity upgrade." NBC News' Christine Romans and TechRadar's Lance Ulanoff discuss how the outage is affecting businesses across the world.
Microsoft on Friday apologised for a global outage that disrupted public services and businesses around the world, as it reported a “broad recovery” for Outlook email and other services. The company ruled out any malicious “cyber or AI” activity as the cause of the outage, which affected several Microsoft products and disrupted healthcare services, delayed corporate earnings reports and left schools struggling to communicate. “We are deeply sorry for the disruption this…
Monday, August 24 Session 1 – The SmallSat Ecosystem: Challenges and Emerging Solutions Examine the key challenges facing the SmallSat community, including technology gaps, supply chain risks, cybersecurity, and integration complexities. Attendees will learn about emerging solutions that are helping to build a more resilient and scalable ecosystem.Session Moderator: Jose Nunez, NASA Kennedy Space Center BryceTech’s
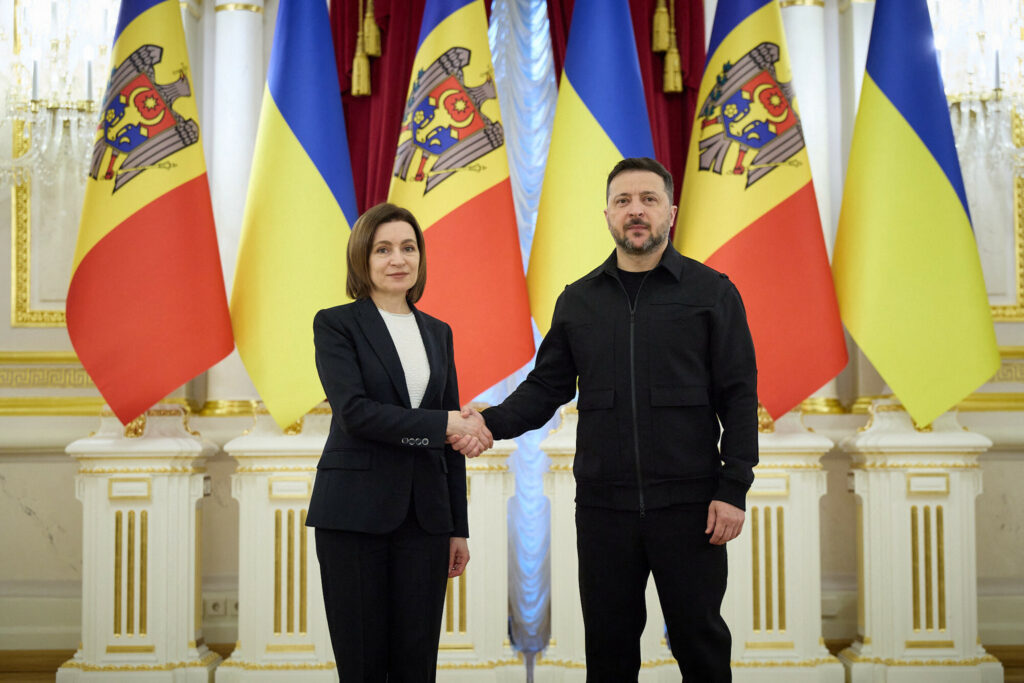
Moldova ratifies an agreement covering defense technology, cybersecurity, and airspace protection as Russian attacks on neighboring Ukraine increasingly spill across its borders.
In a statement to Recorded Future News, a spokesperson said an investigation into the attack confirmed the stolen data but declined to say what information was obtained by the threat actors.
"Companies at the forefront of supporting Ukraine are being targeted precisely because our work is critically relevant to customers' security," the company said in its official statement.
OpenAI has launched two security products under its Daybreak brand. The article OpenAI enters the cybersecurity market with two Daybreak products appeared first on The Decoder.
Proofpoint’s Selena Larson notes that threat actors’ reliance on AI has led to lots of mistakes being made, with little evidence of increased sophistication
In early October, a wave of cyberattacks, leading to fraud losses, hit several Nigerian banks and financial institutions, potentially costing billions of naira in customer funds, according to several sources with direct knowledge of the matter.
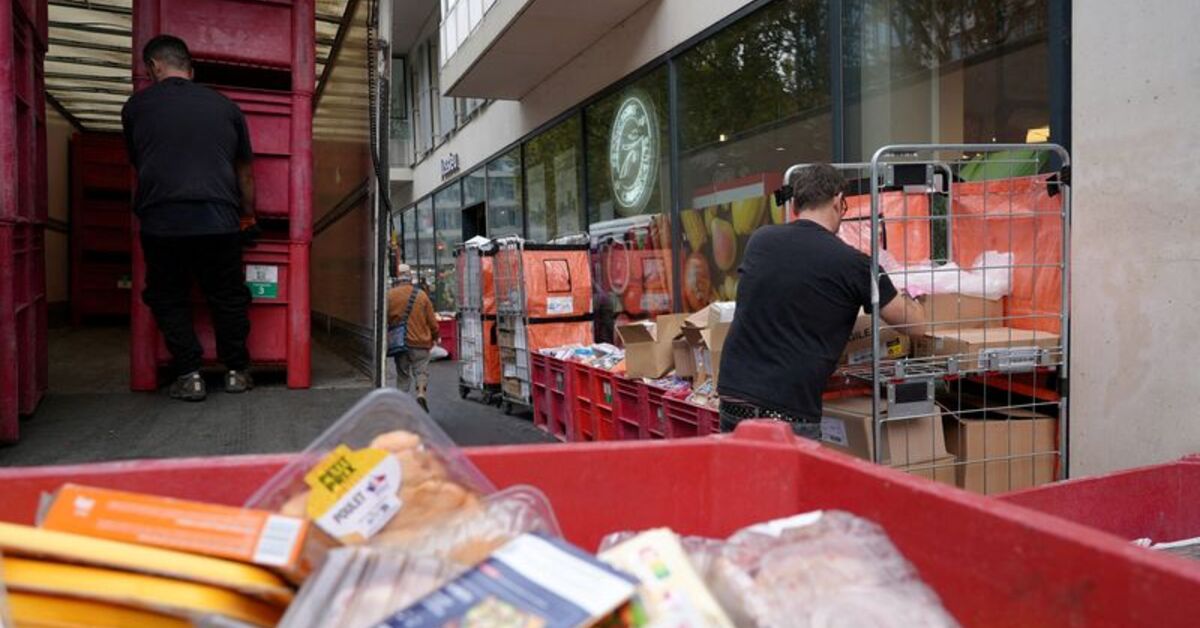
BRUSSELS, Nov 13 (Reuters) - Belgian Interior Minister Bernard Quintin said Iran was "very likely" behind the recent refrigerator cyberattacks on European shops, while Foreign Minister Maxime Prévot said there was insufficient evidence to draw conclusions. "There was enough evidence from our security services for me to say that Iran is very likely behind the cyberattacks we have seen targeting our shops," Quintin told Belgian broadcaster VRT NWS Thursday evening. Quintin…
The web scraping company says an intruder accessed customer accounts and obtained personal information or stored data.
This essay is adapted from a keynote speech delivered at the DEF CON 34 conference in Las Vegas on August 7, 2026. The essay originally appeared in CyberScoop. I want to talk about AI hacking. There are three aspects: people hacking AI systems, people using AI to hack other systems, and AIs hacking systems on their own, not even maliciously. The last two matter more than the first. The third is the weirdest and potentially the most destabilizing. I started writing about this…
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-114713 UnrealIRCd Improper Neutralization of Delimiters Vulnerability CVE-2026-123039 Check Point Multiple Products Incorrect Permission Assignment for Critical Resource Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise. Binding…
A newly identified spying group used hacked equipment inside Asian mobile operators to intercept the calls and texts of selected people, mostly in Taiwan. Enea, a telecom and cybersecurity software company based in Stockholm, found the group's attack sources in at least six Asian countries and named it SilentAir this week. It assessed with high confidence that SilentAir is a state-level actor,
Tesla’s unpredictable CEO is ready to move on from the company’s most controversial vehicle, but owners aren’t about to let him off the hook for what they see as a poor decision.
While Microsoft resolves the global M365 and Outlook outage, cybersecurity teams remain on high alert as cybercriminals prepare to exploit the chaos
Microsoft has said the outage was not caused by a cyber-security incident, but efforts to fix the issues have so far been largely unsuccessful.
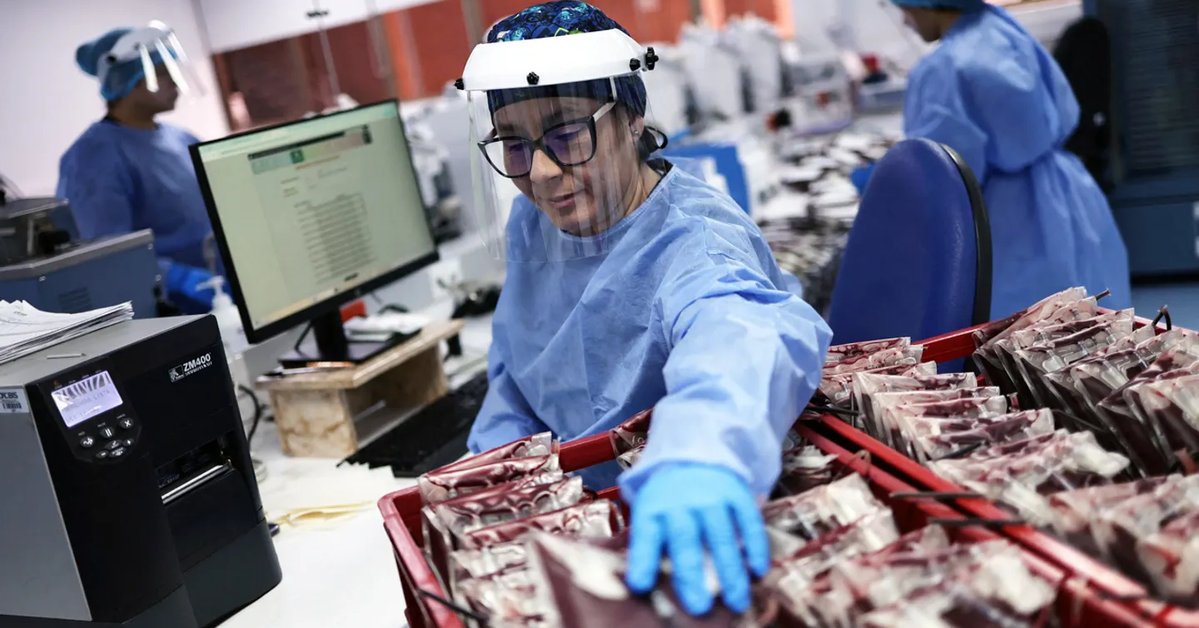
France is investigating a cyberattack on freezers that store blood for hospital patients, its national blood service told Iran International, weeks after Paris blamed Iran’s Revolutionary Guards for hacking the freezers of hundreds of French supermarkets.
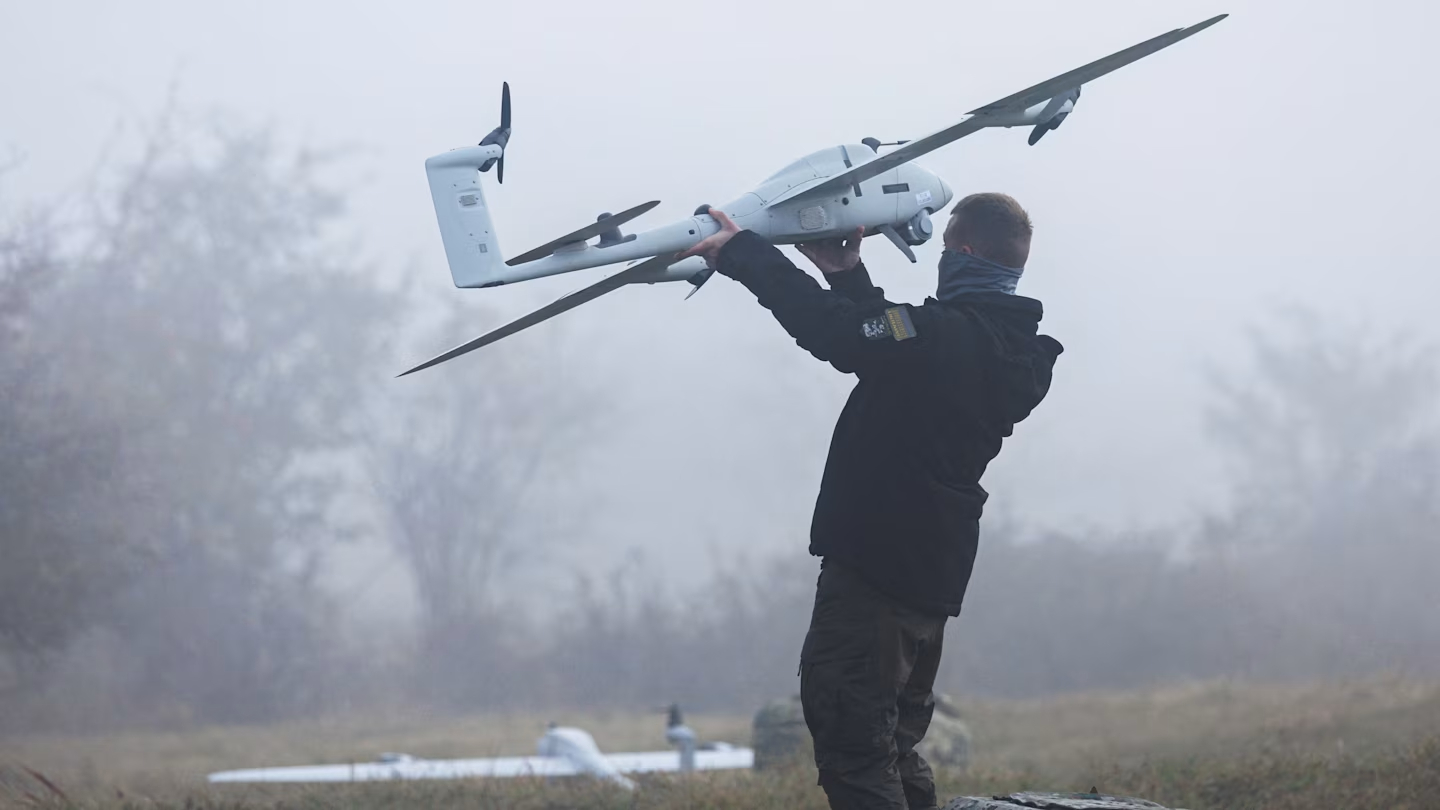
Quantum Systems, a German defence company supplying reconnaissance drones to Ukraine, has confirmed a cyberattack detected in October. Germany's armed forces have suspended use of its drones as a precaution.
Hasn't completely ruled out cyberattack as cause of incident that's damaged Exchange Online and services that rely on it
Hasn't completely ruled out cyberattack as cause of incident that's damaged Exchange Online and services that rely on it
Hasn't completely ruled out cyberattack as cause of incident that's damaged Exchange Online and services that rely on it
Hasn't completely ruled out cyberattack as cause of incident that's damaged Exchange Online and services that rely on it
Many cyber-physical systems (CPS) are multi-mode: they switch between operating modes with different tasksets and timing parameters in response to physical events or user activity. We show that these mode changes create a timing side channel: by altering the interference experienced by co-running tasks, they let an unprivileged co-resident observer infer sensitive events, such as a homeowner's arrival or a vehicle's route, from its own execution timing and, on multicore…
Providing images of one’s face to online platforms can increase the risk of biometric data being collected and exploited to facilitate cyberattacks.
British organizations have reported a record number of cyber incidents to the country’s data protection regulator this year, as cybersecurity firms blame data extortion and artificial intelligence for a surge in attacks.
Cybercriminals using agentic pen-testing tools is a proverbial genie out of the bottle at this point, so enterprises need to get a defense plan in place right away.