Results for “cyber”

South China Morning Post Danny Mok Geopolitics

Hong Kong housewife loses HK$1.3 million in online hotel booking job scam

A housewife in Hong Kong lost HK$1.3 million (US$166,670) after falling victim to an online job scam that lured her with the promise of lucrative commissions for completing bogus hotel booking tasks. Hong Kong police also disclosed on their CyberDefender page on Monday that more than 20 online employment scam cases were reported in the past week, involving total losses exceeding HK$3.2 million. Police warned the public to remain vigilant and be wary of online job offers that…
Read at South China Morning Post

TechCabal Frank Eleanya Startups

Cyberattack alert: What Nigerian banks must tell customers

Nigerian banks must report cyber incidents to regulators, but that does not always mean customers are informed. As cyberattacks expose financial institutions to growing risks, the challenge is balancing transparency, customer protection and public confidence.

Read at TechCabal

South China Morning Post Kolette Lim Geopolitics

Why Singapore’s wave of data breaches signals ‘new era’ of cyber threats

When Singaporean retiree Steven Wong started getting calls from strangers addressing him by his full name, he grew uneasy about how much of his personal information might be out there. The 71-year-old now avoids using his credit card for online purchases and bargains that seem too good to be true. He also ignores unsolicited messages. “You never know what they can do or who they may target,” he said. Singapore has been hit by a wave of data breaches across the aviation…

Read at South China Morning Post

SecurityWeek Eduard Kovacs Security

Microsoft Rules Out Cyberattack in Outage, Warns of Phishing Campaign

Phishing emails posing as Microsoft 365 service notices referenced the real outage incident and threatened to delete held messages.

Read at SecurityWeek

The Guardian UK Politics Peter Walker Senior political correspondent Geopolitics

UK exposed to polycrisis of threats amid government ‘complacency’

Lords report calls for urgent new approach to resilience planning in face of cyber-attacks, sabotage and climate crisis Ministers are complacent in the face of fast-changing and increasingly interconnected threats to the UK, and must act quickly to increase national resilience to possibly very major crises, a parliamentary report has found. While Labour recently launched a “Be Ready” campaign, advising households to have stocks of food and water, most of the public are…

Read at The Guardian UK Politics

arXiv (research papers) Rathan Appana Security

Experience: ENTRAP - An IaC Enterprise Cyber Range for Reproducible Security Assessment and Dataset Generation

An enterprise breach causes most of its damage after the perimeter is crossed. Once an attacker gains a foothold, they can move laterally to other hosts, take over the trusted services of the network, and encrypt the backups needed for recovery. Defenders, on the other hand, need to study this post-compromise stage, but they cannot rehearse it on a production enterprise network. Building such an enterprise network manually is time-consuming, and resetting it to its clean…

Read at arXiv (research papers)

BBC Politics Geopolitics

Workers should get paid time off to train for crises, say peers

A House of Lords committee says more preparation is needed for war, power cuts, and cyber-attacks.

Read at BBC Politics

South China Morning Post Ann Cao Geopolitics

Alibaba says new flagship AI model cuts task costs by 60% while tightening cyber guardrails

Alibaba Group Holding has launched its most advanced artificial intelligence model to date, Qwen4-Max, with strict cybersecurity guardrails, as the tech giant balances safety with a continued commitment to open sourcing amid growing global concerns over AI-enabled cyberattacks. The release highlights a growing focus on safety in China’s AI industry as Alibaba said it intentionally filtered the model’s training data to remove offensive cyberattack capabilities while retaining…

Read at South China Morning Post

The Guardian World Australian Associated Press

Coles investigating ‘cybersecurity incident’ and apologises to customers

Supermarket giant says no customer, team or supplier data breached in cyber-attack but recommends customers update passwords Get our breaking news email, free app or daily news podcast Australia’s second-largest retailer has been targeted in a cyber-attack, though it is still too early to tell whether any of its data has been stolen or compromised. Coles revealed the threat on Monday morning, saying it was investigating the incident with support from the Australian Cyber…

Read at The Guardian World

Ukrinform

Russian hosting provider Beget reports second major cyberattack in two weeks – media

Russian hosting provider Beget, which recently lost its cloud infrastructure, has been hit by a large-scale DDoS attack reaching 2.1 terabits per second.

Read at Ukrinform

arXiv (research papers) Luciano Bozzi Security

Cyber-Secure Wearable, Ultra-Low-Power Networked Sensors for Soldier Health Monitoring: Insights from the CAPSARII project

The CAPSARII project advances a cyber-secure, ultra-low-power wearable platform and Internet of Battlefield Things (IoBT) framework to support real-time monitoring of military personnel and data-driven decision support. The architecture integrates smart-textile sensing, a body/squad area mesh, edge-deployed AI on secure RISC-V microcontrollers, and cloud/federated analytics for cross-mission learning and comparative studies. Two representative use cases--pilot fatigue and…

Read at arXiv (research papers)

South China Morning Post Danny Mok Geopolitics

5,000 people linked to HKMU may have had personal data leaked in cyber breach

About 5,000 people linked to a university in Hong Kong may have had their personal data compromised in a cybersecurity incident, with information allegedly being offered for sale on the dark web. Data advertised by dark web sellers reportedly included the names of Hong Kong Metropolitan University (HKMU) students, Hong Kong identity card numbers, telephone numbers, addresses and grade point averages (GPAs). In response to South China Morning Post queries, the university…

Read at South China Morning Post

VietnamPlus (Vietnamese state media)

ASEAN signs Digital Economy Framework Agreement

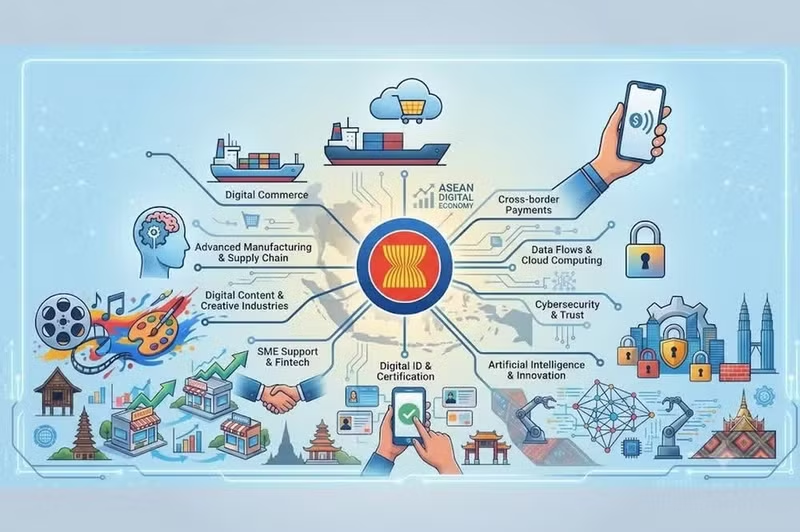
The Digital Economy Framework Agreement (DEFA), the bloc’s first standalone and legally binding digital economy agreement, establishes common rules covering digital trade, cross-border data flows, electronic payments, cyber security and artificial intelligence (AI). Vietnam proposes three strategic directions to strengthen ASEAN cooperation Vietnam backs ASEAN culture of consultation, dialogue, preventive diplomacy Vietnamese PM proposes establishing ASEAN strategic…

Read at VietnamPlus (Vietnamese state media)

South China Morning Post Chong Ming Lee Geopolitics

Can Chinese AI companies curb cyber risks from open-weight models without losing their edge?

China’s leading artificial intelligence model companies are beginning to curb the cybersecurity capabilities of their most advanced open-weight models, following a string of high-profile AI hacking incidents involving both US and Chinese companies. Earlier this month, Chinese technology giant Tencent Holdings said it had stripped its latest Hy4 model of its cyber-hacking capabilities while retaining its cyber defence capabilities, following a similar move by Moonshot AI with…

Read at South China Morning Post

Digital Trends Sudhanshu Kumar Mangalam

Tesla is finally letting customers buy the Cybercab, but there’s a long list of restrictions

Tesla has started accepting orders for its Cybercab from select customers in the US. The two-seater autonomous vehicle, which comes without a steering wheel or pedals, is listed for $29,990. However, buying one also requires a $299 monthly Autonomy Subscription, which works out to $3,588 every year. And if you want to reserve one, Tesla

Read at Digital Trends

The Verge Andrew J. Hawkins

Tesla is inviting some people to buy a Cybercab ‘for personal use’ — but read the fine print

Tesla is doubling, or perhaps tripling down on its bold claims of an autonomous future with the offer to "select customers" to purchase a Cybercab for "personal use." But the gilded, steering-wheel-free two-seater will "only be available in supported service areas" - meaning you'll only be able to buy one if you live in one

Read at The Verge

SecurityWeek Joshua Goldfarb Security

Is AI Making Us Worse at Cybersecurity?

Overreliance on AI could erode the creativity, clear communication, and critical thinking security teams need when there’s no playbook.

Read at SecurityWeek

The Hacker News Security

Attackers Exploit UnrealIRCd Flaw That Enables Server-Level Command Injection

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added a high-severity security flaw impacting UnrealIRCd, an open-source Internet Relay Chat (IRC) server, to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability, tracked as CVE-2026-114713 (CVSS score: 8.6), is a case of improper neutralization of delimiters

Read at The Hacker News

LRT (Lithuanian public broadcaster)

Hybrid warfare in Europe: sabotage, cyberattacks, agents at the service of rival powers

False bomb threats on planes and sabotage create a new pressure scenario on European societies. Russia appears in numerous investigations of these hybrid threats and disposable agents, but it is not the only one.

Read at LRT (Lithuanian public broadcaster)

SecurityWeek Eduard Kovacs Security

No Signs of Hacking in FAA Ground Stop as FBI Reportedly Probes Software Update

Officials say there is no evidence of a cyberattack behind the nationwide FAA outage, which may have been caused by a software update.

Read at SecurityWeek

BBC World Geopolitics

What we know about the longest ground stop since 9/11

US officials say the disruption was caused by old equipment overloading and not a cyber-attack or a Microsoft outage.

Read at BBC World

Ukrainska Pravda Viktoriia Shabranska

Flights resume across US: Trump doubts system failure was caused by cyberattack or AI

The FAA has lifted its nationwide ground stop after a major communications failure. Donald Trump has dismissed suggestions of a cyberattack or AI involvement, while flight delays continue across US airports.

Read at Ukrainska Pravda

NBC News Geopolitics

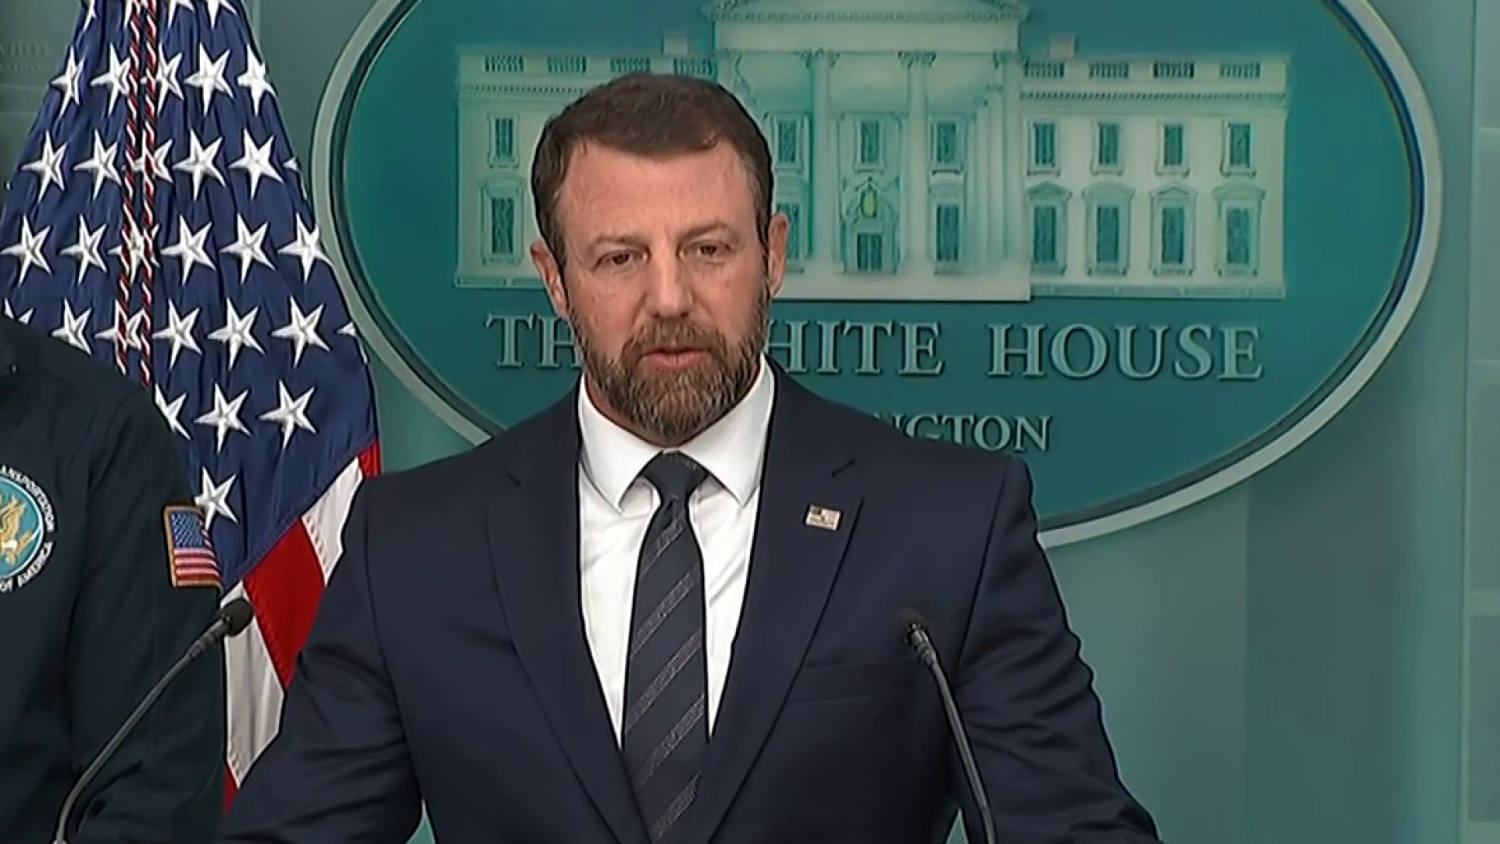
DHS says nationwide ground stop was not a cyberattack: 'We are built to handle crisis like this'

Homeland Security Secretary Markwayne Mullin told reporters during a Friday night White House briefing that there was no sign of a cyberattack in today’s ground stoppage.

Read at NBC News

NBC News

Microsoft scrambles to recover after massive outage

The company says it doesn’t have a timeline for a full recovery and blamed a “technical issue” for the outage, saying it was not the result of a cyberattack or artificial intelligence. NBC News’ Christine Romans reports.

Read at NBC News

SecurityWeek SecurityWeek News Security

FAA Ground Stop Issued Due to ‘Extraordinary Circumstances’

Federal officials have yet to say what caused the communications disruption or whether they are investigating a possible cyberattack.

Read at SecurityWeek

The Record Security

FBI flash alert says Artex tool automating cyberattacks at ‘machine speed’

Open source hacking tool Artex "significantly reduces the time required to chain attack techniques, with some intrusions progressing from initial targeting to privileged access in under three hours," the FBI said.

Read at The Record

EPIC EPIC Tech policy

Now is Not the Time to Limit Cyber Liability and State Enforcement

It is a scary time for those of us concerned about data security and threats posed by the rapid rollout of AI systems. So why are some Senators proposing a law that would limit liability for (and state enforcement authority against) major technology firms?

Read at EPIC

CyberScoop Tim Starks Security

Industry guidelines for offensive cyber tools unveiled through international Pall Mall Process

The United States this week signed on to an international set of industry standards for commercial offensive cyber tools that human rights groups and other advocates wish had been stronger. The Pall Mall Process voluntary industry guidelines for commercial cyber intrusion capabilities (CCICs), such as spyware, are the second step in a U.K.- and France-led

Read at CyberScoop

Just Security Matthew Nagle Geopolitics

Just the Docs: Nonprofits Sue Five Frontier AI Companies to Freeze Development, Citing Cyberattack and Catastrophic Risks

Four nonprofits sue Anthropic, Google, Meta, OpenAI, and SpaceXSI seeking to freeze frontier AI development over cyberattack and catastrophic risks.

Read at Just Security

Older stories