Anthropic won't fix a Claude Dispatch flaw that could let attackers execute remote commands across corporate boundaries
From EOP to RCE in six simple steps
From EOP to RCE in six simple steps
A critical finding can move through several security tools and still leave the organization exposed. The vulnerability has a severity score, and a ticket has reached the queue. Progress then depends on information the finding may lack: who owns the system, whether attackers can reach it, what protection exists, and how a change could affect the business. Each missing detail creates
No gang has claimed the attack on incredible neighborhood resource yet
Tracked as CVE-2026-107441, the out-of-bounds write flaw could allow attackers to execute OS commands via crafted HTTP requests.
October 2026 brought another wave of cyber threats targeting US businesses, with attackers exploiting trusted platforms, legitimate authentication processes, and everyday business workflows. For enterprises, these campaigns raise the stakes beyond individual security incidents, increasing the risk of financial losses, data breaches, and costly operational disruption. Below, we examine five
Editor’s Note: This is the second article in a two-part series exploring the Golden Dome for America proposal. Please also read the first, “Golden Dome Is Technologically and Financially Infeasible.”Golden Dome is an ambitious proposal for a comprehensive, layered defense, with ground, sea, and space-based elements. It is supposed to protect the United States, its allies, and deployed forces from attacks by ballistic missiles, cruise missiles, hypersonic boost-glide…
In mid-October, a Russian military satellite approached X36, which is operated by the Finnish company ICEYE and provides radar imagery to Western governments and militaries, including Ukraine.
The Indian Computer Emergency Response Team (CERT-In) has disclosed that an artificial intelligence (AI)-assisted threat actor it tracks as Crafty Falcon is targeting organizations in the Banking, Financial Services, and Insurance (BFSI) sectors in the country. Describing the threat as active and ongoing, the activity involves the use of publicly-available AI-driven offensive security tools
Indirect prompt-injection (IPI) benchmarks predominantly test planted instructions that redirect a tool-using agent toward an attacker-chosen task. Yet attacker-controlled content can instead tamper with the outcome of the task already in progress. A buyer's dispute evidence can cite a false refund policy to inflate a refund without changing the task. We define IPI by authority rather than instruction-like wording: planted content constitutes an attack when it attempts to…
PARIS, France — French regional bank Credit Mutuel Arkea said Wednesday it had been the victim of a cyberattack that enabled fraudulent transactions amounting to around 100 million euros ($112 million). The bank said the attack, which had been “contained,” allowed hackers to gain access to Arkea’s accounts and transfer funds to other banks, but
Zyxel GS1900 network switches that received the vendor's earlier fix for an actively exploited flaw are still open to the exploit attackers used, researchers at Binarly found. The exploit lets anyone who can reach a switch's web management interface run commands on it without logging in. Zyxel has released new firmware for 10 GS1900 models that closes the hole. The earlier fix is the 2.90
Large language model (LLM) agents increasingly perform complex tasks using high-privilege tools, making indirect prompt injection (IPI) a critical security risk. However, IPI benchmarks lag behind their rapidly evolving utility counterparts, only offering limited task and environment coverage and relying on narrow, static attack scenarios. In this paper, we propose meta-benchmarking for IPI: transforming existing utility benchmarks into end-to-end IPI evaluation suites that…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a medium-severity security flaw impacting multiple Apple operating systems to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability in question is CVE-2024-27834 (CVSS score: 5.5), a case of improper authentication that could allow an attacker with
Integrating the Industrial Internet of Things (IIoT) into smart grids improves their operational efficiency but expands their attack surface. Federated learning (FL) enables privacy-preserving collaborative anomaly detection, but exchanged model updates remain exposed to tampering, impersonation, and replay. This paper proposes a dual-layer architecture in which FL performs distributed anomaly detection at edge nodes without sharing raw data, while a blockchain layer secures…
Abstract The rapid growth of IoT networks has increased their exposure to Distributed Denial-of-Service (DDoS) attacks, particularly HTTP flood attacks that can disrupt service availability in resource-constrained environments. To address the challenges of high-dimensional flow-based traffic data and the need for accurate and efficient detection, this study proposes a hybrid PSO–GWO feature selection framework for HTTP flood-based IoT DDoS attack detection. Particle Swarm…
Modern Electric Vehicles (EVs) and their charging points (CPs) function as Internet of Things (IoT) nodes embedded in the distribution grid: they continuously sense local electrical conditions, exchange real-time data with the Charging Station Management System (CSMS) via the Open Charge Point Protocol (OCPP), and adjust their power consumption in response to remote commands. This dual role as both a controllable load and a networked sensor makes EV charging infrastructure a…
Abstract Objective The intertwining of the criminal legal system with immigration enforcement has shifted under President Donald Trump. The revoking of naturalized citizenship for criminal offending has increased and birthright citizenship has been attacked via executive order. A punitive “crimmigration” process where the criminal legal system is used not just to identify immigrants, but to revoke citizenship and open the door to immigration enforcement (deportation) may be…
Tool-using agents act on email, files, and payments, so an instruction hidden in a web page or a shared document can make an agent send data or money to an attacker. Many runtime defenses put a language model on the decision that lets an action through, so the decision depends on a model that may read the attacker's text and adds model calls to every step. Provenance defenses keep the model off the final check but need a model to plan or route each task first. Where an…
Tool-using agents act on email, files, and payments, so an instruction hidden in a web page or a shared document can make an agent send data or money to an attacker. Many runtime defenses put a language model on the decision that lets an action through, so the decision depends on a model that may read the attacker's text and adds model calls to every step. Provenance defenses keep the model off the final check but need a model to plan or route each task first. Where an…
Tool-using agents act on email, files, and payments, so an instruction hidden in a web page or a shared document can make an agent send data or money to an attacker. Many runtime defenses put a language model on the decision that lets an action through, so the decision depends on a model that may read the attacker's text and adds model calls to every step. Provenance defenses keep the model off the final check but need a model to plan or route each task first. Where an…
In a rare gathering, senior security officials from Pakistan, Saudi Arabia and Turkiye have met Iran's political leadership in Tehran. It is the first high-level meeting between Iran and all three members of the Mecca Defense Pact since Yemen's Iran-aligned Ansarullah movement, better known as the Houthis, escalated its attacks on the Kingdom. For the Islamic Republic, the meeting is a public relations victory, already presented as proof that the region can manage its own…
An attacker could write arbitrary files and read sensitive files via images uploaded to the Rails Active Storage ImageMagick integration, possibly positioning a threat actor for lateral movement.
The web host said hackers exploited a vulnerability to access customer emails and files during a "deliberate attack."
A flaw in APT, the package manager for Debian and Ubuntu, allows an attacker who can modify package downloads to swap a checked package for their own. The attacker's code then runs as root, according to advisories that Debian, Ubuntu, and APT's developers published on November 4. The attack needs APT to retry failed downloads, which it does by default from Debian 12 and
SonicWall has warned of two vulnerabilities impacting end-of-life Global Management System (GMS) systems that it said will not be patched. Details of the security flaws, which affect SonicWall GMS 9.5.2 and earlier versions, are below - CVE-2026-109593 (CVSS score: 9.1) - An unauthenticated file read vulnerability that could allow an attacker with network access to read internal GMS files,
This Insight was published as part of GIFCT’s Working Group on Gaming and Youth (GYWG). GIFCT Working Groups bring together experts from diverse stakeholder groups, geographies and disciplines to offer advice in specific thematic areas and deliver on targeted, substantive projects. Since the right-wing extremist attack in Christchurch (New Zealand) in 2019, an upsurge in research has laid the basis for
Four others were wounded in attacks across the region on Wednesday, local authorities said.
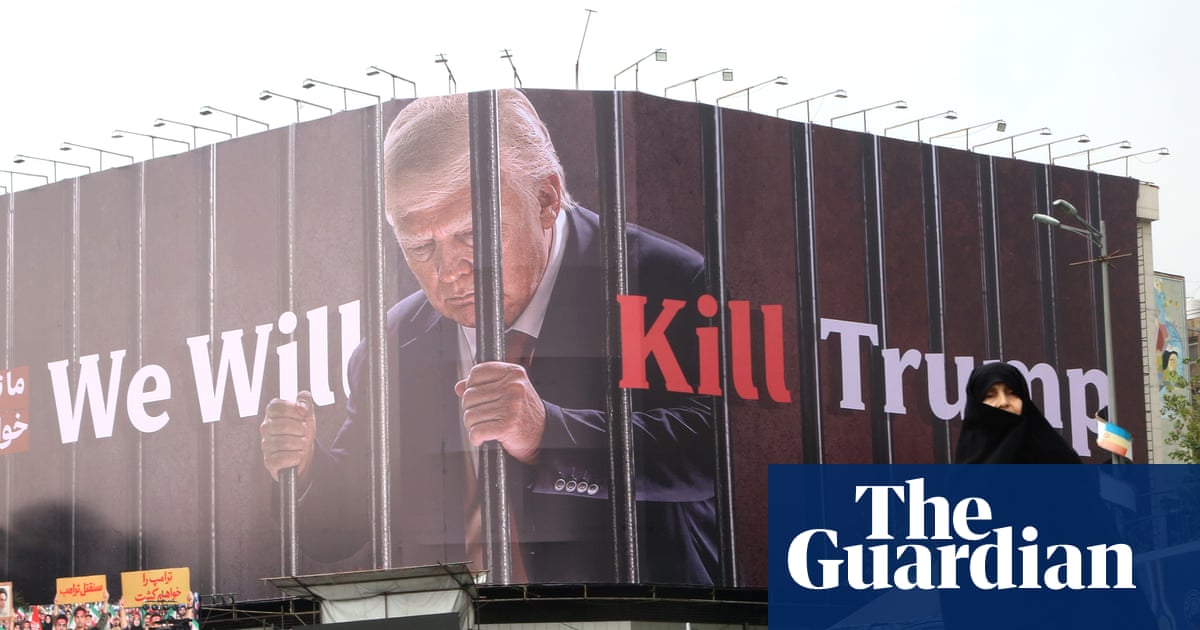
Iran celebrates its claimed role in ‘regime change’ amid pressure on Trump to ‘finish the job’ with attack US midterms live – latest updates Iran this week unveiled a huge billboard and banners over Enqelab Square in central Tehran. The billboard pledged in English: “We will kill Trump” – elevating the degree of personal animus with which Donald Trump is viewed in official Iranian circles. The poster depicts the US president behind bars with his head bowed. And in a sense…
A supplier of the French National Blood Service was hit by a cyber-attack in which hackers turned cold rooms hosting blood samples up to 110°C (230°F)
Hackers have been harvesting AI access tokens and have been using AI-assisted offensive tools to automate attacks.