Microsoft says failed server health checks disrupted Outlook and other Microsoft 365 services. The company is still investigating the cause and has disclosed no evidence of a cyberattack.
The cybercriminals are retargeting law firms that refused to pay its first ransom, with a social engineering con aimed at stealing Microsoft access tokens.
“Sharing account credentials with personal, third-party, AI assistants can expose sensitive information, and actions taken by these tools may result in unintended purchases" and more, United Airlines said.
The incident is the latest in a string of attacks on ports and other shipping organizations worldwide, with Brazil’s largest port hit with ransomware last week.
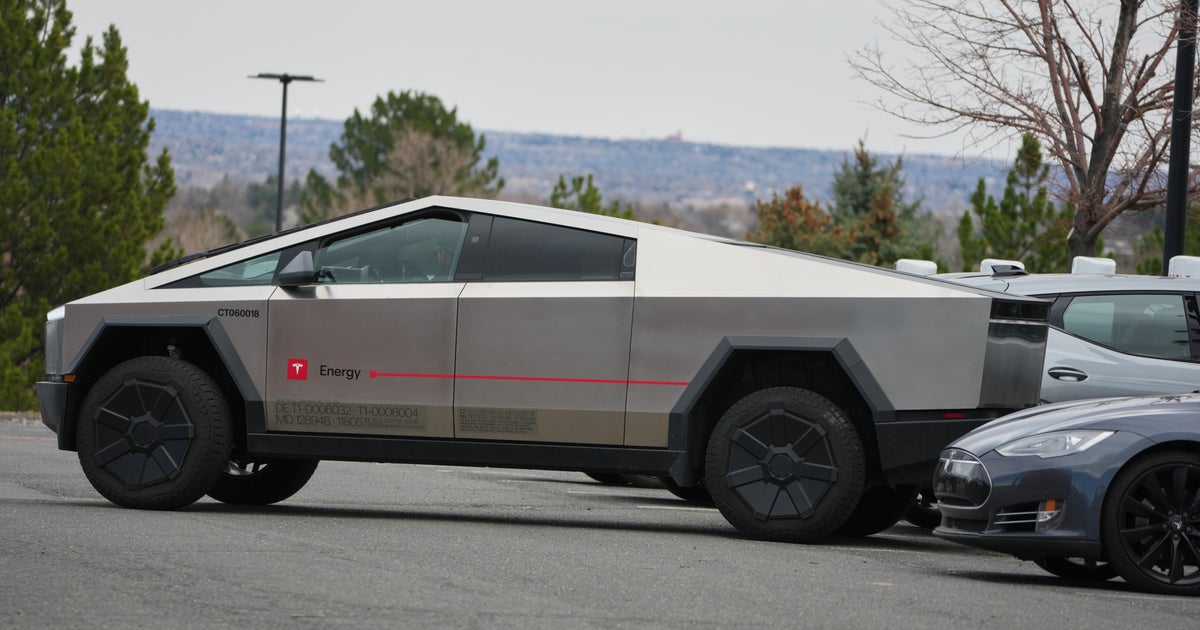
The Cybertruck is heading to that shiny cyber-dumpster in the sky, leaving the folks who built online identities around Elon Musk's polarizing pickup feeling bereft. Usually, Musk's fanbase treads lightly around their idol's mercurial decisions. This time, however, the truck's demise has sparked rare backlash within the Tesla community - aimed squarely at the guy
CyberScoop is exclusively reporting on the letter to the Hill on the controversial snooping authorities under the Foreign Intelligence Surveillance Act.
The increasing penetration of inverter-based resources and growing cyber-physical interdependencies expose electrical power systems to disturbances that challenge conventional resilience assessments. Existing approaches often evaluate resilience dimensions independently, overlooking the non-additive effects of coordinated disruptions and the influence of exogenous stressors. To address this gap, this paper proposes a Grid Multidimensional Resilience Index (GRID-MRI) that…
Abuse of an independent third-party tool led to breaches at ScreenConnect customers, confirmed the software's maker, ConnectWise. Cybersecurity researchers had spotted intrusions at nearly 50.
Crypto agility maturity models aim to support organizations in preparing for cryptographic transitions, such as migrating to post-quantum cryptography. Recognizing the importance of measurable maturity, NIST references several such models in its guidance. Given NIST's influence on cybersecurity practice, these models may shape organizational planning and governance mechanisms. However, their design quality has not been systematically evaluated. In this work, we assess three…
Cybersecurity researchers have found that lookalike domains masquerading as artificial intelligence (AI) tools are being used to serve ClickFix-style lures, browser-hijacking malware, and a set of extensions that hijack user searches. This delivery pattern has been codenamed TypoPrompting by Island. "AI-app lookalikes that turn an attempt to reach a familiar tool into a prompt to verify,
Shipping giant Maersk has confirmed that one of its systems was broken into by hackers who have stolen data. The WhiteArmor gang has claimed responsbility for the attack.
The ongoing campaign targeting ConnectWise ScreenConnect deployments involves the exploitation of a now-patched critical security flaw in the remote access software, and not a new vulnerability, it has emerged. Blackpoint Cyber's Adversary Pursuit Group (APG), which shared the details with The Hacker News, said the recovered attacker toolkit exploits CVE-2026-84869 (CVSS score: 9.9), an
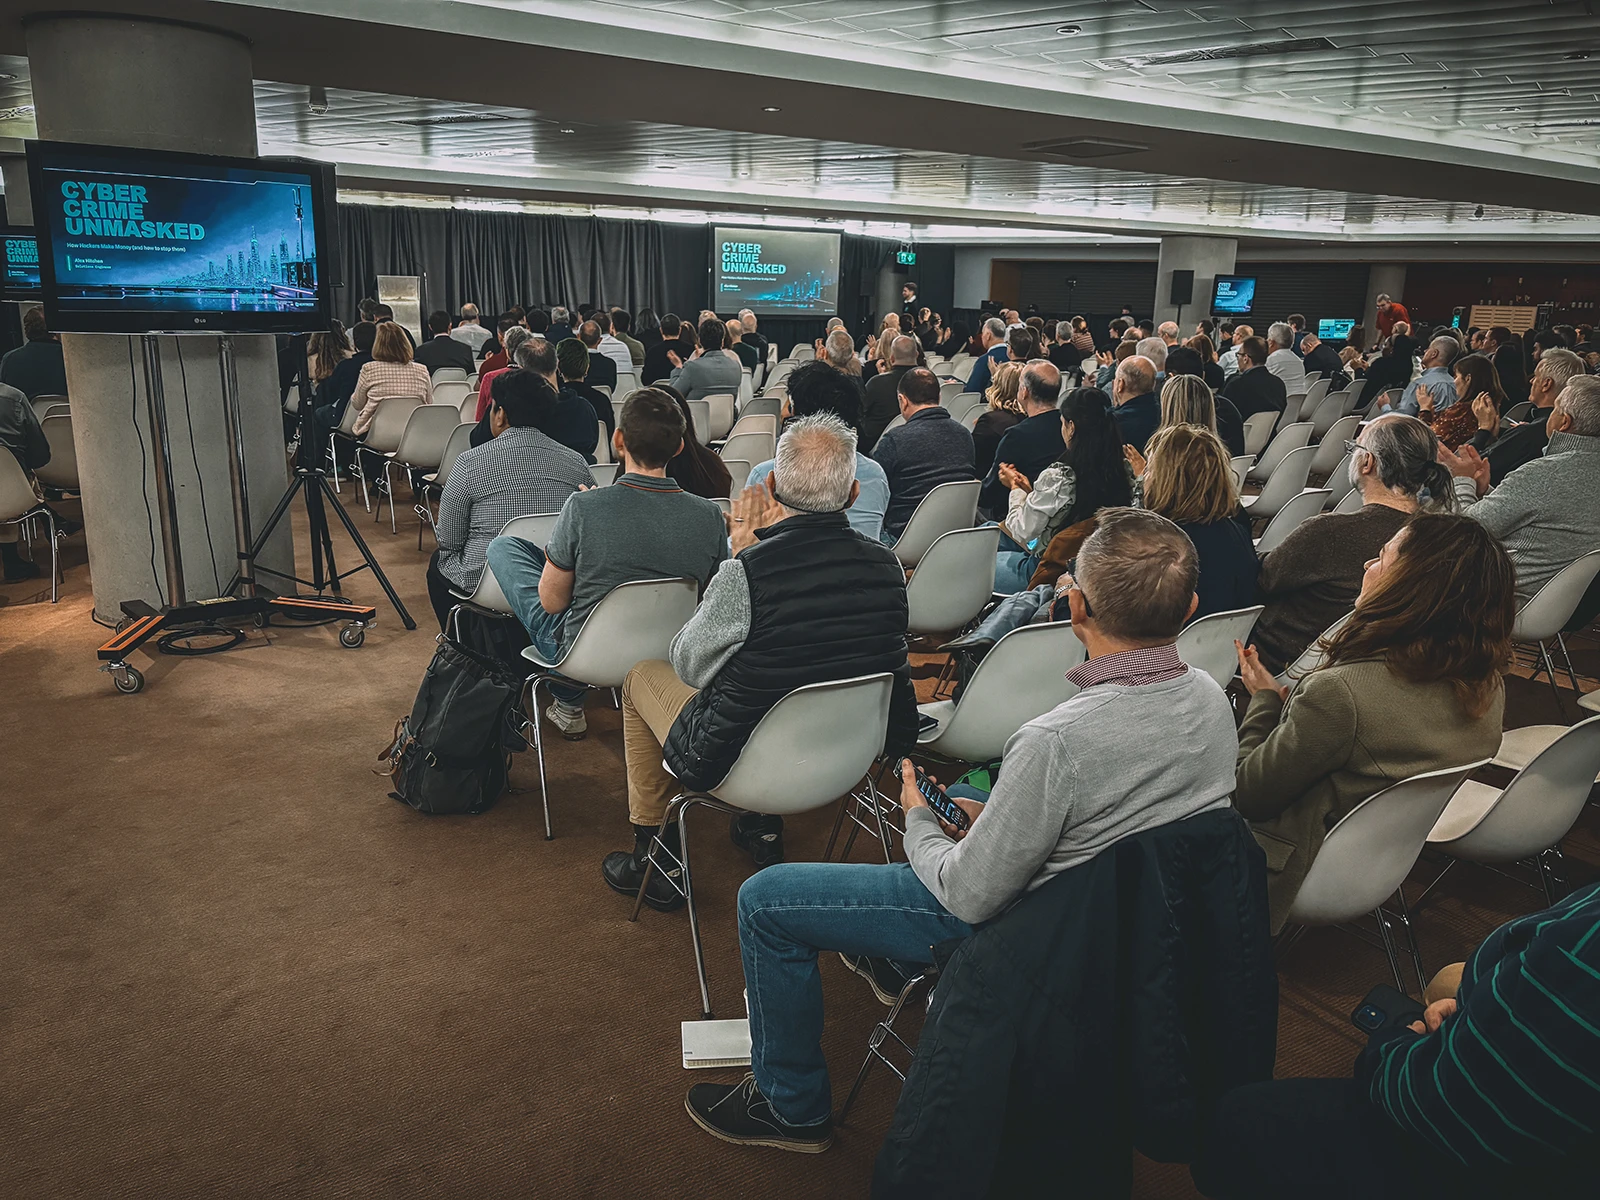
IRISSCON 2026, the annual cybercrime conference organized by IRISSCERT, took place at the Aviva Stadium in Dublin on November 11. The all-day event gives attendees a look at the cyber threats businesses are facing right now, along with practical advice on how organizations can respond to them. Help Net Security was there, and here’s a look at the day. Visitors at IRISSCON 2026 Selena Larson, staff threat researcher at Proofpoint, shared insight about GenAI use … More →
While 60% of Indian organisations report positive returns on AI investments, declining security readiness and infrastructure gaps are creating challenges to sca
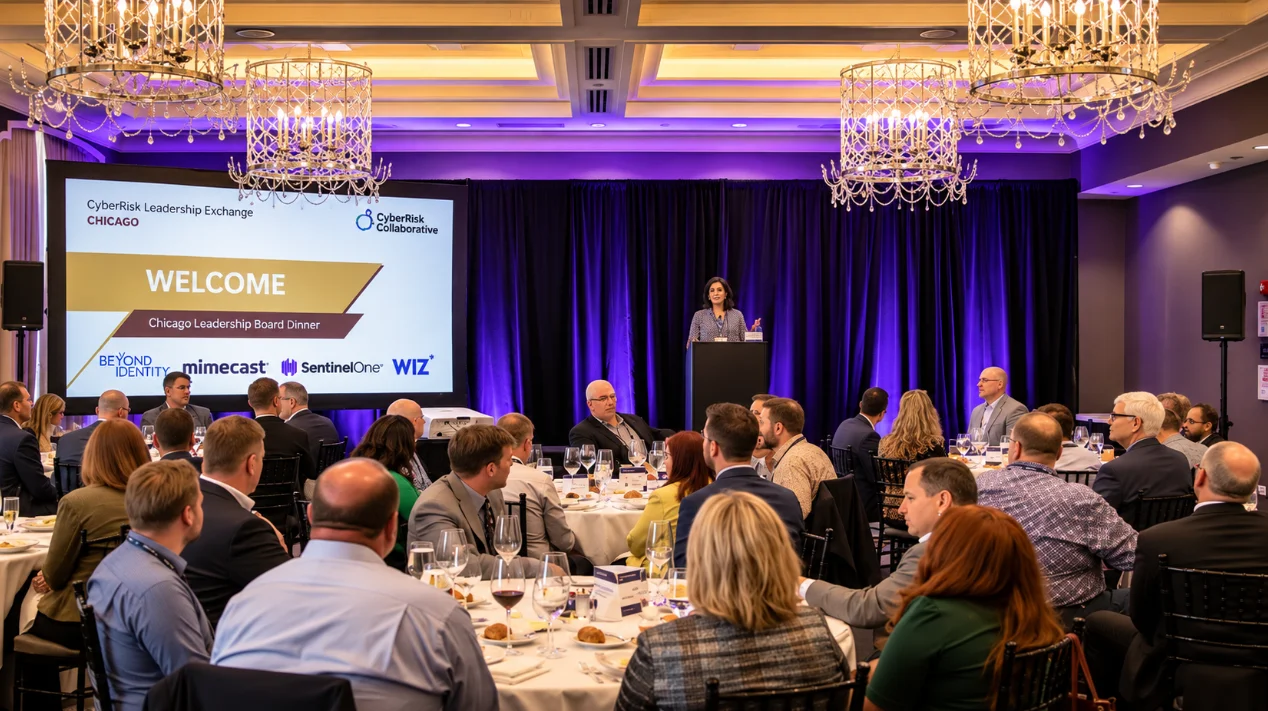
Insider Brief PRESS RELEASE — CyberRisk Collaborative, a membership organization for senior cybersecurity leaders, today announced Post-Quantum Readiness: Preparing for Q-Day, a virtual event taking place Tuesday, Jan. 26, 2027, focused on the security, risk, and technology implications of advances in quantum computing. The program will bring together cybersecurity and technology leaders to examine how
Canadian businesses could provide food processing and preservation solutions, consultancy and design services for energy transition projects, software, artificial intelligence and cybersecurity solutions, as well as diagnostic and digital healthcare technologies.
In today's edition: Egypt’s remittances reach record $38.2 billion || Ghana targets 70% 5G coverage by March 2027 || Kenya launches new cybersecurity centre || Telkom challenges telecoms ownership rules
Ask industrial security chiefs whether their plants would keep running through a full IT compromise, and every one who answered the SANS 2026 ICS/OT survey says yes. Thirty-eight percent expect to run indefinitely on islanded ICS/OT systems, and 62% expect to get by temporarily on manual controls. None foresee degradation or a halt. The 696 practitioners SANS surveyed, the people who would run those manual controls, are less sure. Only 15% said their critical processes ……
A long-awaited slate of sex crime reforms including the criminalisation of persistent child sexual abuse and “cyberflashing” has been set to be gazetted this Friday, with the bill due for scrutiny at the legislature later this month. The Sexual Offences Legislation (Amendment) Bill 2026 “aims to achieve two policy objectives, namely, strengthening protection for victims
The package adds public-private cyber responders, an AI-focused team run by the economic ministry, and more leeway to use the government's new active cyber-defense powers.
An organization's ability to quickly recover from a business disruption will be a competitive advantage in an era of AI-driven threats and business enablement.
"We don't assume every attempt can be prevented, so our focus is on building the readiness to identify threats early and act decisively," says Brian Cincera.