Help Net Security

Recent stories from Help Net Security.

Help Net Security Mirko Zorz Security

Your AI red team may be finding the same prompt injection thousands of times

AI agents retrained on a bigger pile of prompt injection attacks came out easier to hijack in three of four tests run by researchers at the University of Waterloo, Zhejiang University and KTH Royal Institute of Technology. The automated red-teaming tool that found more working attacks produced the weaker defense. Prompt injection purple-teaming workflow (Source: Research paper) Someone hides instructions in an email, a web page or a tool’s output, and the AI agent that ……

Read at Help Net Security

Help Net Security Help Net Security Security

It’s time to retire vanity security dashboards

In this Help Net Security video, Abdul Khadir Mahamed, OT Security Architect at Estée Lauder Companies, explains why security teams should retire vanity dashboards in IT and OT environments. He walks through an example from a manufacturing site, where the same approved maintenance work triggers the same alert week after week. Analysts close thousands of tickets, but the underlying problem stays. He describes how SOC and control engineering teams can review these patterns…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

AI agent API security hasn’t caught up with agents already running in production

Postman asked nearly 9,000 developers, architects and executives how they’re handling AI agents, and the answers tell a familiar story. Companies put the new thing to work first and left the question of who holds the keys for later. A quarter of the organizations that answered already have agents calling their APIs in production. Source: Postman The keys are where it gets uncomfortable. About four in ten respondents haven’t worked out how credentials and identity … More →

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Most CIOs and CISOs expect to contain attacks, though few can reach their gear right away

Most organizations can’t quickly get secure management access to their own critical network infrastructure once the primary network goes down. Opengear surveyed 514 CIOs and CISOs and only a small share said they could get that access immediately or close to it. That gap bites hardest during a ransomware attack or a bad update, the moments when someone has to log in, cut off what’s compromised and bring services back. If the only path to … More →

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Android developer verification will reach every install source, with a side door for power users

Google will extend Android developer verification to every country starting in January 2027, a check that already applies at participating app stores in four countries. Developers who have not verified their identity with Google and registered their apps will see those apps lose the normal install experience on certified Android devices. The rollout opens with seven app distributors: Google Play, Galaxy Store, Honor, Oppo, Xiaomi, Transsion and Vivo. Over several months it…

Read at Help Net Security

Help Net Security Zeljka Zorz Security

NGINX2Root: F5 patches five critical NGINX vulnerabilities

F5 has patched five critical vulnerabilities in NGINX, the world’s most widely used open-source web server, that can allow remote code execution under certain conditions. Dubbed “NGINX2Root” by Xint researchers, two of the bunch (CVE-2026-123633 and CVE-2026-123007) were also independently unearthed and reported by Rapid7, Wiz, Ikotas Labs, Palo Alto Networks and Metnir researchers. There’s no evidence that any of them has been exploited in the wild, and none were on CISA’s…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

PHP 8.6 is out, and here’s what changes for your code

PHP 8.6 has been released. The new version adds partial function application, a Time\Duration class, a polling API for event loops and a clamp() function. PHP 8.6 also changes defaults that existing apps could trip over. Sessions now start with session.use_strict_mode and session.cookie_httponly turned on and session.cookie_samesite set to Lax. Custom session handlers that don’t implement both create_sid() and validateId() are deprecated. If your app relied on the old…

Read at Help Net Security

Help Net Security Sinisa Markovic Security

Russian spies turn one cloud breach into a stepping stone for the next

A Russian cyberespionage group is posing as employees of organizations it has already breached to phish new targets, Google Threat Intelligence Group (GTIG) found. Google tracks the group as COLD RELIC (also known as Star Blizzard, Callisto and Gossamer Bear), and the US Department of Justice has assessed that it operates within Russia’s Federal Security Service (FSB). COLD RELIC goes after government officials, defense contractors and NGOs in Europe and North America. “The…

Read at Help Net Security

Help Net Security Zeljka Zorz Security

Exploited Puppet flaw puts the server that configures your endpoint fleet at risk (CVE-2026-115731)

Attackers are exploiting CVE-2026-115731, a critical remote code execution vulnerability in Perforce Puppet Enterprise, an enterprise solution used by IT teams to centralize and automatize endpoint management. Details about the in-the-wild attacks have yet to be made public, but the US Cybersecurity and Infrastructure Security Agency (CISA) added the flaw to its Known Exploited Vulnerabilities catalog on Tuesday and ordered US federal civilian agencies to address it by…

Read at Help Net Security

Help Net Security Sinisa Markovic Security

Credential stealer slipped into Microsoft’s official Python agent framework

Two releases of Microsoft’s official agent-framework package on the Python Package Index (PyPI) carried code that steals cloud and CI/CD credentials from developers’ systems. Agent Framework is Microsoft’s open-source toolkit for building AI agents and running them in workflows. Three supply chain security companies, StepSecurity, OX Security and Socket, caught the malicious versions and shared their analysis. “On November 17, 2026, versions 1.26.1 and 1.26.2 of the official…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

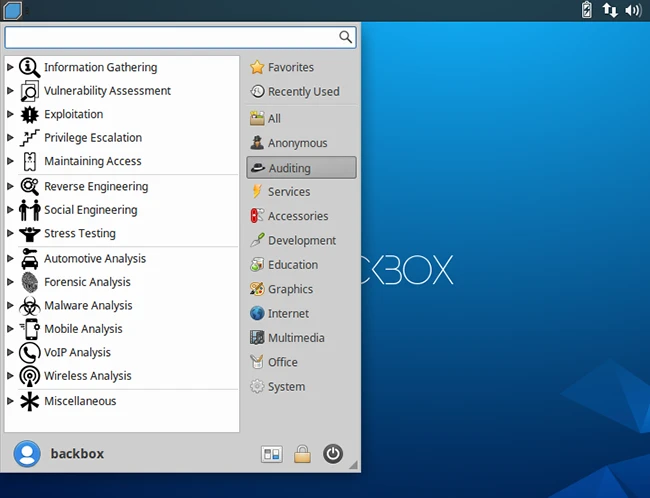
BackBox Linux 10 brings new hacking tools and Ubuntu 26.04 support

BackBox Linux is a free, open source penetration testing distribution made by BackBox, a non-profit community project that keeps its own repositories of ethical hacking tools. On November 19 the project released version 10, codenamed Resolute Raccoon. It’s built for compatibility with Ubuntu 26.04 LTS and ships with the Linux 7.0 kernel and the Xfce 4.20 desktop. It also changes how anonymous mode handles traffic: DNS queries now go through Tor, and IPv6 is blocked … More →

Read at Help Net Security

Help Net Security Industry News Security

Rubrik Configuration Resilience rolls back unauthorized Microsoft 365 changes

Rubrik announced Configuration Resilience for Microsoft 365, a new offering that protects the key settings governing Microsoft applications such as Microsoft 365, Purview and Defender, and rolls back changes to them with a single action. By continuously safeguarding Microsoft 365 configurations, Rubrik equips organizations with a one-click undo button to reverse unauthorized system modifications before attackers can steal sensitive data. Rubrik Security Cloud handles…

Read at Help Net Security

Help Net Security Zeljka Zorz Security

SonicWall urges customers to replace Gen 6 firewalls now

SonicWall is urging customers still running Gen 6 firewalls to replace them immediately and to stop using them at the internet edge. All Gen 6 and Gen 6.5 appliances running SonicOS 6.x have now reached end of support. That means no more firmware updates or security patches, “regardless of severity,” the company said in a product advisory published on Wednesday. Why now? SonicWall calls the Gen 6 fleet a high-risk exposure and expects internet-facing units … More →

Read at Help Net Security

Help Net Security Industry News Security

Bitwarden expands passkey support with new Windows and macOS integrations

Bitwarden announced expanded passkey integrations across Windows and macOS, making it easier to access Bitwarden and use passkeys through native operating system authentication. Users can log in to Bitwarden and unlock their vaults using passkeys verified through Windows Hello or Apple Touch ID. Native operating system integration also enables Windows 11 and macOS to recognize Bitwarden as a passkey provider, allowing users to create and use passkeys that remain securely…

Read at Help Net Security

Help Net Security Industry News Security

Palo Alto Networks to acquire Applied Compute for $4.5 billion

Palo Alto Networks will acquire Applied Compute, a platform for post-training and inference of open-weight AI models. The all-stock transaction is valued at $4.5 billion, subject to adjustments. The acquisition will bring Applied Compute’s platform and world-class AI research team to Palo Alto Networks to help enterprises adopt AI securely, whether they choose open-weight models, closed frontier models, or both. Palo Alto Networks believes the future of enterprise AI is…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

GTA 6 scams are after your Google password, money, and crypto wallet

Scammers are using the GTA 6 launch to steal Google passwords, sell game keys that may never arrive, and get players to connect crypto wallets. Stefan Dasic, a senior malware research engineer at Malwarebytes, tracked the lures. They range from fake giveaways to a phone app that mostly serves ads. The free copy that wants your password One site promises GTA VI to every visitor who meets its “promotion terms.” It then asks them to … More →

Read at Help Net Security

Help Net Security Sinisa Markovic Security

Ukraine arrests key members of ransomware gang that extorted $40.5 million posing as IT support

Four key members of a ransomware group that took more than $40.5 million from at least 28 companies have been detained in Ukraine. The group’s members posed as IT support staff on phone calls to break into corporate networks, according to Ukraine’s National Police. The arrests followed an investigation that Ukrainian police ran with the FBI for more than two years. A phone call to get in Before making contact, the group studied each target’s … More →

Read at Help Net Security

Help Net Security Sinisa Markovic Security

US enlists private firms to cut scammers off from victims’ cash

Stopping victims’ money before it reaches foreign scam, cybercrime and sextortion networks is the goal of a new US unit launched by the Homeland Security Task Force (HSTF). The Threat Disruption Center is part of the HSTF’s National Coordination Center (NCC) in Fairfax, Virginia. The task force calls it “a shared technology resource and collaboration hub.” Investigators will get tools to sort incoming victim complaints and map the criminal groups behind them, along with…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Game consoles and Teslas are slipping past OT network segmentation

Claroty went looking for consumer gadgets on hospital, factory and commercial networks and found tens of thousands of them, from game consoles and Roku streaming sticks to Teslas. Roku sticks and smart watches mostly sat on guest networks, the separate segment meant for visitors’ devices. Sonos speakers and cars mostly stayed off guest networks, and game consoles mostly sat on production networks, next to the equipment that keeps patients cared for and production lines…

Read at Help Net Security

Help Net Security Sinisa Markovic Security

AI agents inherit employee access, and nobody’s watching how they use it

AI agents that employees build inside project trackers, CRMs and automation tools often run on the credentials of the person who created them and carry that person’s access to company data, according to Nudge Security. Source: Nudge Security The AI Adoption in Practice 2026 report draws on anonymized, aggregated telemetry from Nudge Security customer environments. It tracks which AI tools show up in organizations, what those tools connect to, which agents are running and how…

Read at Help Net Security

Help Net Security Mirko Zorz Security

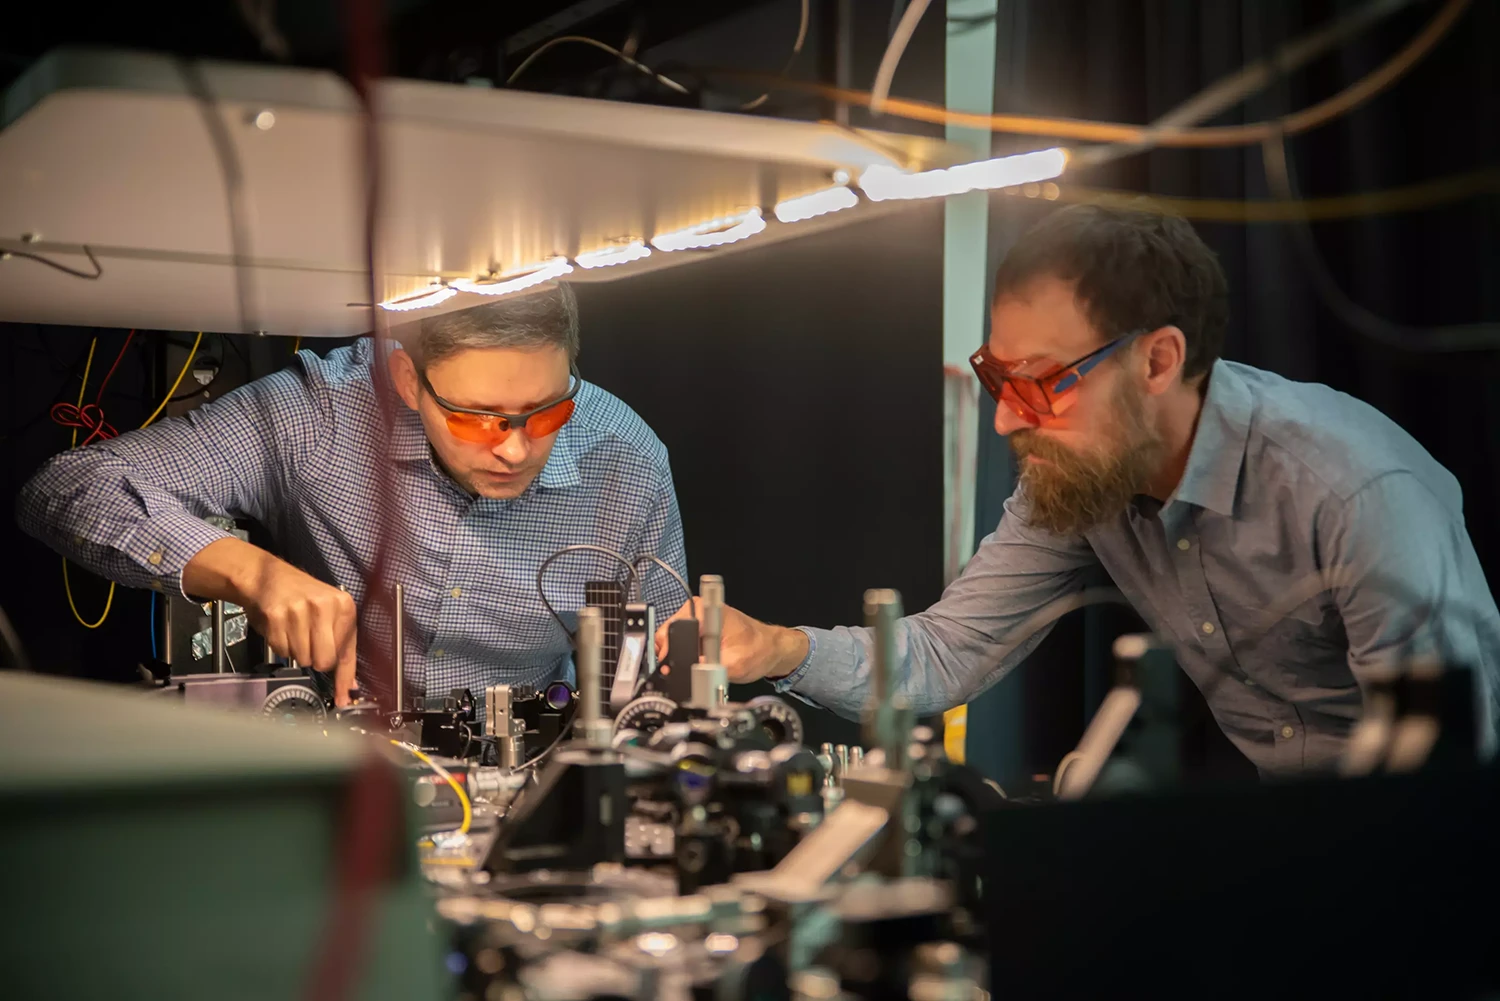
Quantum position verification could lock remote hackers out, NIST shows

Physicists at the National Institute of Standards and Technology have used entangled photons to confirm that a party was physically where it claimed to be. NIST physicist Krister Shalm and an international team ran a quantum position verification protocol inside a research building in Boulder, Colorado, and closed loopholes that had left earlier quantum location schemes open to cheating. NIST researchers Krister Shalm (left) and Marty Stevens use optical components to guide…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Ransomware access brokers are moving their deals off public forums

Ransomware and extortion gangs claimed about 718 victims a month through October 2026, according to threat intelligence firm ZeroFox, up from roughly 573 a month in 2025. Between early 2025 and early 2026, public dark web listings selling access to hacked corporate networks fell from about 620 a quarter to about 370. Those listings worked as an early warning. A broker advertising a foothold in a company’s network could signal that a ransomware crew was … More →

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Azure Linux 4 puts the OS behind Microsoft’s cloud services on your VMs at no extra license fee

Microsoft made Azure Linux 4 generally available. The company is offering its in-house Linux distribution as a general-purpose server OS for customer virtual machines and scale sets. Customers pay for the Azure compute underneath and no additional OS licensing fee. The same distribution already runs on millions of cores across Azure services, including Azure Kubernetes Service, App Service and Azure Cosmos DB. A team that runs one distro on VMs, another on Kubernetes nodes…

Read at Help Net Security

Help Net Security Zeljka Zorz Security

Java4Shell OpenJDK flaw: Exploitation is tricky and hinges on specific CPUs (CVE-2026-114938)

CVE-2026-114938, a memory corruption flaw in Open Java Development Kit’s Base64 decoder, can allow unauthenticated attackers to run code on servers hosting widely used Java applications. Nicknamed “Java4Shell” by Calif, the company whose researchers found it, CVE-2026-114938 was fixed by Oracle and the OpenJDK project on Tuesday. There is currently no evidence of successful attacks leveraging the flaw, but the US Cybersecurity and Infrastructure Security Agency (CISA)…

Read at Help Net Security

Help Net Security Mirko Zorz Security

Ubuntu AI security patches are here, if you’re willing to test them yourself

Canonical is letting Ubuntu Pro customers install security patches written by AI agents before its engineers finish reviewing and testing them. The patches come from Surge, a system Canonical built to fix known vulnerabilities in Ubuntu’s userspace software, meaning everything outside the operating system’s kernel. They ship through a new opt-in channel called the Edge archive. If you leave Edge switched off, nothing changes in how your updates are checked: Ubuntu’s regular…

Read at Help Net Security

Help Net Security Mirko Zorz Security

Deutsche Telekom IoT’s CEO on securing devices that run for 20 years

In this Help Net Security interview, Christian Schwalbe, CEO of Deutsche Telekom IoT, talks about the forgotten devices that create the most risk in IoT deployments. He explains what the EU Cyber Resilience Act means for manufacturers whose products stay in the field for 15 or 20 years, and how threats can be spotted through communication patterns without inspecting payloads. Schwalbe also discusses post-quantum cryptography for constrained devices, including research on…

Read at Help Net Security

Help Net Security Sinisa Markovic Security

Once a scam ends the victim blaming begins

Blaming people who fall for scams deepens the harm and teaches them to stay silent the next time, cyberpsychologist Dr. Nicola Fox Hamilton told the audience at IRISSCON 2026 in Dublin. Dr. Nicola Fox Hamilton, cyberpsychology researcher and lecturer in IADT, talked about the psychology behind phishing and scams Fox Hamilton, a cyberpsychology researcher and lecturer at IADT, talked about the lasting impact scams have on victims and made a point to note that nobody … More →

Read at Help Net Security

Help Net Security Mirko Zorz Security

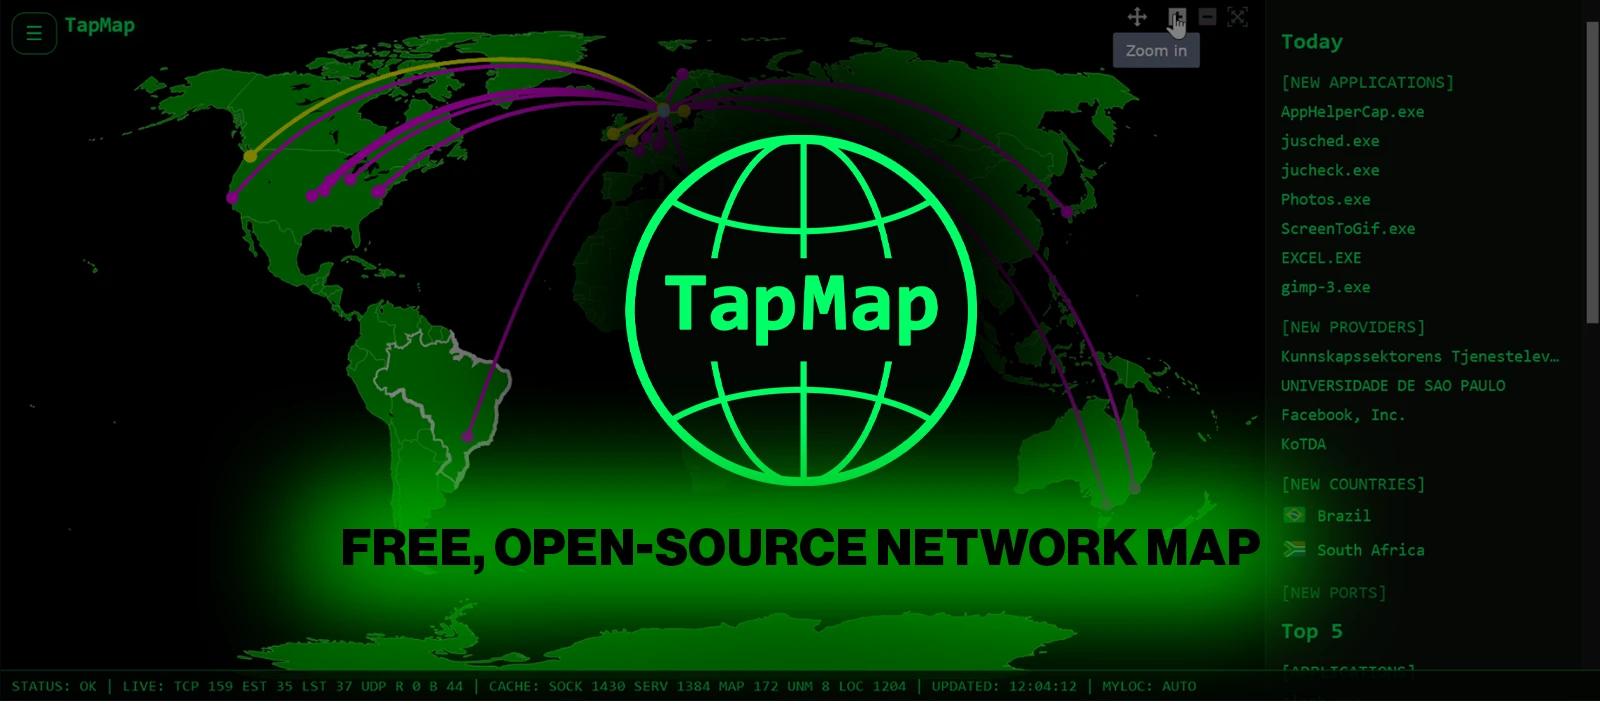
TapMap: Free, open-source network map

TapMap is a free, open-source desktop app that plots a computer’s active network connections on an interactive world map. It scans open sockets, pulls out the remote IP addresses and looks each one up in a local GeoIP database. Then it draws the result in the browser, with the application behind each connection a click away. “Locations are based on IP geolocation data and are approximate. TapMap does not independently determine or verify the physical … More →

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

BubbleLoader malware turns copies of WinRAR and Windows Media Player into carriers

ReversingLabs has taken apart BubbleLoader, a loader that turns ordinary Windows programs into carriers for other malware. The attackers rewrite a handful of instructions at a program’s entry point, the spot where Windows begins running it, and add two PNG images that hold the hidden code. Known hosts include WinRAR, the x64dbg debugger, Windows Media Player, the Firefox launcher and virtiofs. The earliest BubbleLoader samples appeared in February 2026, and ReversingLabs…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Product showcase: iVerify Basic helps users check device security and improve privacy

iVerify Basic is a mobile security app for individuals who want to check their devices for signs of compromise and improve their security settings. It is available for iOS and Android, including tablets. Device security checks The Device tab puts scan controls and security status on one screen. Users can select Run Scan to check device integrity. After a check, the app displays its findings and records when the device was last checked. Device Health … More →

Read at Help Net Security

Older stories