Results for “Mali”

arXiv (research papers) Yuxuan Zhou Security

SEAM: Computer-Use Agents Know the Harm Between Screens, and Commit It Anyway

Safety benchmarks for computer-use agents (CUAs) place the harm either in the intent of the task or on a single screen: a malicious instruction, an injected command, a phishing page. An agent that checks the task and each screen in isolation can pass them, so they do not test whether it combines facts seen on different screens. Yet in delegated work, harm often arises exactly this way: a fact about a person on one screen, a fact about an item on another, and a legitimate…

Read at arXiv (research papers)

arXiv (research papers) Xinxuan Zhang Security

Can Verifiable PIR Match the Online Efficiency of SimplePIR?

Verifiable Private Information Retrieval (vPIR) ensures that a malicious server cannot return tampered database records, but it traditionally incurs significant overhead compared to classical PIR.Recent advancements, notably VeriSimplePIR, approach the online efficiency of SimplePIR by introducing a proof preprocessing phase and requiring only lightweight client-side online verification. However, this scheme relies on an additional Short Integer Solution (SIS) assumption and…

Read at arXiv (research papers)

Infosecurity Magazine Security

Optimizely Flaw Exploited to Serve Malicious Code to Visitors of 178 Organizations

An attacker abused an Optimizely flaw to plant malicious code on websites of 178 organizations

Read at Infosecurity Magazine

arXiv (research papers) Fuyi Wang Security

Flexibility Has a Price: Quantifying Modality Policies in Maliciously Secure Multi-Biometric Authentication

Multi-biometric authentication improves robustness and accessibility by combining information from multiple biometric modalities. Existing research has primarily focused on secure multimodal authentication, feature fusion, and recognition performance, while paying comparatively little attention to the security implications of modality-flexible authentication policies. At the same time, most systems provide limited cryptographic protection for biometric data during…

Read at arXiv (research papers)

IRNA (Iranian state media) Geopolitics

Iran warns against “malicious campaign” to justify infrastructure attacks

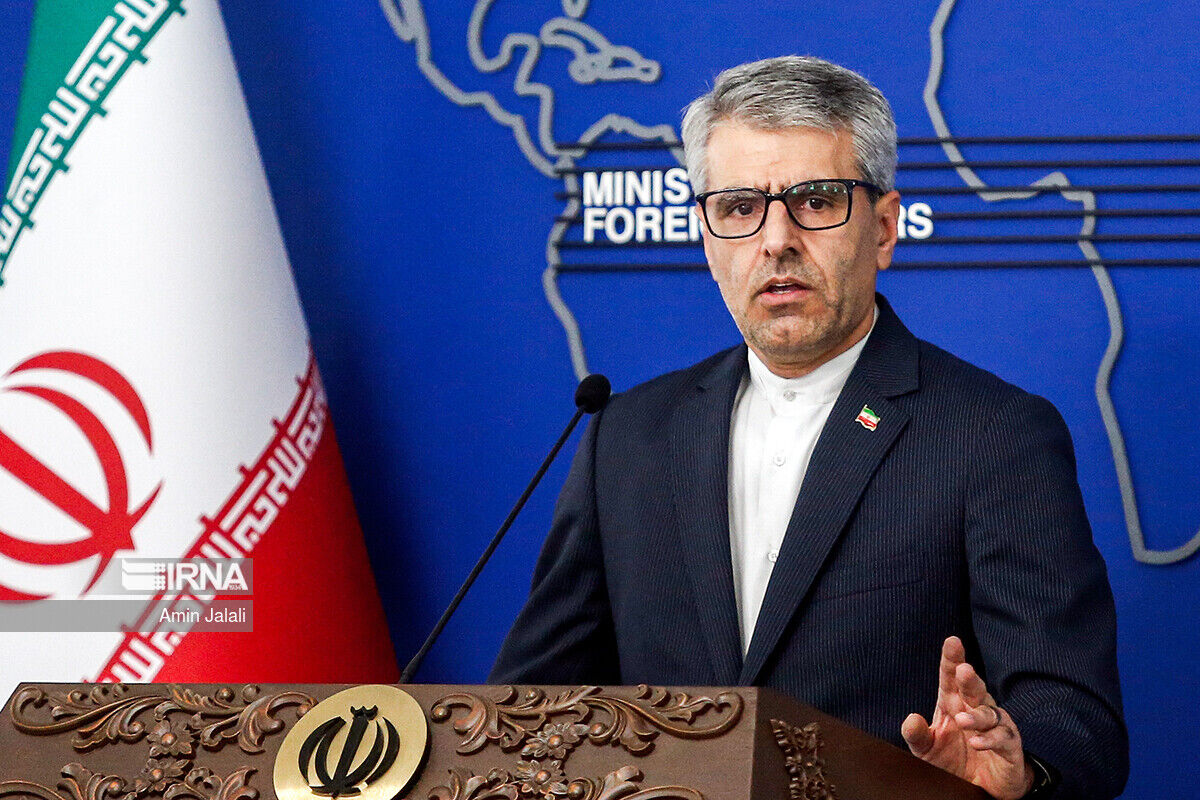
Tehran, IRNA – Iran’s Foreign Ministry spokesperson Esmaeil Baqaei has warned against a malicious campaign to manufacture security pretexts, condemning the baseless allegations linking Iranian dams to missile bases as a means to justify attacks on the country’s vital infrastructure.

Read at IRNA (Iranian state media)

DW Geopolitics

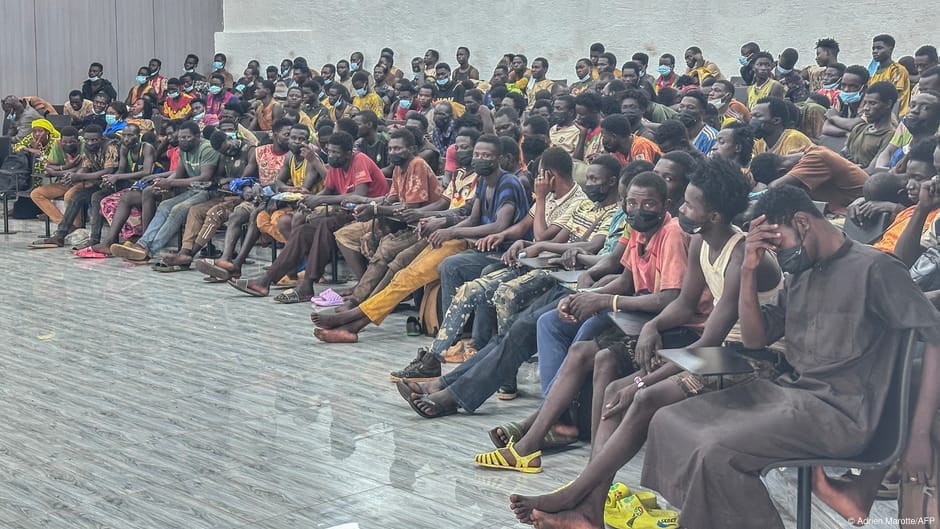
Guinea jails 200 in wildcat gold mining crackdown

A Conakry court has jailed 22 former local officials from the gold-rich northeastern Siguiri region, as well as 200 people accused of illegal mining. It's part of a wider crackdown that sent thousands fleeing into Mali.

Read at DW

The Hacker News Security

Hackers Found a Way Around GitHub SHA Pinning. This Webinar Explains How to Close the Gap

Pinning GitHub Actions to an exact version of their code, known as SHA pinning, has become the go-to defense against software supply chain attacks. Attackers have already found a way around it. In March 2026, the hackers who hijacked Trivy, a widely used open-source security scanner, planted malicious code that looked like it came from GitHub's official checkout tool. They even labeled it a

Read at The Hacker News

CISA advisories CISA Security

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-115731 Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability…

Read at CISA advisories

Help Net Security Sinisa Markovic Security

Malware spread through Optimizely hits 178 organizations, including BBC, CNN and Zoom

An attacker exploited a vulnerability in Optimizely’s web experimentation platform to plant malicious JavaScript on its customers’ websites, the company has confirmed. Companies add Optimizely Web to their sites through a JavaScript snippet loaded from Optimizely’s servers. “Earlier today, Optimizely identified a security incident in which an unauthorized party exploited a vulnerability in Experimentation and used it to add malicious JavaScript to some customer projects…

Read at Help Net Security

arXiv (research papers) Yujun Wang Security

Evolution Under Fire: Evolving Agent Safety Harnesses with Adaptive Injection Stressors

Tool-using language-model agents must act on information from untrusted emails, webpages, and documents. This creates a central security challenge: malicious instructions and legitimate task directives can arrive through the same interaction channel. Existing defenses are largely hand-designed and static, making further improvements dependent on repeated manual redesign. We introduce Evolution Under Fire, a staged framework that couples safety-harness evolution with adaptive…

Read at arXiv (research papers)

ReliefWeb UN Office for the Coordination of Humanitarian Affairs

DR Congo: Afrique de l’Ouest et centrale : Derniers événements en bref (10–16 novembre 2026)

Countries: Democratic Republic of the Congo, Central African Republic, Kenya, Mali, Sudan Source: UN Office for the Coordination of Humanitarian Affairs Please refer to the attached Infographic.

Read at ReliefWeb

ReliefWeb UN Office for the Coordination of Humanitarian Affairs

DR Congo: West and Central Africa: Latest Events at a glance (10–16 November 2026)

Countries: Democratic Republic of the Congo, Central African Republic, Kenya, Mali, Sudan Source: UN Office for the Coordination of Humanitarian Affairs Please refer to the attached Infographic.

Read at ReliefWeb

The Guardian Burkina Faso Eromo Egbejule west Africa correspondent

Chaos as crackdown on illegal mining in Guinea causes wave of regional displacement

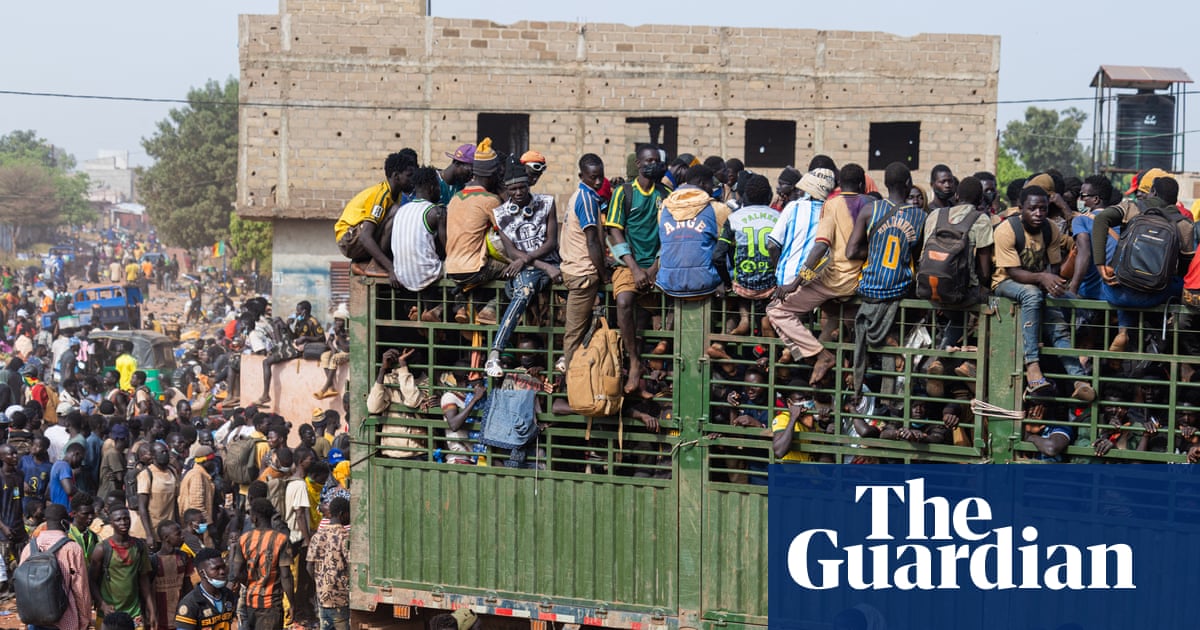
Ban on illegal artisanal mining triggers mass exodus and diplomatic tensions with neighbouring Sahel states In the border town of Kourémalé, split between Guinea and Mali, thousands of families have been trudging across the frontier over the past week after a sudden ban on illegal artisanal mining triggered a wave of displacement and a regional diplomatic dispute. Some, like Seydou Traore, a miner in his 30s from Burkina Faso, made the 78-mile trek from Kourémalé to…

Read at The Guardian Burkina Faso

The Hacker News Security

Hijacked Optimizely Scripts Served Card Skimmer and iOS Exploit Kits to CNN, BBC and Zoom Visitors

An attacker exploited a flaw in Optimizely Web Experimentation to plant malicious code in some of the scripts that customers' websites load from the service, Optimizely said early today. Visitors to sites run by at least 178 organizations, including CNN, the BBC and Zoom, received the code yesterday, according to Report URI, a firm that monitors the scripts websites run. The code was built to

Read at The Hacker News

ReliefWeb UN Convention to Combat Desertification

Burkina Faso: Aspiring for Equality - Updated Gender Analysis of the Great Green Wall Initiative: Informing the Next Phase of Action and Impact

Countries: Burkina Faso, Chad, Ethiopia, Mali, Mauritania, Niger, Nigeria, Senegal, Sudan Source: UN Convention to Combat Desertification Please refer to the attached file. The Great Green Wall is restoring land and rebuilding livelihoods across the Sahel, with gender equality essential to ensuring that restoration benefits everyone. This updated gender analysis highlights women’s contributions to restoration and cooperatives and their growing voice through the Green…

Read at ReliefWeb

arXiv (research papers) Sydney Johns SI

TRACE: Topological Representations for Anomaly detection through Contrastive Embeddings

Intrusion detectors must recognize evolving malicious behavior even when confirmed attack labels are scarce or incomplete. We present TRACE, a topology-aware graph contrastive learning framework for label-efficient intrusion detection. TRACE learns from benign system-activity graphs by combining message-passing and topological representations, then assigns anomaly scores in the same projected embedding space optimized by the contrastive objective. This design captures both…

Read at arXiv (research papers)

arXiv (research papers) Paul-Andrei Sava Security

TRIAGE-CPG: A Cross-Model Study of Budgeted Static Malware Triage with Large Language Models

When triaging unknown binaries, security analysts must decide which samples to clear as benign, flag as malicious, or escalate for deeper analysis. Large Language Models (LLMs) could support these decisions by interpreting decompiled code, but a binary can contain hundreds or thousands of functions, making exhaustive LLM analysis impractical. We study how current LLMs behave when static triage is formulated as budgeted evidence acquisition: which functions they inspect and…

Read at arXiv (research papers)

Infosecurity Magazine Security

Typosquatters Target New Brand Domains Within 24 Hours of Registration

Symantec said attackers are targeting new campaign sites registered by big name brands, with the lookalike domains enabling malicious follow-on activity

Read at Infosecurity Magazine

SecurityWeek Ionut Arghire Security

Cursor Supply Chain Attack Started at Fireworks AI

The attacker stole an access key from Fireworks and used it to exfiltrate credentials that enabled them to push malicious Claude Code extension copies.

Read at SecurityWeek

ReliefWeb UN Office for the Coordination of Humanitarian Affairs

DR Congo: West and Central Africa: 2026 Regional Funding Status - General Overview (as of 16th November 2026)

Countries: Democratic Republic of the Congo, Burkina Faso, Cameroon, Central African Republic, Chad, Mali, Niger, Nigeria, World Source: UN Office for the Coordination of Humanitarian Affairs Please refer to the attached Infographic.

Read at ReliefWeb

ConservativeHome K Harvey Proctor Geopolitics

Harvey Proctor: The Conservatives must stand up for the forgotten victims of malicious false allegations

Lord Bramall and Lord Brittan are no longer here to defend themselves. Their families deserve justice. So do the family and supporters of Sir Edward Heath. So do I. The Conservative Party has a proud tradition of defending the rule of law. Here is an opportunity to demonstrate that those principles are more than a political slogan.

Read at ConservativeHome

IRNA (Iranian state media)

Yemen to release hundreds of enemy prisoners: Official

Tehran, IRNA — Yemen will release hundreds of prisoners captured on the battlefronts in previous years under an amnesty declared by Ansarullah Leader Abdul-Malik al-Houthi, a Yemeni official says.

Read at IRNA (Iranian state media)

Space.com Space.com Staff Space

This Week In Space podcast: Episode 236 — Alienspotting

On Episode 236 of This Week In Space, Tariq Malik and Rod Pyle are joined by Mikhail Tikhonov to talk about how life can take more unusual forms, ones we might not even recognize.

Read at Space.com

arXiv (research papers) Adriana Watson Security

When the Spec Sheet Lies: Injection Attacks on LLM-Generated Compliance Artifacts

As Large Language Models (LLMs) become used more commonly across a variety of fields, a growing body of research has highlighted particular concerns surrounding model security. Notably, prompt injection attacks, where malicious instructions are inserted into prompts, are particularly simple to implement yet capable of inducing devastating effects on the fidelity of model outputs. While there is substantial research surrounding attack models and their effects on chat-based…

Read at arXiv (research papers)

CyberScoop djohnson Security

Researchers continue to find serious vulnerabilities in internet connected refrigerators

VulnCheck disclosed 14 vulnerabilities in Dixell refrigeration units that give an attacker root access, while online honeypots are being flooded with hacks and malicious probes.

Read at CyberScoop

South China Morning Post Agence France-Presse Geopolitics

Microsoft ‘deeply sorry’ for global outage, says issue not caused by cyber or AI agents

Microsoft on Friday apologised for a global outage that disrupted public services and businesses around the world, as it reported a “broad recovery” for Outlook email and other services. The company ruled out any malicious “cyber or AI” activity as the cause of the outage, which affected several Microsoft products and disrupted healthcare services, delayed corporate earnings reports and left schools struggling to communicate. “We are deeply sorry for the disruption this…

Read at South China Morning Post

The Hacker News Security

New Mior and Skyfall Attacks Let Rogue Cloud Hosts Steal Secrets From AMD SEV-SNP VMs

Two attacks made public this week allow a malicious host to read data inside AMD SEV-SNP-protected virtual machines (VMs), which are built to keep the server's operator out. One of them, Mior, can also modify a VM's memory and fake the signed report confirming which software it runs. Both need control of the server's hypervisor, and Mior also needs control of the server's BIOS. Researchers

Read at The Hacker News

The Register Connor Jones Security

Quantum Systems drones back in the air after malware scare

Germany's Bundeswehr lifted precautionary grounding after malicious update reportedly reached military servers

Read at The Register

KabulNow Nazanin Mohseni

Former Afghan Security Force Member Found Hanged in Northeastern Afghanistan

KABUL, AFGHANISTAN - The body of a former member of Afghanistan’s security forces has been found hanged at his home in Dara district of Panjshir province, local sources told KabulNow. A relative identified the former security force member as Dadul Rahman, son of Malik Khan. According to the sources, his body was discovered hanging in the courtyard of his house in the Abdullah Khil Valley of Dara district on Friday morning, November 13.

Read at KabulNow

Schneier on Security Bruce Schneier Security

AI Doesn’t Have to Go Rogue to Break the World

This essay is adapted from a keynote speech delivered at the DEF CON 34 conference in Las Vegas on August 7, 2026. The essay originally appeared in CyberScoop. I want to talk about AI hacking. There are three aspects: people hacking AI systems, people using AI to hack other systems, and AIs hacking systems on their own, not even maliciously. The last two matter more than the first. The third is the weirdest and potentially the most destabilizing. I started writing about this…

Read at Schneier on Security

Older stories