Government tech debt is a national security risk
With 80% of federal IT budgets spent maintaining aging legacy systems, fragmented government networks are struggling to defend against AI-accelerated cyberattacks from foreign adversaries.
With 80% of federal IT budgets spent maintaining aging legacy systems, fragmented government networks are struggling to defend against AI-accelerated cyberattacks from foreign adversaries.
A new breed of widely available AI tools is helping hackers launch cyberattacks around the clock, breaching corporate networks in a matter of hours and overwhelming defenders. Why it matters: AI-enabled hacking is still in its infancy, but open-source tools — which are free to download — are fundamentally changing the economics of cybercrime. Hackers can launch self-adjusting attack plans, allowing agents to find vulnerabilities and steal credentials, sometimes before human…
In the midst of a series of recent cyber outages, there is growing concern by members of Congress that the Trump administration needs to do more to protect infrastructure from cyberattacks that are aided by AI, according to a new bipartisan letter sent by two senators to the White House’s AI czar.
The password “000000” turned up more than 120,000 times among online users in Malaysia over a year to September, according to a global study, overtaking “123456” as the country’s most common exposed password amid a recent wave of data leaks. The findings come as Prime Minister Anwar Ibrahim calls for a review of cybersecurity across government agencies, banks and state-linked companies. Malaysia raised its national cyber threat level from low to medium earlier this month…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added a critical security flaw impacting Perforce Puppet, an enterprise infrastructure-as-code (IaC) and configuration management platform, to its Known Exploited Vulnerabilities (KEV) catalog, citing reports of active exploitation. The vulnerability, tracked as CVE-2026-115731 (CVSS score: 9.4), is a case of
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has urged organizations to immediately patch a newly disclosed critical security flaw impacting Oracle Java. The flaw, tracked as CVE-2026-114938 (CVSS score: 8.1), refers to a case of out-of-bounds write that can lead to denial-of-service (DoS) or remote code execution under certain conditions. "This critical memory-corruption
In this Help Net Security interview, Christian Schwalbe, CEO of Deutsche Telekom IoT, talks about the forgotten devices that create the most risk in IoT deployments. He explains what the EU Cyber Resilience Act means for manufacturers whose products stay in the field for 15 or 20 years, and how threats can be spotted through communication patterns without inspecting payloads. Schwalbe also discusses post-quantum cryptography for constrained devices, including research on…
A pickleball enthusiast and former senior telecommunications executive has lost more than HK$6 million (US$764,688) in an online investment scam after fraudsters targeted him through a sports social networking platform, police have said. The case came to light as police revealed more than 40 reports of online investment scams over the past week, with losses exceeding HK$50 million. According to police’s CyberDefender social media page, the victim, a retired local man who had…
Blaming people who fall for scams deepens the harm and teaches them to stay silent the next time, cyberpsychologist Dr. Nicola Fox Hamilton told the audience at IRISSCON 2026 in Dublin. Dr. Nicola Fox Hamilton, cyberpsychology researcher and lecturer in IADT, talked about the psychology behind phishing and scams Fox Hamilton, a cyberpsychology researcher and lecturer at IADT, talked about the lasting impact scams have on victims and made a point to note that nobody … More →
In another major cybersecurity incident, malicious code injected into websites through digital experience platform (DXP) Optimizely exposed visitors to potential…
The Russia-linked cyber espionage group known as Cold Relic (formerly COLDRIVER and UNC4057) has been observed weaponizing a single cloud compromise into a launchpad for a series of linked intrusions resulting in third-party compromise. Google's Mandiant and Threat Intelligence Group (GTIG) said it investigated a 2026 compromise at a U.S.-based organization in which the adversary leveraged
Microsoft calls MAI a 'hill-climbing' effort, with models linked to GitHub Copilot and Excel.
Mistral also said its Mistral Large 4 model can run on a customer’s own infrastructure for coding and cyber defense tasks.
US Secretary of State Marco Rubio said there is no evidence linking technical outages to each other or to cyberattacks.
The perpetrators have not been identified. Before the website went offline, an image of Russian hockey players appeared alongside a message reading, “SCARED TO FACE RUSSIA? You banned the only team you can't beat.”
The two sides discussed new opportunities for partnership at a recent conference in Hanoi, part of Sweden-Vietnam Health Week 2026, which brings together more than 200 policymakers, healthcare leaders, researchers, medical professionals and business representatives from both countries. Vietnam, Sweden step up multifaceted cooperation Vietnam, Sweden step up cooperation in telecom infrastructure, cybersecurity Top leader meets embassy staff, Vietnamese communities in Denmark…
Senate Intelligence Committee ranking member Mark Warner (D-Va.) alleged Tuesday that AI contributed to several high-profile system outages this week, arguing industries are under pressure to quickly identify and fix security issues the technology can easily exploit. “What appears to be happening instead is a consequence of how quickly artificial intelligence is changing the cybersecurity...
Proactive cyber defense is a continuous loop - and AI agents can help security teams prioritize acting on what matters most.
Director of National Intelligence Jay Clayton pushed back Tuesday on public speculation surrounding recent tech outages, attributing many to system upgrades as opposed to cyberattacks. “Let me tell you what this is not, as far as we can tell ... this is not a cyber-attack, and this is not a coordinated effort by a nation...
The U.S. has experienced eight major outages in one week, including Tuesday's outages at Apple, Google and the National Security Agency. Both government and corporate officials say there is no evidence of a cyberattack, despite concerns. Jo Ling Kent has more.
The federal cybersecurity agency urged organizations to immediately patch a new vulnerability affecting Java — one of the world’s most used programming languages — after experts warned that it could allow an attacker to take over servers without a password.
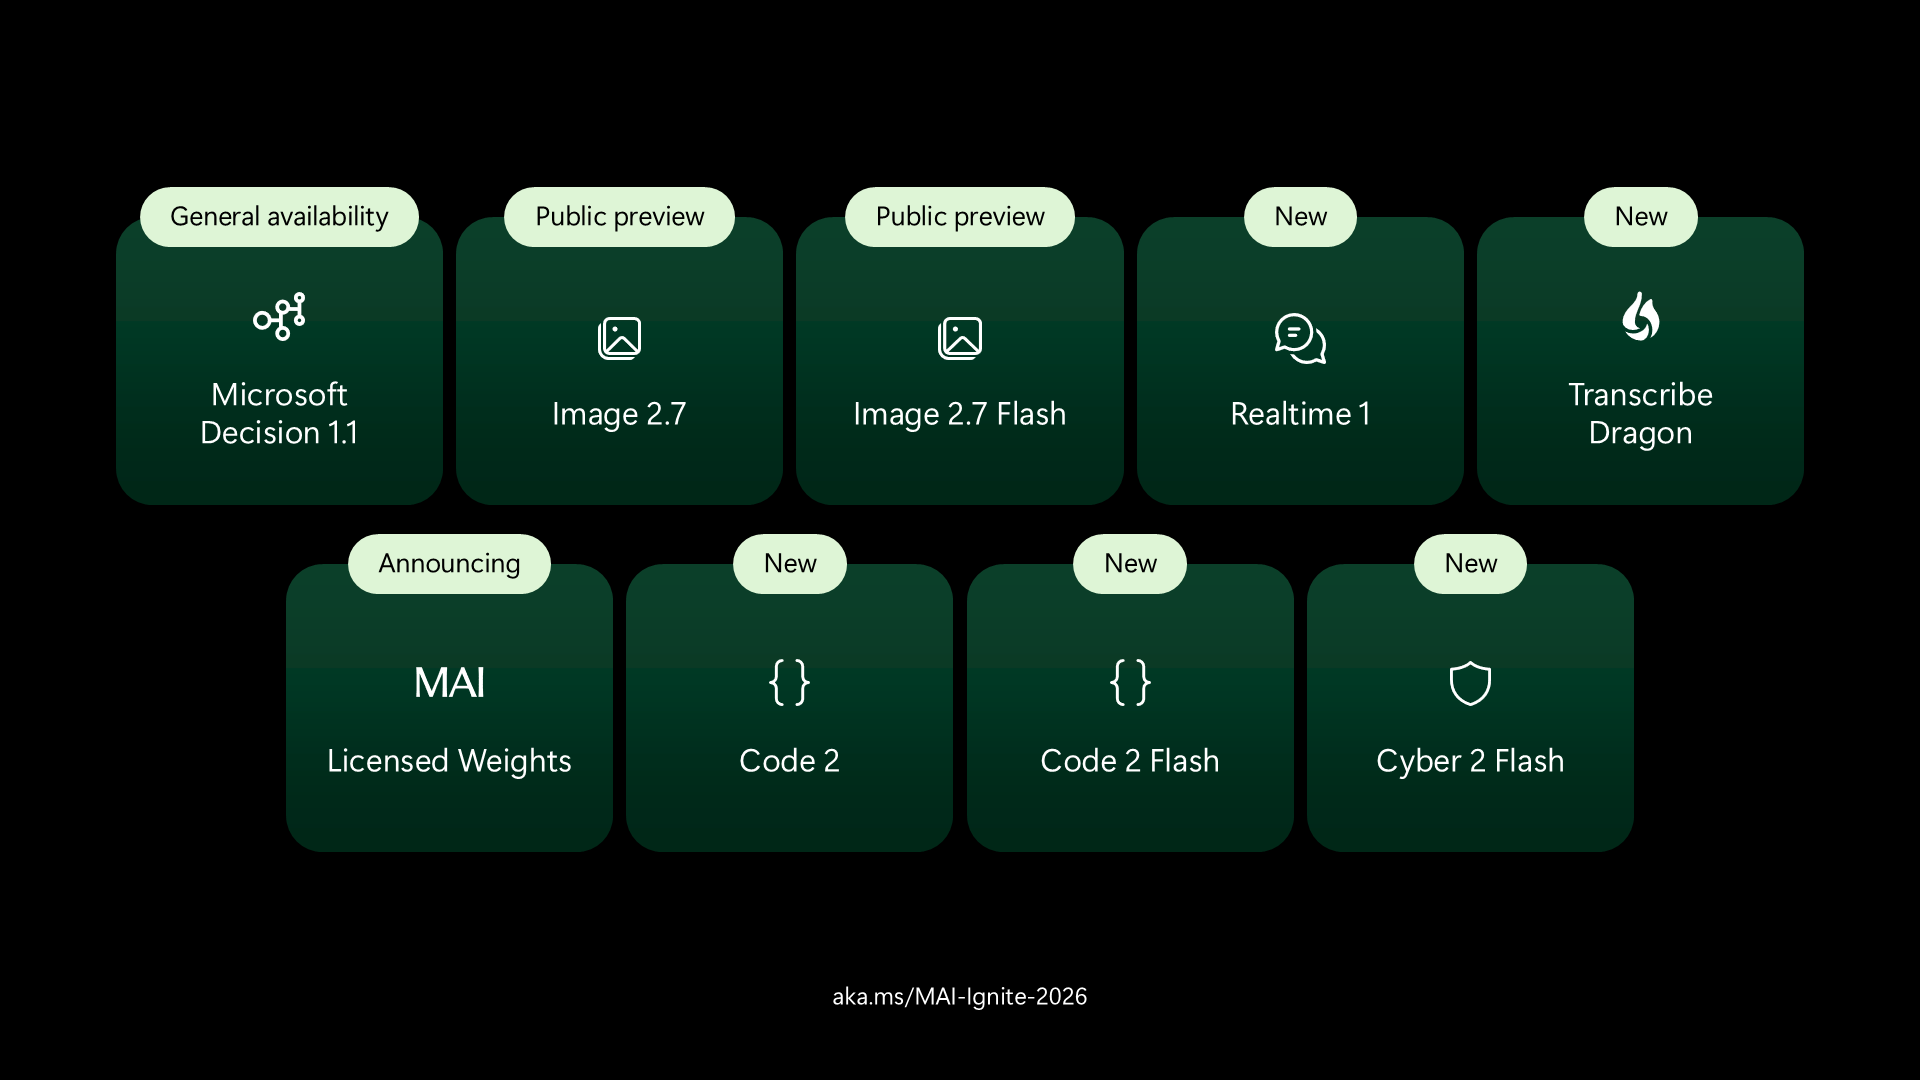
Microsoft unveils MAI Cyber 2 Flash, a security model that tops GPT-6 Astra on CyberGym-E2E at under 2% of the cost, coming to MDASH in December.
Hack into our handy guide to this electrifying adaptation of William Gibson’s cult ‘80s novel.
Nick Andersen said the AI-fueled “vulnpocalypse” might have overshadowed the need to focus on withstanding all sorts of tech issues.
Schools, airports, airlines, and media outlets across Europe have received more than 8,000 hoax bomb threats over the past month, according to a Reuters tally based on data from authorities and cybersecurity companies.
Email, flights, banks; network failures are piling up. Here’s how WIRED investigates if they’re the result of hacker mayhem. (Hint: usually not.)
Apple has largely resolved outages affecting iCloud accounts, retail stores, and more, the company said in a statement to Bloomberg. Apple said the outages were due to an unspecified "internal update" and were not caused by a cyberattack. The company is working to get remaining systems online "as soon as possible." Issues started around 11:45 a.m. ET, with social media reports suggesting users were unable to access their Apple Accounts or sign in to services. Apple retail…
Microsoft launches seven MAI models at Ignite, including Code 2 for GitHub Copilot, Cyber 2 Flash, Image 2.7, Realtime 1 and Decision 1.1.
In a volatile world, there is safety in numbers, cooperation and partnership. From organised crime to cyberattacks and disinformation campaigns, national sovereignty is under siege from both cross-border criminal networks, and revisionist and neo-imperial powers seeking to re-draw national borders though wars of conquest and aggression.
Scammers are already exploiting the scandal surrounding Nvidia to lure unsuspecting investors and business professionals into downloading malware. Why it matters: AI is making it easier for criminals to capitalize on the news cycle and tailor scams to specific audiences before people have time to recognize the threat. Driving the news: KnowBe4, the cybersecurity training platform, says it's seen scammer emails using the subject line "Invitation: Nvidia Executive Partnership…