Results for “cyber”

Committee to Protect Journalists CPJ Staff

Pakistan detains journalist Shahid Maitla for cybercrimes for alleging ex-PM was corrupt

November 19, 2026—The Committee to Protect Journalists calls on Pakistani authorities to immediately and unconditionally release journalist Shahid Maitla, instead of transferring him to restive Balochistan, drop all cybercrime charges against him, and ensure his safety. On the evening of November 17, unidentified uniformed and plainclothes individuals took Maitla, a former TV anchor who is...

Read at Committee to Protect Journalists

The Verge Emma Roth Security

JPMorgan Chase reveals data breach, but says it’s unrelated to this week’s banking outage

JPMorgan Chase says its third-party vendors suffered a cyberattack, exposing marketing data like customer names and email addresses. The confirmation follows a report from Cybernews, which says a ransomware group leaked email addresses belonging to around 16,000 JPMorgan Chase customers. In a post about the attack, JPMorgan Chase says "there is no connection" to the

Read at The Verge

The Quantum Insider Mohib Ur Rehman

SEALSQ Signs LOI to Acquire QuintessenceLabs

Insider Brief PRESS RELEASE — WISeQey Corp. (formerly known as WISeKey International Holding AG, “WISeQey”) (Nasdaq/SIX: WQEY), a global quantum cybersecurity and space IoT company, today announced that its subsidiary, SEALSQ Corp (NASDAQ: LAES) (“SEALSQ”), a company that develops and sells Semiconductors, PKI, and Post-Quantum technology hardware and software products, has signed a non-binding letter

Read at The Quantum Insider

Sky News World

EU reveals it suffered 'AI-powered' cyber attack

The EU has revealed it suffered a cyber attack powered by AI last month and some of its digital tools are still offline as a result.

Read at Sky News World

The Register Carly Page Security

Europe's biggest gas supplier battling cyberattack – with no timeline for recovery

Norwegian energy giant Equinor says oil and gas production remains unaffected

Read at The Register

Infosecurity Magazine Security

CyberPower PowerPanel Exploited to Run Malicious Code on Domain Controller

Symantec found an attacker using CyberPower’s UPS software to run scripts on a domain controller

Read at Infosecurity Magazine

The Record Security

European Commission confirms cyberattack, says hackers used AI tool

POLITICO had reported CERT-EU had identified the attackers’ use of ARTEX, an open-source AI hacking platform that the FBI last week warned was being used both by criminals and state-sponsored groups.

Read at The Record

The Register Carly Page Security

European Commission scrambles to contain AI-assisted cyberattack

Staff HR and medical reimbursement systems taken offline as officials investigate whether personal data was compromised

Read at The Register

DW Geopolitics

EU Commission confirms it was targeted in cyberattack using AI tools

The European Commission was targeted by an "AI-generated cybercampaign," a spokesperson has said. This is the first time the bloc has publicly reported an AI-based cyberattack.

Read at DW

Infosecurity Magazine Security

European Commission Confirms AI-Driven Cyber-Attack Took Systems Offline

The European Commission said the attack targeted “individual systems”, with reports that attackers leveraged ARTEX in the campaign

Read at Infosecurity Magazine

Help Net Security Sinisa Markovic Security

Russian spies turn one cloud breach into a stepping stone for the next

A Russian cyberespionage group is posing as employees of organizations it has already breached to phish new targets, Google Threat Intelligence Group (GTIG) found. Google tracks the group as COLD RELIC (also known as Star Blizzard, Callisto and Gossamer Bear), and the US Department of Justice has assessed that it operates within Russia’s Federal Security Service (FSB). COLD RELIC goes after government officials, defense contractors and NGOs in Europe and North America. “The…

Read at Help Net Security

CBS News

Americans remain skeptical after wave of outages

Americans remain skeptical after a wave of tech outages over the last week, despite the Trump administration's insistence that there are no cybersecurity threats. Jo Ling Kent reports.

Read at CBS News

Help Net Security Zeljka Zorz Security

Exploited Puppet flaw puts the server that configures your endpoint fleet at risk (CVE-2026-115731)

Attackers are exploiting CVE-2026-115731, a critical remote code execution vulnerability in Perforce Puppet Enterprise, an enterprise solution used by IT teams to centralize and automatize endpoint management. Details about the in-the-wild attacks have yet to be made public, but the US Cybersecurity and Infrastructure Security Agency (CISA) added the flaw to its Known Exploited Vulnerabilities catalog on Tuesday and ordered US federal civilian agencies to address it by…

Read at Help Net Security

Meta Newsroom Facebook

Meta premieres India’s First Government-Led Microdrama Series on Scams Awareness

Meta has partnered with The Ministry of Information & Broadcasting (MIB), Prasar Bharati, Securities and Exchange Board of India (SEBI), and Indian Cyber Crime Coordination Centre (I4C) to launch India's first government-led public interest microdrama series on online scams.

Read at Meta Newsroom

The Register Connor Jones Security

Cyberattack on service provider exposes payee data at 40 Irish credit unions

Minister calls notification delay 'not acceptable' after October attack on Irish banking player Wellington IT came to light in November

Read at The Register

Ars Technica Andy Greenberg, wired.com Security

How to tell a cyberattack from a plain old outage

When everything goes down, don’t assume it’s a cyberattack.

Read at Ars Technica

Tech.eu Tamara Djurickovic Startups

Software: Europe’s 10 most-funded companies in H1 2026

European software companies attracted investment across awide range of applications in H1 2026, with AI-powered enterprise solutions,automation, cybersecurity and developer tools emerging as key areas...

Read at Tech.eu

The Hill Niall Stanage Geopolitics

The Memo: Trump administration fails to quell concern over cascade of tech outages

The Trump administration is not out of the woods yet on the knotty issues of cybersecurity, AI threats and creaky tech infrastructure — even though almost a week has gone by since the nation’s longest air traffic ground stop in a quarter-century. The hours-long collapse of the Federal Aviation Administration’s (FAA) air traffic control system...

Read at The Hill

Axios Dan Cox

Putting cyber risk in perspective, from the experts (our own CTO)

Axios chief technology officer Dan Cox, who's spent 25 years at some of the world's biggest tech companies, puts the recent spate of high-profile failures in perspective: My parents, my siblings and plenty of other people are asking the same question: How worried should we be? The big picture: I've been in technology a long time. I take these threats seriously, but I'm not in panic mode. When something breaks, we need to understand what happened, how far it reaches and what…

Read at Axios

Axios Avery Lotz

Doomsday prepping goes mainstream

The internet has caught the emergency preparation bug, fueled by fears of AI-led cyberattacks, power grid vulnerabilities, transportation standstills and international threats. The big picture: The "prepper" mindset is resonating with larger slices of society — who are packing emergency bags, stocking up on water and taking inventory of non-perishables. Michael Mills, a University of Greenwich senior lecturer who studies doomsday preparation, says some people are turning to…

Read at Axios

Axios Sam Sabin

Exclusive: Bots amplified conspiracy theories and panic about recent tech outages

Bot accounts have helped spread conspiracy theories about a wave of major tech outages over the last week, according to new research shared exclusively with Axios. Why it matters: Purveyors of disinformation appear to be exploiting public anxiety over the cyberattacks and fragile infrastructure, amplifying suspicions of coordinated cyberattacks and government cover-ups. While it's unclear who's behind these accounts, the pattern shows that when technology failures lack…

Read at Axios

Analytics India Magazine Kileuna Haralu SI

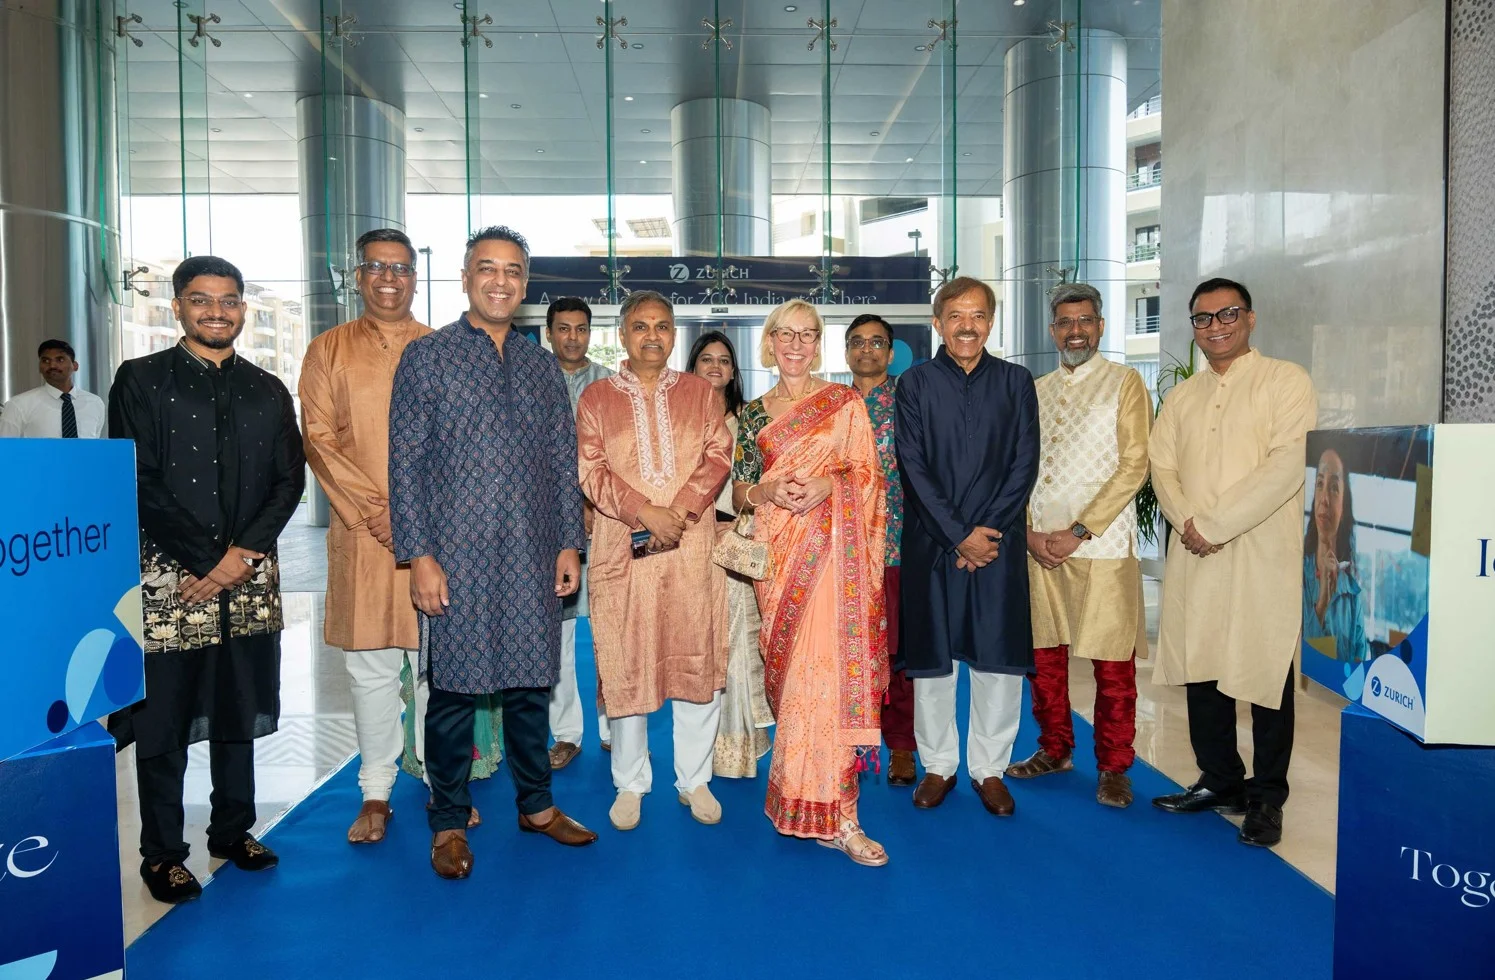
Zurich Insurance to Expand Hyderabad GCC With 1,000 Employees By 2028

Zurich Insurance Group plans to hire across cloud engineering, data and AI, application development, and cybersecurity roles.

Read at Analytics India Magazine

arXiv (research papers) Yule Ding Security

On the Reliability of CyberGym Evaluation: Task Material Consistency and Reference-Target Identity

CyberGym evaluates vulnerability reproduction by checking whether a proof-of-concept input (PoC) crashes a vulnerable program version but not a fixed version. Interpreting this differential pass as successful reproduction requires consistent task materials and evidence that the PoC triggers the intended defect. We examine these requirements through a material audit of all 1,507 CyberGym tasks and an identity assessment of the final PoCs from one complete Level-1 GLM-5.3 run…

Read at arXiv (research papers)

Help Net Security Sinisa Markovic Security

US enlists private firms to cut scammers off from victims’ cash

Stopping victims’ money before it reaches foreign scam, cybercrime and sextortion networks is the goal of a new US unit launched by the Homeland Security Task Force (HSTF). The Threat Disruption Center is part of the HSTF’s National Coordination Center (NCC) in Fairfax, Virginia. The task force calls it “a shared technology resource and collaboration hub.” Investigators will get tools to sort incoming victim complaints and map the criminal groups behind them, along with…

Read at Help Net Security

The Hacker News Security

CISA Warns of 4 Exploited Flaws Linked to Ransomware, Cryptomining, and LLMjacking Attacks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added four vulnerabilities impacting Synology DiskStation Manager (DSM), BerriAI LiteLLM, Apache Axis, and Vanderbilt University Research Electronic Data Capture (REDCap) to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerabilities are listed below -

Read at The Hacker News

Dark Reading Robert Lemos Security

Africa Retakes Top Spot as Most Attacked Region, Led by Nigeria Surge

Nigeria faced more than double the cyber threats of the previous year, with Angola and Kenya also in the top-5 most attacked countries globally.

Read at Dark Reading

The National (UAE) The National Geopolitics

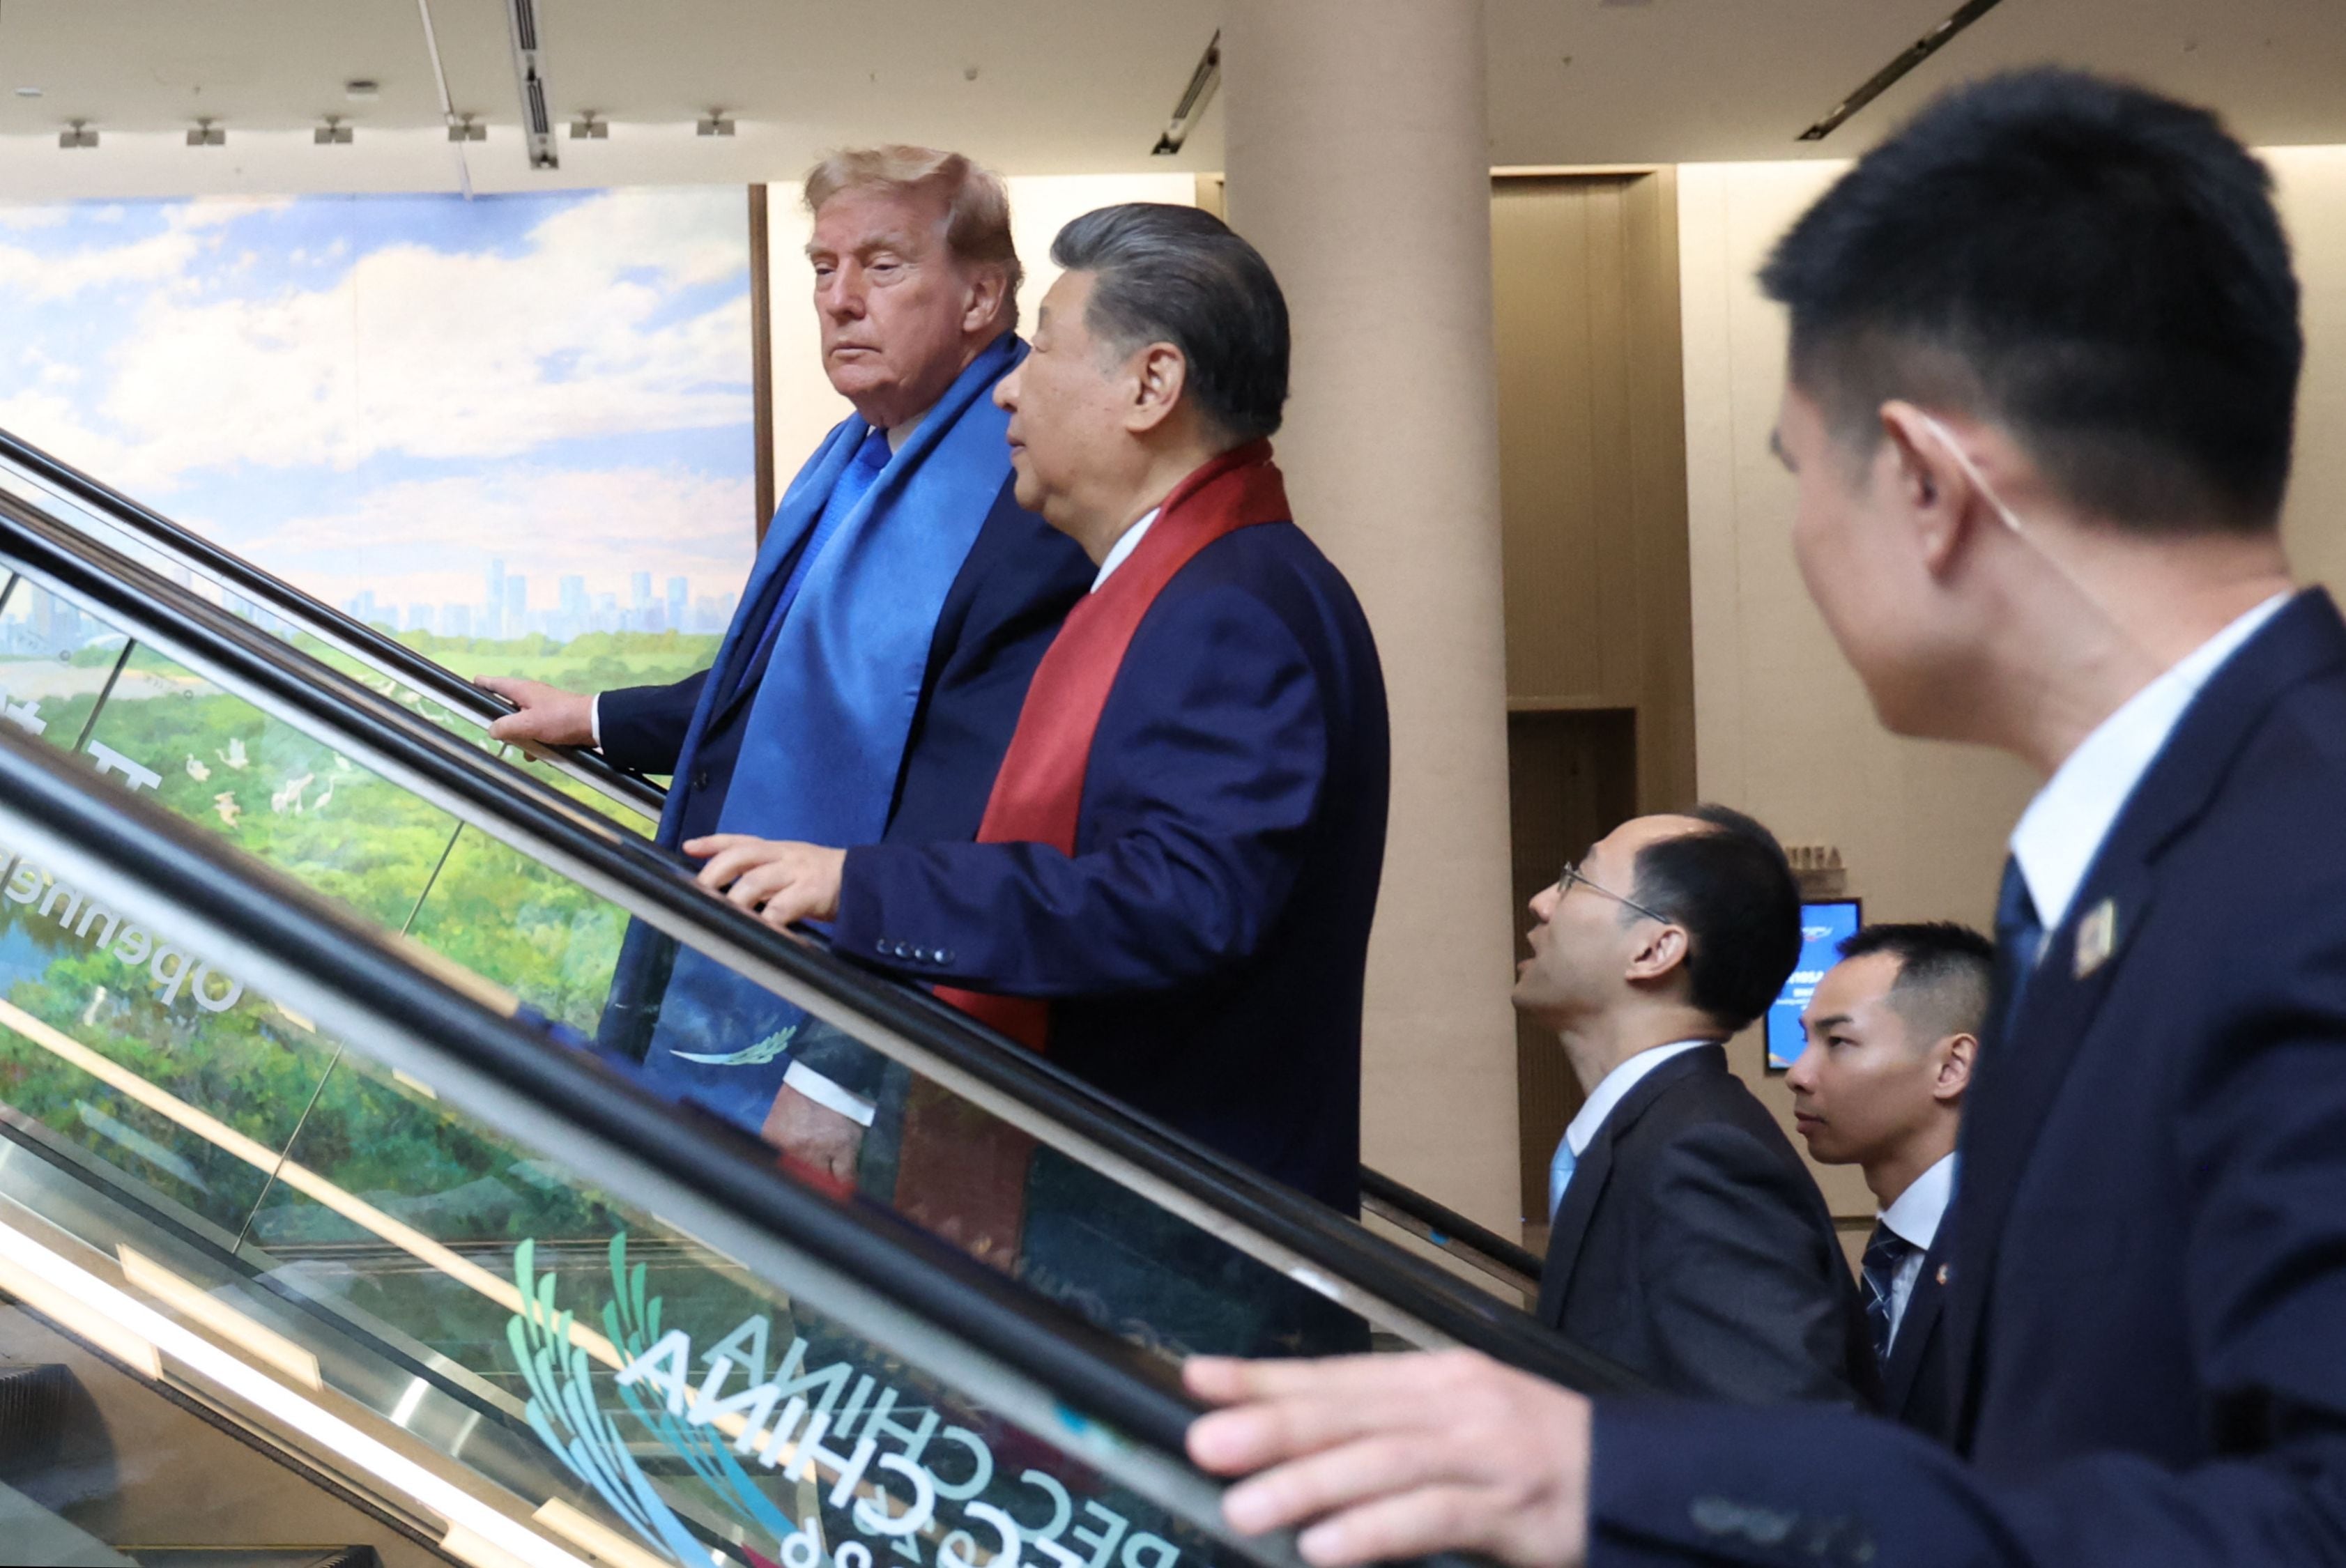
Trump to begin talks in China, Jordan's $5.8 billion water project and Uber's driverless cars in Dubai

Today on Trending Middle East, US President Donald Trump will hold talks with the leaders of China and Russia in the Chinese city of Shenzhen, with the war in Iran expected to be a major focus. Saudi Arabia says a Houthi missile launched towards Riyadh has caused material damage from falling debris. The UAE's cyber-security chief has revealed that Iran used destructive malware against the Emirates' electricity, water, healthcare and education systems during the war. The…

Read at The National (UAE)

SecurityWeek SecurityWeek News Security

Palo Alto Networks to Buy AI Startup Applied Compute for $4.5 Billion

The all-stock deal will give the cybersecurity company a platform for fine-tuning and running open-weight AI models in public and sovereign clouds.

Read at SecurityWeek

Ukrinform

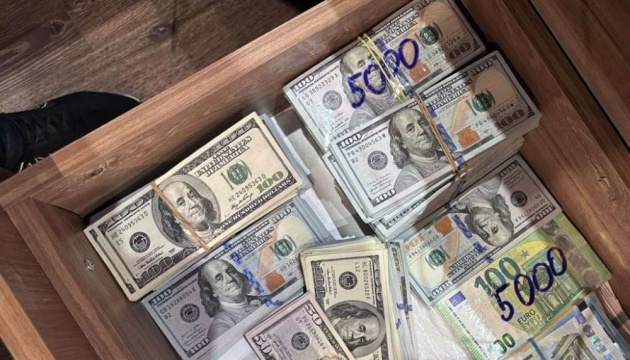
Ukrainian law enforcers, FBI expose hacking network that stole data and demanded multimillion-dollar ransoms

The Ukrainian Prosecutor General’s Office, in cooperation with the U.S. Federal Bureau of Investigation (FBI), has exposed an international criminal organization whose members carried out large-scale cyberattacks on foreign companies and demanded ransoms totaling more than $40 million.

Read at Ukrinform

Ukrinform

Ukrainian law enforcers, FBI expose hacking network that stole data and demanded multimillion-dollar ransoms

The Ukrainian Prosecutor General’s Office, in cooperation with the U.S. Federal Bureau of Investigation (FBI), has exposed an international criminal organization whose members carried out large-scale cyberattacks on foreign companies and demanded ransoms totaling more than $40 million.

Read at Ukrinform

Older stories