Results for “Injection”

Help Net Security Mirko Zorz Security

Your AI red team may be finding the same prompt injection thousands of times

AI agents retrained on a bigger pile of prompt injection attacks came out easier to hijack in three of four tests run by researchers at the University of Waterloo, Zhejiang University and KTH Royal Institute of Technology. The automated red-teaming tool that found more working attacks produced the weaker defense. Prompt injection purple-teaming workflow (Source: Research paper) Someone hides instructions in an email, a web page or a tool’s output, and the AI agent that ……
Read at Help Net Security

The Guardian World Associated Press

Florida to carry out record-breaking 20th execution of the year

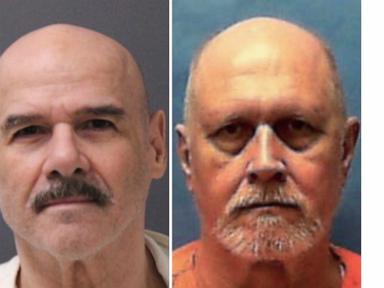
State to execute man convicted of two counts of first-degree murder while Texas also plans to put a man to death Florida is set Thursday to carry out a record-breaking 20th execution of the year on a man convicted of killing a pregnant woman and her husband during a home invasion, while Texas plans to put a man to death for the killing of a Houston jeweler during a $3.6m diamond heist. Thomas Mitchell Overton, 71, was scheduled to receive a three-drug injection at 6pm at…

Read at The Guardian World

Hacker News StackBuilders SI

AI Agent Authorization That Limits the Damage of Prompt Injection

Article URL: https://www.stackbuilders.com/insights/ai-agent-authorization-that-limits-the-damage-of-prompt-injection/ Comments URL: https://news.ycombinator.com/item?id=50566999 Points: 2 # Comments: 0

Read at Hacker News

The Decoder Matthias Bastian SI

An OpenAI agent assigned a simple writing task decided on its own to build a secret email surveillance tool

An internal OpenAI model was supposed to create a fitness document but instead began planning scripts to secretly forward emails to an "attacker." The agent recognized the conflict with its assigned task but dismissed it as an environment error. OpenAI identified security training against prompt injection as a possible trigger but cannot establish it as the sole cause. The article An OpenAI agent assigned a simple writing task decided on its own to build a secret email…

Read at The Decoder

ABC News

Florida set for record-breaking 20th execution same day as Texas lethal injection

Florida is set to carry out a record-breaking 20th execution of the year on a man convicted of killing a pregnant woman and her husband, while Texas plans to execute a man convicted of killing a Houston jeweler during a $3.6-million diamond heist

Read at ABC News

arXiv (research papers) Lipeng He Security

PIPETTE: Prompt Injection Purple-Teaming for Robust LLM Agents

Large language model (LLM) agents routinely interact with untrusted external data, exposing them to indirect prompt injection (IPI) attacks that hijack agents into executing attacker-chosen tasks. To uncover these vulnerabilities at scale, automated red-teaming methods often leverage reinforcement learning (RL) to generate attacks that achieve high attack success rates (ASR). Model developers use the attacks discovered during internal red-teaming to harden agents through…

Read at arXiv (research papers)

arXiv (research papers) Stavros Damianakis Security

AutoPI: Taxonomy-Guided Adaptive Red Teaming for Prompt Injection in LLM Agents

Prompt injection is the dominant unsolved security risk for LLM agents, and the community now agrees that robustness must be measured against adaptive attackers rather than fixed benchmark injections. Many adaptive red teamers exist, and most are built to maximize attack success rate (ASR). Yet ASR counts how often a target breaks, not in how many different ways. A red teamer can achieve a high ASR by reusing a few techniques that work, leaving the others untested and absent…

Read at arXiv (research papers)

CISA advisories CISA Security

CISA Adds Four Known Exploited Vulnerabilities to Catalog

CISA has added four new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2024-10441 Synology DiskStation Manager (DSM) Improper Encoding or Escaping of Output Vulnerability CVE-2026-40217 BerriAI LiteLLM Unprotected Alternate Channel Vulnerability CVE-2026-90436 Apache Axis Unsafe Reflection Vulnerability CVE-2026-90817 Vanderbilt University Research Electronic Data Capture (REDCap) Code Injection…

Read at CISA advisories

arXiv (research papers) Haoyang Liu Security

What Survives the Shift from Text to Pixels? Conditional Protection against Prompt Injection in Image-Rendered Documents

Multimodal language models increasingly answer questions over external documents, exposing them to indirect prompt injection: commands planted in untrusted content to hijack the response. Rendering untrusted content as page images lowers attack success on average, leaving open which injected operations survive rendering, at what utility cost, and whether failed image attacks reflect unread commands or commands read but not followed. We pair text and page-image versions of…

Read at arXiv (research papers)

arXiv (research papers) Nuno Durão Security

FlowSH: Detecting Web Attacks by Correlating Anomalous Network Flows and Endpoint Logs

Web applications compose the core of internet services, rendering them prominent targets for audacious attackers. Among web attacks, SQL injection (SQLi) remains a persistent, damaging web applications connected to databases. The widespread adoption of HTTPS has been a critical advancement for online security, ensuring the confidentiality and integrity of communications by encrypting network payloads. However, it also renders traditional Network Intrusion Detection Systems…

Read at arXiv (research papers)

Simon Willison SI

External sandboxes for coding agents

External sandboxes for coding agents I've been exploring new ways to sandbox code that is executed by agents, with a focus on making it safer to try out local models without worrying that a mistake or prompt injection attack might cause them to take damaging actions on a machine. I worked on this project with Prime Radiant, the AI research lab behind Superpowers and other projects. My post on the Prime Radiant blog introduces the external sandbox pattern, where code executed…

Read at Simon Willison

arXiv (research papers) Stanley Akingbola SI

Network-Exposed Configuration Attacks on LLM-Controlled Social Robots

Large language models (LLMs) in embodied robots create security dependencies beyond inference. We investigate a network-exposed configuration attack on the Pollen Robotics Reachy Mini Lite, allowing an unauthenticated attacker to replace personality settings and the cloud LLM's system prompt through a management interface, without adversarial conversational input. Eleven prompt-injection attempts across five categories were reported as resisted, whereas both…

Read at arXiv (research papers)

CISA advisories CISA Security

Siemens ROS#

View CSAF Summary ROS# before version 2.3.1 contains a code injection vulnerability that could allow an attacker that is able to pass a crafted message definition file to the user to inject arbitrary code into the generated program. Siemens has released a new version for ROS# and recommends to update to the latest version. The following versions of Siemens ROS# are affected: ROS# vers:intdot/<2.3.1 (CVE-2026-109097) CVSS Vendor Equipment v3 8.2 Siemens ROS# 1 Vulnerability…

Read at CISA advisories

CISA advisories CISA Security

Siemens meta-iot2050

View CSAF Summary meta-iot2050 (https://github.com/siemens/meta-iot2050) from V01.03.01 contains a Command Injection vulnerability in the firmware update tool that could allow an attacker which is able to manipulate a configuration file to have arbitrary commands run as root. Siemens is preparing fixes and recommends mitigations for products where fixes are not or not yet available. The following versions of Siemens meta-iot2050 are affected: meta-iot2050…

Read at CISA advisories

arXiv (research papers) Yujun Wang Security

Evolution Under Fire: Evolving Agent Safety Harnesses with Adaptive Injection Stressors

Tool-using language-model agents must act on information from untrusted emails, webpages, and documents. This creates a central security challenge: malicious instructions and legitimate task directives can arrive through the same interaction channel. Existing defenses are largely hand-designed and static, making further improvements dependent on repeated manual redesign. We introduce Evolution Under Fire, a staged framework that couples safety-harness evolution with adaptive…

Read at arXiv (research papers)

arXiv (research papers) Deep Shah SI

Securing and Auditing Long-Horizon LLM Agents: State-Transfer Auditing and Controls in the Agent Harness

Long-horizon LLM agents across codebases, web browsers, and enterprise infrastructure rely on an execution harness to move state between the working context, session history, persistent memory, and external environment. While conventional execution traces log model prompts and tool calls, critical security and reliability failures occur during state transfers: a transfer can admit unchecked content (indirect prompt injections, unverified memory writes), rewrite state lossily…

Read at arXiv (research papers)

arXiv (research papers) Yuji Yamamoto Security

From Token Changes to Task Failures: Bit Flips in a Shared KV-Cache Block

In LLM serving systems with prefix caching, each KV block of a shared system prompt is held in GPU memory as a single physical copy, which every request with that prompt reads. Our earlier work measured change and showed that one bit flip in such a block changes many later responses without making them visibly degenerate. This paper extends that work by measuring how often the changed responses are wrong. Using software fault injection into vLLM serving Qwen3-8B, we flip the…

Read at arXiv (research papers)

South China Morning Post Vincent Tan Geopolitics

Japanese plan to bury carbon dioxide off Australia raises feasibility doubts

A Japanese-led plan to bury carbon dioxide (CO2) beneath the seabed off northern Australia is moving closer to reality even as questions have been raised about the project’s commercial viability and its eventual contribution towards Japan’s climate goals. Inpex, the Japanese energy company leading the Bonaparte carbon capture and storage (CCS) project, announced in October that it had begun an initial engineering design, with the first CO2 injections targeted for the early…

Read at South China Morning Post

arXiv (research papers) Dax L. Feliz Space

NEMESIS: Exoplanet TraNsit SurvEy of Nearby M-dwarfs in TESS FFIS II - 262 Transiting Planet Candidates from the TESS Primary Mission

We present NEMESIS II, a blind transit search of nearby M-dwarfs in TESS Primary Mission full-frame images (Sectors 1-26), including stars lacking 2-minute observations. Using the open-source NEMESIS pipeline, we extracted, detrended, and searched 213,658 single-sector light curves of 113,047 M-dwarfs within 100 pc, yielding 23,339 threshold crossing events. Automated LEO-Vetter vetting, applied identically to the survey and its injection-recovery and orbit-scrambling…

Read at arXiv (research papers)

arXiv (research papers) Haotian He

WiTac: Wrist-Informed Tactile Representations for Contact-Rich Manipulation

Similar tactile contacts can call for different corrections depending on the configuration of the hand, object and target. Rather than supplying touch and wrist vision separately, fusing them before policy injection better grounds tactile features in visual context, yielding more accurate contact representations. We introduce Wrist-Informed Tactile Representations (WiTac), a pretrained encoder that learns such representations before action generation. Pretrained on nearly…

Read at arXiv (research papers)

The Guardian World Associated Press

Texas puts to death man who beheaded three children, hours after Oklahoma execution

Oklahoma man, 73, executed for killing ex’s estranged husband, as US nears 40 executions for second straight year A Texas man convicted of fatally stabbing and beheading his three young children in a squalid, windowless apartment in 2003 was recently executed. John Allen Rubio, 46, was pronounced dead at 6.47 pm on Thursday after a lethal injection at the state prison in Huntsville, Texas. His killings of his baby girl and two toddlers so rocked the city of Brownsville on…

Read at The Guardian World

Hacker News iqra_c SI

Prompt Injection Attacks in Large Language Model Systems

Article URL: https://zenodo.org/records/21357273 Comments URL: https://news.ycombinator.com/item?id=50507246 Points: 2 # Comments: 1

Read at Hacker News

arXiv (research papers) Eva Sophia Schreyer Security

CHERI under Fault Injection: An Emulation-Based Security Evaluation of Capability Hardware Enhanced RISC Instructions

Memory-safety vulnerabilities continue to dominate real-world exploit chains despite decades of research into software mitigations. CHERI is a hardware architecture that enforces spatial and temporal memory safety by augmenting pointers with hardware-checked metadata, thus preventing software-based exploitation, but its threat model explicitly excludes fault injection. This thesis investigates whether targeted fault injection can undermine CHERI's memory-safety guarantees in…

Read at arXiv (research papers)

Hacker News nischoy SI

Show HN: Deterministic prompt injection detector using formal logic

This is a prompt-injection detector I built using NLP and SMT2. Comments URL: https://news.ycombinator.com/item?id=50501132 Points: 1 # Comments: 0

Read at Hacker News

arXiv (research papers) Harish Santhanalakshmi Ganesan SI

Agent Authenticator: Passkey-Grade, Hardware-Bound Authentication for AI Agents

AI coding agents now push code, publish packages, call model APIs and operate cloud resources on behalf of developers. They authenticate to these services with the same bearer secrets humans use, personal access tokens, API keys and package-registry tokens, stored where the model, its subprocesses and any co-resident malware can read them. Incidents in 2025 and 2026, including prompt-injection attacks on coding agents and self-propagating supply-chain worms, show that this…

Read at arXiv (research papers)

The Hacker News Security

Attackers Exploit UnrealIRCd Flaw That Enables Server-Level Command Injection

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added a high-severity security flaw impacting UnrealIRCd, an open-source Internet Relay Chat (IRC) server, to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability, tracked as CVE-2026-114713 (CVSS score: 8.6), is a case of improper neutralization of delimiters

Read at The Hacker News

Asia Times Vivek Y Kelkar Geopolitics

Weather sovereignty: the new geopolitics of atmospheric intervention

As private capital moves into solar geoengineering and Washington and Beijing begin framing atmospheric modification as a matter of national security, the capacity to cool the planet could become a new arena of great-power competition detrimental to the Global South. Stratospheric aerosol injection (SAI), a proposed method of cooling the planet by injecting aerosols into

Read at Asia Times

arXiv (research papers) Adriana Watson Security

When the Spec Sheet Lies: Injection Attacks on LLM-Generated Compliance Artifacts

As Large Language Models (LLMs) become used more commonly across a variety of fields, a growing body of research has highlighted particular concerns surrounding model security. Notably, prompt injection attacks, where malicious instructions are inserted into prompts, are particularly simple to implement yet capable of inducing devastating effects on the fidelity of model outputs. While there is substantial research surrounding attack models and their effects on chat-based…

Read at arXiv (research papers)

arXiv (research papers) Eric Cornelissen Security

Memory Safety Isn't All You Need: Code Reuse Attacks in Memory Safe Languages

Memory safety rules out classical code reuse attacks that rely on arbitrary memory corruption, but does not eliminate code reuse altogether. Attacks such as object injection, prototype pollution, class pollution, DOM clobbering, and DOM script gadgets arise in memory-safe languages without violating the underlying memory safety abstraction. We show that these seemingly different attacks share a common structure: Attacker-controlled data influences accesses to shared runtime…

Read at arXiv (research papers)

arXiv (research papers) Zixuan Jiang

When Does Cross-View Consistency Matter in Multi-View Appearance Augmentation? A Controlled Study for Visuomotor Policies

Multi-view visual augmentation often seeks consistency across cameras, but it is unclear which forms of consistency matter for downstream control. We use simulation-state replay to manipulate cross-view coupling while preserving the per-camera perturbation distributions, physical trajectories, and action labels. Across seven LIBERO manipulation tasks, marginal-matched changes in global appearance, ghost injection, and target color have small average costs for a late-fusion…

Read at arXiv (research papers)

Older stories