Results for “Mali”

ReliefWeb International Federation of Red Cross and Red Crescent Societies

World: Global Update | November 2026: An Inter-Agency Report of the Global ENSO Analysis Cell - El Niño Status & Humanitarian Outlook

Countries: World, Afghanistan, Angola, Bangladesh, Burkina Faso, Burundi, Cambodia, Cameroon, Central African Republic, Chad, Colombia, Cuba, Djibouti, Dominica, Ecuador, El Salvador, Ethiopia, Fiji, Guatemala, Haiti, Honduras, India, Indonesia, Kenya, Madagascar, Malawi, Mali, Marshall Islands, Micronesia (Federated States of), Mozambique, Myanmar, Nepal, Nicaragua, Niger, Nigeria, Pakistan, Papua New Guinea, Peru, Philippines, Saint Lucia, Samoa, Solomon Islands, Somalia…

Read at ReliefWeb

ReliefWeb Food and Agriculture Organization of the United Nations

World: Locust Watch: Seasonal precipitation predictions in the Desert Locust winter and spring breeding areas (December 2026–May 2027) (19 November 2026)

Countries: World, Algeria, Chad, Djibouti, Egypt, Eritrea, Ethiopia, India, Iran (Islamic Republic of), Libya, Mali, Mauritania, Morocco, Niger, Oman, Pakistan, Saudi Arabia, Somalia, Sudan, Tunisia, Yemen Source: Food and Agriculture Organization of the United Nations Please refer to the attached file. The extremely strong El Niño reaches its peak. Dry conditions are expected across most regions until the end of November, except for parts along the Red Sea coasts and in…

Read at ReliefWeb

ReliefWeb United Nations Population Fund

UNFPA Situation Report: Crisis in Mali - October 2026

Country: Mali Source: United Nations Population Fund Please refer to the attached file. During October, Mali continued to face persistent instability and complex protection challenges, including the forced recruitment of young people, widespread displacement of communities, and gender-based violence. While the reopening of transit routes into Léré marked a significant improvement in humanitarian access for relief operations, comprehensive rapid assessments revealed critical…

Read at ReliefWeb

Al Jazeera Geopolitics

Trump’s case against NYT and Penguin Random House may proceed: Judge

The lawsuit cited a book about Trump by two NYT reporters and what it said were 'false, malicious, defamatory' articles.

Read at Al Jazeera

The Moscow Times

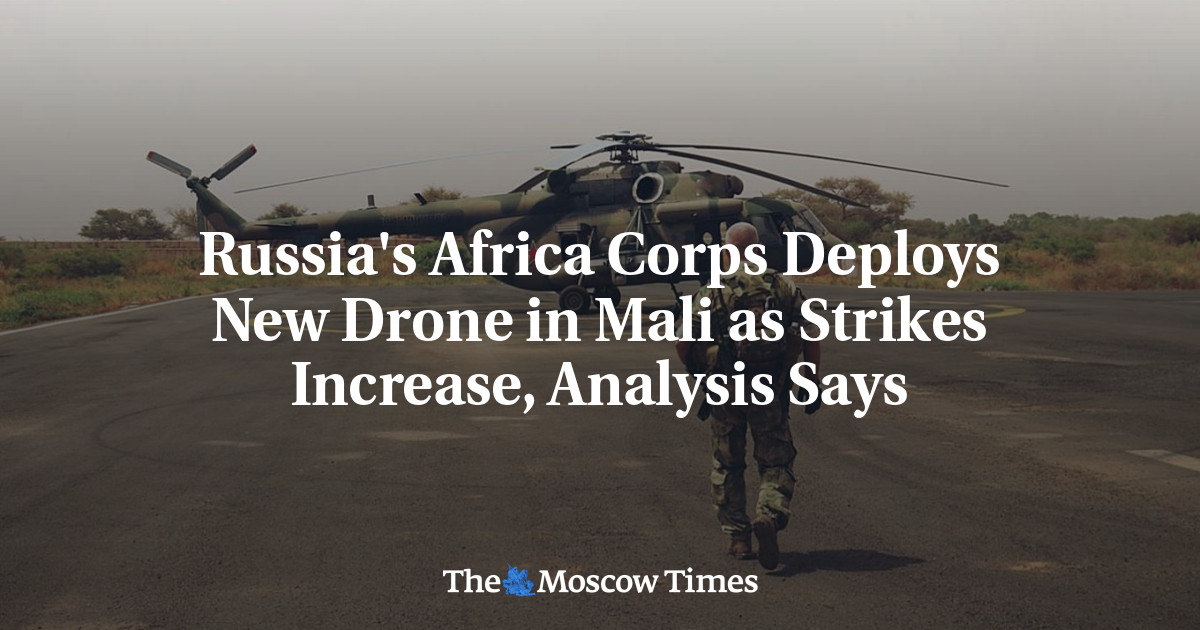
Russia's Africa Corps Deploys New Drone in Mali as Strikes Increase, Analysis Says

Russia's Africa Corps has around 2,500 men fighting alongside Mali's military government against a range of separatist rebels and militants.

Read at The Moscow Times

arXiv (research papers) Saharnaz Mehrani Security

When Suspicion Adds Up: A Stochastic Framework for Optimizing Honeypot-Based Insider-Threat Detection

Insider threats pose security risks when employees or other trusted users misuse their access to organizational systems. Detecting these threats is difficult because harmful activity can resemble routine behavior. Honeypots, or decoy resources monitored for suspicious interactions, can provide evidence of potentially malicious activity. We develop a decision framework that models evidence accumulation through honeypot interactions using a continuous-time Markov chain and…

Read at arXiv (research papers)

Infosecurity Magazine Security

CyberPower PowerPanel Exploited to Run Malicious Code on Domain Controller

Symantec found an attacker using CyberPower’s UPS software to run scripts on a domain controller

Read at Infosecurity Magazine

arXiv (research papers) Nehal Ameen Security

Phantom of the Masquerade: Graph Neural Network-Based Detection of Masquerade Attacks in Controller Area Networks

The lack of built-in security in controller area networks (CANs) exposes modern vehicles and industrial systems to masquerade attacks that can compromise safety and reliability. These attacks inject malicious messages that mimic legitimate communication patterns, making them difficult to detect using existing intrusion detection systems (IDS). Prior graph-based IDS approaches often rely on shallow embeddings that decouple representation learning from classification, which…

Read at arXiv (research papers)

Help Net Security Sinisa Markovic Security

Credential stealer slipped into Microsoft’s official Python agent framework

Two releases of Microsoft’s official agent-framework package on the Python Package Index (PyPI) carried code that steals cloud and CI/CD credentials from developers’ systems. Agent Framework is Microsoft’s open-source toolkit for building AI agents and running them in workflows. Three supply chain security companies, StepSecurity, OX Security and Socket, caught the malicious versions and shared their analysis. “On November 17, 2026, versions 1.26.1 and 1.26.2 of the official…

Read at Help Net Security

ReliefWeb International Committee of the Red Cross

Mali: People returning from gold-panning sites in Guinea get help on arrival

Countries: Mali, Guinea Source: International Committee of the Red Cross Bamako (CRM/ICRC) – At the beginning of November 2026, over 160,000 people crossed into Mali from Guinea at short notice, following the closure of the gold-panning areas of northern Guinea where they were working. Exhausted after covering long distances on foot, they are staying at several locations in Mali. Many arrived with nothing to live on. On 5 November, volunteers from the Mali Red Cross…

Read at ReliefWeb

The Guardian World Alexandra Topping Political correspondent Geopolitics

Tulip Siddiq says she is considering legal action against former Bangladesh leader

Former minister, who was sentenced to prison in Bangladesh in her absence, says she was victim of ‘malicious prosecution’ The former minister Tulip Siddiq has said she is considering taking legal action against the former interim leader of Bangladesh over corruption allegations made by his administration led her to resign from the UK government last year. The MP for Hampstead and Highgate, whose aunt Sheikh Hasina was put on trial in absentia over crimes against humanity…

Read at The Guardian World

ReliefWeb UN Development Programme

World: EU and UNDP Expand Partnership to Strengthen Local Conflict Prevention and Peacebuilding

Countries: World, Gambia, Guatemala, Mali, Moldova, Papua New Guinea, Peru, Sri Lanka, Yemen Source: UN Development Programme New phase of Insider Mediation programme will help local peacebuilders respond more rapidly to emerging tensions and prevent conflict. November 17, 2026 New York and Brussels – The United Nations Development Programme (UNDP) and the European Union (EU) have launched a new phase of their partnership on Insider Mediation (2026-2029), expanding support…

Read at ReliefWeb

CBS News

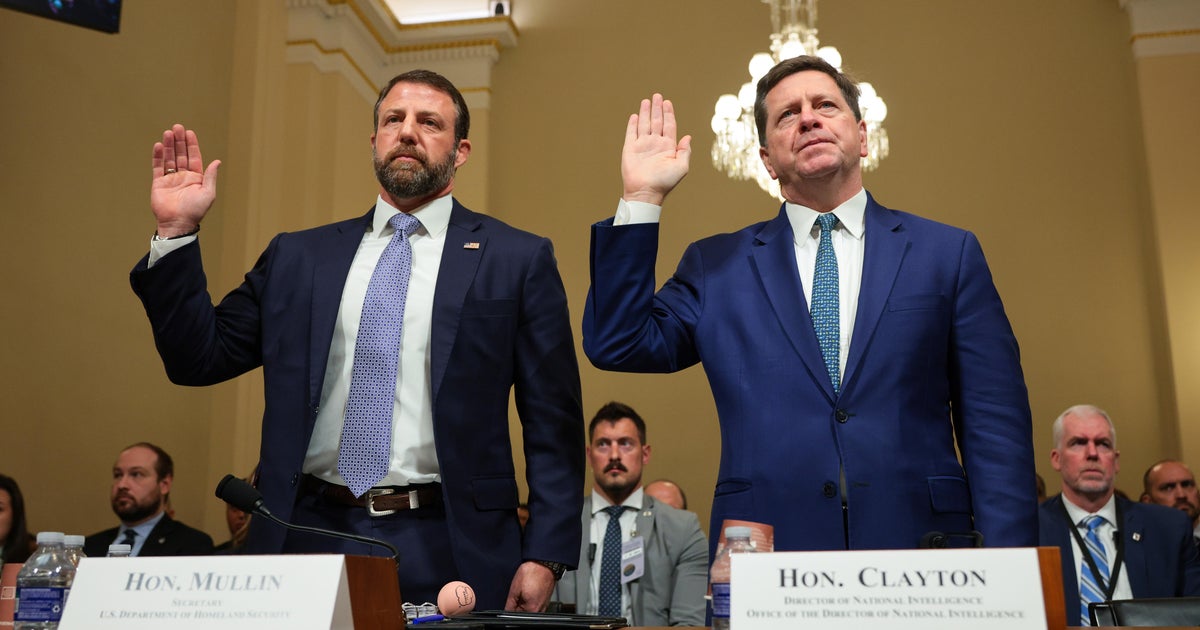
"Cyber malicious activity" not related to outages, officials say

Officials are testifying at a House committee hearing on worldwide threats as a series of network outages, including Microsoft Outlook and several banking institutions, have rattled Americans.

Read at CBS News

arXiv (research papers) Omkar Shrikanth Security

Stealing Exact Training Data from Other Clients during Federated Learning

Malicious adversaries can employ gradient inversion attacks to reverse-engineer private data using the model updates of a round in Federated Learning. While there have been developments in gradient inversion for text, exact text recovery by a malicious client has so far remained infeasible, as FedAvg entangles the gradient contributions of many clients and obscures the signal of any individual sentence. We introduce a novel attack pipeline that unwinds this entanglement…

Read at arXiv (research papers)

arXiv (research papers) Haochen Sun Security

Robust, Lightweight Locally Differentially Private Histogram Estimation and the Role of Dropout Attacks

Local differential privacy (LDP) is vulnerable to output manipulation by malicious clients. Zero-knowledge proofs can enforce correct report computation, but clients may still selectively drop out after inspecting their outputs. Prior work combines zero-knowledge proofs with homomorphic encryption to hide reports from clients and prevent selective dropout, but incurs substantial computational cost. We instead develop a three-message lightweight verification framework for…

Read at arXiv (research papers)

arXiv (research papers) Mohammed A. Alharbi Security

Drift-Aware Explainable Prioritization for Windows PE Malware Forensic Triage with Semantic Consistency Checks

Forensic investigators must decide which suspicious files to examine first. Machine-learning (ML) and deep-learning (DL) malware detectors usually return a bare score that neither explains why a file deserves attention nor signals when changing data make the model unreliable. We present a framework for Windows Portable Executable (PE) malware forensic triage that works only on pre-extracted static features and never executes malware. A calibrated maliciousness score sets…

Read at arXiv (research papers)

Tehran Times (Iranian state-aligned)

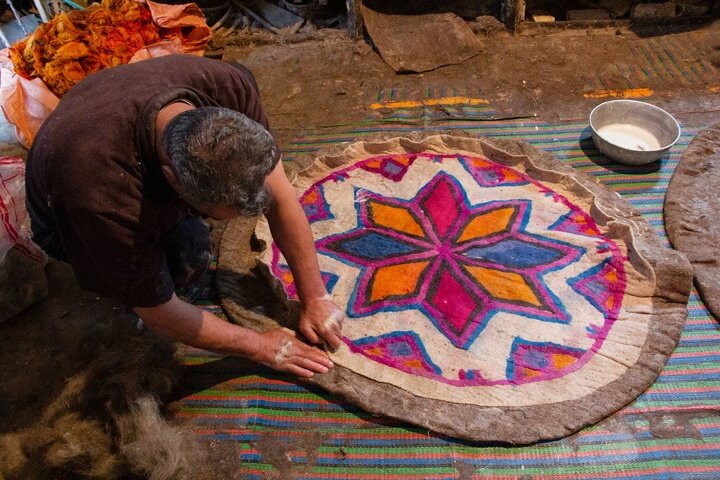
Iran’s traditional felt-making craft needs new markets to survive

TEHRAN – Iran’s traditional felt-making craft, known as namad-mali, faces an uncertain future as declining consumer demand, changing lifestyles and the gradual loss of traditional skills threaten its continuity. Although the centuries-old practice has considerable potential for producing a wide range of contemporary goods, artisans say its survival depends on developing sustainable markets, supporting workshops and passing on their knowledge to younger generations.

Read at Tehran Times (Iranian state-aligned)

Ukrainska Pravda VALENTYNA ROMANENKO Geopolitics

Carthage suspect General Duka says former security service chief told him not to pursue corruption cases against anti-corruption bureau

The Carthage suspect claims Maliuk gave the instruction in autumn 2025 after returning from the President's Office, and that prosecutor general Ruslan Kravchenko received it too.

Read at Ukrainska Pravda

ReliefWeb Norwegian Refugee Council

Nigeria: Advancing displaced women’s housing, land and property rights

Countries: Nigeria, Jordan, Mali, Syrian Arab Republic, Uganda Source: Norwegian Refugee Council Please refer to the attached file.

Read at ReliefWeb

NPR The Associated Press Geopolitics

Rubio says there's 'zero' information that U.S. outages are caused by a malign actor

Secretary of State Marco Rubio sought to calm Americans as he traveled with President Trump and they prepared for key meetings with Chinese President Xi Jinping and Russian President Vladimir Putin.

Read at NPR

Inc42 Shrishti Bisht Startups

How Optimizely Hack Exposed 178 Websites To Crypto, Card Theft

In another major cybersecurity incident, malicious code injected into websites through digital experience platform (DXP) Optimizely exposed visitors to potential…

Read at Inc42

The Hacker News Security

Attackers Compromise Microsoft's Agent Framework PyPI Package to Steal Cloud Credentials

Threat actors have compromised Microsoft's agent-framework package to push a credential stealer, according to reports from Aikido, Chainguard, Endor Labs, OX Security, SafeDep, Socket, StepSecurity, and Google-owned Wiz. The malicious versions, 1.26.1 and 1.26.2, were published 33 minutes apart on November 17, 2026, and are designed to run a credential stealer on every Python start. As of

Read at The Hacker News

The Guardian US Associated Press

‘Zero’ evidence that recent cascade of tech outages are linked, says Rubio

The US secretary of state was speaking after Microsoft, major banks, and the National Security Agency were all affected by technical failures in recent days US secretary of state Marco Rubio has sought to assure Americans that there’s “zero” information that the cascade of service outages – which have grounded flights, cut off work access, limited bank access and disrupted classified communications – are related to each other or to a malign actor. In recent days, Microsoft…

Read at The Guardian US

arXiv (research papers) Yuelin Han Security

Weighing the Envelope: Component Weight and Arbitration in Envelope-Layer Defenses for a Single LLM Agent

The envelope layer is the channel through which malicious content enters an LLM agent. Prior work established label and memory effects on multi-agent A2A envelopes, but the weight structure when MCP tools and memory coexist in a single agent remains unclear. Our threat model assumes an attacker pre-plants a malicious tool and poisons long-term memory; a benign user request inadvertently triggers it, and the attacker never enters the conversation. Following GDA Measurement…

Read at arXiv (research papers)

Krebs on Security BrianKrebs Security

Attackers Used Optimizely to A/B Test Malware on Top Websites

At least 178 top web destinations unwittingly served a variety of malware exploits against visitors over the past 24 hours thanks to a security vulnerability involving Optimizely, a company that helps websites customize user experiences and test out new features. Experts say the incident, which saw data-stealing malicious software silently injected into sites like the BBC, CNN, Equifax, Ledger and Zoom, was exacerbated by the reality that few popular websites enforce strict…

Read at Krebs on Security

arXiv (research papers) Tingxuan Han Security

Data Poisoning Attacks to Locally Differentially Private Triangle Counting Protocols

Local differential privacy (LDP) has become a crucial paradigm for privacy-preserving graph analytics, enabling graph analytics tasks such as subgraph counting without requiring a trusted curator. However, while LDP provides strong privacy guarantees, the integrity and robustness of LDP subgraph counting protocols in the presence of malicious participants remain poorly understood. In particular, since data are randomized locally before collection, it is inherently difficult…

Read at arXiv (research papers)

The Record Security

Website management platform Optimizely confirms hackers put malicious code into customer sites

Researchers said they found malicious JavaScript code on 178 different widely visited websites run through the Optimizely Web experimentation platform. The company confirmed the breach.

Read at The Record

The Hill Tara Suter Geopolitics

FBI says Chase outage tracks back to software release, not malicious activity

The FBI said on Monday that the Chase outage was connected to a software release, not malicious activity. The agency told The Hill’s sister network NewsNation that it didn’t see any signs pointing toward malicious or external activity in the outage, finding that it was linked to a software release. In a Monday post to...

Read at The Hill

The Hacker News Security

Researchers Claim Two RCE Exploits That Bypass Telegram’s New Android Defenses

A malicious widget can bypass the security filter that Telegram added to its Android app last week and run code outside it, according to NebuSec, a security company. Widgets are small interactive blocks that bots send inside chat messages, and their JavaScript runs on the user's phone. The researchers ran their demonstration on a Telegram test server, because only approved bots can send

Read at The Hacker News

Dark Reading Jai Vijayan Security

Cursor Traces Malicious Claude Code Extension to Third-Party Breach

A compromised key issued to AI infrastructure provider Fireworks was used by threat actors to access Cursor data and credentials.

Read at Dark Reading

Older stories