Results for “Code”

arXiv (research papers) Kenta Kasai

Vanishing Relative Distance of Uniformly Random CSS LDPC Codes Built from Permutation Matrices

Classical random regular low-density parity-check codes can have minimum distance growing linearly with block length. We study CSS check matrices formed as full $J\times L$ arrays of arbitrary $P\times P$ permutation matrices, sampled uniformly subject to commutation. For fixed column weight $J\ge3$ and fixed even row weight $L>2J$, we prove that the relative minimum distance converges to zero in probability as $P\to\infty$, with block length $n=LP$. We analyze the weight…
Read at arXiv (research papers)

arXiv (research papers) Paul-Andrei Sava Security

TRIAGE-CPG: A Cross-Model Study of Budgeted Static Malware Triage with Large Language Models

When triaging unknown binaries, security analysts must decide which samples to clear as benign, flag as malicious, or escalate for deeper analysis. Large Language Models (LLMs) could support these decisions by interpreting decompiled code, but a binary can contain hundreds or thousands of functions, making exhaustive LLM analysis impractical. We study how current LLMs behave when static triage is formulated as budgeted evidence acquisition: which functions they inspect and…

Read at arXiv (research papers)

arXiv (research papers) Ben Howe

TCBP-JOBS: GPU-Accelerated Quantum Error Correction Decoding and Noise Learning with Near-Optimal Accuracy

Achieving near-optimal quantum error correction (QEC) decoding accuracy often requires computationally expensive searches that limit both large-scale simulation and real-time operation. We introduce trajectory-calibrated belief propagation (TCBP), which learns calibrated fault probabilities from BP trajectories, and jittered OSD beam search (JOBS), which uses these probabilities to guide parallel GPU searches. Across surface, color and bivariate-bicycle code memory and…

Read at arXiv (research papers)

The Manila Times Franco Jose C. Baroña South China Sea

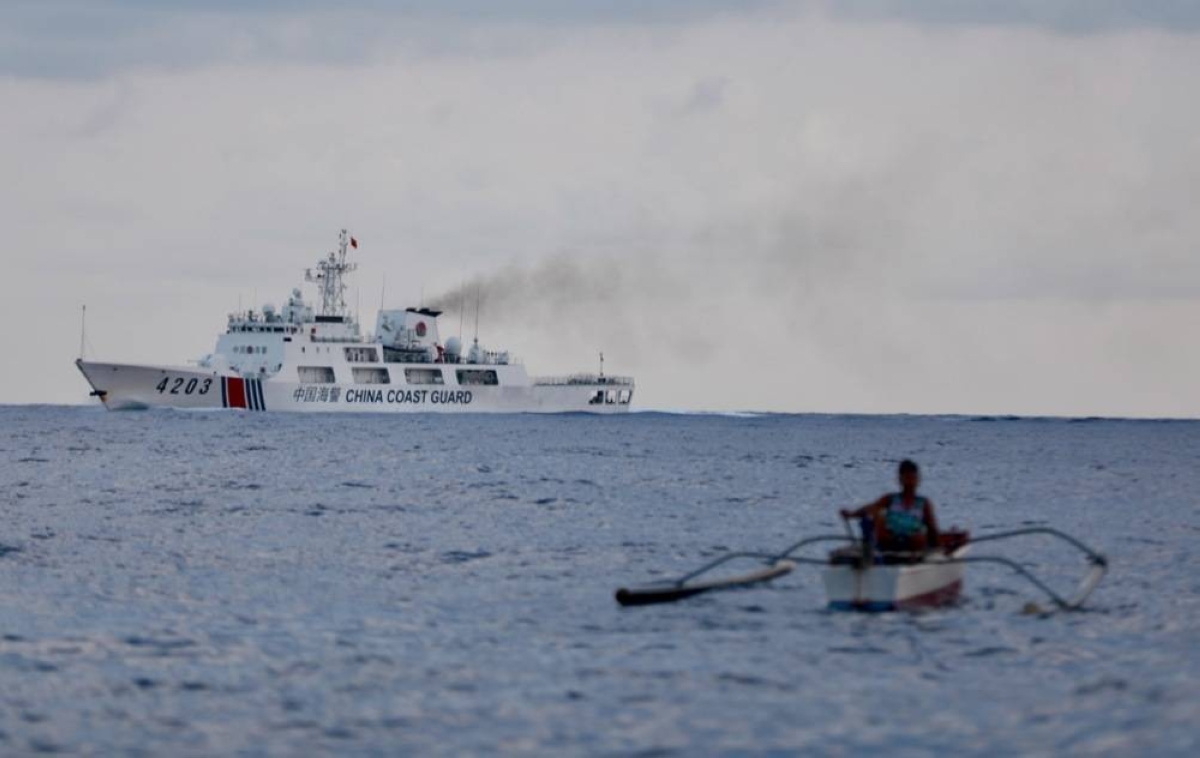
SCS claimants seen pursuing own strategies

ASEAN'S failure to agree on key provisions of a proposed Code of Conduct (COC) in the South China Sea, coupled with China’s position on the negotiations, is likely to push the Philippines, Vietnam and Malaysia to continue pursuing separate strategies in dealing with Beijing, a Japanese defense research institute said. In its China Security Report 2027: China and the South China Sea: The Dynamics of Maritime Issues, Japan’s National Institute for Defense Studies (NIDS) said…

Read at The Manila Times

The Register Security Security

Has AI’s ‘Black October’ changed the way you secure your code?

PARTNER CONTENT: AI agents are making security vulnerabilities easier to find and exploit in your code. Software engineering and application security teams need new ways to find and fix them

Read at The Register Security

SecurityWeek Ionut Arghire Security

Cursor Supply Chain Attack Started at Fireworks AI

The attacker stole an access key from Fireworks and used it to exfiltrate credentials that enabled them to push malicious Claude Code extension copies.

Read at SecurityWeek

ReliefWeb Mercy Corps

DR Congo: Crisis Analysis Team - Monthly displacement report Eastern DRC (October 2026)

Country: Democratic Republic of the Congo Source: Mercy Corps Please refer to the attached file. Key trend highlights for October : Armed conflict and deteriorating security remain the principal drivers of new displacement in eastern DRC. Clashes between the FARDC, Wazalendo groups and various armed factions, notably the FRN, the CRP, CODECO and the Maï-Maï Kata Katanga, continued to trigger significant population movements. These were compounded by violence against…

Read at ReliefWeb

ReliefWeb Mercy Corps

DR Congo: Crisis Analysis Team - Monthly displacement report Eastern DRC_October 2026

Country: Democratic Republic of the Congo Source: Mercy Corps Please refer to the attached file. Key trend highlights for October : Armed conflict and deteriorating security remain the principal drivers of new displacement in eastern DRC. Clashes between the FARDC, Wazalendo groups and various armed factions, notably the FRN, the CRP, CODECO and the Maï-Maï Kata Katanga, continued to trigger significant population movements. These were compounded by violence against…

Read at ReliefWeb

ReliefWeb Mercy Corps

DR Congo: Crisis Analysis Team - Rapport mensuel sur les déplacements à l'Est de la RDC (octobre 2026)

Country: Democratic Republic of the Congo Source: Mercy Corps Please refer to the attached file. Points saillants des tendances pour le mois d’octobre : Les conflits armés et la dégradation de la situation sécuritaire demeurent les principaux moteurs des nouveaux déplacements dans l’Est de la RDC. Les affrontements entre les FARDC, les groupes Wazalendo et diverses factions armées, notamment le FRN, la CRP, la CODECO et les Maï-Maï Kata Katanga, ont continué de provoquer…

Read at ReliefWeb

ReliefWeb Mercy Corps

DR Congo: Crisis Analysis Team - Rapport mensuel sur les déplacements à l'Est de la RDC_octobre 2026

Country: Democratic Republic of the Congo Source: Mercy Corps Please refer to the attached file. Points saillants des tendances pour le mois d’octobre : Les conflits armés et la dégradation de la situation sécuritaire demeurent les principaux moteurs des nouveaux déplacements dans l’Est de la RDC. Les affrontements entre les FARDC, les groupes Wazalendo et diverses factions armées, notamment le FRN, la CRP, la CODECO et les Maï-Maï Kata Katanga, ont continué de provoquer…

Read at ReliefWeb

Just Security Ambassador Daniel Fried Geopolitics

Chasing Yalta: Putin Reverts to Goal of Dividing Europe, as U.S. Appears to Open Door

Russia emerges from a flurry of meetings in a stronger position, extracting U.S. agreement to consider the "European security order," Kremlin code for "spheres of influence."

Read at Just Security

SANS Internet Storm Center Security

Scans for LiteLLM/Starlette (CVE-2026-42271, CVE-2026-48710), (Mon, Nov 16th)

This weekend, we started seeing requests for /mcp-rest/test/tools/list hitting our honeypots. These requests appear to attempt to exploit CVE-2026-42271 and CVE-2026-48710. Horizon3.ai published a short write-up about how these vulnerabilities can be chained to achieve remote code execution without authentication [Horizon3]

Read at SANS Internet Storm Center

MacRumors Tim Hardwick Gadgets

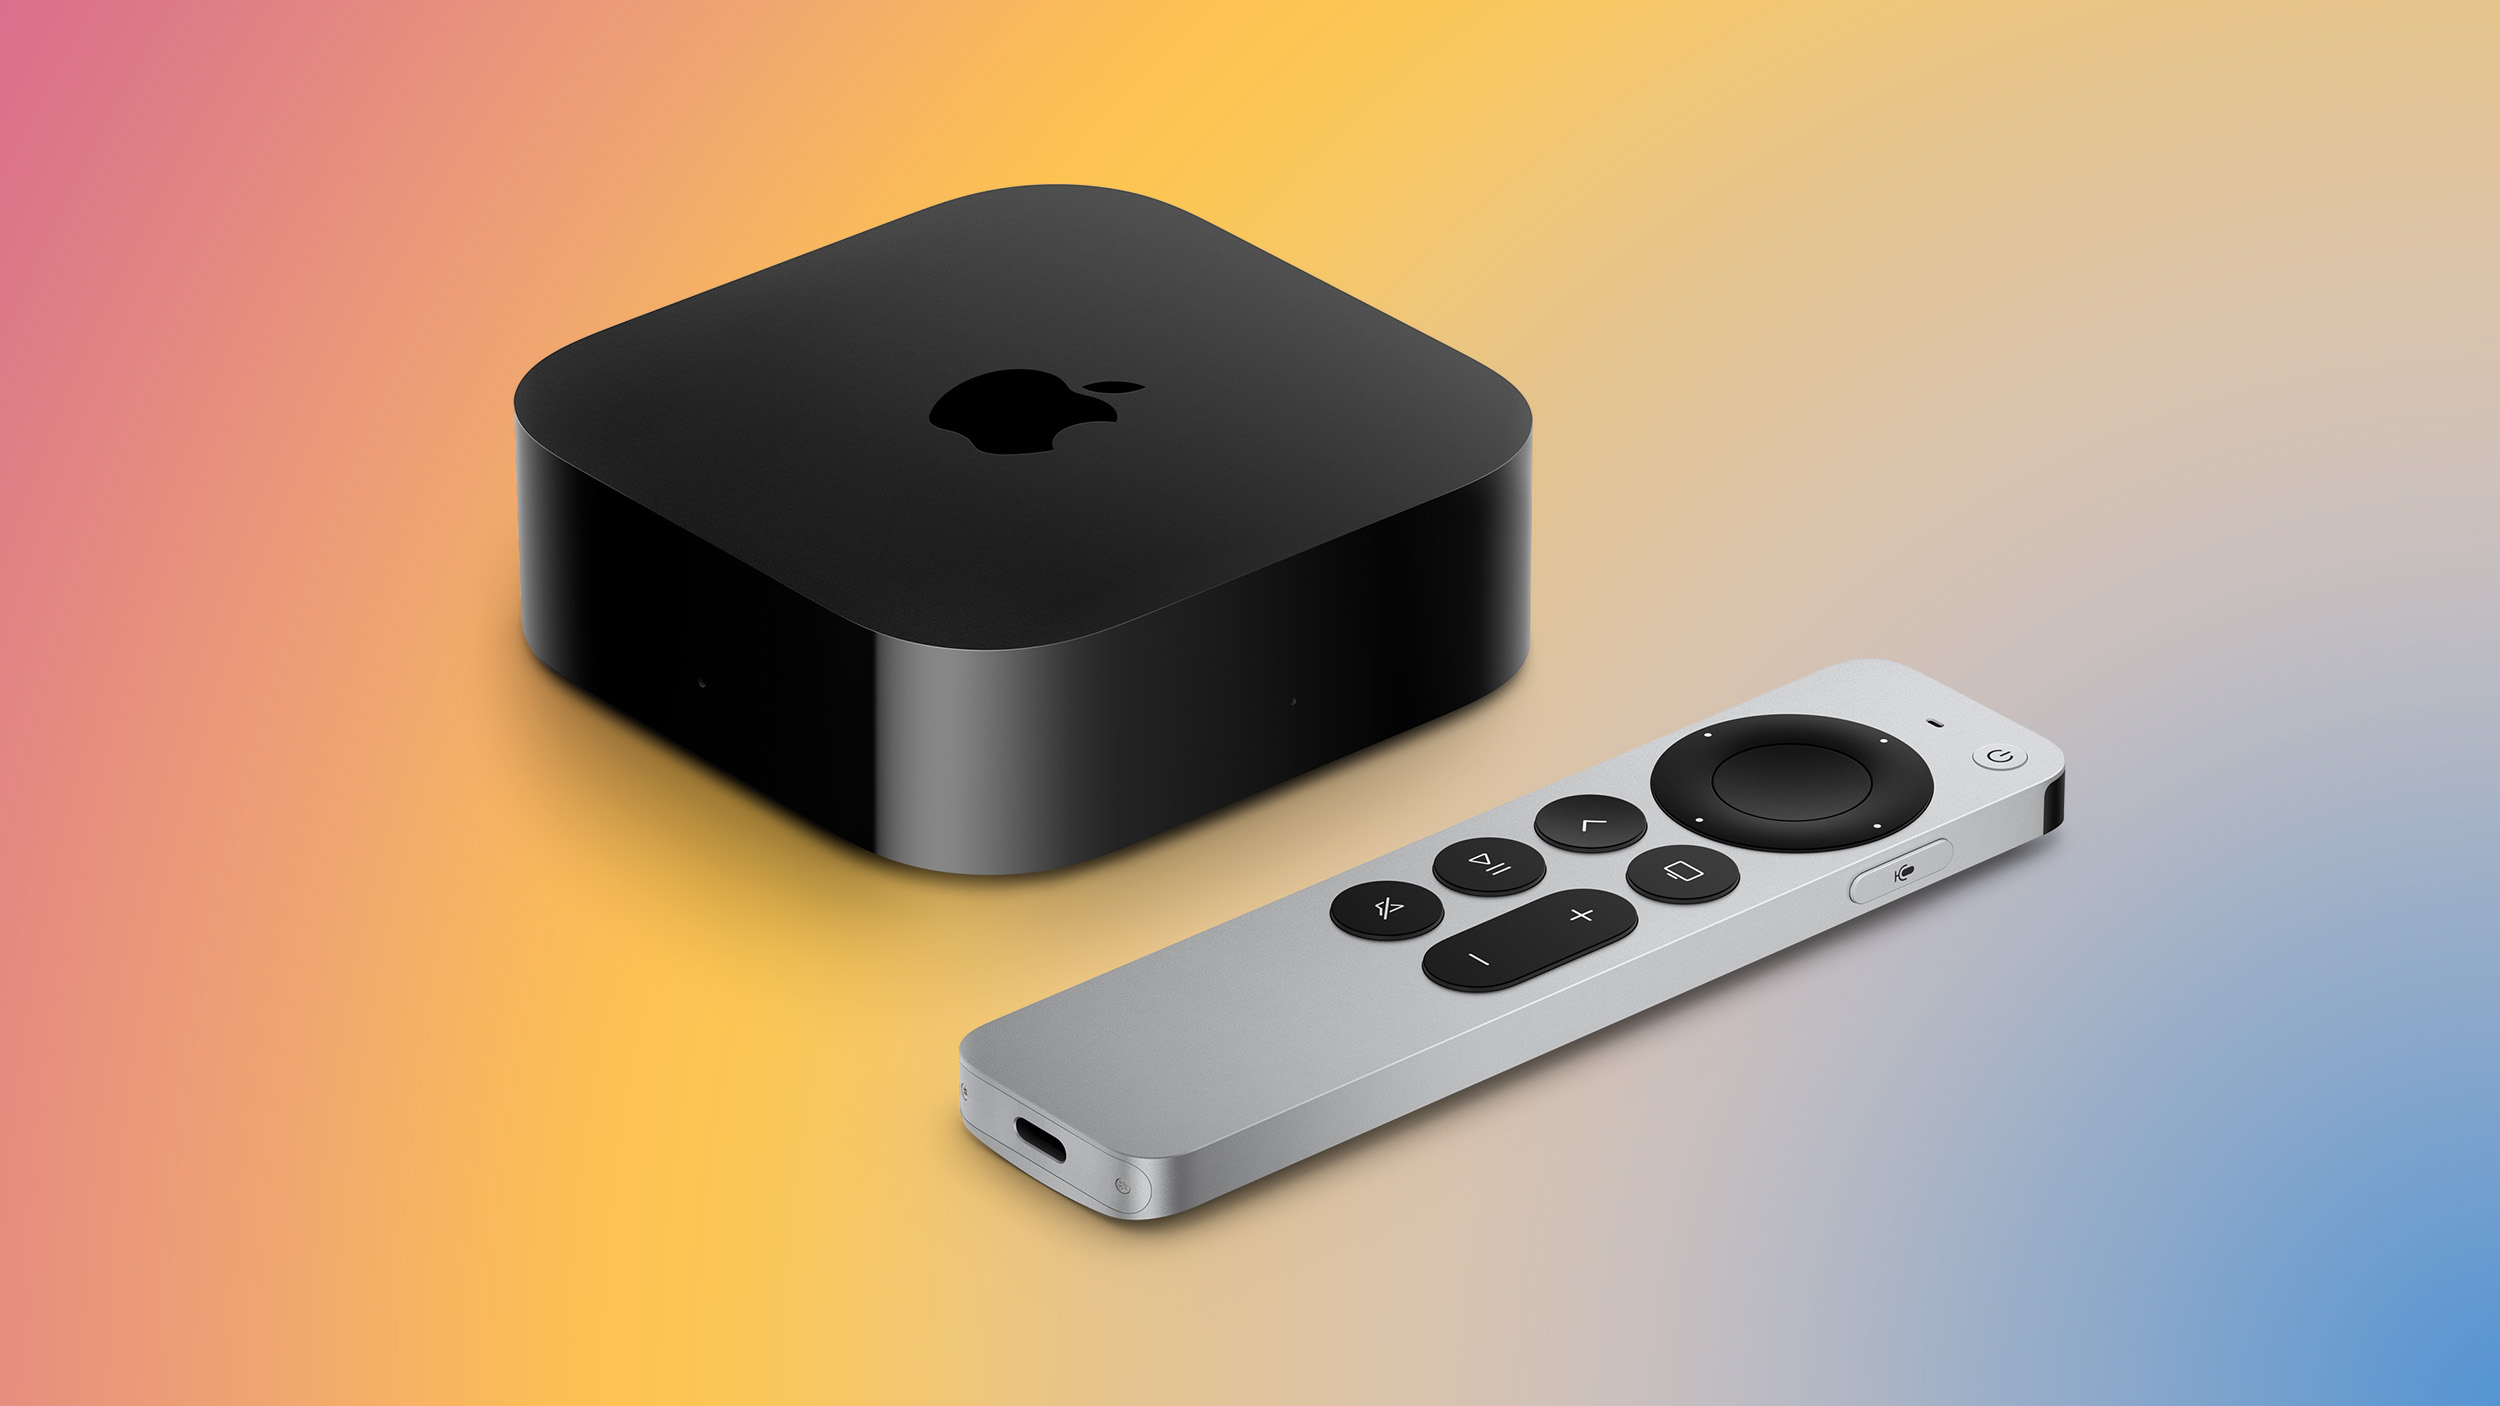
New Apple TV 4K's A19 Chip Has One Core Switched Off

Apple's new Apple TV 4K uses an A19 chip with one efficiency core disabled, according to system diagnostic data shared by code explorer pdfu. That suggests a five-core CPU with two performance cores and three efficiency cores, compared with the six-core CPU in the iPhone 17. The reported maximum clock speeds are 4.26GHz for performance cores and 2.592GHz for efficiency cores, with a five-core GPU reaching 1.47GHz. (These are maximum frequencies, not measurements of sustained…

Read at MacRumors

The Register Richard Speed

Microsoft blames monster email outage on software defect introduced in July fix

Summer code change caused a Fall fail – frantic engineers had to patch the patch instead of rolling back

Read at The Register

Digital Trends Rachit Agarwal

Samsung Galaxy Claw could let AI send messages, make calls, and manage your schedule

Galaxy Claw has surfaced in Samsung’s code, and it points to a Galaxy AI that can send messages, make calls, and run tasks on a schedule instead of just answering you.

Read at Digital Trends

MarkTechPost Michal Sutter SI

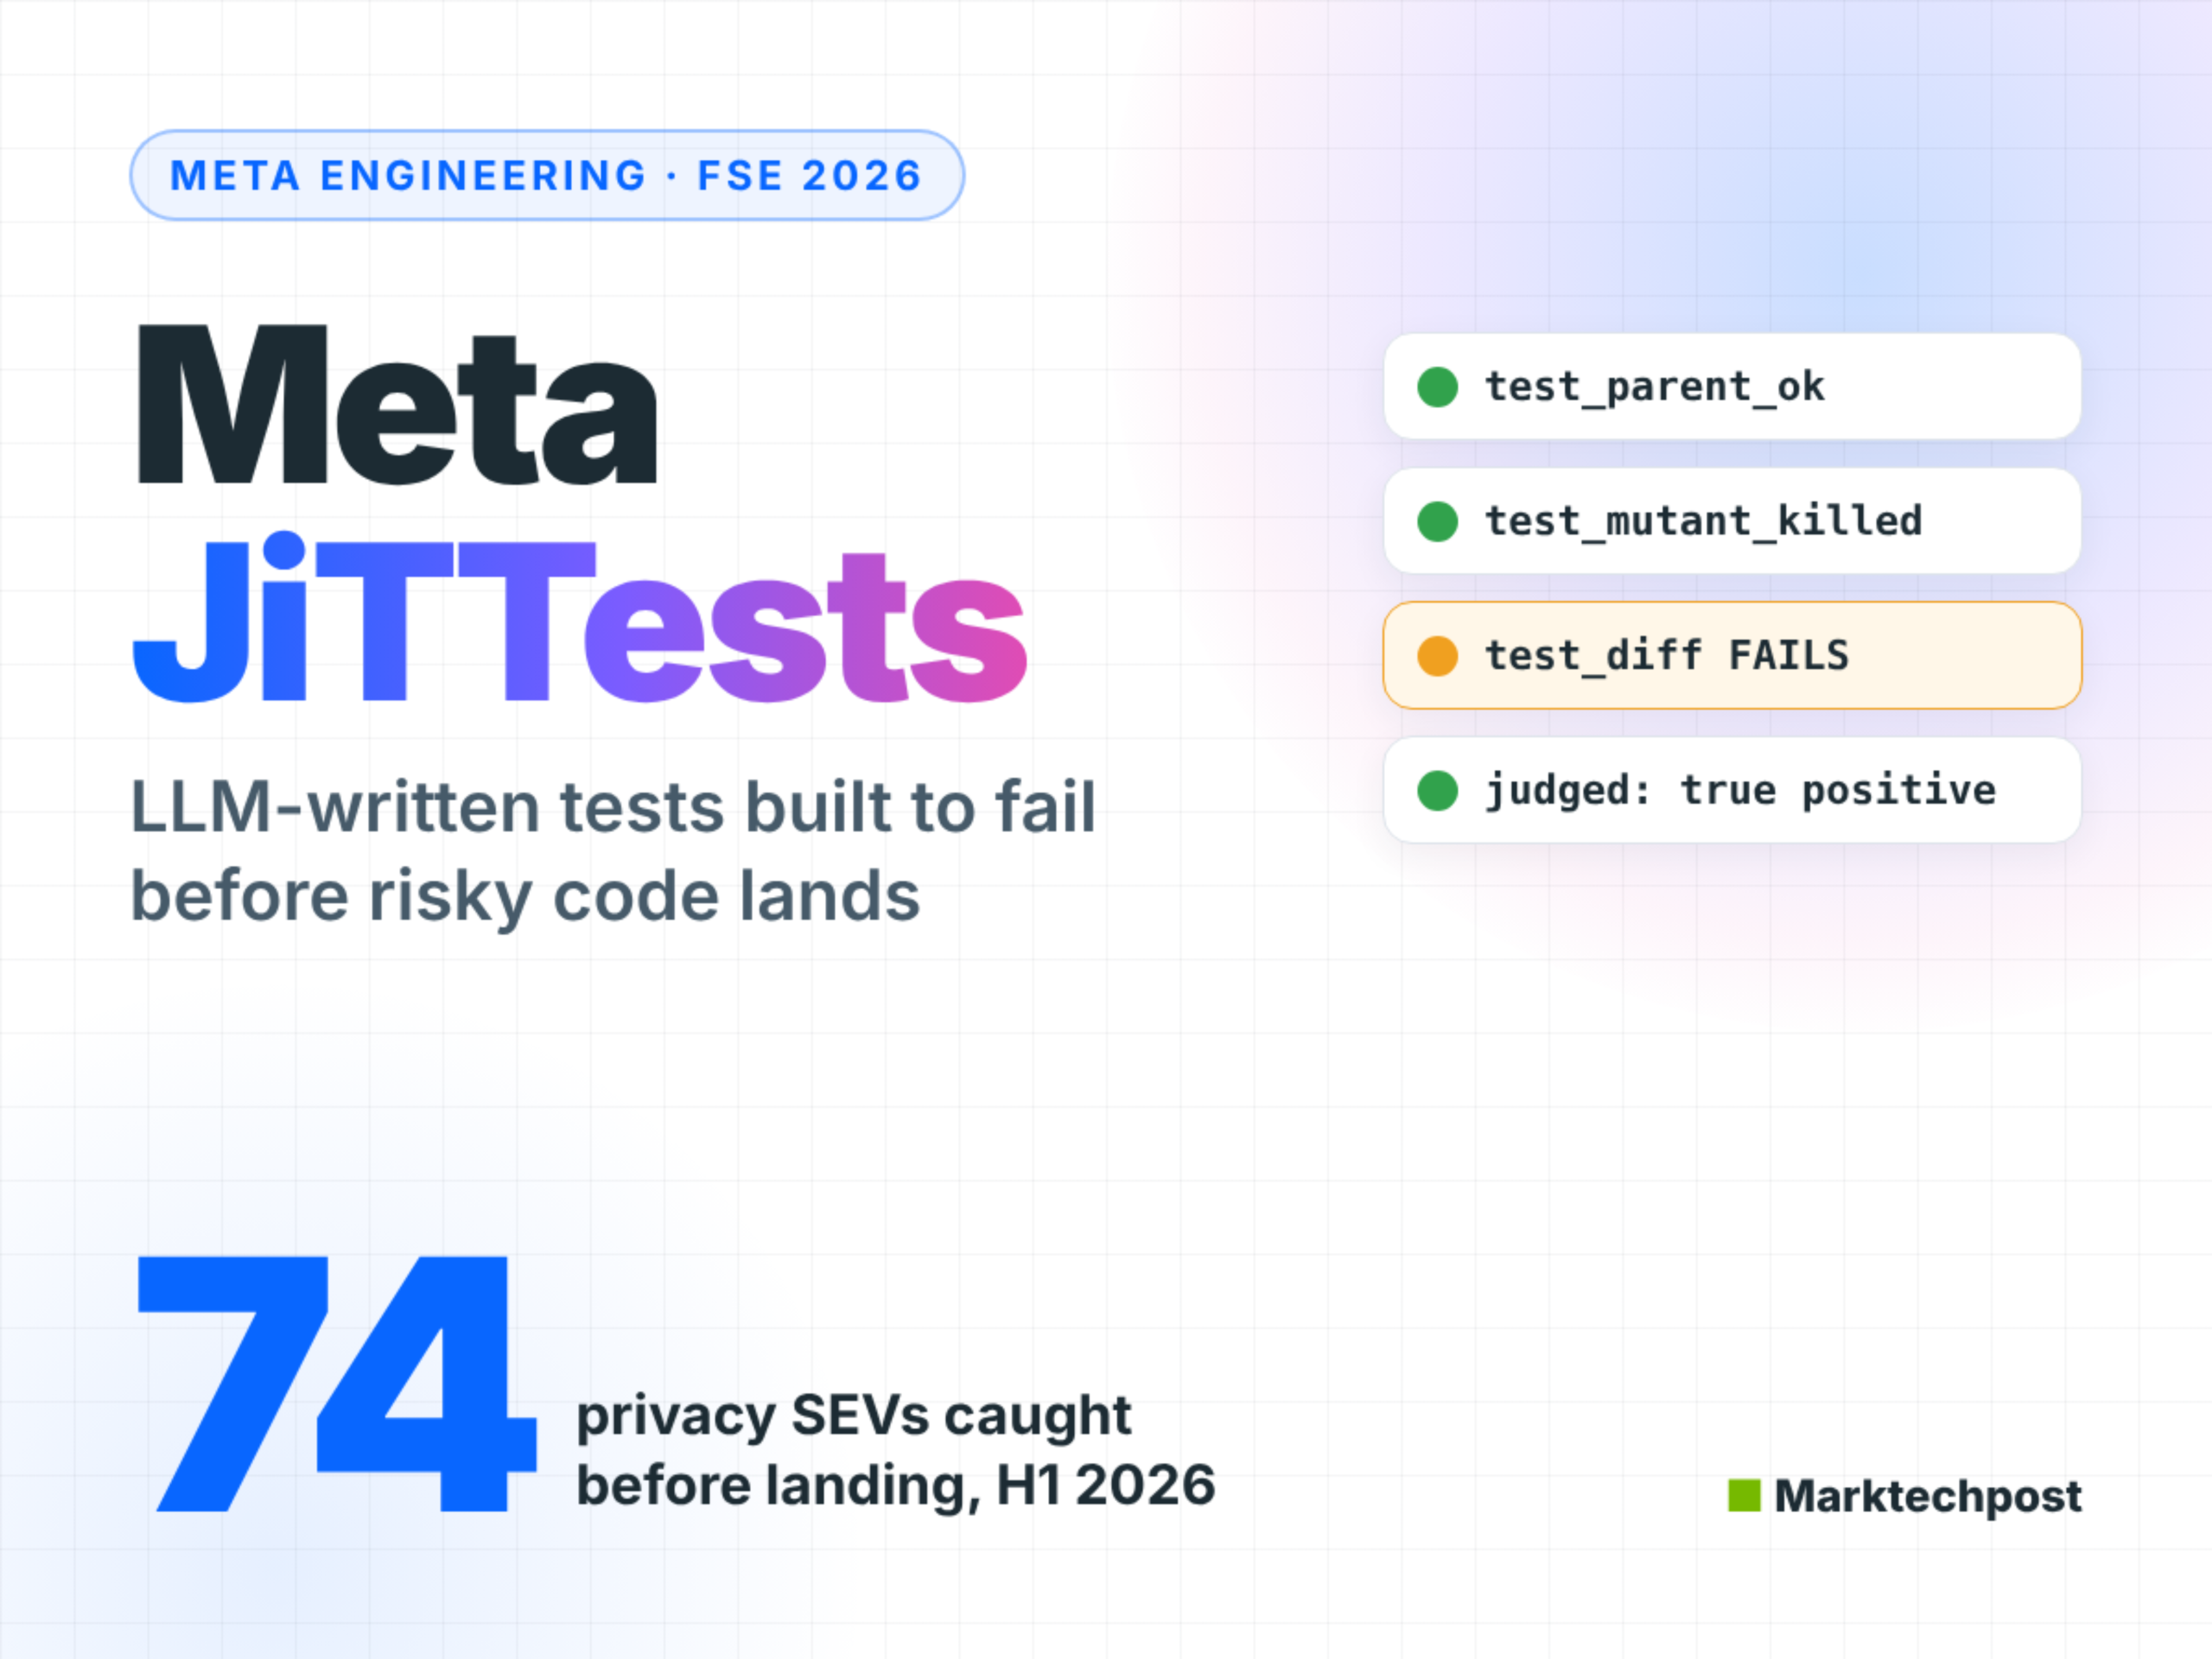
Meet Meta’s JiTTests: LLM-Generated Tests Designed to Fail Before Risky Code Lands

Meta has moved Catching JiTTests into production. The LLM system writes tests designed to fail on risky diffs, and caught 74 privacy SEVs before landing in H1 2026, with a 60% engineer-reported true-positive rate.

Read at MarkTechPost

The Manila Times Allen Limos South China Sea

China is committed to early conclusion of sea code with Asean — Lazaro

MANILA, Philippines — Foreign Affairs Secretary Ma. Theresa Lazaro said China is committed to finalizing the Code of Conduct (COC) in the South China Sea with the Association of Southeast Asian Nations (Asean). In a press briefing at the International Media Center, Lazaro said both Asean and China are committed to concluding the COC but no definite timeline can be given as to when it will be finalized Lazaro earlier said that the COC is more than 80 percent complete but its…

Read at The Manila Times

OpenAI News SI

How Revolut raises ambition without lowering the bar

Discover how Revolut uses OpenAI models and Codex to cut coding time by 30–60%, scale financial crime investigations, and innovate without compromising security.

Read at OpenAI News

Viet Nam News (state-run daily) South China Sea

PM suggests priorities for elevating, deepening ASEAN–China cooperation

Regarding the South China Sea, the Vietnamese Government leader urged both sides to maintain the current momentum and work towards an early conclusion of an effective and substantive Code of Conduct in the East Sea (COC) in accordance with international law

Read at Viet Nam News (state-run daily)

arXiv (research papers) Pier Mattia Basciano Security

A First Look at System One Decision Models for Malware Detection

Malware detection needs scores calibrated at a fixed false positive rate (FPR) and decisions an analyst can read: feature-based detectors give the first, large language models (LLMs) on decompiled code the second, through generated text of uncalibrated confidence. System One decision models answer a typed question about a text with a probability over its declared answers in one forward pass. We present the first evaluation of these models for Windows Portable Executable…

Read at arXiv (research papers)

arXiv (research papers) Wenhan Yu SI

VIVID: A Visual Harness for Agentic Video Editing

Video editing requires agents to make editing decisions grounded in audiovisual observations and precise temporal localization, and to evaluate their effects in rendered outputs. General-purpose coding agents possess strong comprehension, reasoning, and code execution capabilities, while media interaction and evidence management mechanisms tailored to video tasks can further unlock their editing potential. We introduce VIVID, a visual harness that supports multiple native…

Read at arXiv (research papers)

Help Net Security Mirko Zorz Security

You can now self-host Kitesurf, Cloudflare’s open-source browser for AI agents

Kitesurf is Cloudflare’s browser for AI agents, built to load web pages and run their JavaScript on Cloudflare Workers without starting up a full desktop browser. Cloudflare has published its source code so developers can inspect it, modify it, test it on their own machines, and deploy a copy to their Cloudflare account. A browser without Chromium Kitesurf needs no browser container, and it can return screenshots of the pages it loads. It supports the … More →

Read at Help Net Security

The Hacker News Security

BO Team Exploits Log4Shell in VMware vCenter, Compromises Russian Firm's Code-Signing Server

An investigation into suspicious activity within a Russian software developer's network has uncovered a months-long compromise of its development infrastructure and a software code-signing server. The activity, documented by Kaspersky's ICS CERT team after it was contacted by the affected developer in June 2025, has been attributed to a threat actor named BO Team (aka Black Owl, Hoody Hyena,

Read at The Hacker News

South China Morning Post SCMP’s Asia desk Geopolitics

Bid to marry off pregnant girl, 12, in Malaysia leads to man’s arrest

Malaysian police have arrested a 28-year-old man in Sarawak on suspicion of impregnating a girl, 12, who was still in primary school. The case has reignited debate over child marriage in Malaysia, as the girl’s mother reportedly told the school that she wanted her daughter to marry the baby’s father. Police are investigating the man for statutory rape, an offence that carries a maximum penalty of up to 20 years in prison and caning under the country’s penal code. They…

Read at South China Morning Post

Help Net Security Anamarija Pogorelec Security

AI uncovers flaws in discontinued devices with no vendor left to patch them

Forescout researchers built a tool to test if generally available AI models could find security flaws on a limited budget. They examined both open-source code and compiled software whose source code was unavailable, testing an approach attackers could also use. The team confirmed 99 vulnerabilities across 10 TCP/IP stacks, the software components that allow devices to communicate over networks. Sixty-six were previously unknown, and 52% of those newly discovered…

Read at Help Net Security

arXiv (research papers) Chaitanya Garware Security

Beyond the Patch: Reconstructing an Incomplete-Fix Patch Bypass in LLM Agent Frameworks with Control-Gated, Benign Probes

Replaying a vulnerability's original proof-of-concept after patching tests whether its reported trigger remains reproducible, but does not establish that the underlying security invariant holds on other code paths. We present a benign, control-gated reconstruction method and a pilot study across four LLM agent frameworks and four invariant classes. For PraisonAI, we compare original-trigger replay (B0) with a distinct sibling-path probe (M). We also perform five before/after…

Read at arXiv (research papers)

Al Jazeera South China Sea

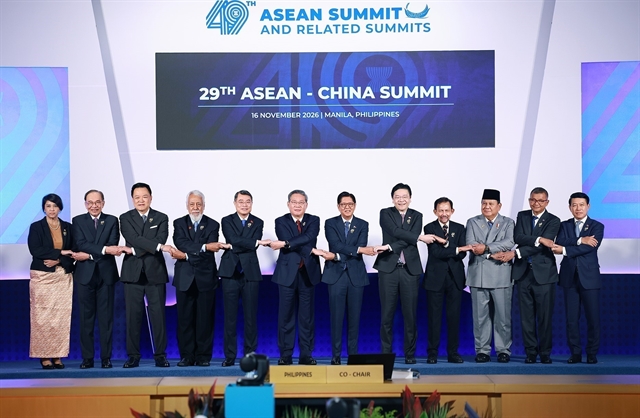
ASEAN, China fall short of agreeing on South China Sea code

Southeast Asian leaders also denounce violence in Myanmar and extend ban on country's leader attending bloc's summits.

Read at Al Jazeera

arXiv (research papers) Jiaxuan Zhang

Rate-1/2 Quantum LDPC Codes for Multi-tier Superconducting Hardware

Quantum error correction is essential for scalable quantum computing, while its resource overhead is governed in large part by the encoding rate, namely the number of logical qubits encoded per physical data qubit. Recent quantum low-density parity-check (qLDPC) constructions have entered the ultra-high-rate regime with encoding rates above 1/2, but their syndrome-extraction circuits generally rely on reconfigurable connectivity or long-range qubit transport, making them…

Read at arXiv (research papers)

arXiv (research papers) Silei Ren Security

Type-Confusion Security

Type systems are a lightweight way to obtain formal assurance that code upholds security properties. However, decentralized systems, such as smart contracts and Model Context Protocol ecosystems, have limited ability to constrain the behavior of untrusted code. In such systems, attackers may attempt to confuse trusted code by supplying values that do not behave according to their advertised types, an attack that we call type confusion. Well-known attacks such as confused…

Read at arXiv (research papers)

arXiv (research papers) Juan Carlos García Escartín Security

A Bleichenbacher bit-by-bit oracle attack from partial message knowledge

Oracle attacks show the importance of a correct implementation of cryptographic standards when translated into code. A notable example is the Bleichenbacher attack on RSA with PKCS#1 v1.5 padding and all the improvements that have been suggested over the decades. This paper shows how an attacker knowing a few least significant bytes of an RSA message can take advantage of a server with an oracle side-channel to decrypt the full message bit by bit. We will consider two…

Read at arXiv (research papers)

Older stories