Results for “Code”

CISA advisories CISA Security

Siemens Industrial Software Products

View CSAF Summary On October 21, 2026, the Node.js project released security updates addressing a critical vulnerability in the Brotli decoder bundled with Node.js, commonly referred to as "Node2Shell" (tracked as CVE-2026-111497). The vulnerability is an out-of-bounds write that could allow a remote attacker to cause memory corruption and potentially execute arbitrary code. This advisory covers the status of impact of various Siemens software products. Please also have a…

Read at CISA advisories

CISA advisories CISA Security

Siemens SIMATIC WinCC

View CSAF Summary Graphics Designer of SIMATIC WinCC before V8.2 contains an implicit active content execution vulnerability upon opening files, which could allow an attacker to cause arbitrary code execution on the device. Siemens is preparing fixes and recommends specific mitigations for products where fixes are not or not yet available. The following versions of Siemens SIMATIC WinCC are affected: SIMATIC WinCC V7.5 vers:all/* (CVE-2026-59082) SIMATIC WinCC V8.0…

Read at CISA advisories

The Hacker News Security

New GitDoor and GraphDoor Backdoors Turn GitHub and SharePoint Into Covert C2 Channels

Government sectors in Asia and Africa have been targeted by an active cyber intrusion campaign that delivers to previously undocumented backdoors that leverage legitimate services like Microsoft SharePoint and GitHub for command‑and‑control (C2). The activity has been codenamed Operation ShadowCloud by Kaspersky. The Russian cybersecurity company said it identified the campaign in early 2026.

Read at The Hacker News

arXiv (research papers) Deep Shah SI

Securing and Auditing Long-Horizon LLM Agents: State-Transfer Auditing and Controls in the Agent Harness

Long-horizon LLM agents across codebases, web browsers, and enterprise infrastructure rely on an execution harness to move state between the working context, session history, persistent memory, and external environment. While conventional execution traces log model prompts and tool calls, critical security and reliability failures occur during state transfers: a transfer can admit unchecked content (indirect prompt injections, unverified memory writes), rewrite state lossily…

Read at arXiv (research papers)

Tech in Asia Naomi Li Gan Startups

Chinese AI firms tap US models as chip restrictions tighten

The documents show Chinese developers turning answers, code, and problem-solving steps generated by American models into training data for smaller local models.

Read at Tech in Asia

Asia Times Rommel C Banlaoi South China Sea

Manila’s ASEAN push for South China Sea code close but no cigar

Armed with optimism, the Philippines wanted its 2026 chairmanship of the Association of Southeast Asian Nations (ASEAN) to be remembered for delivering a long-awaited Code of Conduct (COC) in the South China Sea. But Manila leaves ASEAN’s rotational leadership having brought negotiations close to the finish line, but regrettably not across it. ASEAN and China

Read at Asia Times

Digital Trends Dwayne Cubbins

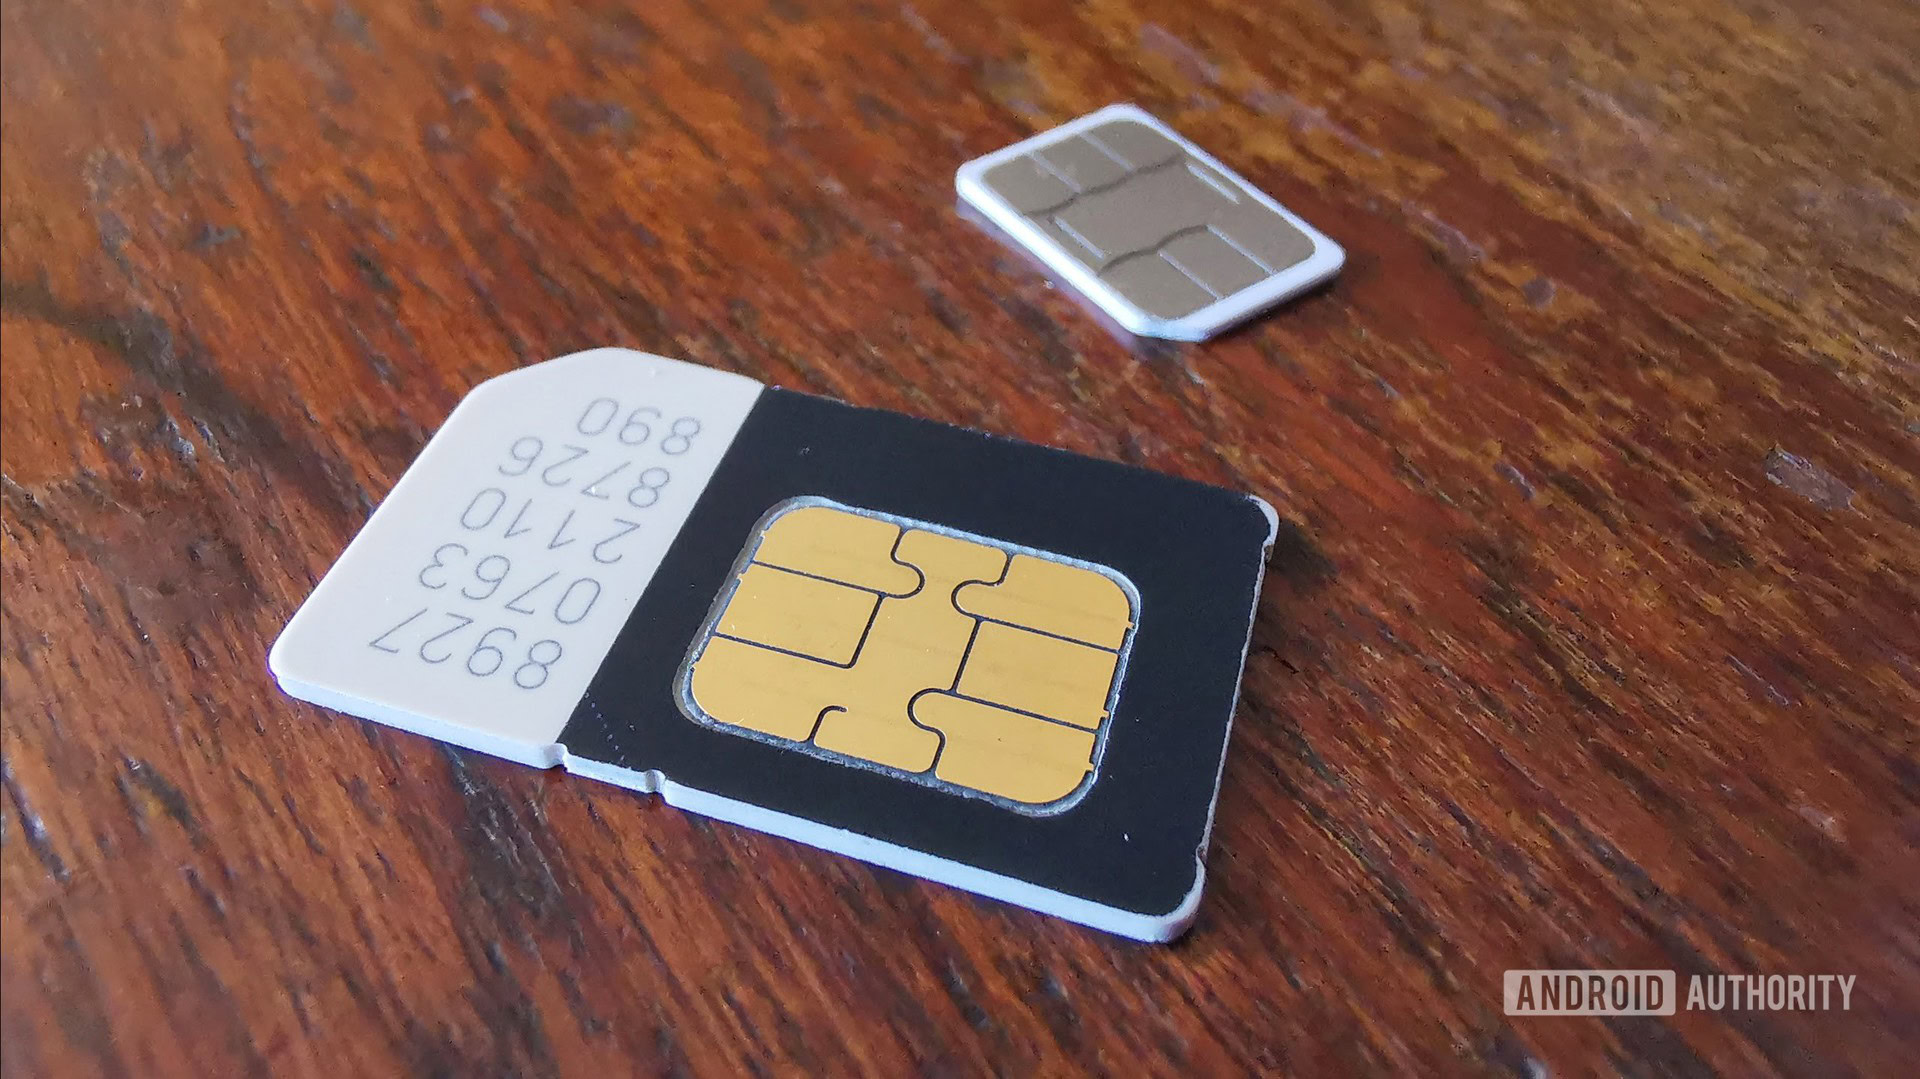
Android Fast Switch could make carrying two phones a lot less annoying

Google appears to be building Android Fast Switch, its answer to iPhone Handoff. Code in the SIM Manager app shows it would let you use one phone number on two phones.

Read at Digital Trends

arXiv (research papers) Mehul Arora

CoBoVLA: Decoupling Language from Action with Discrete Codes for Robust and Interpretable Robot Manipulation

Vision-Language-Action (VLA) models achieve high success rates on the LIBERO benchmark but remain sensitive to paraphrasing. Existing VLAs ranging from 0.6B to 7.5B parameters experience a 22-52 point performance drop on LIBERO-Para while SmolVLA exhibits an even larger decline, from 83\% to 8\%. Because most VLAs jointly learn language understanding and action generation, it is difficult to determine whether a failure originates from misunderstanding an instruction or…

Read at arXiv (research papers)

Help Net Security Mirko Zorz Security

NATO’s AI cyber defense work hits up to 300 billion OpenAI tokens a month

NATO’s Communications and Information Agency (NCIA) gives NATO’s core institutions access to OpenAI’s cybersecurity models to help protect Allied networks. NATO has used up to 300 billion raw input and output tokens a month. Access comes through Daybreak, OpenAI’s program for vetted defenders doing authorized work like reviewing code, chasing suspicious activity and testing fixes. The exposure sits in software that European institutions run every day. ENISA, the EU’s cyber…

Read at Help Net Security

The Manila Times Bernadette E. Tamayo South China Sea

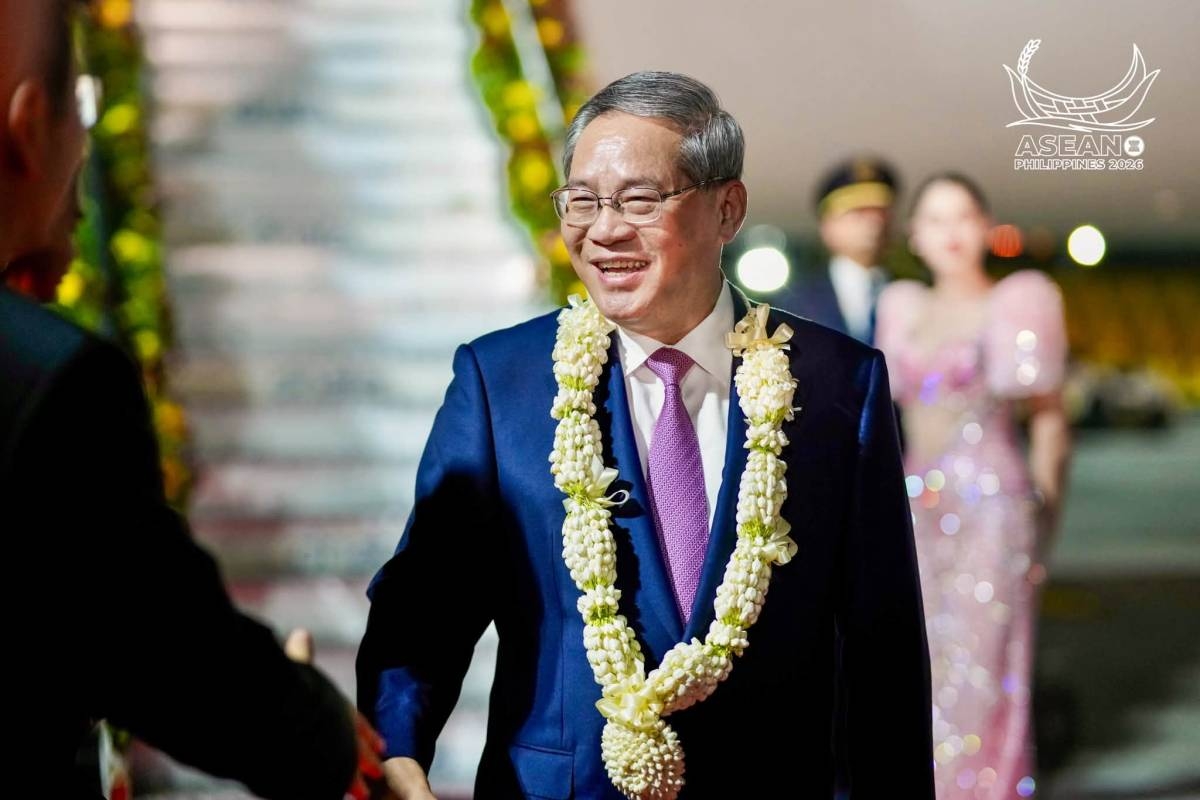
China looks forward to early conclusion of Code of Conduct in South China Sea, says Premier Li

MANILA, Philippines — China looks forward to the early conclusion of the Code of Conduct (COC) in the South China Sea with the Association of Southeast Asian Nations (Asean), which will provide a "solid institutional guarantee" for lasting peace and stability in the region. The Chinese Embassy in Manila said Chinese Premier Li Qiang made the remark during the 29th China-Asean Summit on Monday. "The two sides should promote regional development and prosperity," Li said. The…

Read at The Manila Times

The Hacker News Security

Hijacked Optimizely Scripts Served Card Skimmer and iOS Exploit Kits to CNN, BBC and Zoom Visitors

An attacker exploited a flaw in Optimizely Web Experimentation to plant malicious code in some of the scripts that customers' websites load from the service, Optimizely said early today. Visitors to sites run by at least 178 organizations, including CNN, the BBC and Zoom, received the code yesterday, according to Report URI, a firm that monitors the scripts websites run. The code was built to

Read at The Hacker News

arXiv (research papers) Arjun Sivaraman SI

Readie: Low-Latency Code Sandboxes for AI Agents

From quantitative research to personal assistance, AI agents act by iteratively generating and executing code. To decouple the agent harness from code execution, many agents offload execution to dedicated systems called code sandboxes. However, existing code sandboxes suffer from slow startup. Whether they rely on custom snapshots or a single fat image, the root cause is the same: it is hard to build a compact, pre-warmed snapshot that can be shared across diverse…

Read at arXiv (research papers)

arXiv (research papers) Changxuan Fan SI

RoboTeam: Benchmarking Vision-Based Multi-Agent Control of Many Robot Arms in Real Time

Multimodal agents can now control robot arms by calling tools and writing code. Existing benchmarks fall short in three ways: most test one or two arms on short tasks, many pause the world while the agent thinks, and many give it ground-truth object positions. We present RoboTeam, a simulated benchmark where agents control 4 to 16 robot arms in real time from camera images alone. Its 36 tasks are long jobs that the arms must do together, such as passing timbers or building a…

Read at arXiv (research papers)

arXiv (research papers) Haoran Liao

Magic state cultivation with lattice-surgery escape on superconducting hardware

Magic state cultivation (MSC) is a low-overhead protocol for fault-tolerantly preparing logical magic states. In this work, we implement two MSC variants to prepare a magic state in a distance-5 code on a publicly available IBM Nighthawk processor. The first is a lattice-surgery escape, recently proposed by Hirano et al. and experimentally studied here for the first time. The second is a grafting escape, previously demonstrated by Rosenfeld et al., and extended here by…

Read at arXiv (research papers)

CBS News

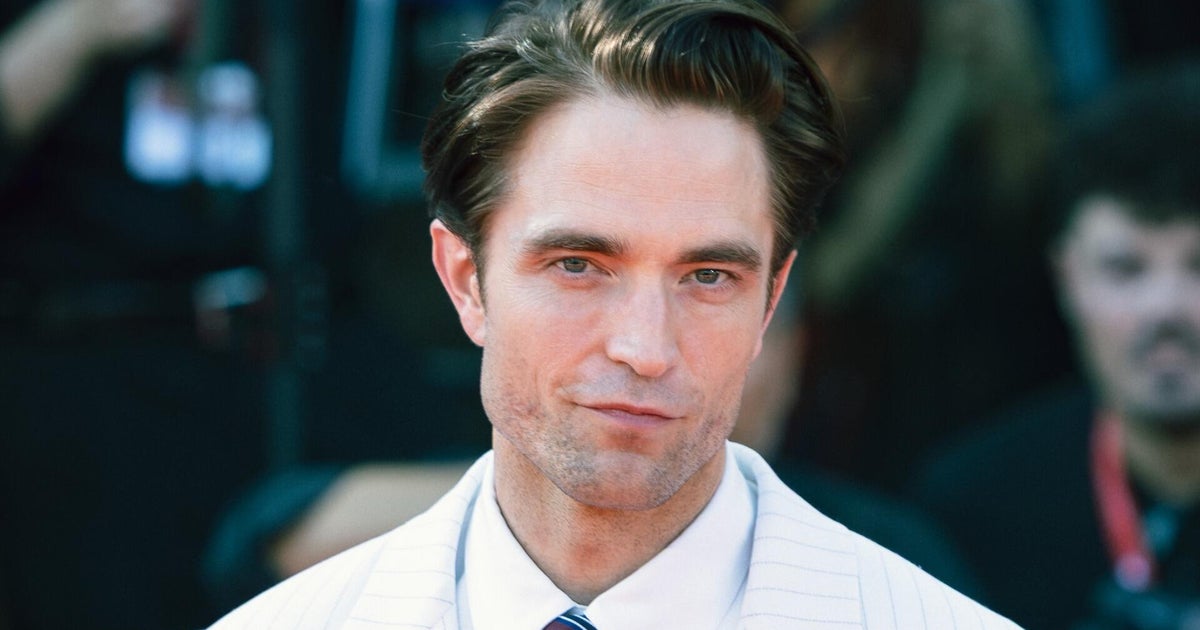
Robert Pattinson lands coveted James Bond role

Going back more than 60 years, only six actors have played James Bond, the British secret agent code-named 007. After years of speculation, Amazon MGM Studios cast 40-year-old Robert Pattinson as the leading man. Tom Hanson has the story.

Read at CBS News

arXiv (research papers) Muhammed Fatih Balın

Computed Permutation Trellis Coding: Near-Optimal Quantization from Two Multiplications and a 64-Byte Table

We propose Computed Permutation Trellis Coding (CPTC), a low-bit quantization format for tensors written once and read many times. Formats that round each value on its own, such as INT4 and FP4, waste a large part of their bits against the information-theoretic ideal. Trellis codes recover this loss by encoding values jointly, but prior decoders either need a large lookup table for their best quality or compute values with a hash that restricts what they can decode. CPTC's…

Read at arXiv (research papers)

9to5Mac Seth Kurkowski

9to5Mac Daily: November 16, 2026 – Apple glasses rumors, more

Listen to a recap of the top stories of the day from 9to5Mac. 9to5Mac Daily is available on iTunes and Apple’s Podcasts app, Stitcher, TuneIn, Google Play, or through our dedicated RSS feed for Overcast and other podcast players. Sponsored by Backblaze: Backup you can rely on. Save 20% with code 9to5daily.

Read at 9to5Mac

Simon Willison SI

llm 0.37.3

Release: llm 0.37.3 A bug fix release for LLM, mainly to cover a problem with the most recent Homebrew package of the software. Homebrew now ships the latest SQLite, 3.54.1, which includes a fix that broke LLM's logging code. Short version: in SQLite 3.54.0 the following SQL: select json_object('a', (select json_array(1))) Returns this: {"a":[1]} But in 3.54.1 the same query returns this: {"a":"[1]"} According to D. Richard Hipp: That was a bug fix. Per the documentation…

Read at Simon Willison

Android Authority Stephen Schenck Gadgets

Samsung’s working on new international SIM tools for One UI 9.5

One UI 9.5 code shows travel SIM usage tracking by trip and day.

Read at Android Authority

The Decoder Matthias Bastian SI

Google warns that fully automated cyberattacks have arrived and will get worse fast

Google's Threat Intelligence Group has for the first time caught attackers finding and exploiting security vulnerabilities with no human involvement at all. An AI framework called "exploit_agent," found on an exposed server, automatically compared code before and after patches, built exploits, and ran them on its own. The article Google warns that fully automated cyberattacks have arrived and will get worse fast appeared first on The Decoder.

Read at The Decoder

arXiv (research papers) Devki Nandan Jha Security

Threat Landscape of Vibe Coding and the Road to Secure Autonomy

Vibe coding is reshaping software development, enabling faster implementation and allowing individuals with limited programming experience to describe requirements in natural language while AI agents write, test, and deploy the code. As these agents evolve into autonomous systems that execute commands, manage dependencies, access cloud resources, and interact with other agents, their security risks extend beyond incorrect code to actions with direct consequences for software…

Read at arXiv (research papers)

arXiv (research papers) Yasir Rahman Security

LLMs as Validators for Cross-Chain Bridges: Evaluating Source-Level and Transaction-Level Attack Detection on Solana

Cross-chain bridges have suffered substantial asset losses due to vulnerabilities in their on-chain programs. On Solana, missing validation checks can enable exploits even when the underlying blockchain operates correctly. The ability of large language models (LLMs) to diagnose these flaws from source code or transaction records, rather than merely raise alarms, remains insufficiently understood. We implement a native Rust lock-and-mint bridge on a local Solana validator…

Read at arXiv (research papers)

Quantum Computing Report Mohamed Abdel-Kareem

IBM and AMD Open-Source Pelagos GPU Decoder Framework for Large-Scale qLDPC Error Correction Simulations

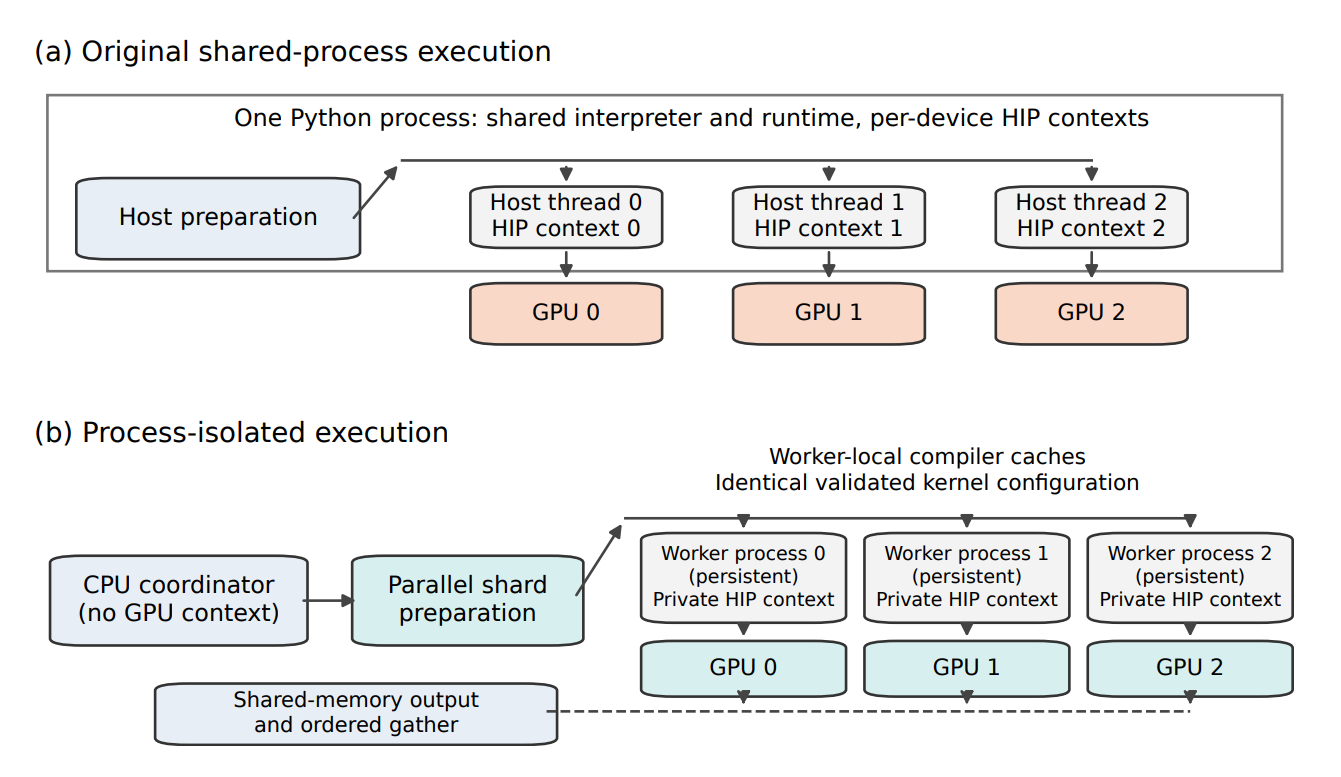
IBM and AMD have open-sourced Pelagos, a GPU-accelerated quantum error-correction (QEC) decoding framework for evaluating qLDPC codes at supercomputing scale. This release, announced at SC26, aims to advance quantum computing through vendor-neutral, efficient error correction, building on a joint QEC co-design platform. Pelagos offers significant speedups and efficient multi-GPU orchestration, enabling large-scale simulations crucial for fault-tolerant quantum computing.

Read at Quantum Computing Report

The Decoder Manuel Uth SI

Moonshot AI pivots Kimi models from coding to science as benchmark gains flatten

Moonshot AI is done chasing coding benchmarks, it says. The Beijing startup is pivoting its Kimi language models toward biology, chemistry, and pharma research, arguing that science demands smarter AI than law, finance, or code. The article Moonshot AI pivots Kimi models from coding to science as benchmark gains flatten appeared first on The Decoder.

Read at The Decoder

arXiv (research papers) Alec Eickbusch

Resolving and Suppressing Temporally Correlated Noise in Quantum Error Correction

Scaling fault-tolerant quantum error correction (QEC) requires suppressing errors in both space and time, yet standard logical memory experiments primarily probe spatial faults. Here, we use a 105-qubit Willow superconducting quantum processor to realize and scale the surface code stability experiment, which is alternatively sensitive to temporal error chains. Scaling from patch sizes of $3 \times 3$ to $7 \times 7$, we realize a timelike block suppression factor of $μ_T =…

Read at arXiv (research papers)

arXiv (research papers) Arunkumar V SI

Optimistic Verifiers Get Hacked: Reward Hacking Under an Exact Process Oracle

Reinforcement learning from verifiable rewards inherits whatever its verifier gets wrong. Outside mathematics and code the verifier is a proxy, a rubric, a learned judge or a hand-written checker, and its distance from the true objective is never measured, so a rising reward cannot be told apart from a hack. We build a setting where the true reward is exactly computable at the process level: executable authorization policies over 124,416 contexts admit an oracle that lists…

Read at arXiv (research papers)

Meduza

Russian court fines opposition politician Yulia Galyamina for disobeying police after holding her for nearly two days in Kazan

Kazan’s Vakhitovsky District Court fined politician Yulia Galyamina 2,000 rubles for disobeying police under Article 19.3 of Russia’s Code of Administrative Offenses, the legal aid project Slovo Zashchite reported.

Read at Meduza

The Quantum Insider Resonance

From First-Timers to PhDs: 1,000+ Builders Take on Quantum at the Qollab × IonQ Hackathon

Insider Brief Last month, more than 1,000 students, researchers and professionals in 37 countries spent a weekend writing quantum software, competing at 22 university sites from Finland to Argentina. Some of the best work came from people who had never written a line of quantum code. An avionics engineer in Argentina taught himself from online

Read at The Quantum Insider

Google (The Keyword) Naomi Ben-Ayoun General Manager, AdMob

New Google AdMob AI tools help app creators build, fix, and grow faster

New Google AdMob AI tools help app developers fix setups fast, protect brand safety, and automate monetization in code.

Read at Google (The Keyword)

arXiv (research papers) Hugo Delavenne Security

A counterexample to the soundness of the Flowering IOPP for codes on graphs

The Flowering protocol of Delavenne, Medevielle and Roussel (ISIT 2025, arXiv:2501.14337) and its generalization by Delavenne and Lallemand (CANS 2025, arXiv:2508.10510) are Interactive Oracle Proofs of Proximity (IOPPs) for codes on graphs with Reed-Solomon local codes. Similarly to FRI for Reed-Solomon codes, the graph is recursively cut into isomorphic subgraphs and the word is folded along the cuts. We show that the soundness claims of both papers are false. The commit…

Read at arXiv (research papers)

Older stories