Results for “Code”

The Guardian World Donna Lu Assistant editor, climate, environment and science

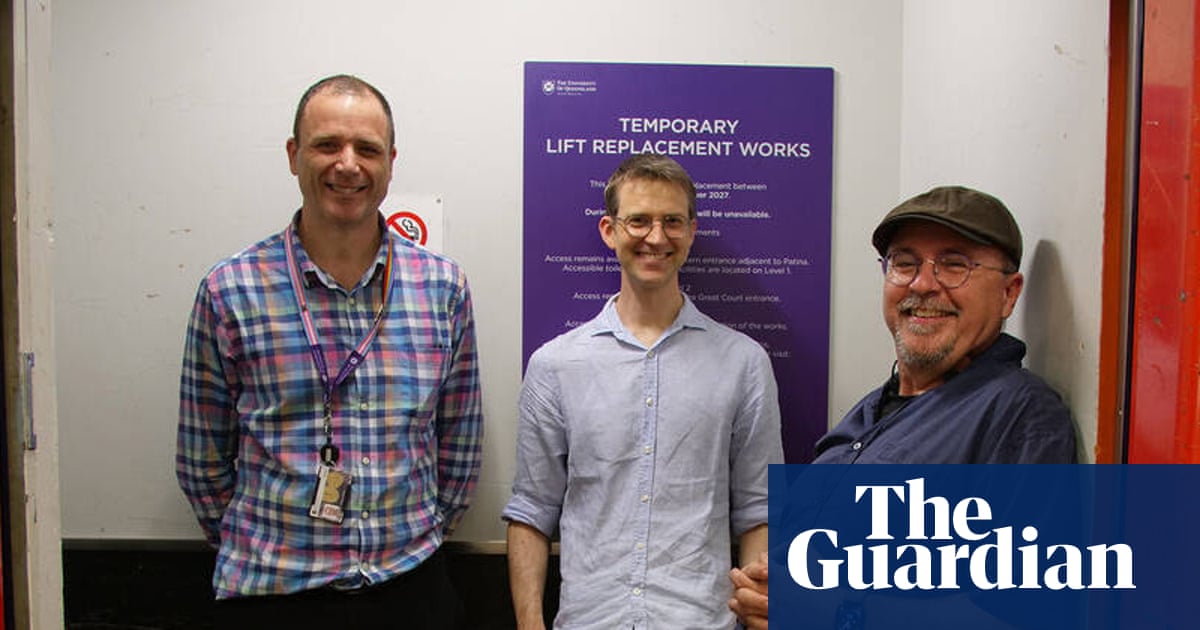
An elevator, a brick wall and a bathroom: scientists use gravity to send ‘practically unblockable’ message

Australian physicists chose to transmit the word ‘gravity’ in binary code through brick wall Get our breaking news email, free app or daily news podcast Australian scientists have used gravity as a means of communication, in a proof-of-concept experiment involving a snail-paced 1950s elevator, a brick wall and a men’s bathroom. Physicists at the University of Queensland have used gravity to transmit a “practically unblockable” message about 70cm through a brick wall, by…
Read at The Guardian World

Android Authority Aamir Siddiqui Gadgets

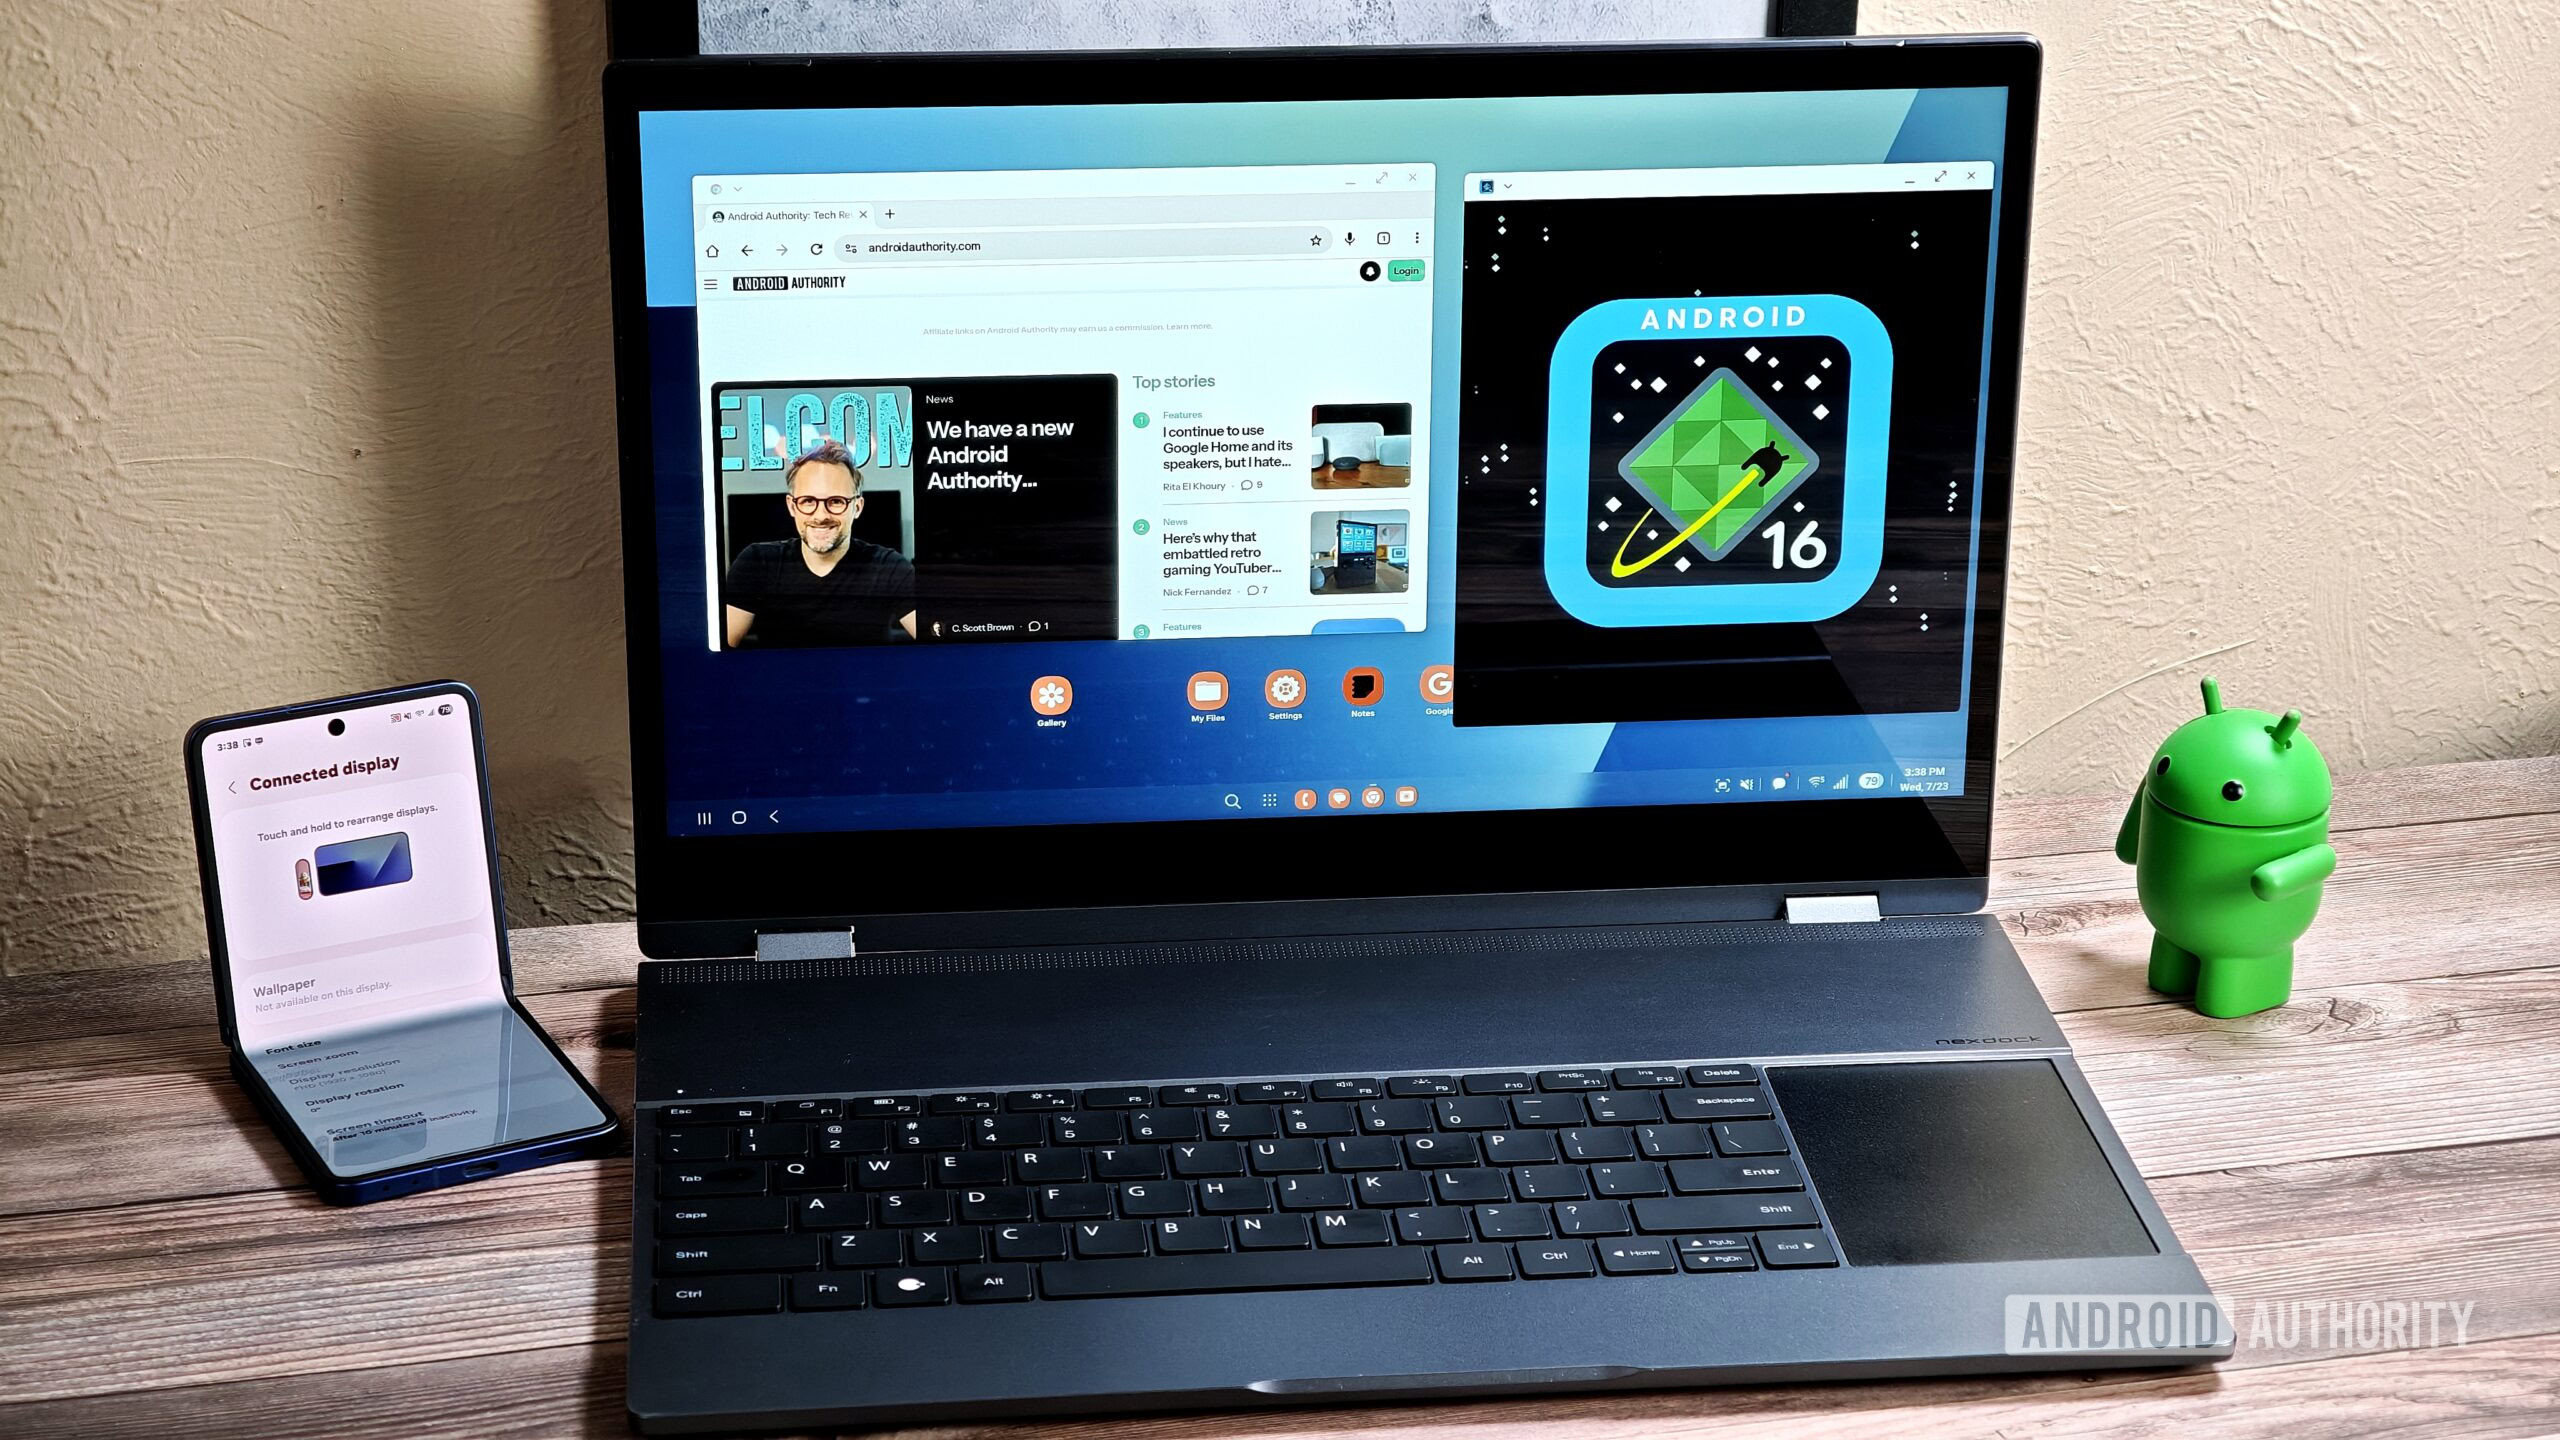
One UI 9.5 code reveals Samsung’s dedicated Android laptop interface with Circle to Search

Samsung’s Origin laptops could get their own taskbar, lid controls, and haptic touchpad settings, separate from DeX.

Read at Android Authority

arXiv (research papers) Tim Barsch Security

SCARVA: Interpretable Agentic Reasoning in Software Supply-Chain Analysis

Complex applications may inherit security vulnerabilities from their dependencies, though a vulnerable dependency does not necessarily endanger the application. Existing tools flag dependencies associated with public vulnerabilities, and more advanced ones analyze the call graph to assess whether the vulnerable code is reachable. However, these approaches are limited to specific programming languages and ecosystems. LLM agents are promising candidates for this task, yet they…

Read at arXiv (research papers)

Help Net Security Zeljka Zorz Security

Exploited Puppet flaw puts the server that configures your endpoint fleet at risk (CVE-2026-115731)

Attackers are exploiting CVE-2026-115731, a critical remote code execution vulnerability in Perforce Puppet Enterprise, an enterprise solution used by IT teams to centralize and automatize endpoint management. Details about the in-the-wild attacks have yet to be made public, but the US Cybersecurity and Infrastructure Security Agency (CISA) added the flaw to its Known Exploited Vulnerabilities catalog on Tuesday and ordered US federal civilian agencies to address it by…

Read at Help Net Security

Help Net Security Sinisa Markovic Security

Credential stealer slipped into Microsoft’s official Python agent framework

Two releases of Microsoft’s official agent-framework package on the Python Package Index (PyPI) carried code that steals cloud and CI/CD credentials from developers’ systems. Agent Framework is Microsoft’s open-source toolkit for building AI agents and running them in workflows. Three supply chain security companies, StepSecurity, OX Security and Socket, caught the malicious versions and shared their analysis. “On November 17, 2026, versions 1.26.1 and 1.26.2 of the official…

Read at Help Net Security

The Hacker News Security

Everything Is a Web Application, Including Your Firewall

One of the early targets of PHP2Shell exploitation was the firewall. On October 28, Palo Alto Networks confirmed that attackers were exploiting the two PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, against PAN-OS management interfaces exposed to the internet. Both flaws let anyone execute code on the web server without authentication. The disclosure itself went a little wrong.

Read at The Hacker News

Android Authority Aamir Siddiqui Gadgets

Exclusive: Samsung’s upcoming 14-inch and 16-inch Android laptops are codenamed ‘Origin’

One UI 9.5 beta code reveals Wi-Fi-only XE940 and XE960 models powered by Qualcomm's Snapdragon X Elite chip.

Read at Android Authority

Help Net Security Anamarija Pogorelec Security

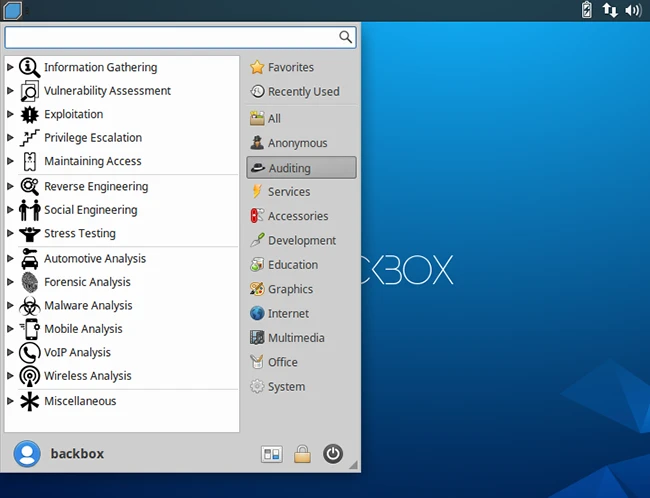
BackBox Linux 10 brings new hacking tools and Ubuntu 26.04 support

BackBox Linux is a free, open source penetration testing distribution made by BackBox, a non-profit community project that keeps its own repositories of ethical hacking tools. On November 19 the project released version 10, codenamed Resolute Raccoon. It’s built for compatibility with Ubuntu 26.04 LTS and ships with the Linux 7.0 kernel and the Xfce 4.20 desktop. It also changes how anonymous mode handles traffic: DNS queries now go through Tor, and IPv6 is blocked … More →

Read at Help Net Security

SecurityWeek Ionut Arghire Security

Splunk Patches Nearly 140 Flaws Across Three Core Products

The security updates resolve critical and high-severity issues leading to authentication bypass, remote code execution, and privilege escalation.

Read at SecurityWeek

SecurityWeek Ionut Arghire Security

F5 Patches Critical NGINX2Root Flaws as PoC Exploits Go Public

The five NGINX2Root vulnerabilities could allow remote, unauthenticated attackers to execute arbitrary code.

Read at SecurityWeek

Digital Trends Vikhyaat Vivek

Microsoft’s new AI coder is gunning for Claude and ChatGPT. It’s coming with a price advantage

Microsoft has launched two homegrown AI coding models that promise performance comparable to expensive OpenAI and Anthropic alternatives at a fraction of the cost, with both already available in GitHub Copilot.

Read at Digital Trends

arXiv (research papers) Shengwei You Security

Signed but Unbound: The Authority Gap Between Agent Commerce Mandates and Crypto Wallet Signatures

When an artificial intelligence agent pays with a stablecoin, the commerce protocol can specify the merchant, order, amount, and facilitator. The token contract enforces the fields the wallet signs. We call the difference the authority gap, define nine constraint classes, and derive them for 12 authorization configurations, including Coinbase's deployed Commerce Payments Protocol. All 31,800 trials on local copies of deployed contract code match the derivation. A controlled…

Read at arXiv (research papers)

The Hacker News Security

Ruby Releases Fixes for 7 Regex and String Flaws, Warns 5 Have Proof-of-Concept RCE

Ruby contains seven memory-safety flaws in its regular expression engine and its string case-conversion code. For five of them, its maintainers say, proof-of-concept exploits, or PoCs, have shown that crafted input can run code on the machine. "We are aware of PoCs that prove some of them can be used to trigger remote code execution," the maintainers said. The project released fixed versions

Read at The Hacker News

arXiv (research papers) Zhenhao Tian Security

Hardening JavaScript Programs against LLM-Based Vulnerability Detection

JavaScript programs are often distributed as source code, so attackers can analyze them for vulnerabilities. LLM-based vulnerability detection agents now make this analysis much easier. To mitigate this emerging threat, we present AntiAgent, a defense that lets developers harden their programs against such detection agents. AntiAgent transforms a program before release to impede an agent's analysis. To find effective transformations, AntiAgent evolves a corpus of programs…

Read at arXiv (research papers)

The Hacker News Security

Researcher Demonstrates Database RCE Exploits Affecting PostgreSQL, MySQL and Oracle

Low-privilege database accounts that cannot read a single application table can still be used to run code on the database server itself, a researcher has shown, by reaching memory-corruption bugs in the engine code behind ordinary SQL. The exploits, published yesterday, are the researcher's proofs of concept against PostgreSQL, MySQL and ClickHouse, plus a separate Oracle chain that needs no

Read at The Hacker News

OpenAI News SI

How OpenAI’s Performance Factory keeps ChatGPT fast

Learn how OpenAI built the Performance Factory, a system of Codex-powered workflows that finds and fixes performance issues to help keep ChatGPT fast.

Read at OpenAI News

arXiv (research papers) Jingyi Zhou

GRODE-RTL: Source-Mapped Dependency Views for LLM-Based RTL Repair

Large Language Models show great potential for automated Register-Transfer Level repair, yet they struggle with non-local faults where root causes and failing outputs reside far apart in source code. Treating RTL as a flat token sequence obscures hardware dataflows, whereas exposing complete synthesized graphs overwhelms the model with fine-grained metadata. To resolve this representation dilemma, we propose GRODE-RTL, an anchor-centric representation that extracts the…

Read at arXiv (research papers)

YourStory Startups

AI can write code, but knowing what to build still matters

At TechSparks 2026, Srinivas Chamarthy of Diligent India, Madhusudan N. Murthy of EY GDS, and Arun Kalyanaraman of Target discussed why domain expertise, engineering skills, and human judgement remain important as AI makes software development more accessible.

Read at YourStory

The Hindu International

U.S. court orders delivery of summonses to Doval, Goel through Delhi courts

Citing the Hague Conventions and relevant provisions of the Indian Code of Civil Procedure (CPC), a U.S. federal court Judge Katherine Polk Failla said foreign courts can serve summonses to Mr. Doval and Mr. Goel through Indian courts

Read at The Hindu International

Analytics India Magazine Kanishk Singh SI

GitHub Now Lets Indian Enterprises Store Code Locally Ahead of DPDP Deadline

Global AI labs and cloud hyperscalers have accelerated their data residency and local inference rollouts in India ahead of full enforcement of the DPDP Rules.

Read at Analytics India Magazine

MarkTechPost Asif Razzaq SI

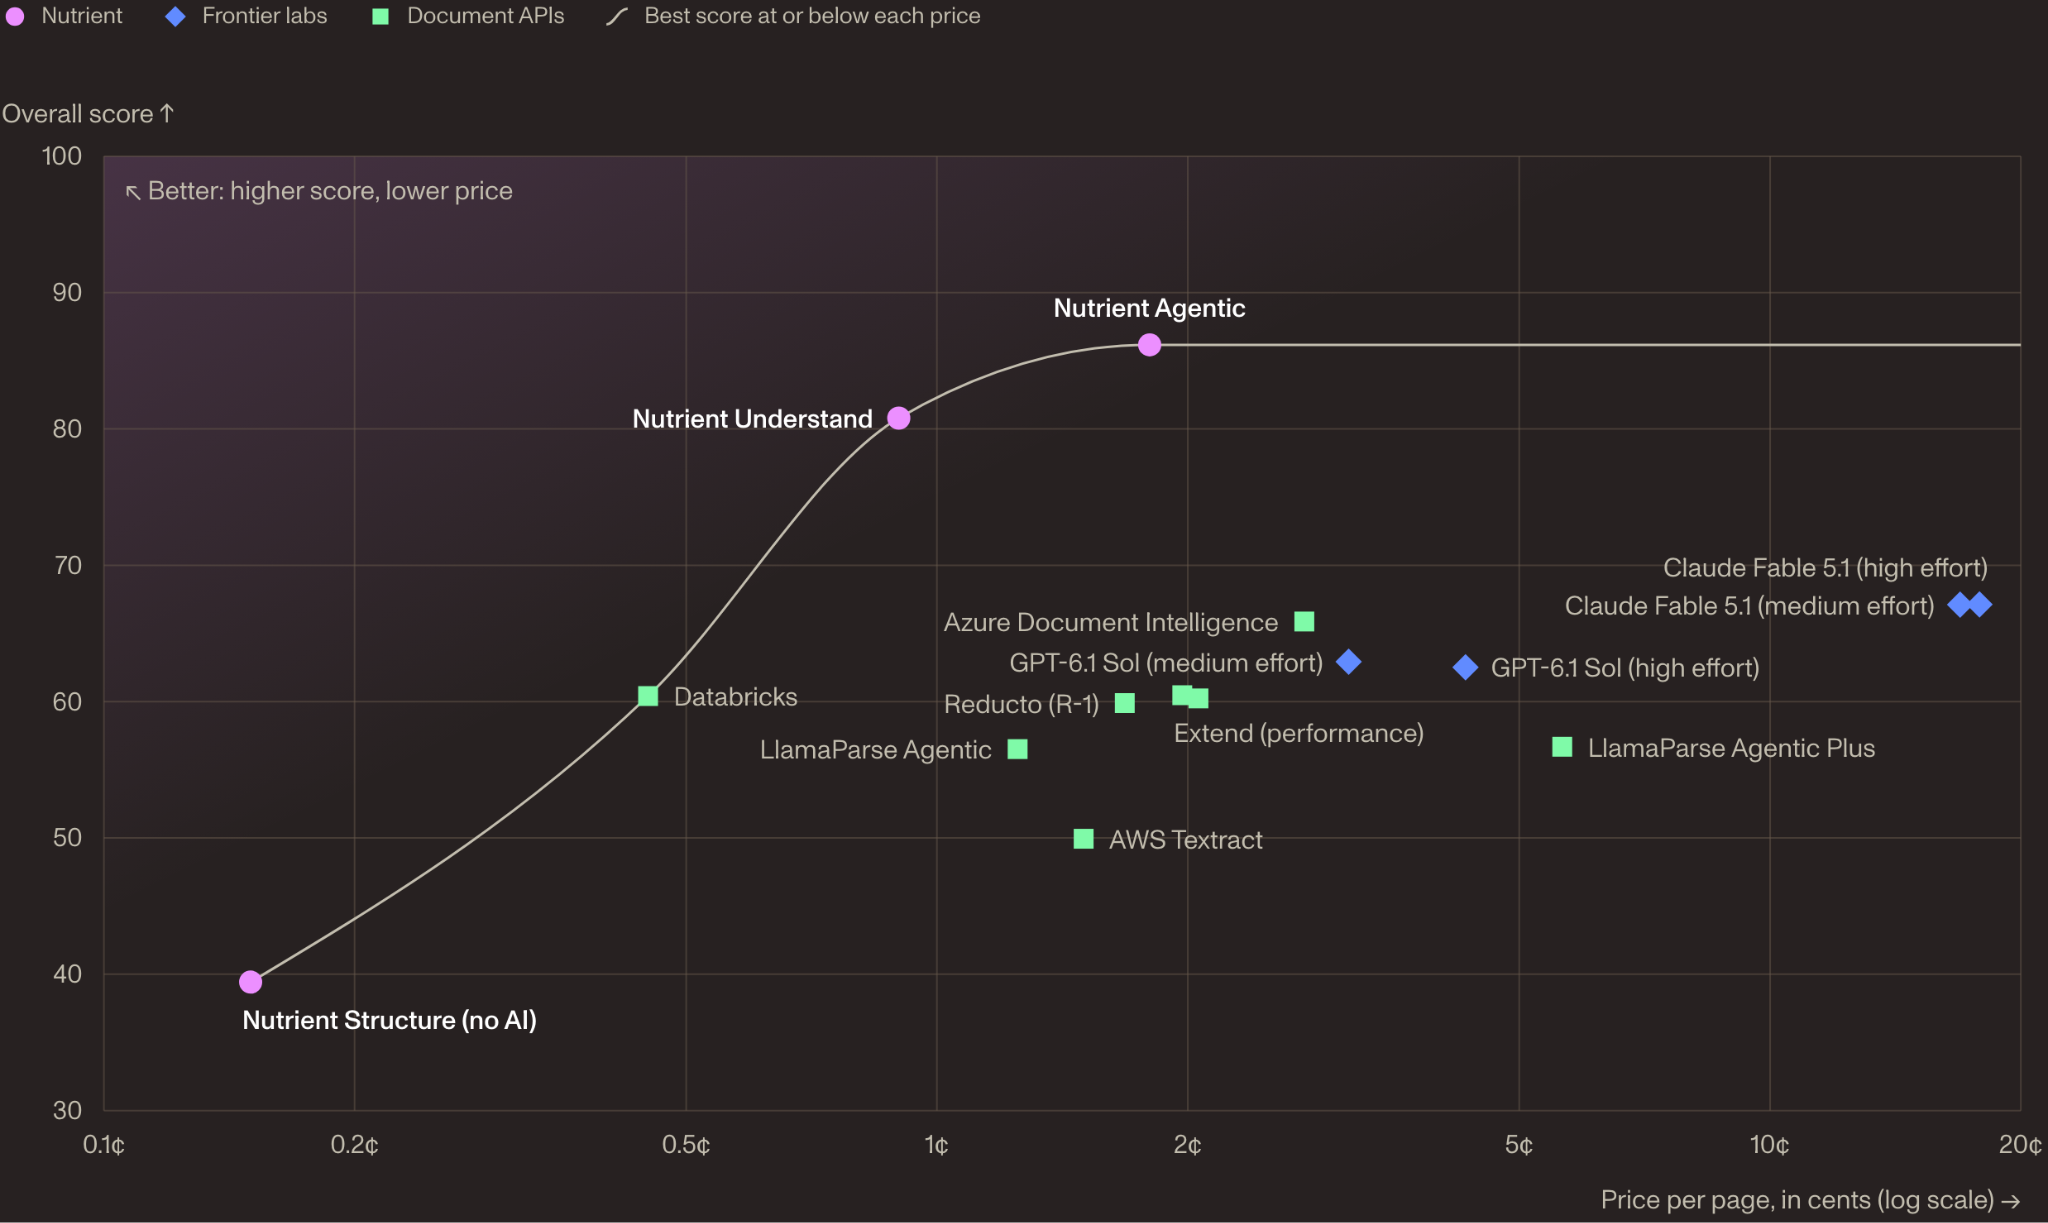
Nutrient Data Extraction API: JSON Matching Your Schema With Per-Field Citations and Confidence

Nutrient Data Extraction API parses PDFs, scans and Office files into JSON matching your schema. Fields carry page, region and match-label citations, and Studio lets teams test before writing code.

Read at MarkTechPost

arXiv (research papers) Siyang Chen SI

SGLayout: Schema-Guided Closed-Loop Refinement for LLM-Driven Parameterized Layout Generation

Large Language Models (LLMs) have shown strong potential in parameterized layout generation via tool-augmented code synthesis. However, LLMs lack spatial awareness, making one-shot generation unreliable. While layout quality can be evaluated with established techniques, a critical gap remains: geometric-domain evaluation outcomes cannot be directly translated into actionable code-level fixes, trapping iterative refinement in blind refactoring. We propose SGLayout, a…

Read at arXiv (research papers)

Eurasia Review RFA South China Sea

South China Sea Code Of Conduct Could Depend On Landlocked Laos – Analysis

By Taejun Kang Key Takeaways: Landlocked Laos could play a huge role in future negotiations between ASEAN and China on

Read at Eurasia Review

arXiv (research papers) Yixiong Chen SI

Pro$^2$ Agent: Scientific Problem Probing for Autonomous AI R&D

Large language model (LLM) agents can now autonomously conduct AI research by writing code and running experiments. They typically do so by iteratively optimizing a codebase, while ignoring the problem structure behind the task. This formulation is effective on simpler tasks, but on difficult problems it often gets stuck in the wrong solution region because the agent never explicitly represents its understanding of the problem. We introduce Pro$^2$ Agent, which shifts the…

Read at arXiv (research papers)

arXiv (research papers) Minxing Chu

ReLay: Bidirectional Layout-Code Translation and Library Evolution for Reusable and Process-Portable Analog Design

Analog layout generators provide a programmable interface for design reuse and process migration, but their coverage is limited by handcrafted libraries. The designer knowledge embedded in complete layouts remains implicit in their geometry, making it difficult to capture in reusable generator libraries. We present ReLay, a bidirectional layout-code framework that recovers generator programs from existing layouts, enabling cross-PDK portability and parametric resizing of…

Read at arXiv (research papers)

arXiv (research papers) Ahmet Efe Security

Verified Netlist-to-RTL Recovery with LLM Agents

Gate-level netlists circulate among IP integrators and foundries and can be extracted from chips. Reverse engineering them into readable register-transfer-level (RTL) code would help an adversary understand and modify a design, but remains difficult because word-level operations are scattered across many gates. Large language models (LLMs) can write and optimize RTL, but often fail to recover it from a whole netlist. We propose LOCA (LOgic Cone Attack), an LLM-based attack…

Read at arXiv (research papers)

OpenAI News SI

Explore the Codex Security Plugin

Watch a demo of the Codex Security Plugin and see the workflow in action, from getting started to reviewing the results shown in the recording.

Read at OpenAI News

TechCrunch Aisha Malik SI

Snapchat now lets developers build AR Lenses with AI assistants like Claude Code and Cursor

Lens creators can describe the Lens they want in plain language, and their AI assistant handles the process from start to finish, Snapchat says.

Read at TechCrunch

Older stories