Help Net Security

Recent stories from Help Net Security.

Help Net Security Anamarija Pogorelec Security

Apple details Secure Exclaves, isolated runtimes for camera and microphone data

Apple published details of Secure Exclaves, a security architecture designed to protect camera and microphone data during background processing. Apple says data processed and analyzed within Secure Exclaves cannot be accessed by the main operating system, apps, or the company itself. The company uses Secure Exclaves for person recognition on HomeView, as well as for Siri Recap and Live Rewind. The architecture also protects the on-screen camera and microphone indicators on…
Read at Help Net Security

Help Net Security Mirko Zorz Security

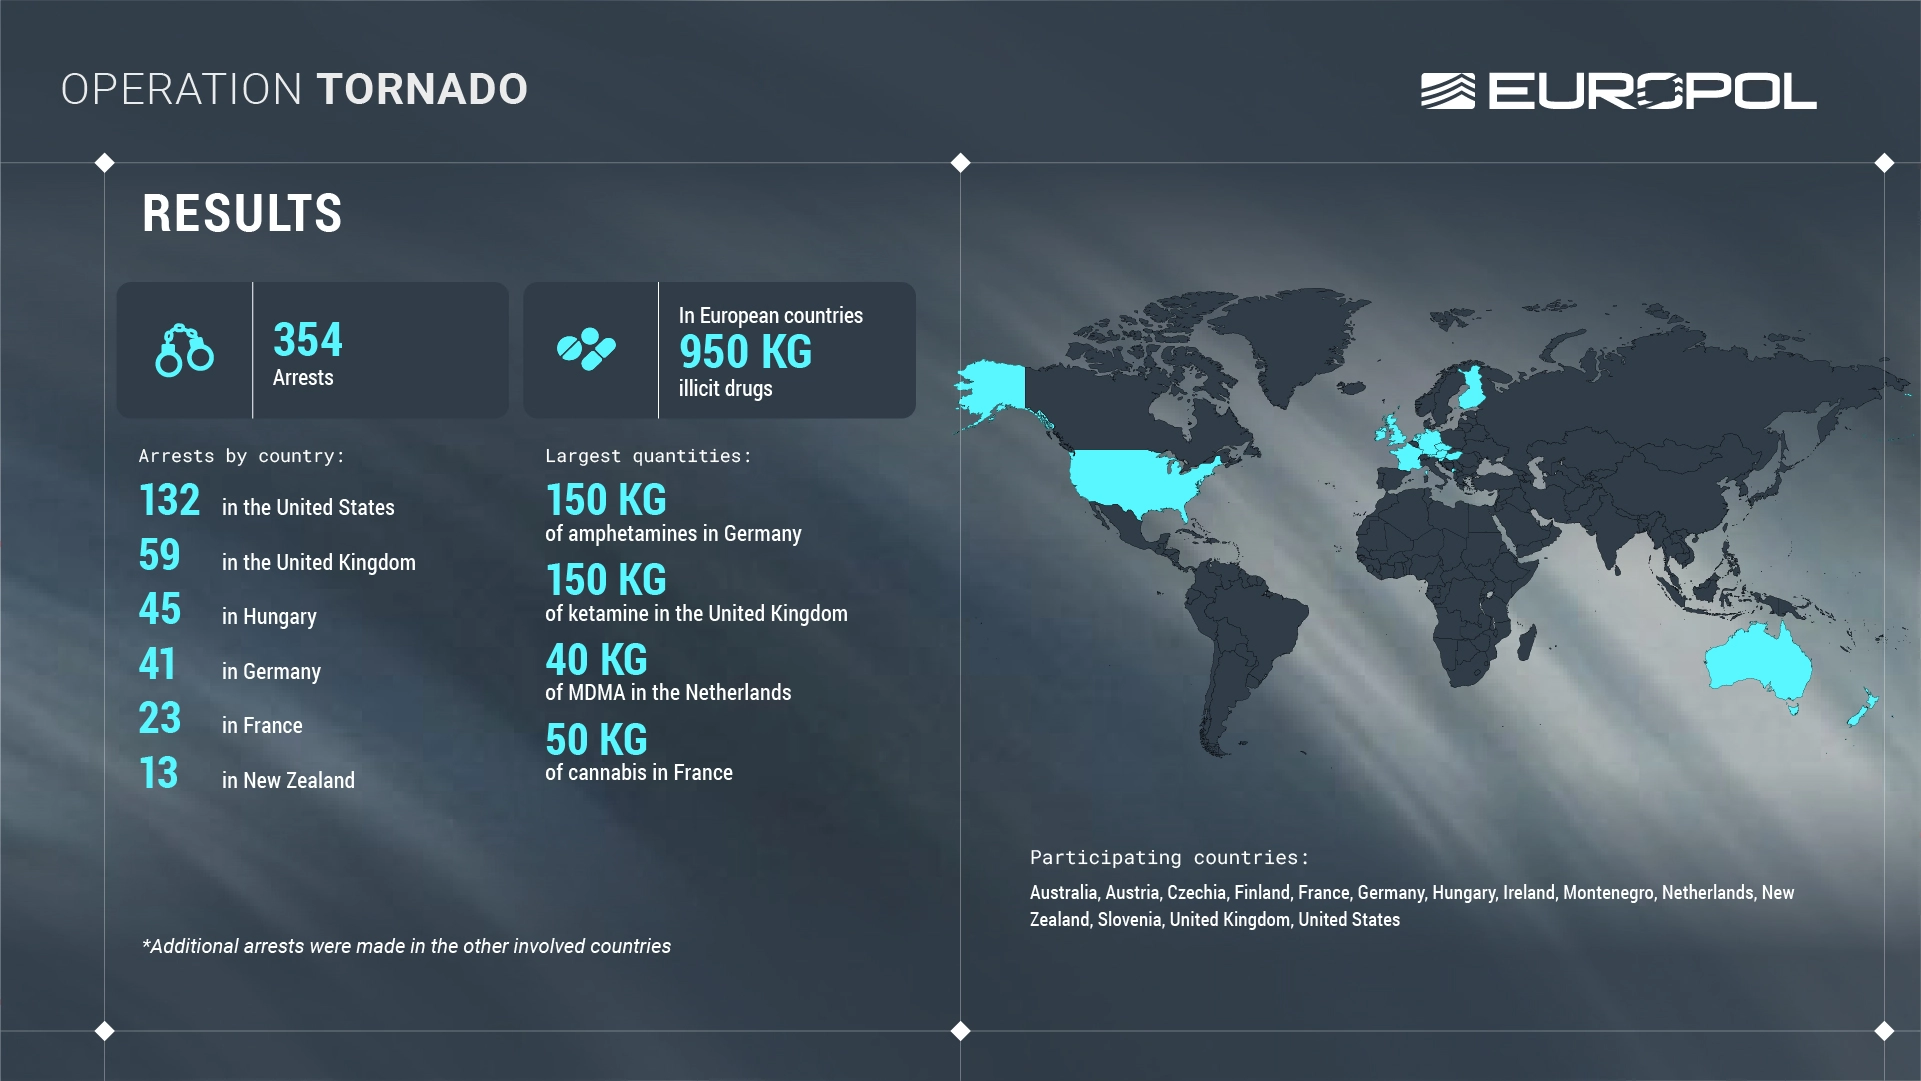
354 dark web vendors and buyers arrested in Operation TorNado

Europol and police in 14 countries arrested 354 dark web vendors and buyers in Operation TorNado, which ran from May 2025 to October 2026. Investigators went after people who had traded on five marketplaces that were already offline: Archetyp, Bohemia, Nemesis, Kingdom and Tor2Door. Seized money (Source: Europol) The people who used those markets were still exposed after the sites went dark. Police also went after vendors and buyers on forums, single-vendor shops and…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

OpenAI’s Daybreak brings AI agents to security testing and vulnerability fixes

OpenAI is bringing AI agents into more of the software security process with Daybreak, pairing web application penetration testing with tools that investigate vulnerabilities and develop fixes. The two offerings, Red Team and Defense Factory, connect the work of finding security weaknesses with patching and retesting them. Red Team tests applications and verifies fixes Daybreak Red Team, offered through an early-access program, uses coordinated agents to examine application…

Read at Help Net Security

Help Net Security Mirko Zorz Security

Stolen webcam clips of 900+ victims feed North Korea’s $400 million fake Zoom scheme

North Korean state hackers have stolen more than $400 million in cryptocurrency over the past 18 months by pulling targets into fake Zoom and Teams calls filled with webcam footage of earlier victims. The FBI calls the scheme FaceStealer. It has seized more than 900 of those recordings, and on November 12 it warned crypto and web3 workers and open-source maintainers about the scheme. Source: FBI Every successful call infects the target and records them, … More →

Read at Help Net Security

Help Net Security Mirko Zorz Security

How attackers turned a Teams meeting booking into a device code phishing trap

Attackers used a fake Microsoft Teams meeting scheduler to trick an employee at a construction company into approving a device code sign-in. They got a valid session token before Huntress’s security operations center identified the incident. Device code phishing abuses a real Microsoft sign-in flow. The attacker starts a sign-in, gets a short code back, and persuades the victim to type it into Microsoft’s genuine device login page. The victim enters the code, completes MFA ……

Read at Help Net Security

Help Net Security Mirko Zorz Security

Suspected North Korean IT workers reached onboarding at companies with open data

Material Security followed suspected North Korean fake IT workers through the hiring pipelines of organizations it monitors and counted 27 personas that reached onboarding over one year. At one company where a persona got that far in the past month, about 277,000 files containing Social Security numbers were shared company-wide or by public link. The personas are fabricated job seekers, complete with résumés and faces, applying for remote engineering roles. Over the year…

Read at Help Net Security

Help Net Security Mirko Zorz Security

Your pinned MCP server may not be as pinned as you think

An MCP server configured to run one fixed release on an administrator’s workstation ran with 15 different sets of dependencies over five weeks, with its configuration untouched. James Lagermann, Director of Technical Alliances at Corelight, found the drift in his company’s lab. Twenty-three of the server’s 69 packages changed versions, including the cryptography library, the JSON Web Token library and the MCP software development kit itself. MCP (Model Context Protocol)…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Digital sovereignty leaves enterprises chasing their own audit trails

94% of surveyed enterprises experienced at least one digital sovereignty challenge in the past three years, according to IBM’s Digital Sovereignty Index. Of those affected, 91% were required to demonstrate that they retained control during their most challenging event, and 81% had to provide formal evidence to regulators, auditors, customers or internal stakeholders. The report defines digital sovereignty as an organization’s ability to retain control and provide credible…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Google smart glasses privacy features cover wearers and the people around them

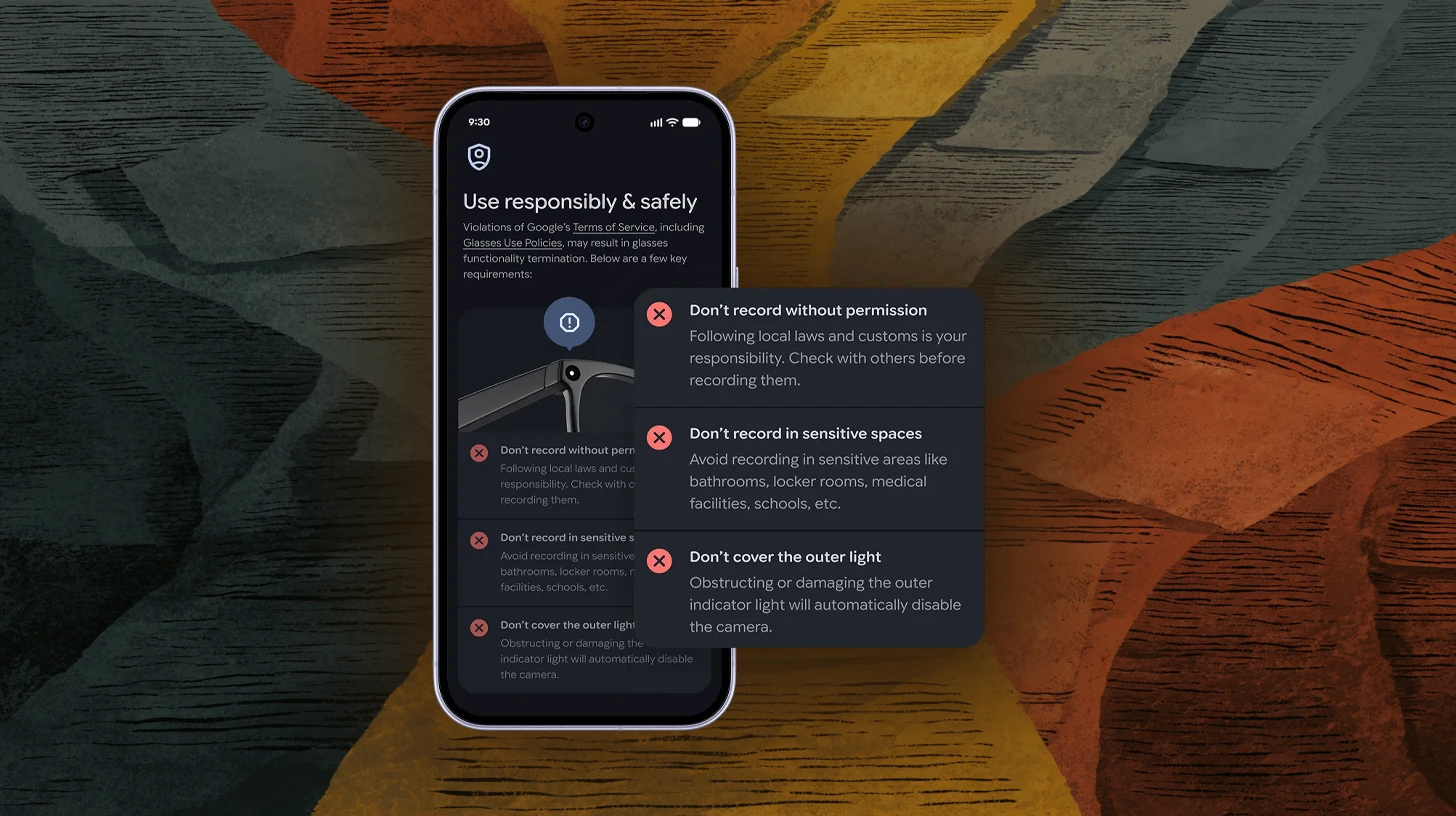
Google has built its Gemini-powered intelligent eyewear to stop taking photos and video when someone covers or tampers with the outward-facing recording light. Shahram Izadi, Google’s VP and GM of XR, laid out that safeguard along with face redaction, limits on data handling, and app restrictions. Bystanders told Google during years of research that they worried about being filmed without their knowledge, and that a sign of recording would help them most. Wearers face a ……

Read at Help Net Security

Help Net Security Mirko Zorz Security

Fake Zillow pages use ClickFix NetSupport RAT to target apartment hunters

EfficientIP Research Labs traced a ClickFix campaign that used fake Zillow apartment-review pages to install NetSupport RAT on visitors’ Windows computers. Each page showed what looked like a routine verification check. Behind it, the page quietly copied a PowerShell command to the clipboard and walked the visitor through pasting and running it. Doing that installs remote-control software that keeps its window hidden and starts back up every time the user logs in. Renters…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

PostgreSQL security update fixes 52 vulnerabilities, ends support for PostgreSQL 14

The PostgreSQL Global Development Group released PostgreSQL 18.7, 17.12, 16.16, 15.20 and 14.25 on November 12, fixing 52 security vulnerabilities and more than 140 other bugs. Most of those code execution bugs are memory errors or type confusion, where PostgreSQL handles a value as the wrong data type. They turn up in PL/Perl and PL/Tcl, text search functions such as ts_rank_cd(), parallel query, logical replication, dblink and statistics import. Thirty-two of the 52 CVEs…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Self-hosted Claude Managed Agents keeps agent credentials in your environment

Anthropic has released a self-hosted version of Claude Managed Agents. Companies can run the agent harness, sandboxes, credentials, and session history in their cloud or on-premise. The option opened as a private beta on November 12, and customers request access through their Anthropic account team. The change matters for agents that already work unattended inside corporate systems, fixing broken builds, testing releases, triaging alerts, and working through bug backlogs…

Read at Help Net Security

Help Net Security Industry News Security

Picus puts AI agents on the offensive with autonomous pentesting

Picus Security has announced Picus Autonomous Penetration Testing, an agentic pentesting capability that puts AI agents on the offensive: they think like attackers, chain real exploits toward an organization’s crown jewels, and prove what a breach would look like, under governance the agent cannot override. The launch rebuilds Picus’s automated penetration testing for the agentic era on five years of enterprise deployments and thousands of automated pentests. In the…

Read at Help Net Security

Help Net Security Mirko Zorz Security

Attackers breached 10 organizations with an open-source AI pentest framework

Chinese-speaking attackers used Cairn, an open-source AI penetration testing framework, to run 25 operations against at least 19 organizations in August and September 2026. Palo Alto Networks’ Unit 42 found that the attackers gained unauthorized access or pulled data at 10 of them, often after typing little more than a domain name and a one-line goal. Most of the targets fall into three groups: seven in the semiconductor and advanced-manufacturing supply chain, three in…

Read at Help Net Security

Help Net Security Mirko Zorz Security

Operation Endgame malware takedown turns up over 6 million stolen logins

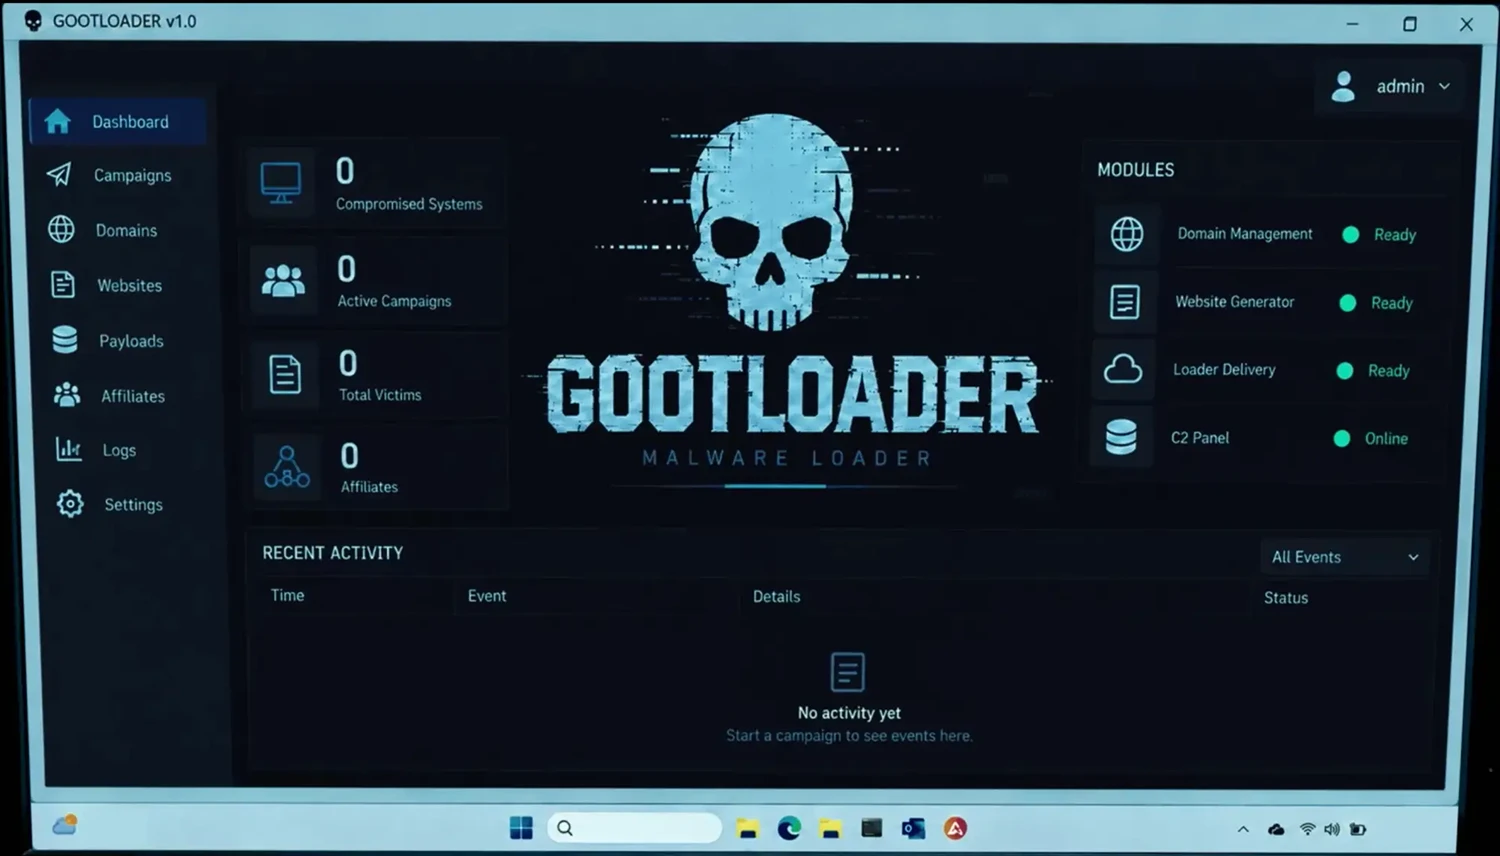
Police in nine countries, working with Europol, took down servers behind the Gootloader, CastleRAT and StealC malware operations this week and recovered more than 6 million credentials stolen from infected computers. Europol announced the action as the latest round of Operation Endgame, the international campaign against the services that give ransomware gangs their way into a network. Those logins are what reach ordinary users and companies. The suspects sold credentials…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Microsoft Entra adds a seven-day safeguard against irreversible identity deletion

Microsoft Entra’s Hard Deletion Protection, now in preview, gives administrators a seven-day window to recover selected identities before they can be permanently erased. The feature is designed to help organizations respond to accidental or malicious deletion of critical directory objects. It supports users that are not synchronized from on-premises systems, cloud-only groups, applications, and service principals. Entra Agent ID objects are covered through their underlying…

Read at Help Net Security

Help Net Security Mirko Zorz Security

Stolen Claude API keys can turn Claude Code into a remote-controlled implant

Darktrace researchers turned Claude Code into a remote-controlled implant in a lab test, steering the coding agent through the memory stores feature of Anthropic’s Claude platform and pulling a 1 GB file out through the Claude Files API. Once the agent was set up, every job and every result traveled through api.anthropic.com, the endpoint the agent already calls for inference, so the attacker’s traffic looked like a coding agent doing its job. The technique needs … More →

Read at Help Net Security

Help Net Security Zeljka Zorz Security

Photos: IRISSCON 2026 cybercrime conference

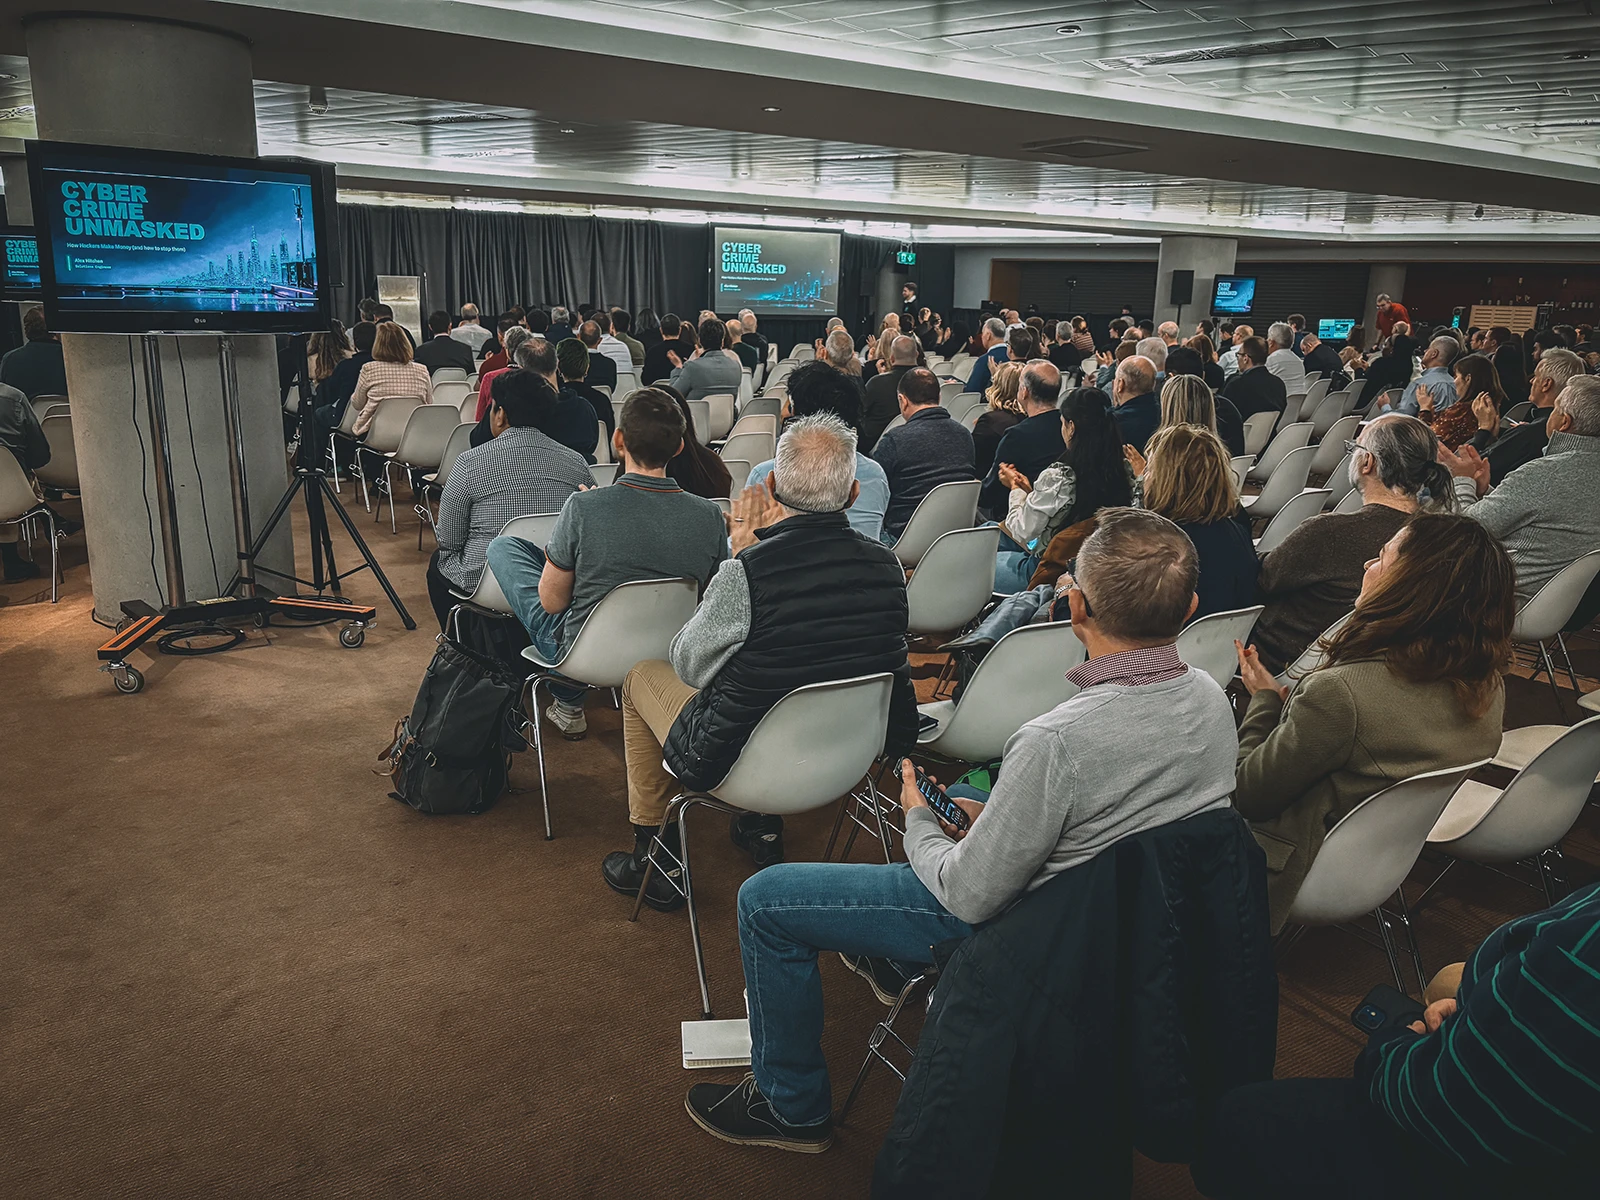
IRISSCON 2026, the annual cybercrime conference organized by IRISSCERT, took place at the Aviva Stadium in Dublin on November 11. The all-day event gives attendees a look at the cyber threats businesses are facing right now, along with practical advice on how organizations can respond to them. Help Net Security was there, and here’s a look at the day. Visitors at IRISSCON 2026 Selena Larson, staff threat researcher at Proofpoint, shared insight about GenAI use … More →

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

AWS Emulator: Open-source tool for testing AWS apps locally, built by autonomous AI agents

Amazon Web Services has released AWS Emulator, a free tool that simulates AWS services on a developer’s laptop, a development server or in a continuous integration (CI) pipeline. The company says autonomous AI agents wrote the tool entirely, with no code written or reviewed by its engineers. There is no additional service fee, users pay for AWS resources when they deploy applications on AWS. How three teams of AI agents build AWS Emulator Three teams … More →

Read at Help Net Security

Help Net Security Mirko Zorz Security

Check your GitHub repos: A secret stealer hit tens of thousands of them

A threat actor using stolen GitHub credentials has pushed a credential-stealing payload into tens of thousands of repositories since November 10. In more than 1,800 of them, the malware ran and shipped GitHub Actions secrets and cloud credentials to the attacker. Aikido spotted the campaign and named it wfx-loot. The name comes from the attacker’s own labels, “wfx” for the malware and “loot” for what it steals. Aikido counted 4,837 compromised accounts opening probe pull ……

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

.NET 11 security changes target the software supply chain

Microsoft has released .NET 11, a Standard Term Support (STS) release that will receive two years of support. .NET 10 is still the Long Term Support (LTS) option. The release covers C# 15, ASP.NET Core, .NET MAUI, and Windows development. Several of the changes affect software supply chain integrity, authentication handling, and platform lifecycle. .NET 8 and .NET 9 are out of support The most urgent item for defenders isn’t a new feature. .NET 8 … More →

Read at Help Net Security

Help Net Security Mirko Zorz Security

GitHub Agentic Autofix and the question of who owns a bad AI patch

In this Help Net Security interview, Marcelo Oliveira, VP of Product Management at GitHub, talks about who is accountable when an AI-generated patch fixes one flaw and introduces another. He explains how Agentic Autofix re-runs detection engines and project tests, and what a CISO should change before pointing an agent at thousands of old alerts. Oliveira also discusses which metrics show a codebase is getting safer, how GitHub picks the models behind autofix, and whether ……

Read at Help Net Security

Help Net Security Mirko Zorz Security

Dagster: Open-source cloud-native data pipeline orchestrator

Dagster is an open source orchestrator for data pipelines. It decides what runs, in what order, and when. It also tracks how the tables, datasets, machine learning models, and reports it manages connect to the data they came from. When a source table goes bad, the tables built from it carry the problem forward. Dagster’s lineage graph shows which ones sit downstream, and that list is the starting point for fixing a broken dashboard or … More →

Read at Help Net Security

Help Net Security Help Net Security Security

Who collects the keys when an AI agent retires?

Think about the last time a good engineer left your company. Someone collected the laptop and the badge. IT revoked their logins before the end of the day. Their manager reassigned the open tickets, and HR filed their records somewhere they’ll stay for years, in case anyone ever challenges a decision they made. Now think about the last time an AI agent left. Someone probably deleted it from the dashboard. I’ve started describing agents as … More →

Read at Help Net Security

Help Net Security Mirko Zorz Security

CISOs say OT will survive a cyberattack, but their engineers aren’t so sure

Ask industrial security chiefs whether their plants would keep running through a full IT compromise, and every one who answered the SANS 2026 ICS/OT survey says yes. Thirty-eight percent expect to run indefinitely on islanded ICS/OT systems, and 62% expect to get by temporarily on manual controls. None foresee degradation or a halt. The 696 practitioners SANS surveyed, the people who would run those manual controls, are less sure. Only 15% said their critical processes ……

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Bots pose as AI agents, AI agents pose as humans, and defenses believe both

Over one week in October, an online marketplace took 414,210 visits from traffic wearing the name of a widely used consumer AI agent. Every visit went for the sign-in page, and every one returned errors. Behind the name was a credential stuffing operation, with attackers running stolen username and password pairs against the site in bulk. The fake agent was busier than the real ones. Its volume came to about one and a half times … More →

Read at Help Net Security

Help Net Security Industry News Security

Kai extends Autonomous Defense Platform visibility to internet-facing assets

Kai has announced External Attack Surface Management (EASM), now available on the Kai Autonomous Defense Platform. The company also launched Kai Labs, an expanded research team focused on the hardest open problems where AI meets security. Most exposure management programs only see inside, so they miss the exposures attackers find first. With EASM, Kai unifies internal and external exposures into a single remediation plan, accelerating the path to zero. The external view…

Read at Help Net Security

Help Net Security Anamarija Pogorelec Security

Git fixes six vulnerabilities, including code execution during recursive clones

The Git project has released security updates addressing six vulnerabilities that could allow attackers to execute code, write to unintended files or cause memory corruption when Git processes malicious repositories or other specially prepared input. Code execution during cloning A vulnerability tracked as CVE-2026-111760 stems from an integer truncation in Git’s handling of its index. An extremely long file path can pass Git’s safety checks under one name and then be…

Read at Help Net Security

Help Net Security Industry News Security

Embed Security lets analysts teach its AI SOC Platform how to investigate

Embed Security announced new capabilities that let security teams teach Embed how they investigate, what matters in their environment, and how to improve their detections. With customer-built iSteps, expanded NoiseIQ Memories, and Detection Engineering, organizations can extend Embed’s built-in security expertise with their own knowledge and operating practices. Rather than programming workflows, analysts can teach Embed what they know, and its decision layer applies that…

Read at Help Net Security

Help Net Security Industry News Security

Rubrik enhances DevOps Protection to preserve legitimate work during recovery

Rubrik has announced cyber recovery capabilities for DevOps platforms Microsoft Azure DevOps and GitHub. With built-in anomaly detection, blast radius investigation, and surgical recovery, organizations will be able to detect suspicious activity on their code, instantly scope the impact of an attack, and undo the attackers’ changes from air-gapped, immutable backups, without disrupting legitimate developer work. “An organization’s source code is where innovation lives, and…

Read at Help Net Security

Older stories