Results for “Code”

arXiv (research papers) Hua Yang Security

PrivacyPR: A Dataset of Real-World Privacy Fixes for Benchmarking Privacy-Aware Code Review

Coding agents increasingly review code, yet whether they catch the privacy defects that laws such as the GDPR require software to avoid remains largely untested, partly because few datasets connect real privacy defects to their accepted fixes and review context. We present PrivacyPR, a dataset of 4,131 merged GitHub pull requests (PRs) from 1,469 repositories, created between June 2018 and January 2024. Each PR includes its commits, diffs, review discussion, and…

Read at arXiv (research papers)

OpenAI News SI

Introducing ChatGPT Wallet

Introducing ChatGPT Wallet, a secure way for agents in ChatGPT Work, Codex, and dots to complete purchases with user approval and existing card protections.

Read at OpenAI News

The Hacker News Security

FBI Says North Korean Hackers Stole Over $400 Million in Crypto Using Deepfake Video Calls

The U.S. Federal Bureau of Investigation (FBI) has established that threat actors tied to the Democratic People's Republic of Korea (DPRK aka North Korea) have stolen more than $400 million worth of cryptocurrency as part of a social engineering scheme codenamed FaceStealer in the last 18 months. As part of a coordinated set of actions announced by the U.S. government, the cloud-based

Read at The Hacker News

The Verge Allison Johnson SI

Claude’s Duet agent is a little neurotic and surprisingly helpful

Normally, the products I test don't offer to help me write up my experience with them. Duet is different. Claude Duet is Anthropic's AI agent for consumers, the latest attempt by an AI company to try to convince us that agents can be useful for people who don't write code. It's been an interesting couple

Read at The Verge

arXiv (research papers) Gang Zhou

Entropic quantum error correction for independent and correlated amplitude damping errors

The idea of using quantum entropy for quantum error correction (QEC) has existed for a long time. However, its computational complexity has limited its practical use: even a $[[4,1]]$ code for standard independent amplitude damping errors involves a $256\times 256$ Hermitian matrix, so the approach scales poorly as the codeword length increases. For correlated errors, the situation is even worse. In this paper, we show that, by using the insights developed in our previous…

Read at arXiv (research papers)

arXiv (research papers) Taro Suzuki

NPU-Accelerated GNSS Signal Acquisition

On small single-board computers (SBCs), GNSS signal acquisition is a major CPU load. This paper proposes using the neural processing unit (NPU) of an SBC not for machine learning but as an accelerator for the parallel code search in GNSS signal acquisition. The discrete Fourier transform (DFT) used in acquisition is decomposed by the four-step DFT into matrix products of small DFTs and expressed by $1\times1$ convolutions, element-wise products, and transposes, which NPUs…

Read at arXiv (research papers)

The Hacker News Security

SilentAir Hijacks Asian Telecom Networks to Intercept SMS 2FA Codes and Spy on Taiwanese Users

A newly identified spying group used hacked equipment inside Asian mobile operators to intercept the calls and texts of selected people, mostly in Taiwan. Enea, a telecom and cybersecurity software company based in Stockholm, found the group's attack sources in at least six Asian countries and named it SilentAir this week. It assessed with high confidence that SilentAir is a state-level actor,

Read at The Hacker News

eeNews Europe

Linux MMX optimisations set for removal in kernel 7.5

The last Linux MMX optimisations are set to be removed from the kernel, ending nearly three decades of specialised support for Intel’s original multimedia instruction set. A three-patch series submitted by Google engineer Eric Biggers removes obsolete assembly routines from the software RAID subsystem, eliminating 837 lines of code while adding just 12. The changes

Read at eeNews Europe

arXiv (research papers) Kuai Yu

DiffusionSSD: Achieving Extreme Visual Compression with Dual-stage Diffusion and Cross-level Near-Data Processing

Growing visual data overwhelms storage on resource-constrained edge devices, making compression essential. Traditional codecs offer inadequate rate-distortion performance, motivating the exploration of diffusion codecs. Diffusion codecs face two limitations: (1) At the algorithm level, diffusion decoders preserve perceptual quality under extreme compression, but require substantial computation. (2) At the architecture level, in NPU-centered devices, neural codecs occupy the…

Read at arXiv (research papers)

The Guardian UK Politics Simon Jenkins Geopolitics

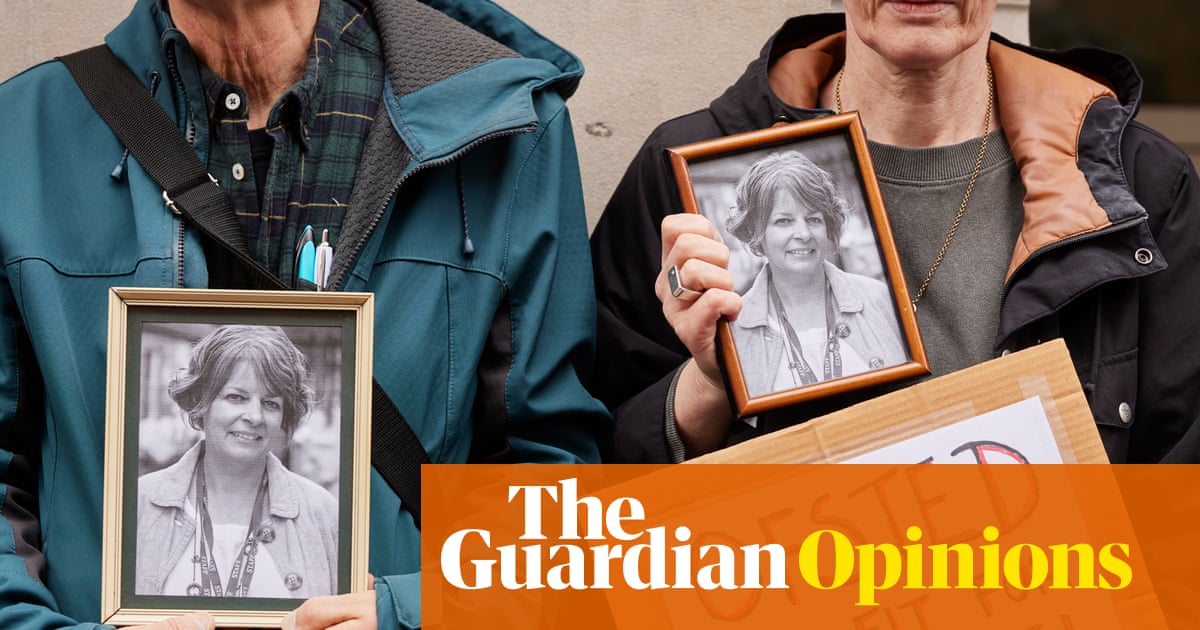
Ofsted’s menacing inspections are still disastrous. Schools should answer to the communities they serve | Simon Jenkins

For all the supposed improvements, inspectors still obsess over statistics and adjectives, but surely school success depends on teachers and parents The government regulation of state schools by Ofsted in England is a fiasco. Following the 2023 suicide of the Reading headteacher Ruth Perry, after her school was downgraded from outstanding to inadequate, Ofsted appears to have referred to a dictionary. Single words were replaced by colour-coded report cards, which use a wider…

Read at The Guardian UK Politics

SecurityWeek Ionut Arghire Security

Hackers Exploit New N-central Zero-Day Hours After PoC Publication

Dubbed 4EverAble2Shell, the flaw could allow remote, unauthenticated attackers to execute code with root privileges.

Read at SecurityWeek

The Register Simon Sharwood

Developer cleverly shrank 2,600 lines of C into a six-line script but still ending up losing sleep

It wasn't the not-very-legal source code raid that caused it, but a colleague who punted a pager

Read at The Register

Help Net Security Mirko Zorz Security

How attackers turned a Teams meeting booking into a device code phishing trap

Attackers used a fake Microsoft Teams meeting scheduler to trick an employee at a construction company into approving a device code sign-in. They got a valid session token before Huntress’s security operations center identified the incident. Device code phishing abuses a real Microsoft sign-in flow. The attacker starts a sign-in, gets a short code back, and persuades the victim to type it into Microsoft’s genuine device login page. The victim enters the code, completes MFA ……

Read at Help Net Security

The Manila Times Allen Limos South China Sea

Asean-China COC on South China Sea 70% done — DFA

MANILA, Philippines—The Department of Foreign Affairs (DFA) said the negotiations for the Code of Conduct (COC) for the South China Sea between the Association of Southeast Asian Nations (ASEAN) and China were now 70 percent complete. In a press briefing following the opening of the International Media Center in Pasay City for the 49th ASEAN Summit, DFA Spokesman for Asean matters Dominic Xavier Imperial said there was progress in the ongoing talks while emphasizing that…

Read at The Manila Times

Help Net Security Anamarija Pogorelec Security

PostgreSQL security update fixes 52 vulnerabilities, ends support for PostgreSQL 14

The PostgreSQL Global Development Group released PostgreSQL 18.7, 17.12, 16.16, 15.20 and 14.25 on November 12, fixing 52 security vulnerabilities and more than 140 other bugs. Most of those code execution bugs are memory errors or type confusion, where PostgreSQL handles a value as the wrong data type. They turn up in PL/Perl and PL/Tcl, text search functions such as ts_rank_cd(), parallel query, logical replication, dblink and statistics import. Thirty-two of the 52 CVEs…

Read at Help Net Security

9to5Mac Seth Kurkowski Gadgets

9to5Mac Daily: November 12, 2026 – OLED iPad Air rumors, MacBook Pro teardown

Listen to a recap of the top stories of the day from 9to5Mac. 9to5Mac Daily is available on iTunes and Apple’s Podcasts app, Stitcher, TuneIn, Google Play, or through our dedicated RSS feed for Overcast and other podcast players. Sponsored by Backblaze: Backup you can rely on. Save 20% with code 9to5daily.

Read at 9to5Mac

MarkTechPost Asif Razzaq SI

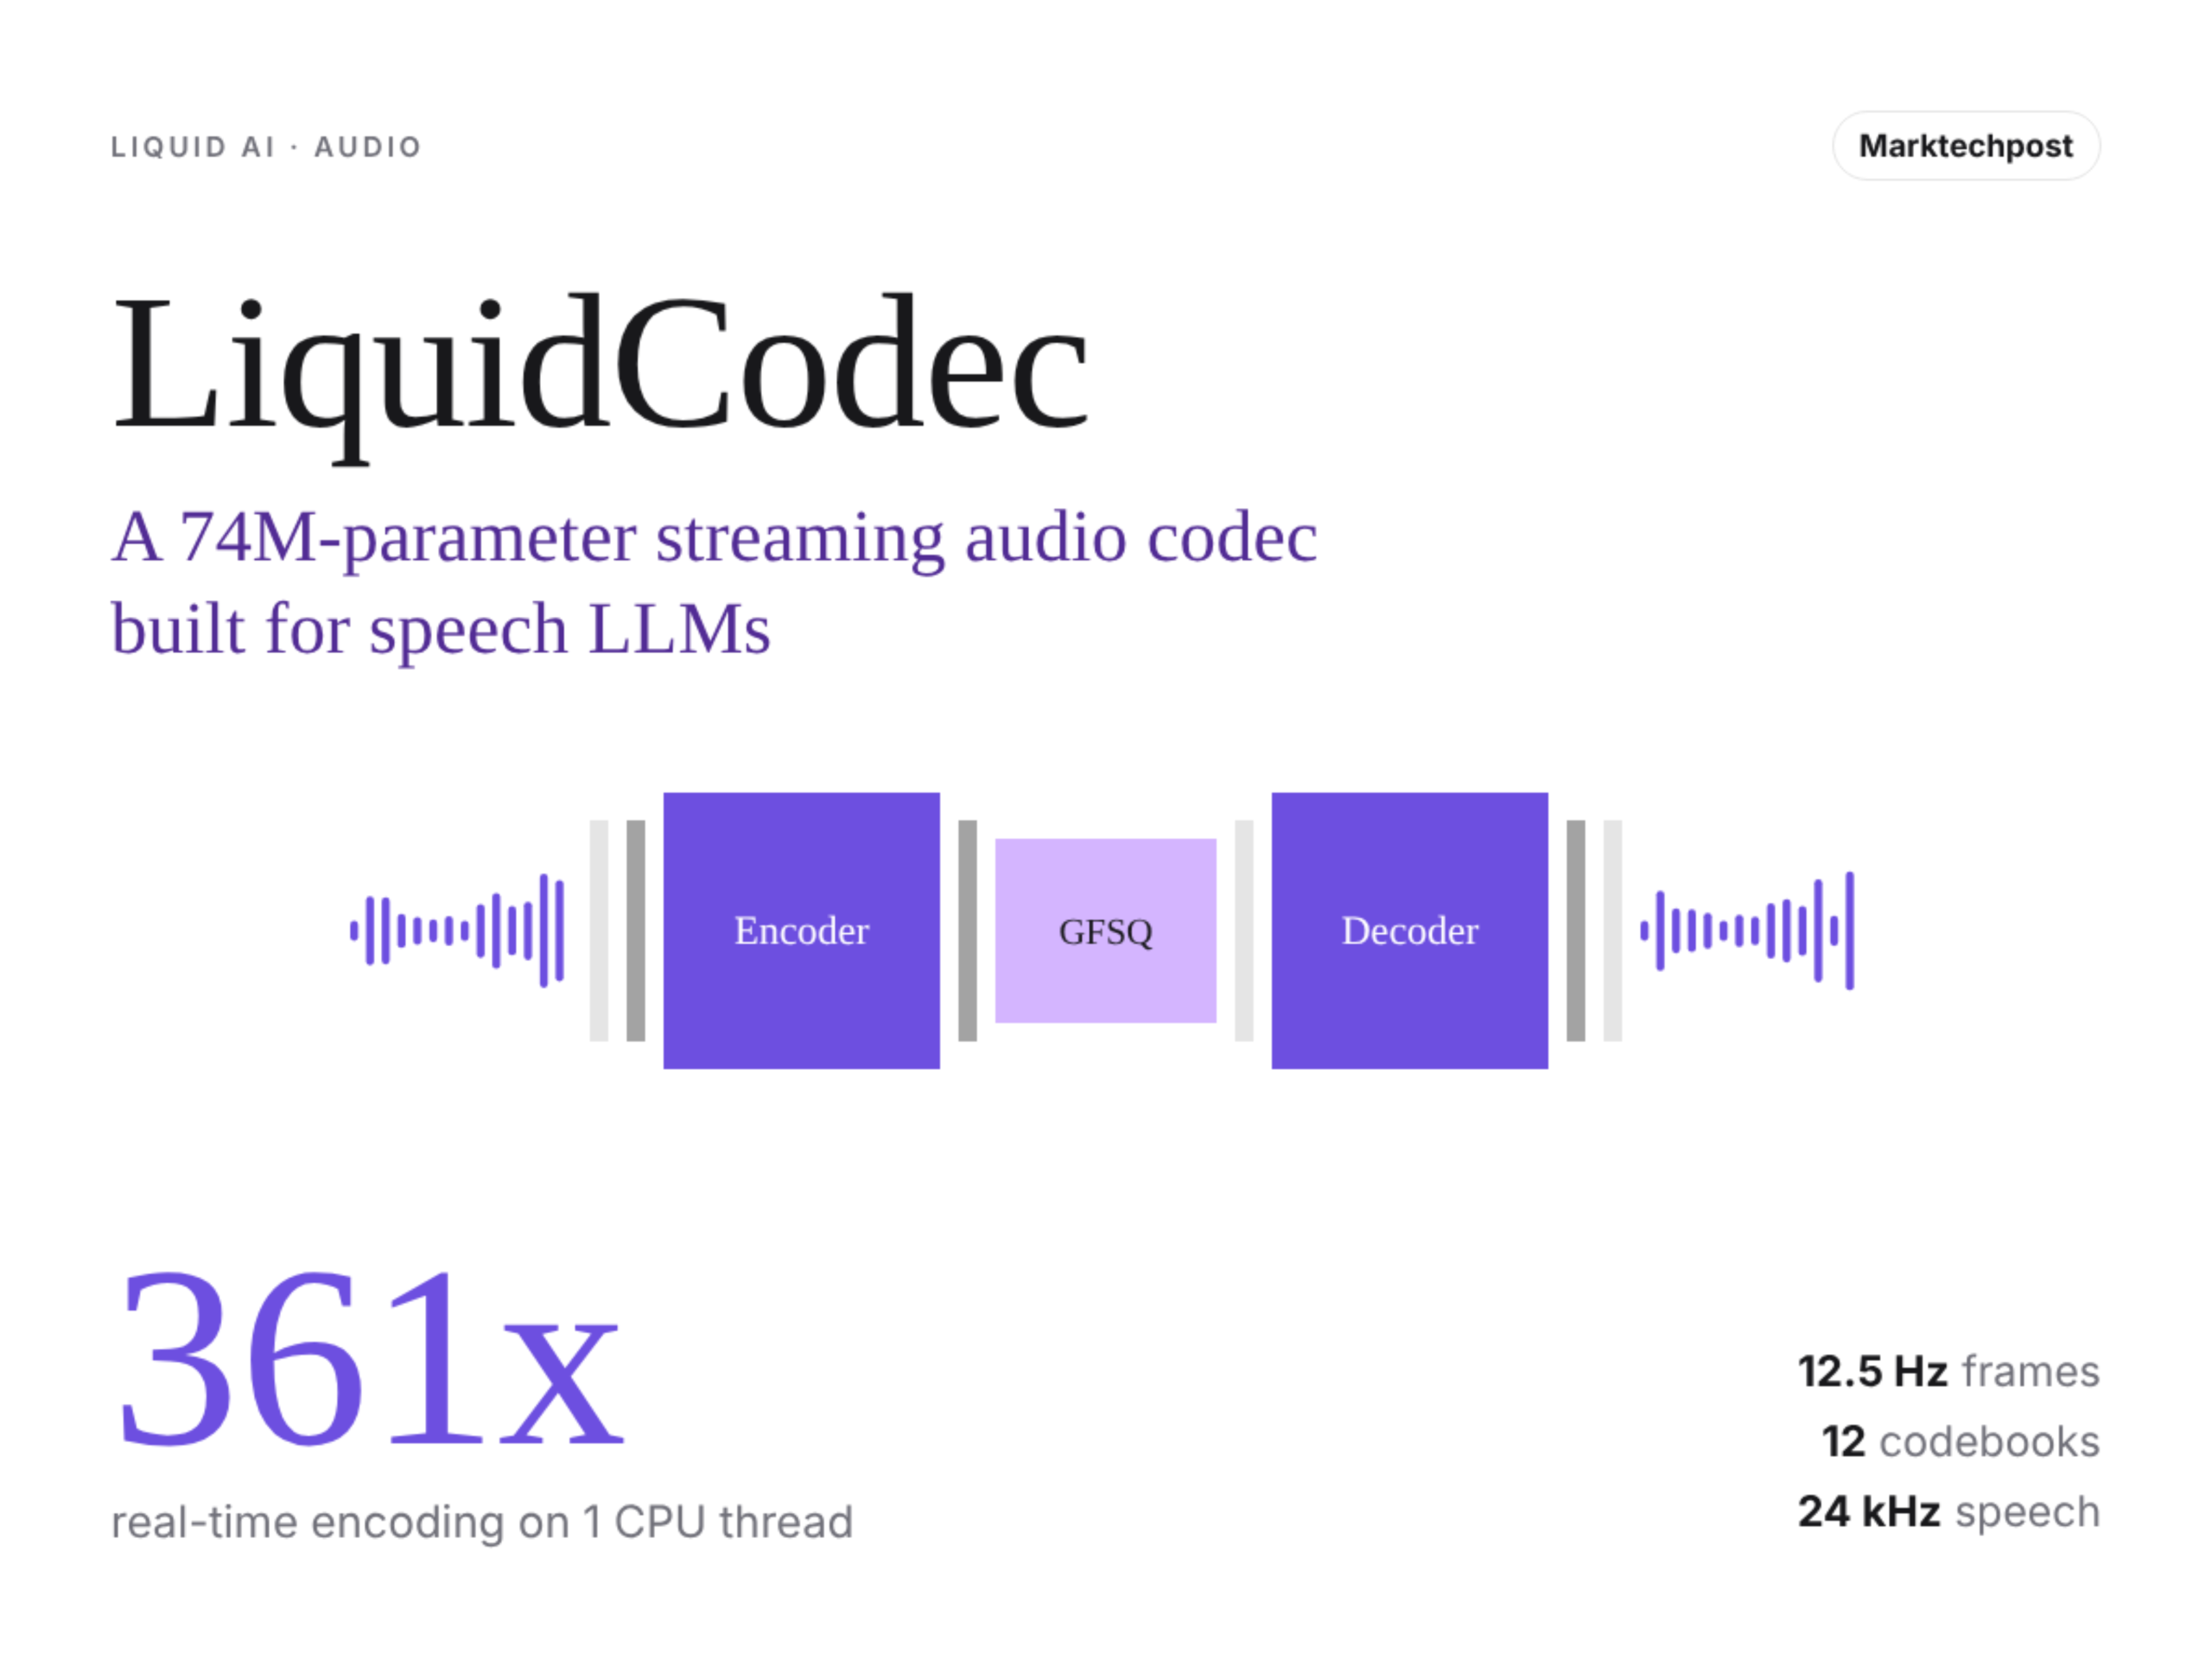
Liquid AI Releases LiquidCodec, a 74M-Parameter Streaming Audio Codec

Liquid AI released LiquidCodec, a ~74M-parameter streaming audio codec that powers LFM3-Audio-2B and LFM3-Omni-2B. It runs at 12.5 Hz with 12 codebooks and encodes about 361x faster than real time on a single CPU thread.

Read at MarkTechPost

SiliconANGLE AI Sloane Kali Faye SI

Google retools Kubernetes for AI agents instead of building a new stack

Agentic workloads are pushing Kubernetes into territory its creators never planned for. Agents generate untrusted code on the fly, sit idle for long stretches and churn through pods at a pace that strains the orchestrator’s control plane. Cloud providers are now rethinking how general-purpose a cluster should be. Google LLC’s answer is to stop treating

Read at SiliconANGLE AI

Ars Technica Kyle Orland SI

The Elder Scrolls' most obscure adventure gets a 4K PC makeover

N-Gage exclusive Shadowkey gets an AI-coded glow-up with plenty of new features.

Read at Ars Technica

AWS Machine Learning Blog Arun Chandapillai SI

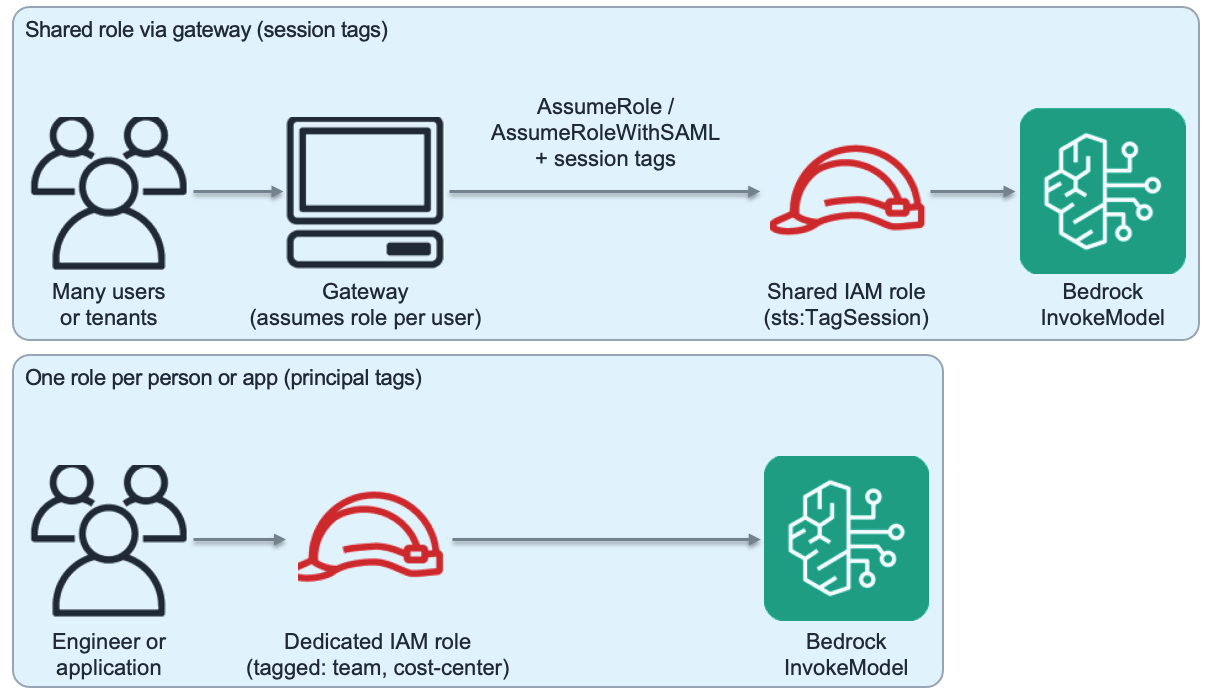
Tokenomics at scale: Track and cap Amazon Bedrock spend per IAM principal with CUR 2.0 and AWS Budgets

Get per-identity Amazon Bedrock cost visibility and enforceable spend limits using only AWS-native features, with no application code for the common case. Attribute spend with IAM principal tags, report with CUR 2.0 or Cost Explorer, and enforce with AWS Budgets actions that apply a Deny policy when a threshold is crossed.

Read at AWS Machine Learning Blog

The Hacker News Security

New SignDrop Zero-Day Exploit Turns Windows CLFS Security Feature Into SYSTEM Access

Public exploit code released earlier this week claims that a local Windows user can gain SYSTEM privileges through the Common Log File System driver. The proof of concept, called SignDrop, targets a log-authentication feature added to the driver last year. It abuses how clfs.sys creates companion files when a privileged process opens a prepared log, using path redirection to take control of

Read at The Hacker News

MarkTechPost Asif Razzaq SI

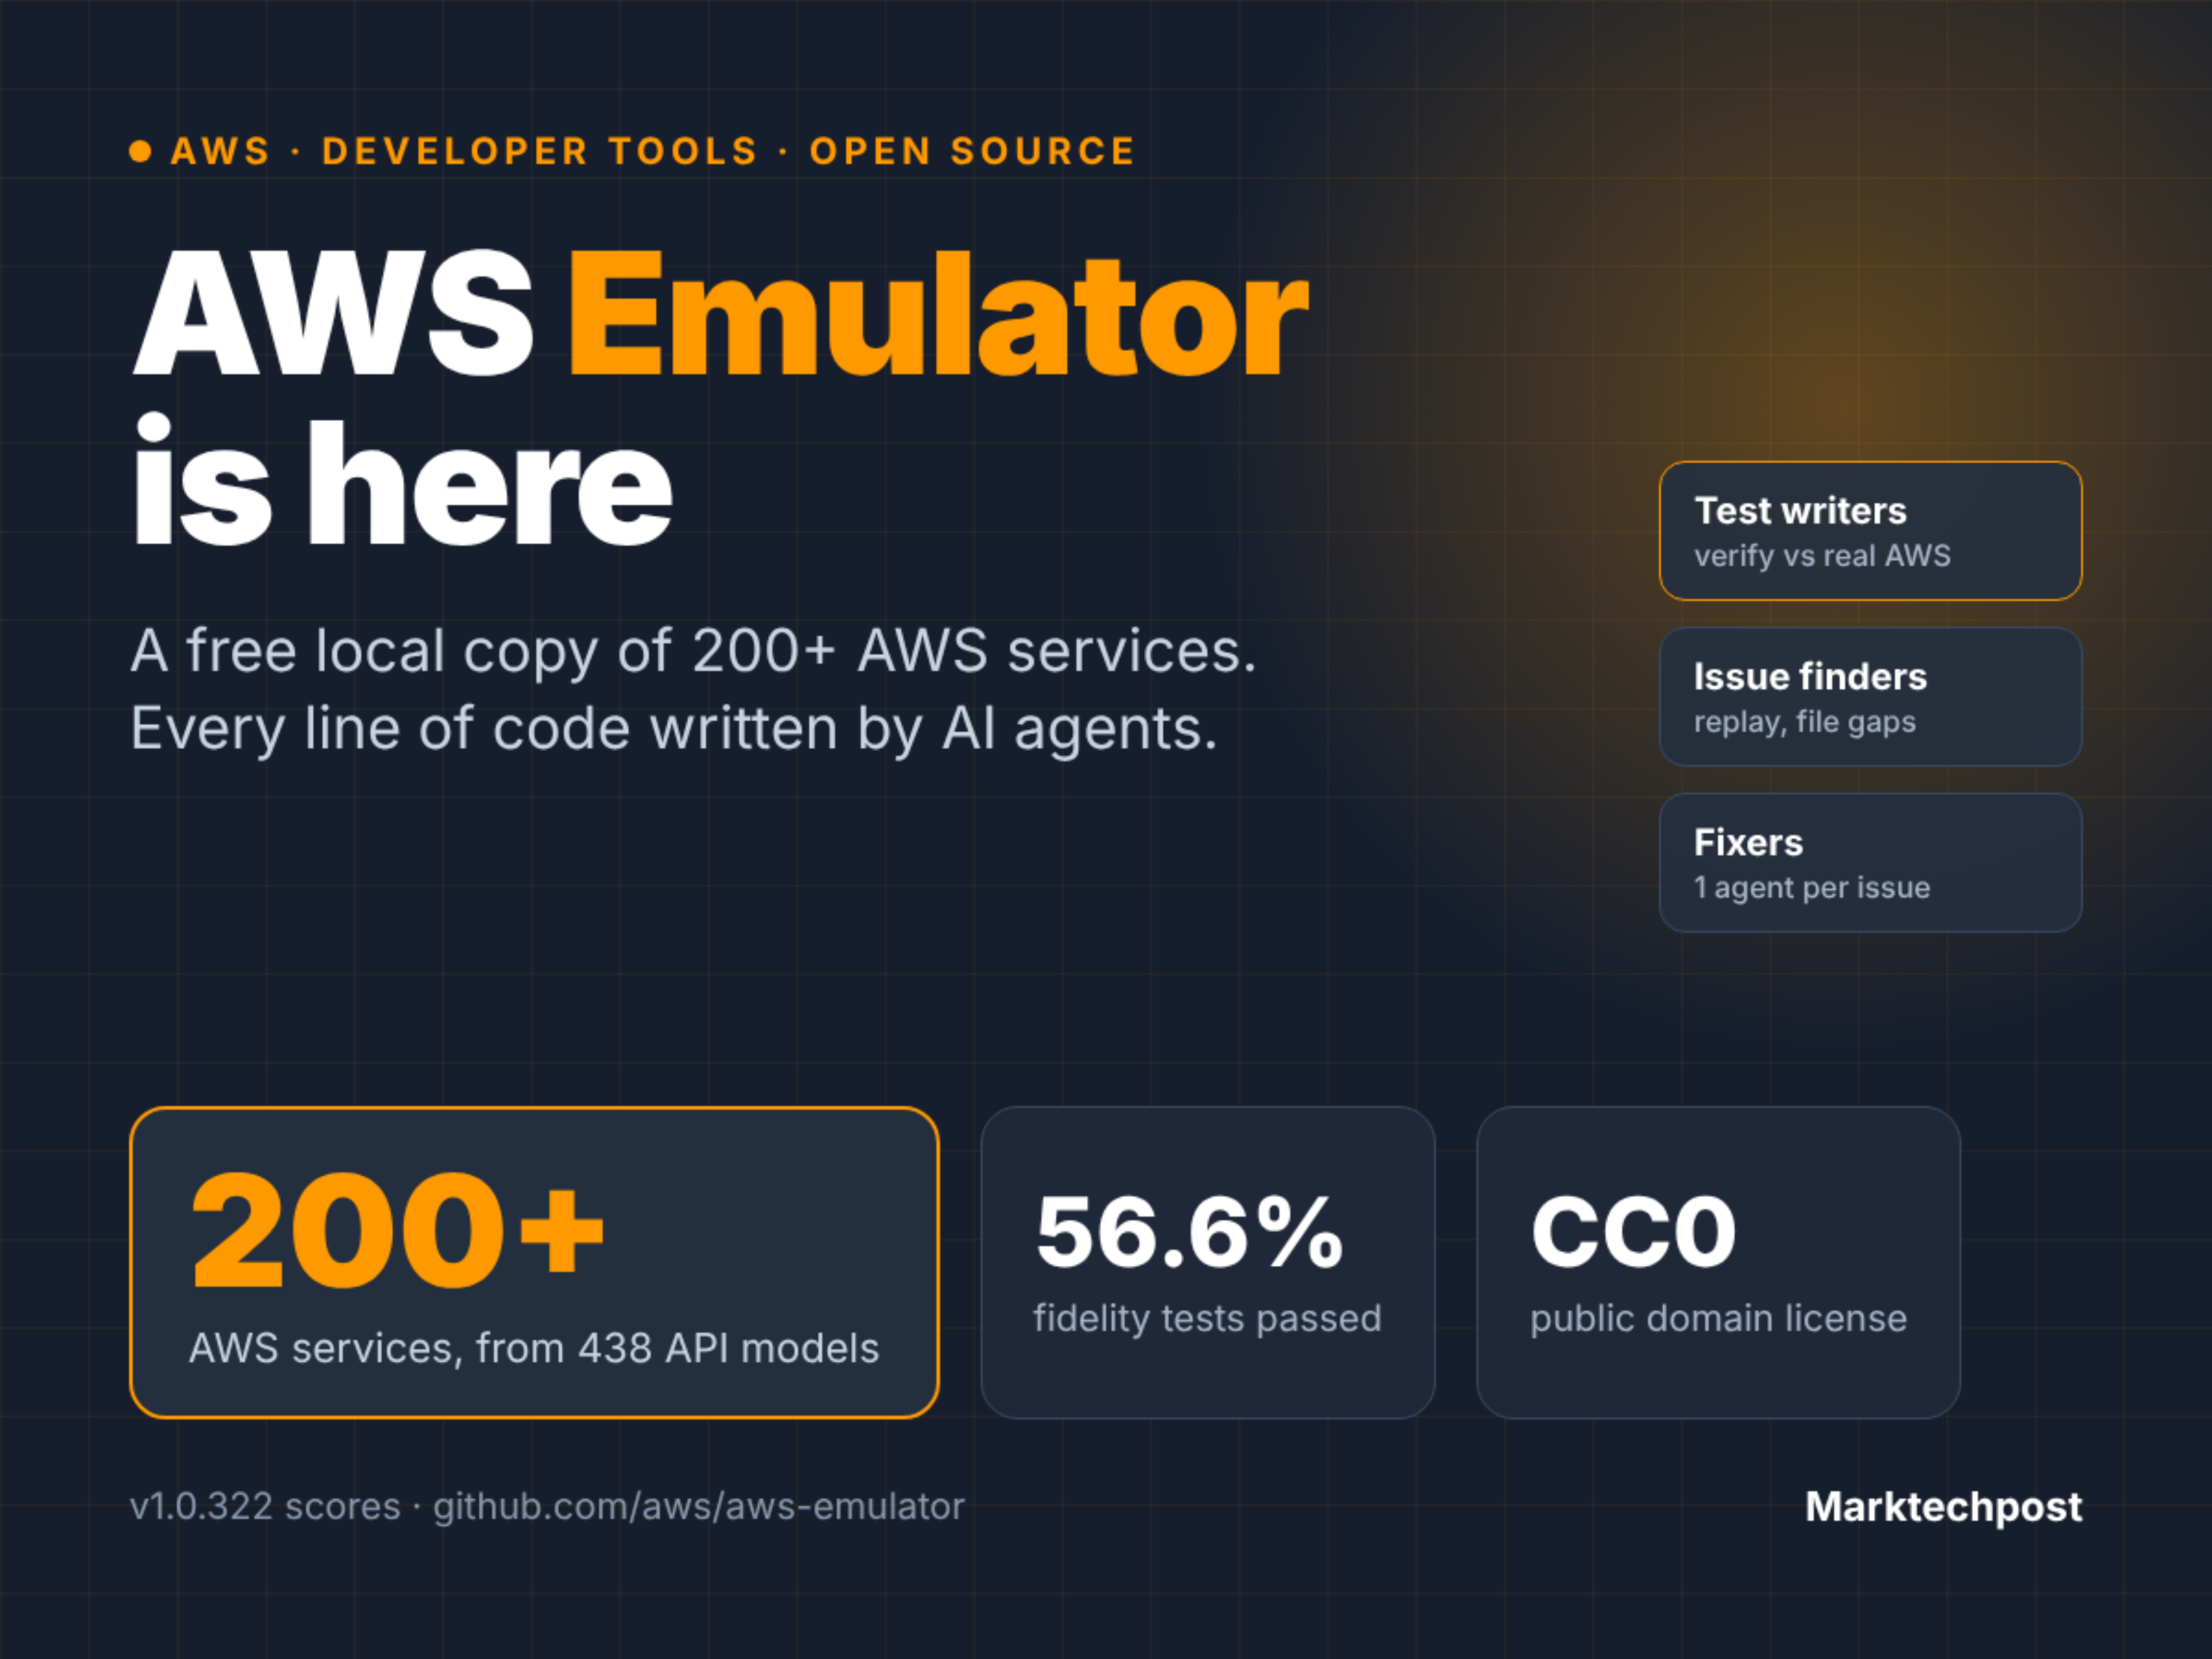
AWS Releases AWS Emulator: A Local Copy of 200+ AWS Services Built by AI Agents

AWS released AWS Emulator, a free, CC0-licensed local emulator of AWS APIs built from 438 API models. Autonomous agents wrote all of its code. It passes 56.6% of 42,857 published fidelity tests at launch.

Read at MarkTechPost

arXiv (research papers) Zhezhen Cao Security

Preserve the Vulnerability, Break the Alert: Testing the Robustness of CodeQL Taint Tracking with Natural Rewrites

Static application security testing (SAST) tools such as CodeQL serve as security gates in continuous integration and code review, and a gate is also read in reverse. When a previously reported alert disappears after a change, developers and the tools around them often take the vulnerability to be gone. That inference holds only if the analyzer is robust to changes that keep the vulnerability. We test this robustness for CodeQL's JavaScript taint tracking with natural…

Read at arXiv (research papers)

arXiv (research papers) Zimo Xu SI

CapLite: Prompt-Injection Defense for Small Language Model Agents without Model-Written Security Artifacts

Enforcement defenses against prompt injection, such as CaMeL, Progent, IPIGuard and DRIFT, ask the agent's own model to write a security artifact (a program, a privilege policy, a dependency graph or a constraint list) that code then enforces. We ask whether small language model (SLM) agents can be trusted to write these artifacts. Across 15 open-weight models, 13 of them between 1.7B and 12B parameters, they cannot: the policies, graphs and constraints that the agent's…

Read at arXiv (research papers)

arXiv (research papers) Arnab Sanyal

LazyWeights: Decode-on-Demand Edge LLMs

Memory decides which LLMs an edge device runs, and how fast: capacity on a 4 GB Jetson Nano, bandwidth on an 8 GB Jetson Orin Nano Super. Deployed formats (GPTQ, AWQ, llama.cpp's K- and I-quants) spend equal bits on every integer code of a matrix, although the codes are far from uniform. LazyWeights keeps these formats but tunes GPTQ so the codes compress, Huffman-codes them losslessly in interleaved lanes, and decodes them on demand in a small unit between DRAM and L2, so…

Read at arXiv (research papers)

arXiv (research papers) Arnab Sanyal

LazyWeights: Decode-on-Demand Edge LLMs

Memory decides which LLMs an edge device runs, and how fast: capacity on a $4$ GB Jetson Nano, bandwidth on an $8$ GB Jetson Orin Nano Super. Deployed formats (GPTQ, AWQ, $\texttt{llama.cpp}$'s K- and I-quants) spend equal bits on every integer code of a matrix, although the codes are far from uniform. $\texttt{LazyWeights}$ keeps these formats but tunes GPTQ so the codes compress, Huffman-codes them losslessly in interleaved lanes, and decodes them on demand in a small unit…

Read at arXiv (research papers)

AWS Machine Learning Blog Josh DeMuth SI

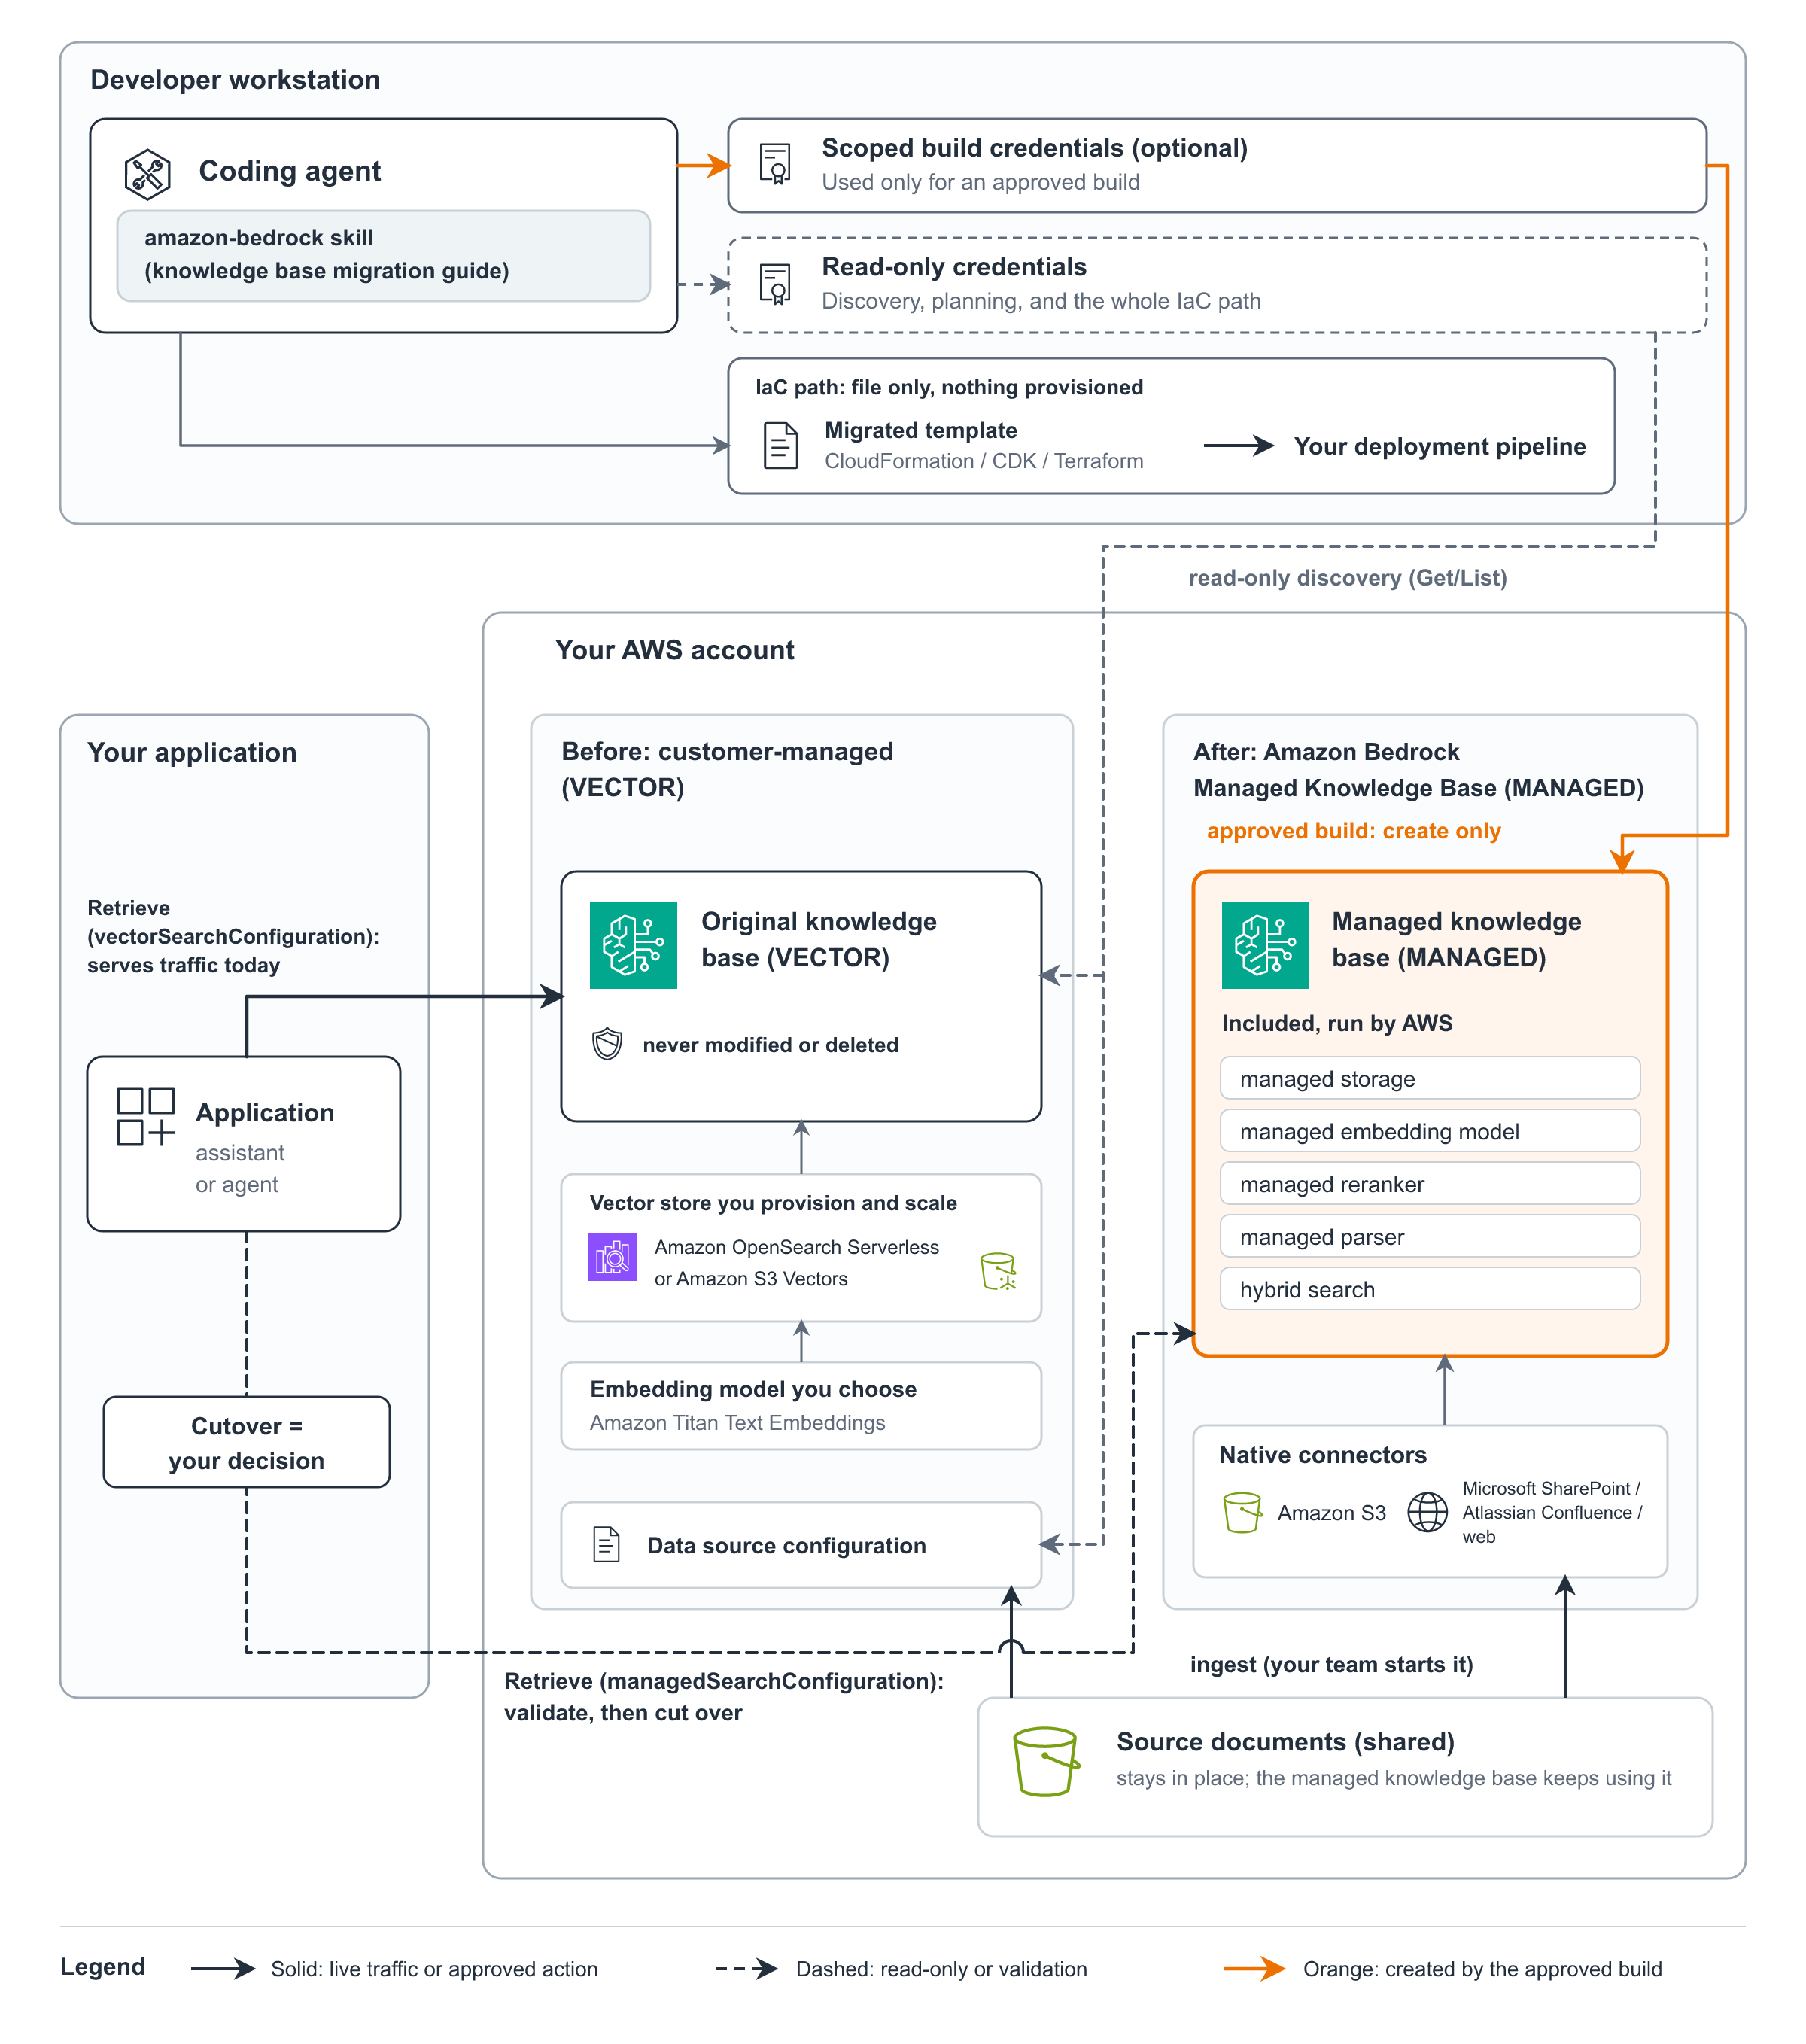
Migrate to Amazon Bedrock Managed Knowledge Base with your coding agent

The migration guide in the amazon-bedrock skill helps you migrate a customer-managed Amazon Bedrock knowledge base to a Managed Knowledge Base. Your coding agent plans the move with read-only discovery, creates the new knowledge base or an infrastructure-as-code template alongside the original, and validates retrieval before you cut over.

Read at AWS Machine Learning Blog

SecurityWeek Eduard Kovacs Security

Apache Patches Critical HTTP Server RCE Found by Anthropic, Google

The mod_http2 race condition, CVE-2026-119618, could let unauthenticated attackers execute code on servers with HTTP/2 enabled.

Read at SecurityWeek

The Hacker News Security

186 Fake AI Domains Redirect Users to ClickFix Lures, Browser Malware, and Search Hijackers

Cybersecurity researchers have found that lookalike domains masquerading as artificial intelligence (AI) tools are being used to serve ClickFix-style lures, browser-hijacking malware, and a set of extensions that hijack user searches. This delivery pattern has been codenamed TypoPrompting by Island. "AI-app lookalikes that turn an attempt to reach a familiar tool into a prompt to verify,

Read at The Hacker News

arXiv (research papers) Jarosław Janas Security

Look It Up: Multi-bit LLM Watermarking via Codebook Search

Attributing short LLM-generated texts to a specific source remains challenging for existing multi-bit watermarking methods, which often require long generations or costly decoding to recover payloads reliably. We propose a codebook-based watermarking scheme that maps an $n$-bit payload to a longer $u$-bit codeword and embeds it during generation through token-level logit biasing. During extraction, the received bit sequence is matched to the nearest codeword in a precomputed…

Read at arXiv (research papers)

Older stories