Three AI Models Agree on Just One of 121 Potential Code Flaws
Echo tested Claude Mythos, GPT-5.6 Sol and GLM-5.3 on the same code and found little overlap
Echo tested Claude Mythos, GPT-5.6 Sol and GLM-5.3 on the same code and found little overlap
We construct continuous-variable stabilizer codes realizing every achiral 2D abelian topological order, both bosonic and fermionic. Starting from an arbitrary signature-zero integer $K$-matrix, we show that the corresponding topological order can be obtained by condensing a lattice of dyons with trivial pairwise mutual braiding in an $\mathbb{R}^N$ gauge theory. We implement this condensation microscopically by gauging a non-on-site 1-form symmetry of the $\mathbb{R}^N$…
Vietnam and the Philippines agreed to boost bilateral parliamentary cooperation as well as coordination in multilateral inter-parliamentary forums. On global and regional issues of shared concern, they pledged to maintain ASEAN’s common stance on the East Sea issue and make active, responsible contributions to developing an effective and substantive Code of Conduct in the East Sea (COC). Vietnam, Philippines promote more effective ASEAN parliamentary diplomacy Vietnam…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added a critical security flaw impacting Perforce Puppet, an enterprise infrastructure-as-code (IaC) and configuration management platform, to its Known Exploited Vulnerabilities (KEV) catalog, citing reports of active exploitation. The vulnerability, tracked as CVE-2026-115731 (CVSS score: 9.4), is a case of
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has urged organizations to immediately patch a newly disclosed critical security flaw impacting Oracle Java. The flaw, tracked as CVE-2026-114938 (CVSS score: 8.1), refers to a case of out-of-bounds write that can lead to denial-of-service (DoS) or remote code execution under certain conditions. "This critical memory-corruption
Intent contracts are an authorization interface for tool-using LLM agents in which the planning model holds no tools. For each step it submits a short logged contract: a goal, a verbatim quotation of the user, and scope fields. Code validates the contract, and a small trusted model checks it against the user's words and writes the tool call itself. Provided the validation and dispatch code is correct, every executed call is written by the trusted model, the planner's…
Sumitomo Life uses ChatGPT Enterprise to research insurers, prepare proposals, and draft code for investment analysis. Early use by executives helped drive adoption.
See how Codex runs commands on your machine while enforcing the filesystem and network limits you control across macOS, Linux, and Windows.
Calif demonstrated remote code execution in Jira, Jenkins and Keycloak, while VulnCheck says real-world RCE requires per-target work
Anthropic has added Code Mode to Claude Code v2.1.323. The experimental feature lets Claude write JavaScript that chains Bash, Read and Edit calls in 1 step, and keep talking while long commands run.
In another major cybersecurity incident, malicious code injected into websites through digital experience platform (DXP) Optimizely exposed visitors to potential…
The tool supports 11 ASEAN languages as well as code-switching, according to A*STAR.
ReversingLabs has taken apart BubbleLoader, a loader that turns ordinary Windows programs into carriers for other malware. The attackers rewrite a handful of instructions at a program’s entry point, the spot where Windows begins running it, and add two PNG images that hold the hidden code. Known hosts include WinRAR, the x64dbg debugger, Windows Media Player, the Firefox launcher and virtiofs. The earliest BubbleLoader samples appeared in February 2026, and ReversingLabs…
Inference-time scaling, allocating more compute during generation rather than pre-training, has demonstrated dramatic quality improvements for LLM reasoning tasks. Its behaviour in structured hardware verification code generation, where outputs must satisfy compiler correctness, protocol semantics, and functional coverage constraints simultaneously, is less understood. We present a systematic, simulator-grounded study of inference-time compute scaling for agentic UVM…
‘I would say that it was a success simply because of the work that we were able to achieve,’ President Ferdinand Marcos Jr. says, despite no big breakthroughs on Myanmar or the long-awaited South China Sea Code of Conduct
A Java flaw called Java4Shell can let attackers without an account run their own code on Jira, Jenkins, Keycloak, and three other widely used applications, says Calif, the security research firm that disclosed it this week. The flaw is present in Java 17.0.6 and later, and the vulnerable code runs only on x86-64 Intel and AMD chips that support the AVX-512 VBMI feature. Tracked as
Compiler rewrites can preserve returned values while violating object lifetime or ownership. Such failures arise when a rewrite changes when an object remains live, whether a borrowed pointer stays supported, or what ownership reaches the caller. We present JITAtlas, a source-level checker that reconstructs reference and target computations from optimizer code and checks valid uses, continuous borrow support, and caller-visible ownership. On a 58-input benchmark constructed…
The 2026 Quantum Open Source Survey, with over 1,800 respondents, reveals key trends in quantum software adoption, hybrid workflows, and AI tooling. Qiskit leads in SDKs, IBM Quantum in cloud services, and Anthropic Claude Code in AI assistants. The survey also highlights the growing use of Python and C/C++, challenges in QEC and HPC, and cautious optimism regarding AI's role in quantum development.
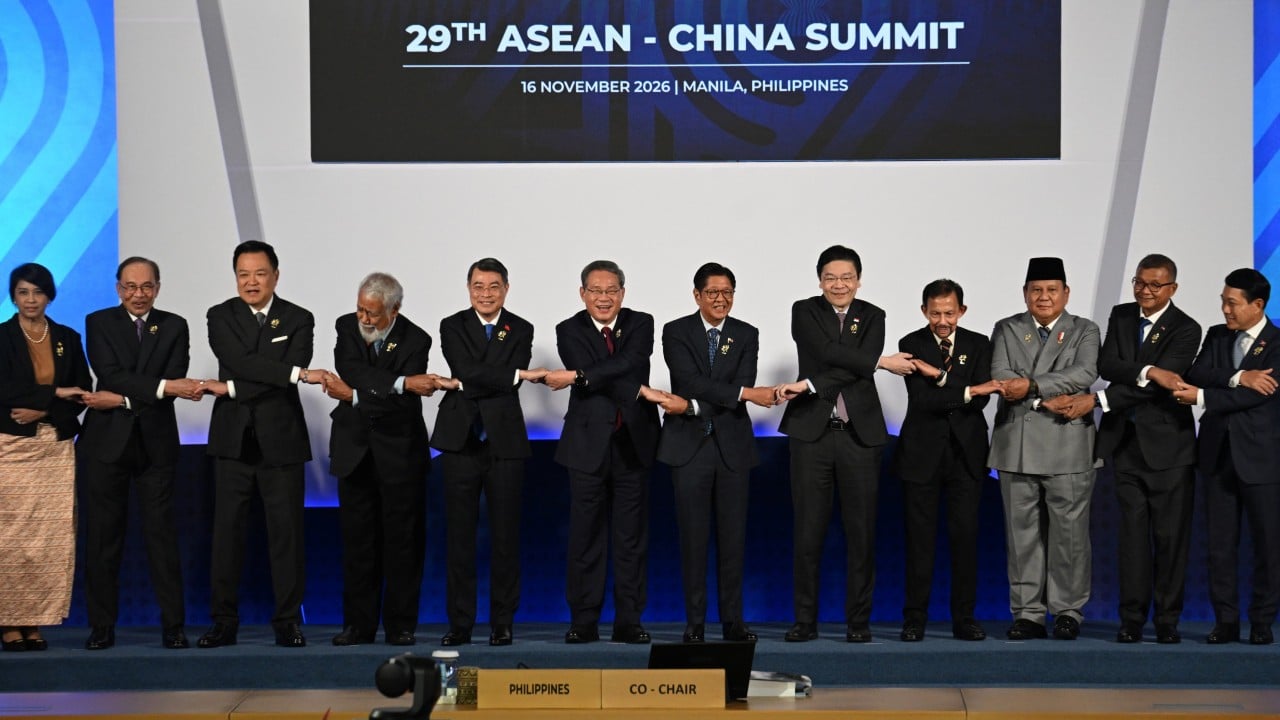
A long-delayed South China Sea code of conduct (COC) may be within reach, but regional experts at a forum held alongside the Asean summit in Manila have cautioned against unrealistic expectations over an agreement designed to manage tensions rather than to resolve the maritime row. On Tuesday, the Philippines handed the rotating chairmanship gavel to Singapore at the closing of the Association of Southeast Asian Nations summit in Manila, with the city state expected to lead…
Hardware specialization can improve datacenter efficiency. Unfortunately, identifying computations that justify dedicated hardware is difficult. Existing approaches analyze hot functions, instruction patterns, or overheads such as datacenter tax. They can miss fine-grained computations whose aggregate cost is spread across applications and libraries, especially when different pieces of code obscure the same underlying computation. We observe that seemingly unrelated code…
Fairness audits treat a trained model as a fixed decision function, but the arithmetic that evaluates it is part of that function. This study holds the model, records, threshold and audit code fixed and varies the numerical execution contract in two tiers. Tier 1 changes only how products and sums are computed, with the serialized weights byte-identical, and is the causal test of arithmetic. Tier 2 runs reduced-precision deployment configurations (BF16 compute, FP8 and 8-bit…
External sandboxes for coding agents I've been exploring new ways to sandbox code that is executed by agents, with a focus on making it safer to try out local models without worrying that a mistake or prompt injection attack might cause them to take damaging actions on a machine. I worked on this project with Prime Radiant, the AI research lab behind Superpowers and other projects. My post on the Prime Radiant blog introduces the external sandbox pattern, where code executed…
AMD just sent out invitations to its CES 2027 media event to be held in Las Vegas next January. The invitation has a curious peak-shaped motif. This could hint at "Olympic Ridge," codename for the next-generation Ryzen desktop processor powered by the "Zen 6" microarchitecture. AMD in its recent EPYC 9006 "Venice" server processor release unveiled "Zen 6" to offer significant IPC increases in enterprise workloads; but these gains were evaluated in enterprise benchmarks. "Zen…
The European Union Deforestation-Free Regulation (EUDR), Brazil’s Forest Code (Law No. 12,651/2012), and the proposed National Policy for Digital Transformation in Agriculture (Bill No. 4,132/2025) together create a complex regulatory framework for Brazilian agricultural exports. Although these frameworks share common objectives such as preventing deforestation, ensuring traceability, and promoting sustainable production, they differ in their definitions, thresholds, and…
Researchers said they found malicious JavaScript code on 178 different widely visited websites run through the Optimizely Web experimentation platform. The company confirmed the breach.
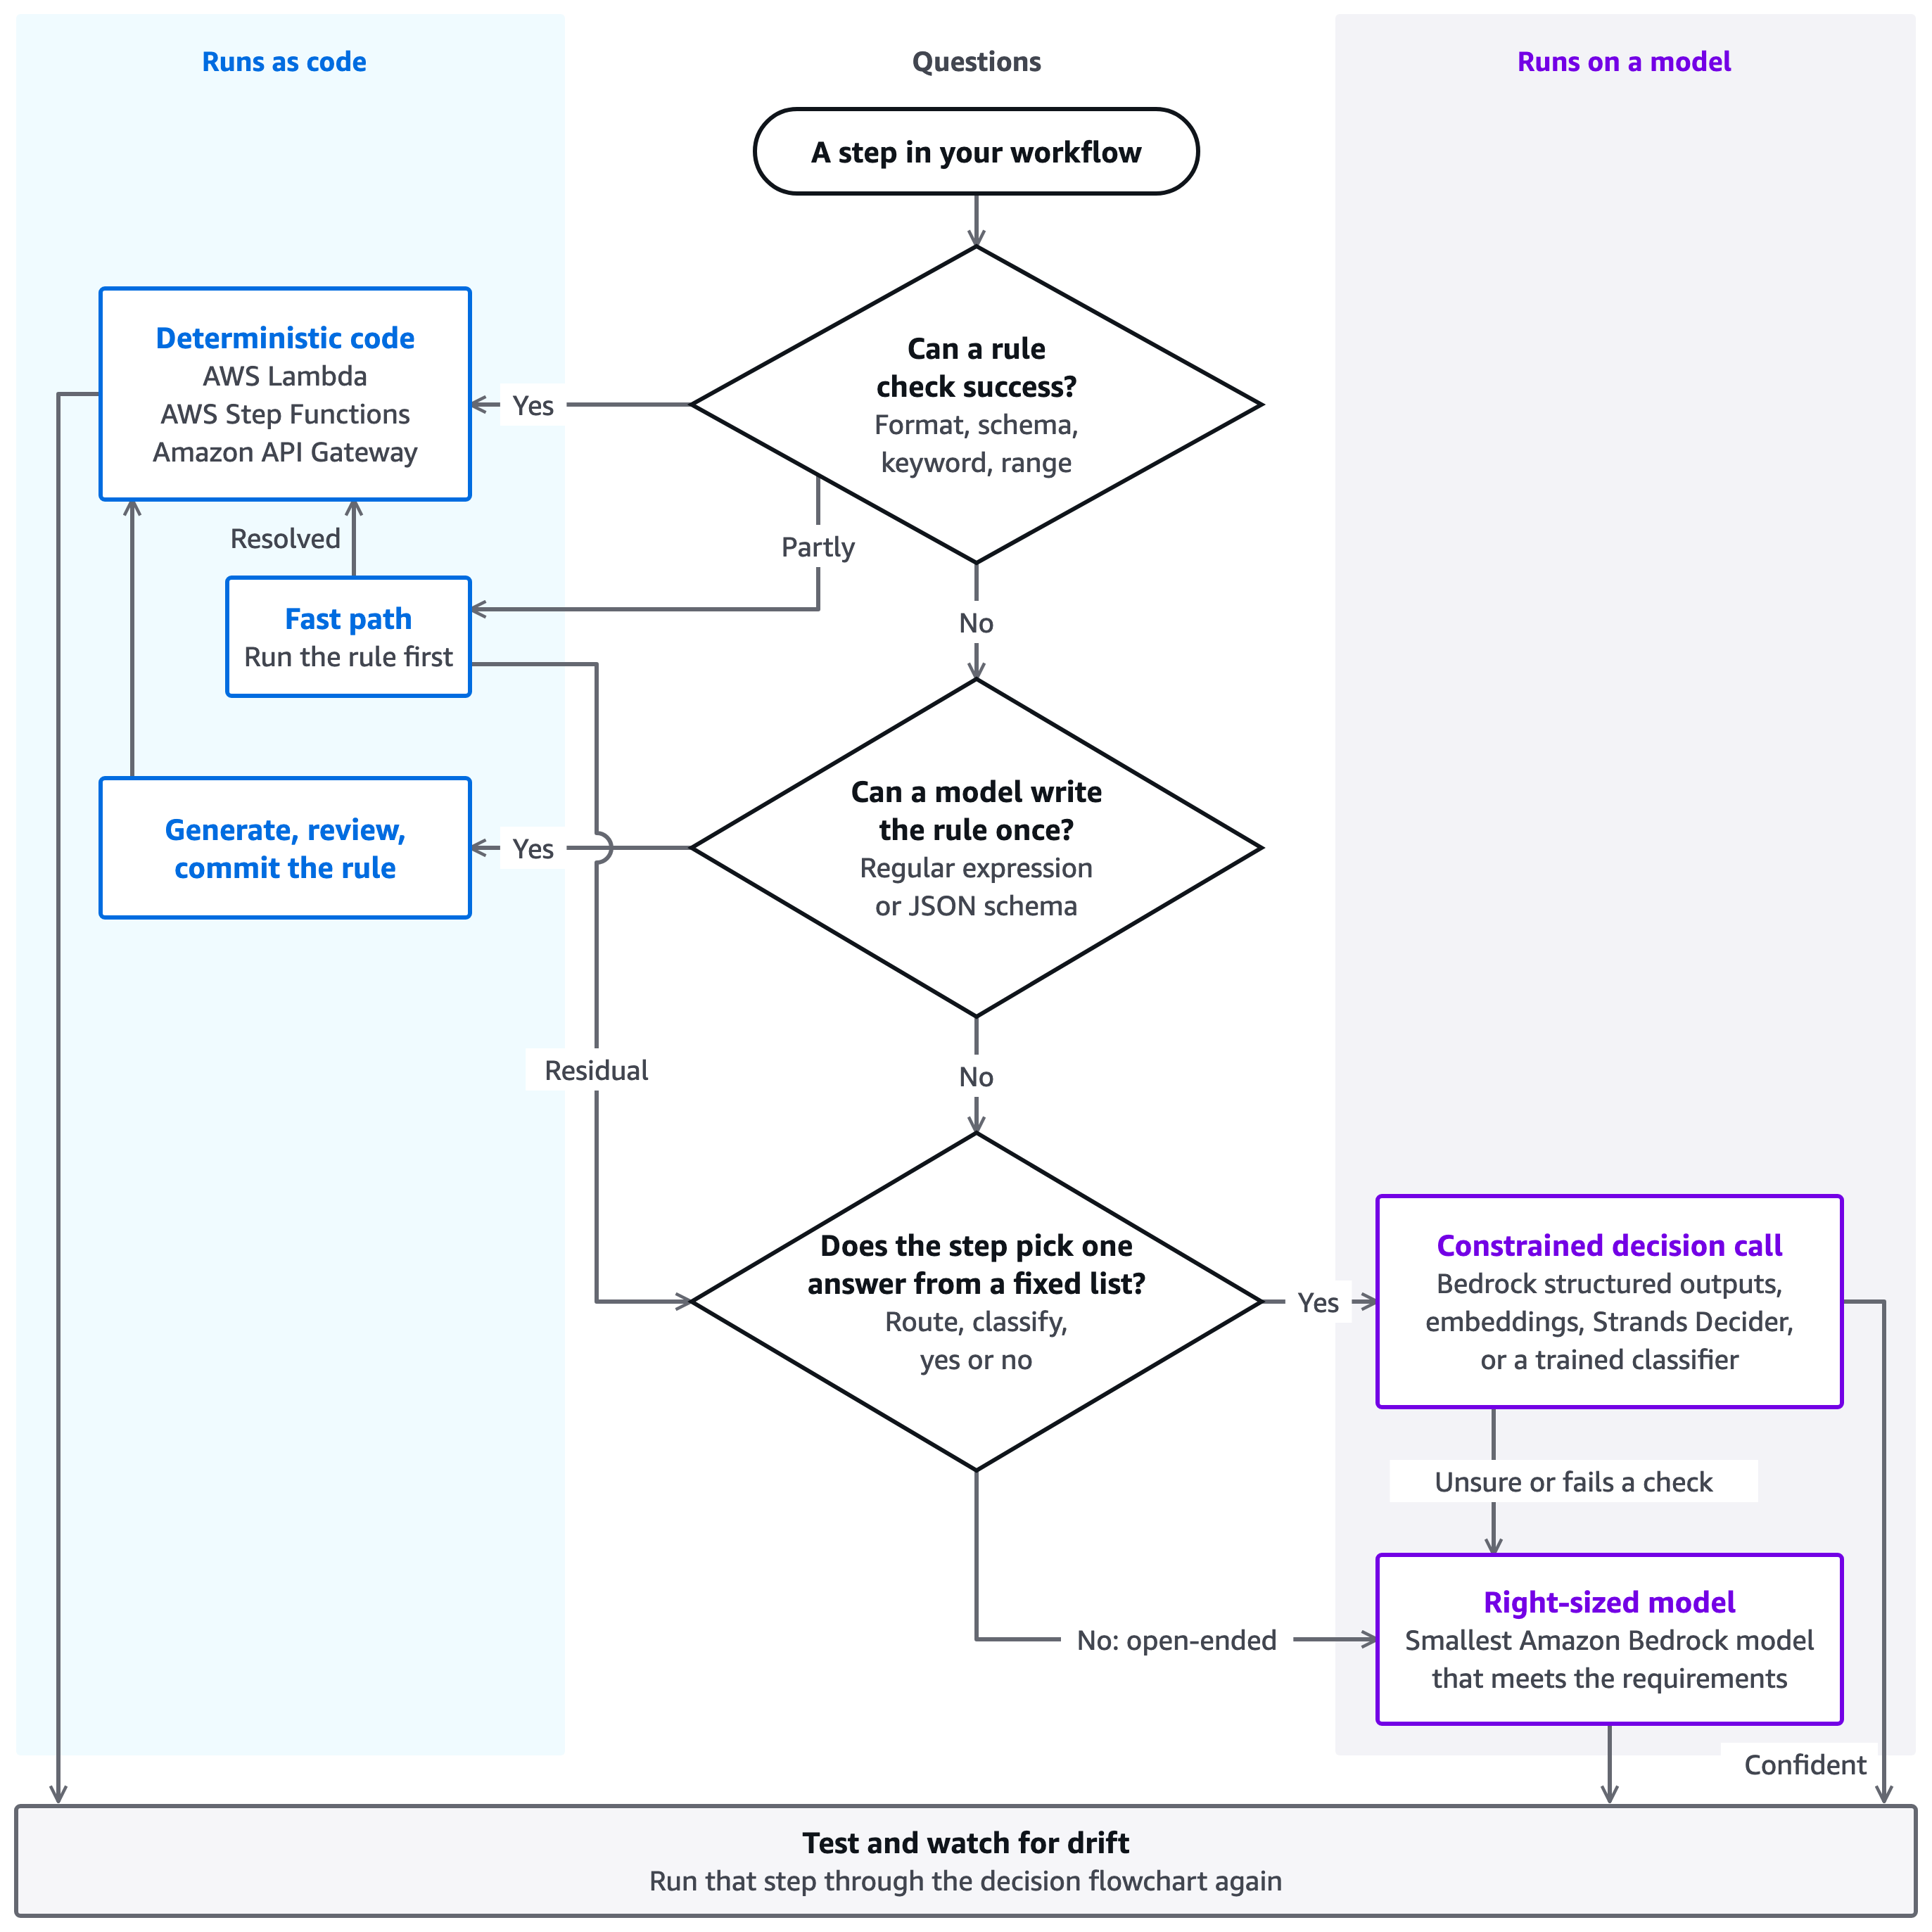
The biggest cost lever in a generative AI system is whether you call a model at all. Learn how to decide whether each workflow step needs a model, and map each option to AWS: deterministic code, a constrained decision call, or a right-sized model on Amazon Bedrock.
The OPTIMJACK supply chain attack demonstrates how a compromised vendor script can expose websites, highlighting the need for strict segmentation.
Official development assistance fell by 23.1 per cent in 2025, and the decision of who is helped first when there is not enough for everyone is moving into software. A leading published machine-learning targeting system excluded 53 per cent of eligible households as deployed. If the rule of distribution ends up in code, it should carry the judgement of many cultures, and the machine should execute while a person judges. AllotNet is an interpretable mixture-of-experts…
Programmable logic controllers (PLCs), the industrial computers that operate power and process plants, often run programs whose source code is no longer available; however, every input and output of the controller is logged continuously. This paper therefore asks whether a large language model (LLM) can recover an executable program in Structured Text (ST), the standard PLC language of IEC 61131-3, from such input/output records (traces) alone and, equally important, how the…
A malicious widget can bypass the security filter that Telegram added to its Android app last week and run code outside it, according to NebuSec, a security company. Widgets are small interactive blocks that bots send inside chat messages, and their JavaScript runs on the user's phone. The researchers ran their demonstration on a Telegram test server, because only approved bots can send